
このページの内容
ユースケース:Eduroam向けMist Edgeプロキシ
ジュニパーMist™とeduroamの導入を計画する際には、このユースケースに目を通して、Mist EdgeをIdPプロキシとして使用することで、Juniper Mist Access Assuranceをeduroamと統合する方法を確認してください。
概要
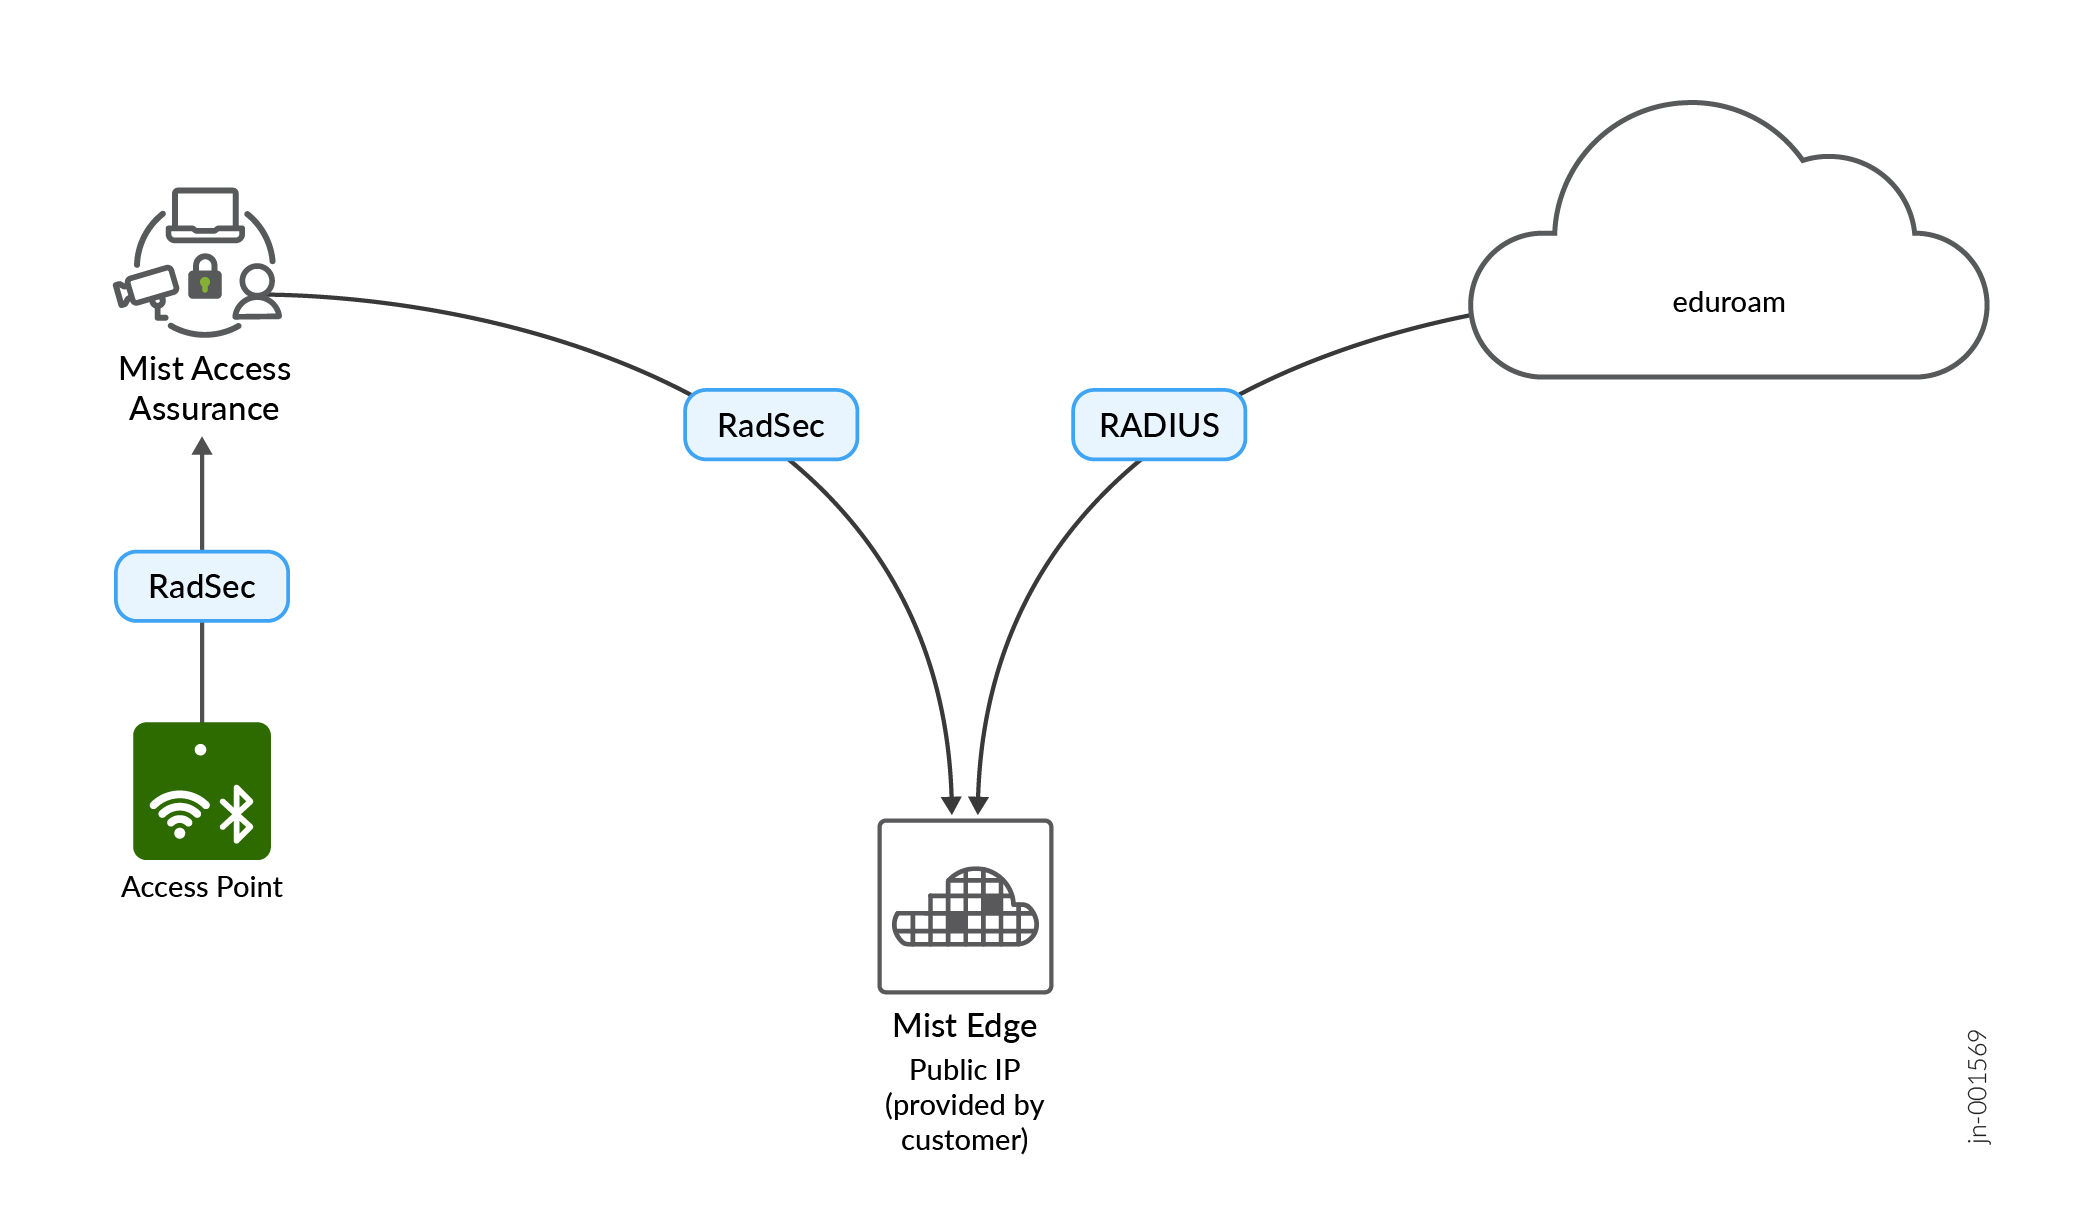
このユースケースでは、RADIUSプロキシとして機能するMist Edgeを使用して、ジュニパー Mist Access Assuranceをeduroam NRO(National Roaming Operators)と統合する方法を示しています。Mist Edgeは、eduroam管理ポータルでRADIUSクライアントとして登録できるように、静的なパブリックIPまたはNAT IPが割り当てられたeduroamRADIUSサーバーへのゲートウェイとして機能します。
Mist Edgeプロキシは、特にeduroam SPとIdP認証フローで使用されます。ホームユーザーの認証には影響しません。
次のコールフローは、eduroamネットワーク内の3つのタイプのユーザーと、それぞれのタイプがMist Access AssuranceとMist Edgeプロキシを介して認証される方法を示しています:キャンパス内のホームユーザー、キャンパス内の外部訪問者(SP)、ホームローミングユーザー(IdP)。
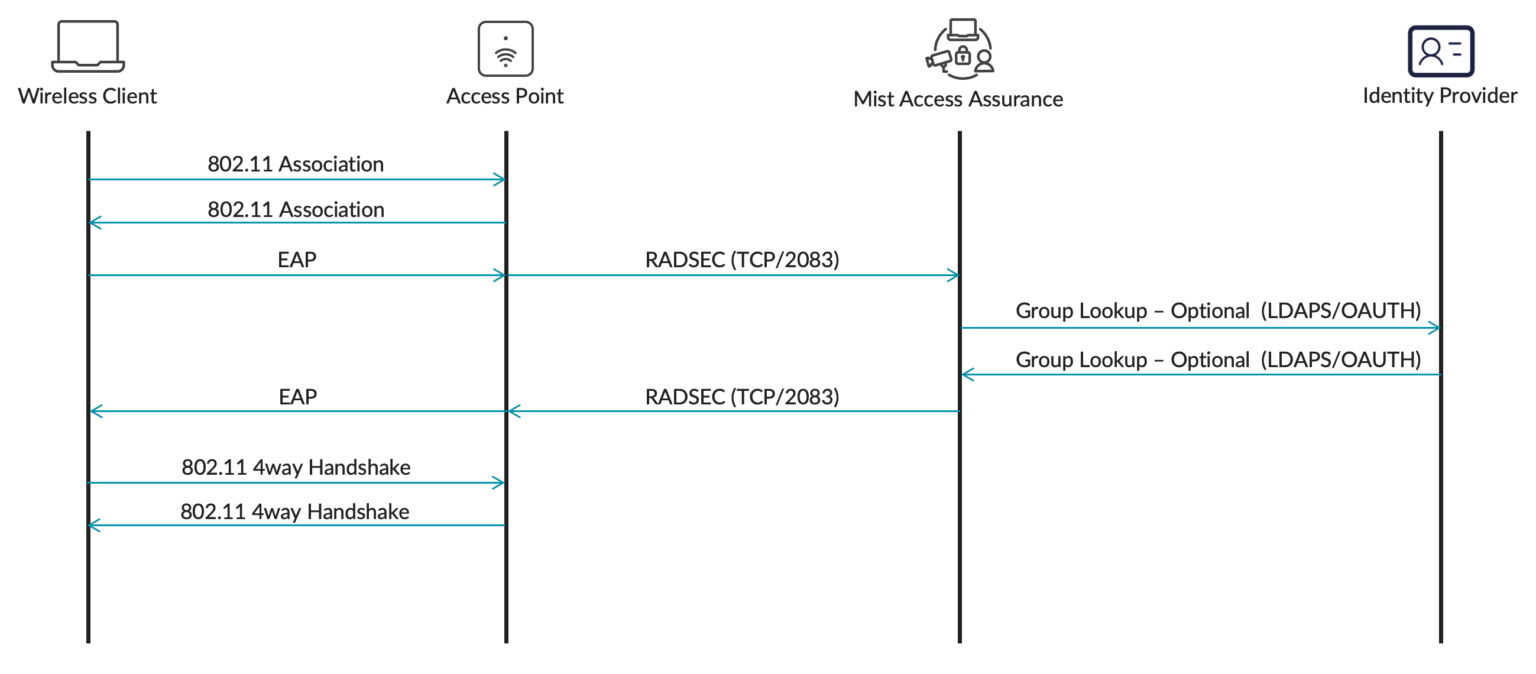
ホームユーザー
ホームユーザーは、自分の大学キャンパスでeduroam SSIDに接続しているクライアントです。たとえば、 @university1.edu アカウントを持つユーザーは現在 University 1 にいます。このユーザーは「ホーム」領域にいます。これは、この大学で毎日行われているほとんどの認証の典型的なシナリオです。
このシナリオでは、Mist Edgeプロキシは必要ありません。ユーザーは、Mist Access Assuranceで直接認証します。
外部訪問者
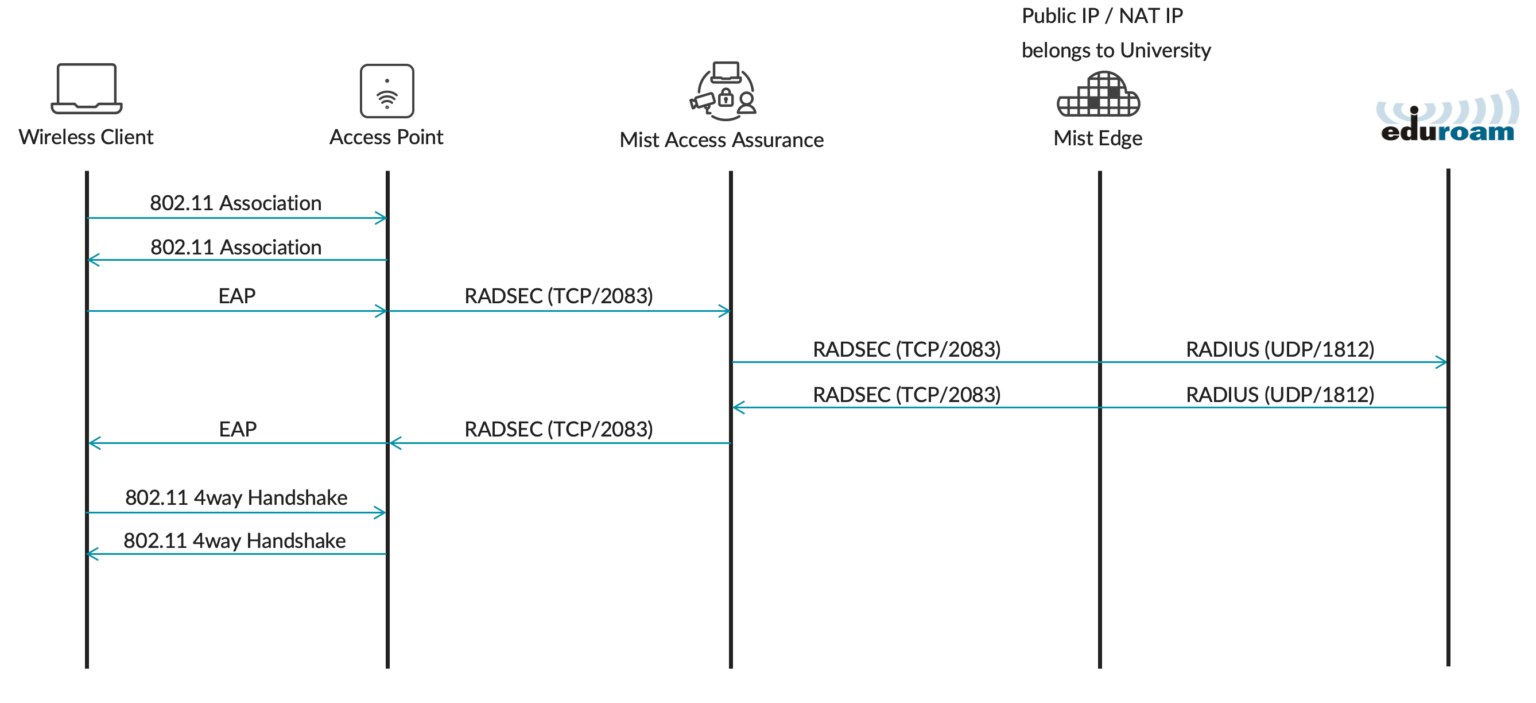
外部訪問者とは、他の機関から大学キャンパスを訪問するクライアントです。たとえば、 @university2.edu アカウントを持つユーザーが現在大学 1 にアクセスしています。このユーザーは、「ホーム」レルムではないレルムによって識別されます。
このシナリオではMist EdgeプロキシIDPが eduroam RADIUS サーバーを介して認証要求を university2.edu に転送する必要があります。外部訪問者は、Mist Edgeプロキシを介して認証します。Mist Edgeプロキシは、eduroamの国内RADIUSサーバーに向けて認証要求をプロキシします。
ホームローミングユーザー
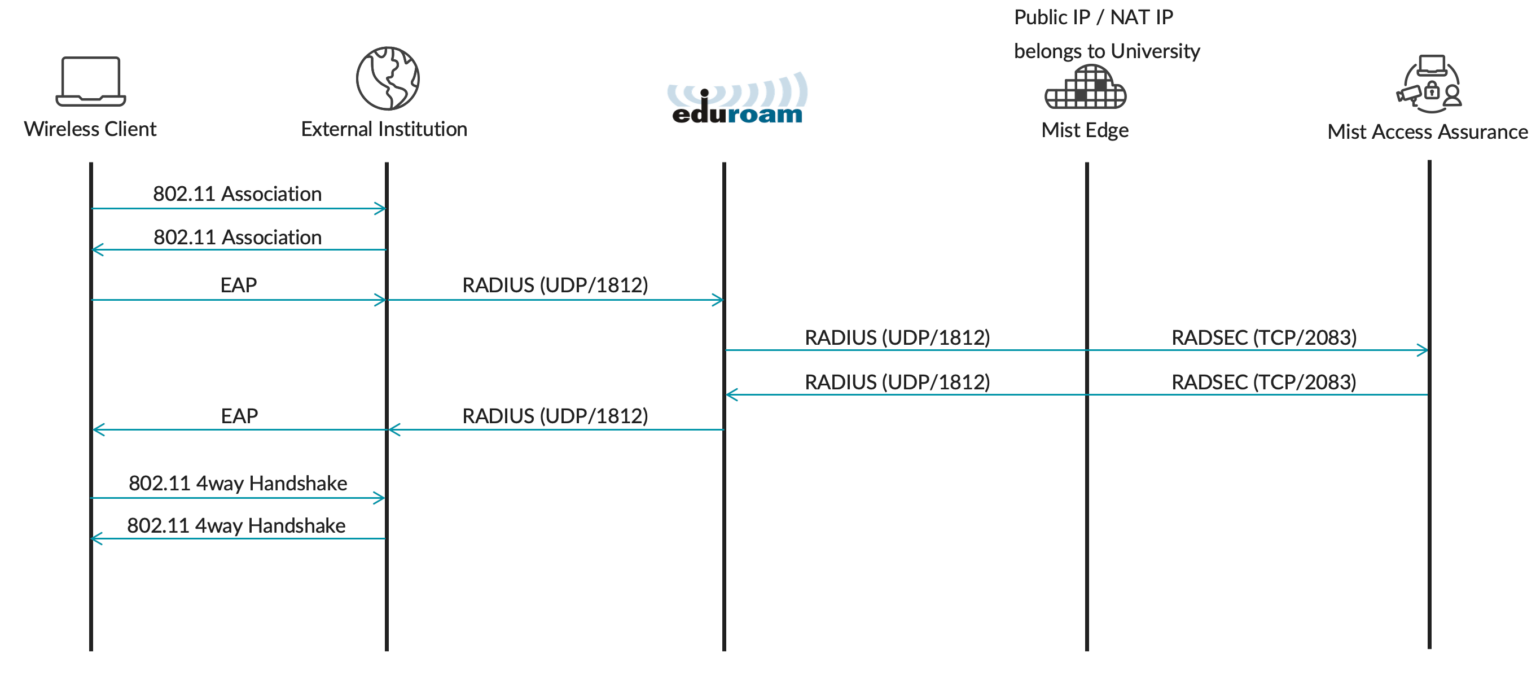
ホームローミングユーザーは、別の教育機関を訪問し、自国の大学の資格情報を使用してeduroam SSIDに認証したいクライアントです。
この例では、 @university1.edu アカウントを持つユーザーが University 2 にアクセスしています。認証要求は、university2.edu からeduroam経由で university1.edu RADIUSサーバーに送信されています。eduroamの国内RADIUSサーバーからのRADIUSアクセスリクエストは、Mist Edgeプロキシによって受信され、認証のためにMist Access Assuranceサービスに転送されます。
ファイアウォール要件
Mist Edge uses Out Of Band Management interface (OOBM) for all its proxy functionalities. You need to ensure that traffic can flow to and from the Mist Edge OOBM interface.
Allow the following ports and destinations:
-
Inbound (towards Mist Edge OOBM interface)
-
RADIUS Auth & Acct (1812 / 1813 UDP). You can limit source IPs to eduroam national RADIUS servers.
-
RadSec (2083 TCP). You can limit source IPs based on the following document.
-
-
Outbound (from Mist Edge OOBM interface):
-
RADIUS Auth & Acct (1812 / 1813 UDP)
-
RadSec (2083 TCP) towards radsec.nac.mist.com
-
HTTPS (443 TCP) towards ep-terminator.<mist_cloud_env>.mist.com (more on correct endpoint for your cloud environment in this document).
-
- Mist Access Assurance only supports EAP-TLS, TEAP or EAP-TTLS methods for home users and home roaming users.
- For external visitors any EAP method is supported, including PEAP-MSCHAPv2. EAP method support is determined by an external institution RADIUS servers.
- Dedicated Mist Edge(s) are a must for the IDP proxy functionality.
- For proxy service redundancy, multiple Mist Edges can be used as part of the same Mist Edge cluster.
ジュニパー Mist の設定
- Mist EdgeプロキシIDPを追加します。
ヒント:
-
プロキシを使用してIDプロバイダを追加するにはMist Edge:左側のメニューから、 組織 > アクセス > IDプロバイダを選択します。ページの静的設定セクションで、 IDPの追加をクリックします。IDPタイプとして Mist Edge プロキシを選択します。設定セクションのフィールドに入力します。ヘルプについては、画面のヒントを参照してください。
-
プロキシホストを指定するには—Mist EdgeがRadSecおよびRADIUSリクエストをリッスンするパブリックIPv4アドレスを入力します。これらのデバイスはすべて、指定されたMistクラスターに属している必要があります。
-
このプロキシからドメイン/レルムを除外するには—ドメイン/レルムをカンマで区切って入力します。たとえば、ほとんどの場合、独自のユーザーに対してローカル認証を使用するため、myuniversity.edu などの大学のドメインを除外します。
-
要求でRADIUS Operator-Name属性を指定するには—1myuniversity.com などの1<fqdn>形式で属性を入力します。
例文
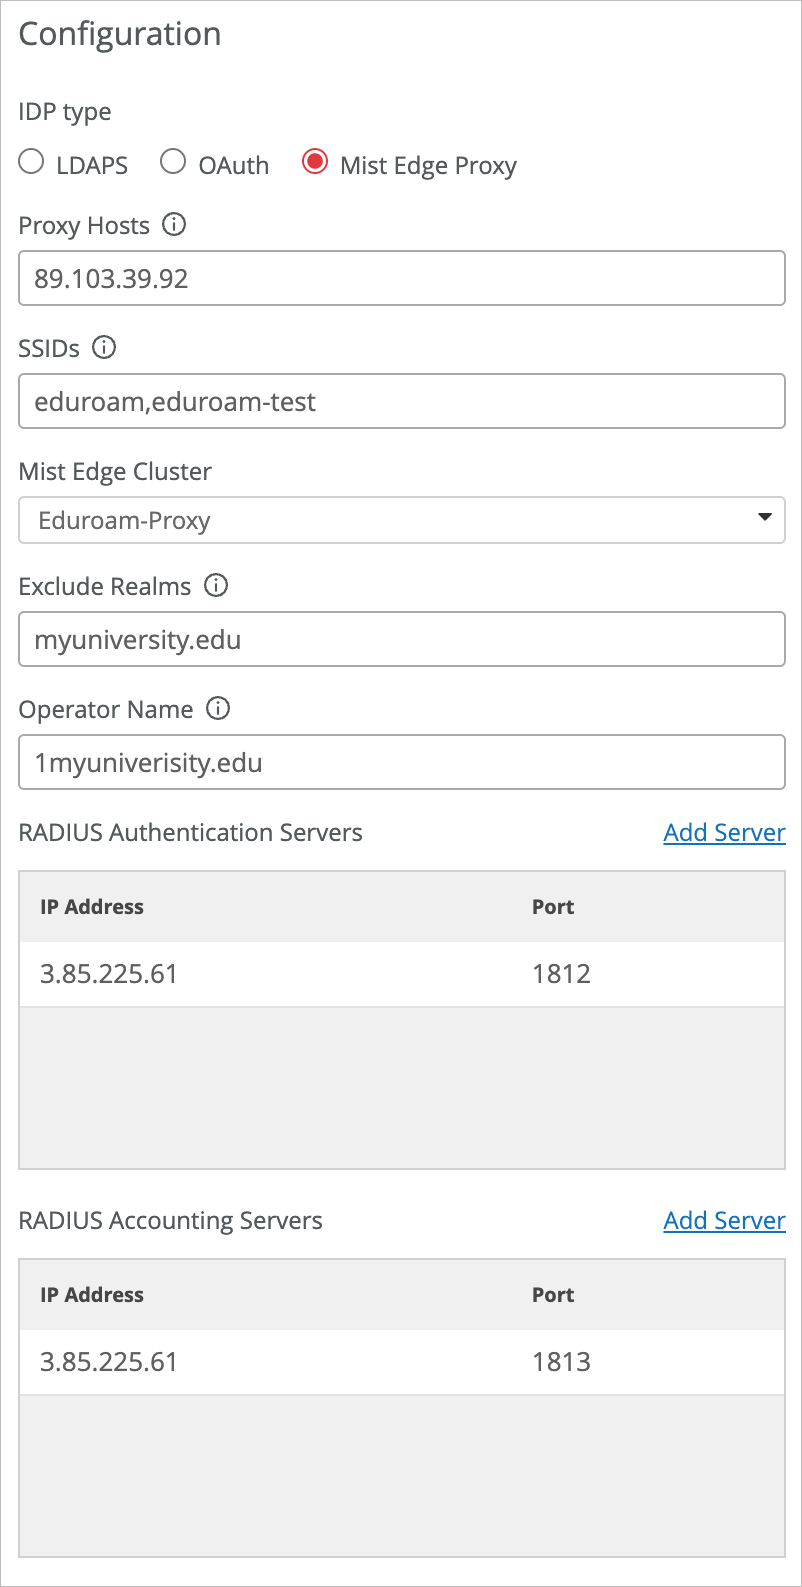 詳細については、「 ジュニパー Mist Access Assurance の ID プロバイダの追加」を参照してください。
-
- ユーザーと訪問者のアクセスルールを設定します。
ヒント:
-
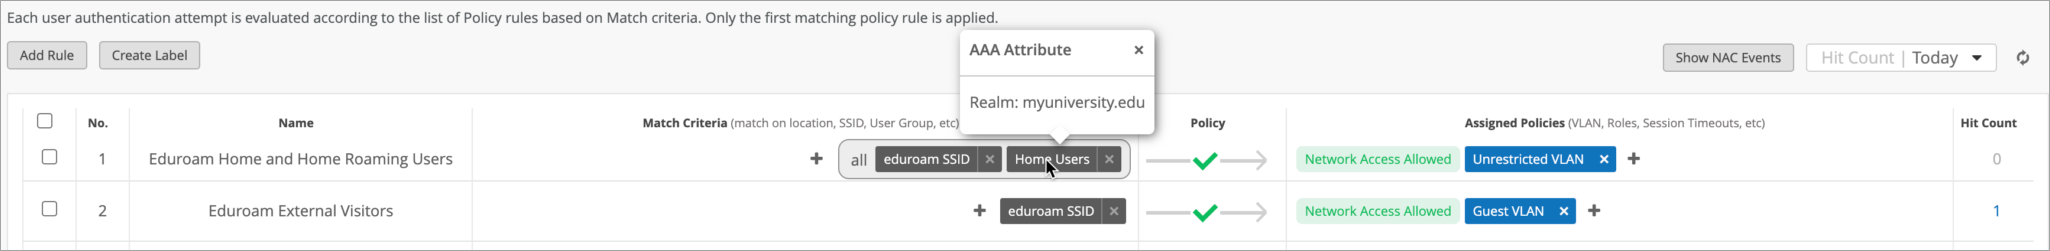
ポリシーを追加するには—左側のメニューから、 組織 > アクセス > 認証ポリシーを選択します。 ルールを追加をクリックします。名前、一致基準、アクション(許可またはブロック)、ポリシーを入力します。
-
詳しい手順については、「 認証ポリシーの設定」を参照してください。
次の例は、3種類のユーザーすべてに適用されるルールを示しています。最初のルールは、ホームローミングユーザーとホームローミングユーザーをプライマリ大学VLANに配置します。2つ目のルールは、外部訪問者をゲストVLANに配置します。
-
eduroamを設定する
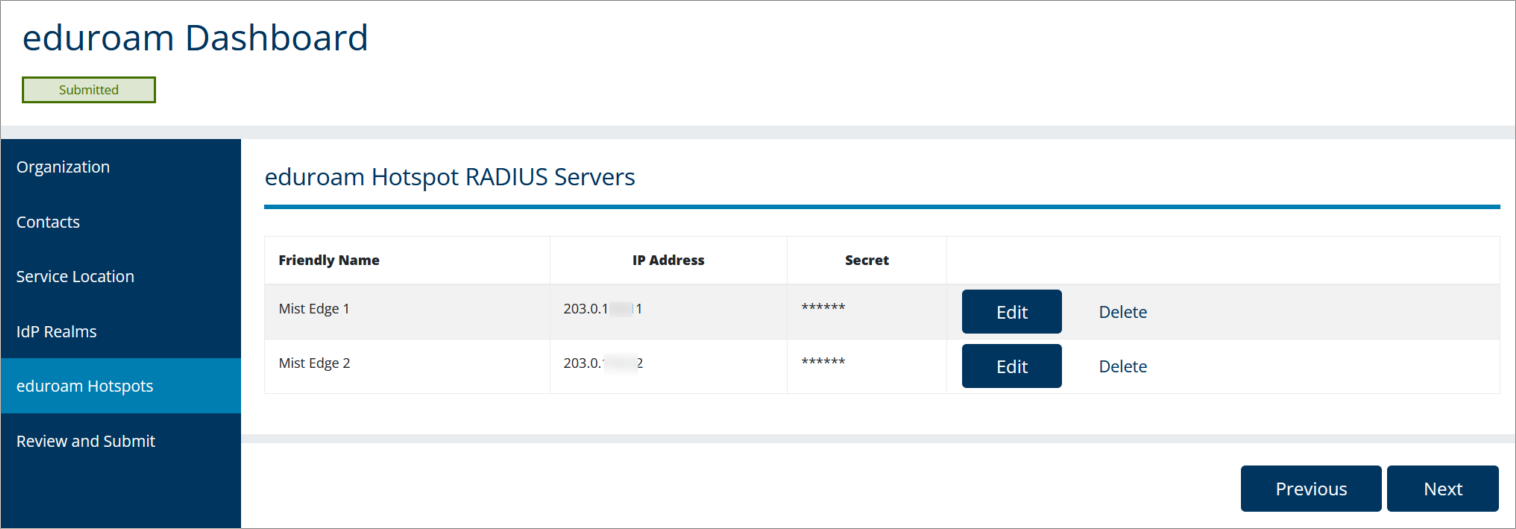
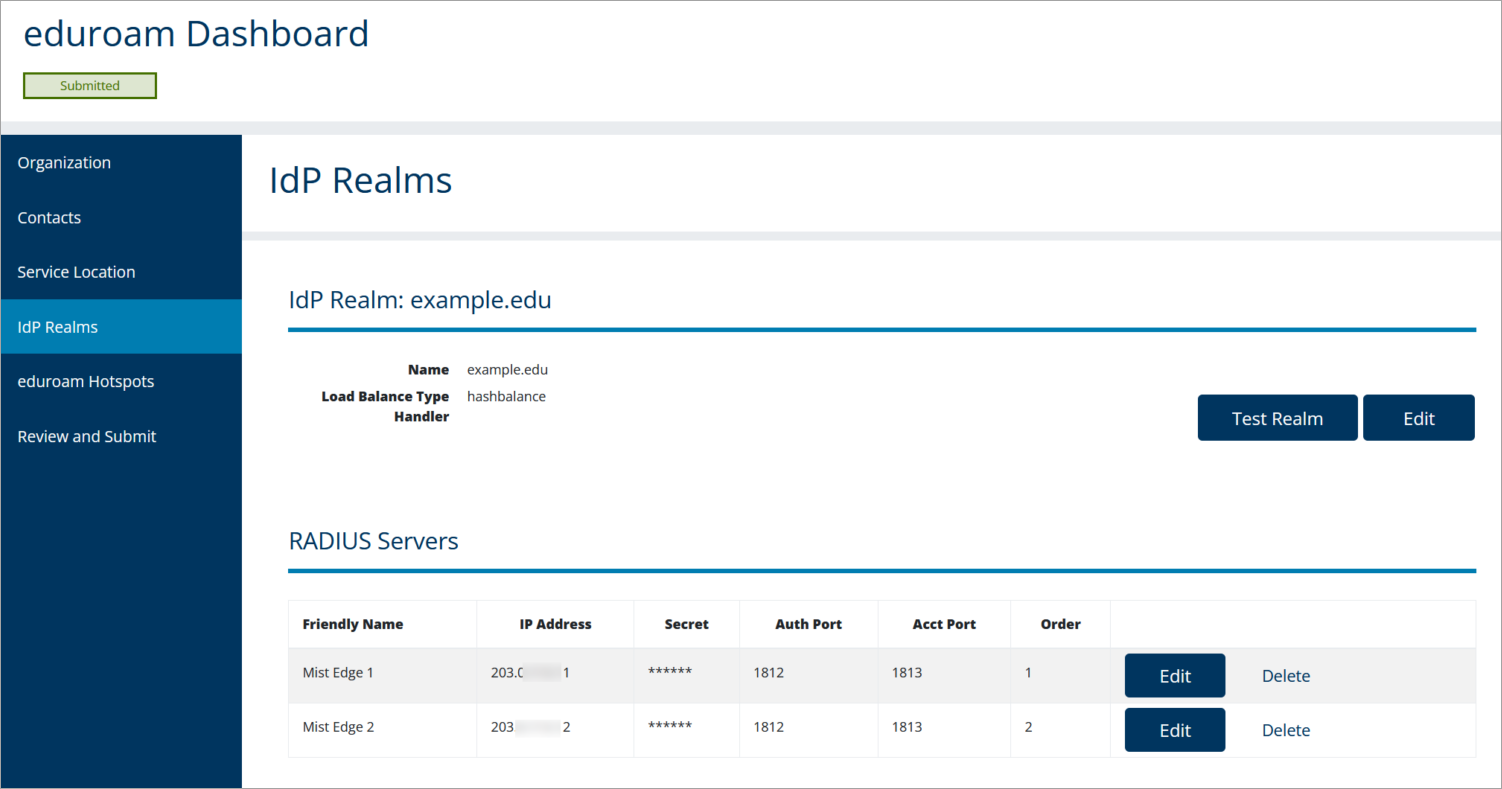
eduroam管理コンソールで、Mist Edgeを追加します。eduroam NROによっては、管理コンソールの外観が異なる場合がありますが、全体的な統合ポイントは変わりません。
EduroamホットスポットRADIUSサーバー
Eduroam IdPレルム
検証
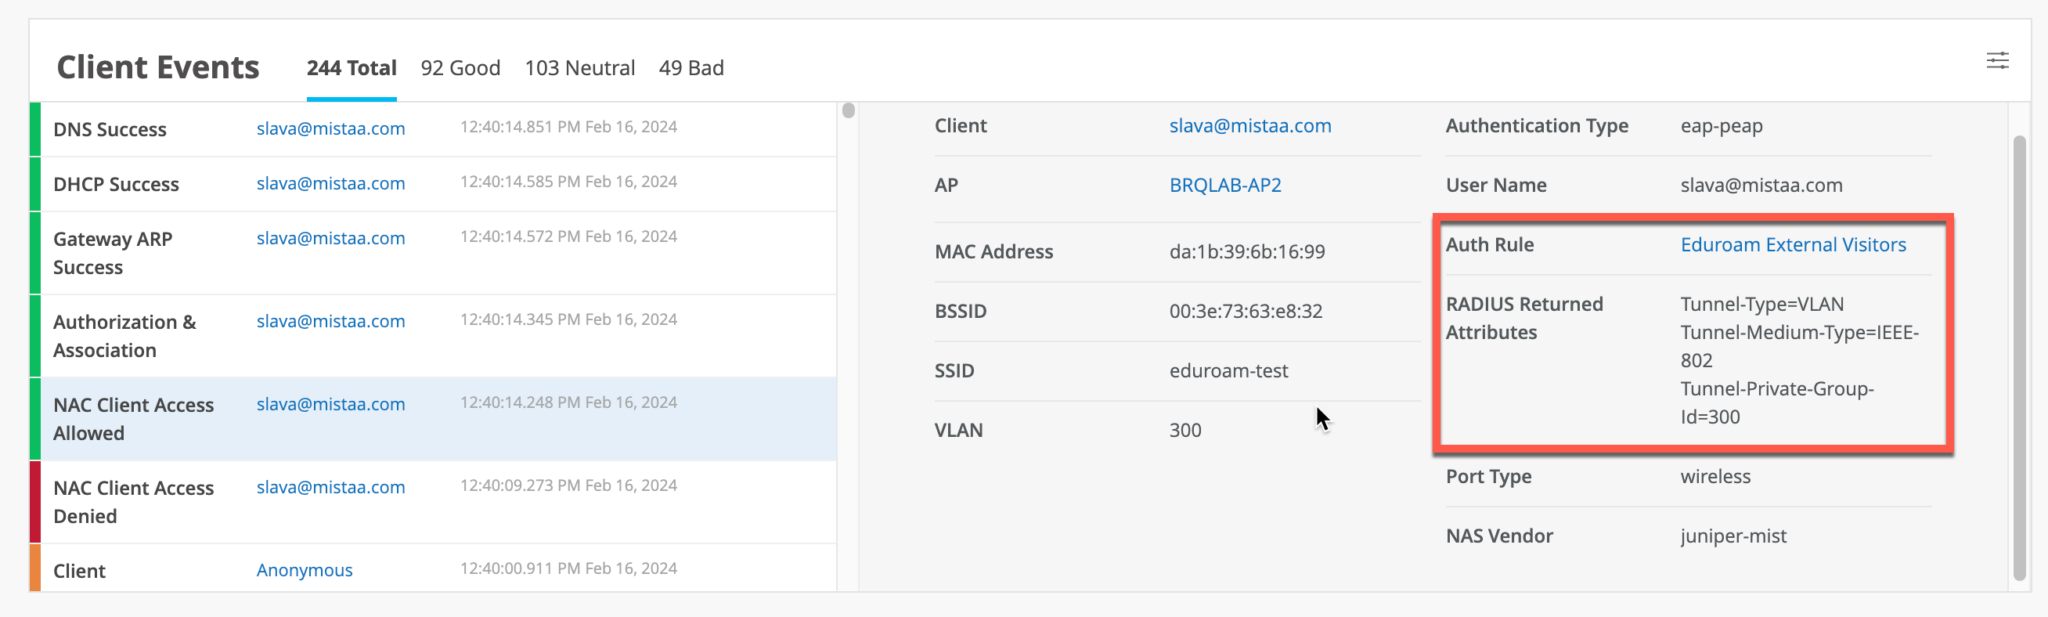
構成を確認するには、クライアントインサイトページまたは認証ポリシーページのNACイベントでイベントを確認します。
外部ユーザーの場合のみ、外部のRADIUSサーバー(eduroam)によって認証が処理されるため、他のNACイベントなしでNACクライアントアクセスが許可または拒否されたイベントが生成されます。
トラブルシューティングのヒント: 期待通りの結果が得られない場合は、ファイアウォールの設定を確認してください。必要なポートと宛先をすべて開いていることを確認します。