
資格情報ベースの(EAP-TTLS)認証を設定する
資格情報ベースの認証でネットワークを保護するには、次の手順に従って証明書をインポートし、認証ポリシーを作成し、EAP-TTLS(802.1X)認証を使用するようにポートプロファイルを更新します。
Extensible Authentication Protocol–Tunneled TLS(EAP-TTLS) クライアント側でユーザー名とパスワードを使用し、サーバー側でサーバー証明書を使用して安全なアクセスを提供します。
以下のタスクでは、有線クライアントの EAP-TTLS を設定する方法を示します。これらの認証方法は、IDプロバイダ(IdP)に保存されている資格情報を使用して、ユーザー名とパスワードを検証します。
前提条件
-
IDプロバイダ(IdP)をジュニパーMistポータルと統合して設定する必要があります。「 ジュニパー Mist Access Assurance の ID プロバイダの追加」を参照してください。
-
クライアントデバイスをサプリカントとして設定する必要があります。この設定では、エンタープライズ公開鍵基盤(PKI)のルート認証機関(CA)証明書を追加し、IdPにユーザー名とパスワードを入力する必要があります。
-
無線クライアント認証(クライアント固有のタスク無線)を実行するには、ジュニパーアクセスポイントが必要です。
-
クラウド RADIUS サーバーが使用するパブリックまたはプライベートのエンタープライズ TLS サーバー証明書を設定する必要があります。
Azure IdP 統合を使用して資格ベース (EAP-TTLS) 認証を構成する方法については、次のビデオをご覧ください。
Now, what else could we do with an IDP? We've already established that if we are using certificates or tell us to authenticate, we could use IDP and an additional source of information or context about the user. So namely, group memberships. Now, what about the authenticating users themselves without certificates?
What about authenticating users using usernames and passwords? We could leverage the existing connector with Azure to do EAP-TTLS authentication. With EAP-TTLS, the clients are using usernames and passwords to authenticate, as opposed to client certificates. So we can create another rule. We could say we are matching on the wireless user that is using TTLS instead of TLS.
And let's also match on the employee group. Why not? So we'll call it credential authentication - no - show authentication employees. Now, we will assign them to corporate VLAN. We'll hit Save. One thing we need to make sure that on the Azure portal on the app that we've created previously, there's one requirement for password authentication to work, you'll need to enable public client flows. Just click yes right here under authentication. You'll hit save.
And now we can go and check our client device. Let's take a look at the Windows device, how we can configure a Windows device to use TTLS. So we'll connect to mist-secure-net SSID. We'll be immediately prompted by the system to provide our username and password. So I'm going to give my full username and password. The important piece is to provide the full domain name - microsoft.com.
This is how the access assurance will find out which identity provider to talk to based on the domain name after the user. So click OK. Ask us to connect. And we're not connected using username and password. Now, let's take a look at our client events.
Let's look at the client insights. What we're seeing here is a slightly different flow because we are using usernames and passwords, we are not dealing with client certificates here. But the client is still trust in the server certificate. That's mutual trust is still there.
Now, we are going immediately to the identity provider to do the authentication to validate the credentials of that specific user. Now, after this phase is successful, we'll go ahead and look up all the user groups, the user roles from Azure, and finally we are matching on a specific authentication policy rule which we've just created to match on our new condition when clients are using TTLS.
有線ネットワークの認証情報ベース(EAP-TTLS)認証の設定
ジュニパー Mistポータルを使用して有線ネットワークの証明書ベースの認証を設定するには:
- 信頼できるルート認証機関(CA)をインポートします。ジュニパー Mist は、認証機関(CA)が生成した証明書をサーバー証明書として使用します。詳細については、「 デジタル証明書の使用」 を参照してください。
- 認証ポリシーを作成します。
- スイッチを設定します。
- 接続された有線クライアントがネットワークアクセスを必要とするスイッチの各ポートにポートプロファイルを割り当てます。
ポート設定タブのスイッチ設定の選択セクションで、ポート範囲を追加をクリックして、ポートプロファイルをポートに関連付けます。
図1:スイッチのポート範囲にポートプロファイルを割り当てる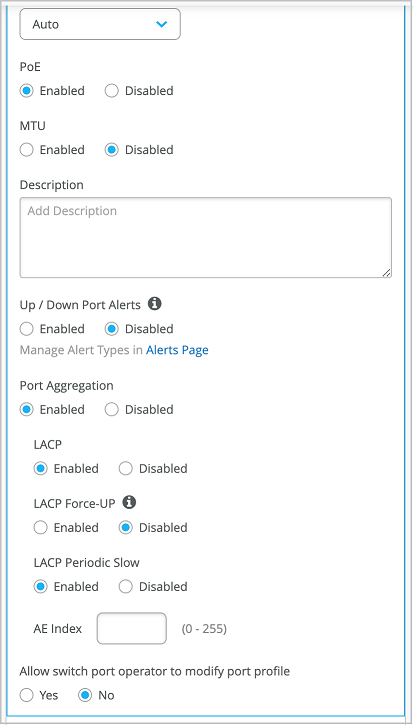
- 接続された有線クライアントがネットワークアクセスを必要とするスイッチの各ポートにポートプロファイルを割り当てます。
これで、ネットワークはEAP-TTLSを使用してクライアントを安全に認証できます。
認証ポリシーにより、有効なユーザー名とパスワードを持つクライアントがネットワークにアクセスできます。
ジュニパーMistクラウドは、公開資格プロバイダーに保存されている資格情報とユーザー名とパスワードを検証し、 ラベル設定に基づいてアクセスと資格を付与します。
関連するクライアントは、ジュニパー Mistポータルで確認できます。
- クライアント>有線クライアントを選択して、クライアントの詳細を表示します。
- クライアントイベントを表示するには、監視 >サービスレベル>インサイト を選択します。