Help us improve your experience.

Let us know what you think.

Do you have time for a two-minute survey?


Create API Tokens

Create tokens to provide authentication for your APIs.

API tokens contain authentication information and are bound to specific users or an entire organization. API tokens send identification information about the user or organization to the API server to indicate whether or not the user has access to the API, to ensure security.

Like many other API providers, Juniper Mist offers a way to generate API tokens for authentication (in the HTTP header). When considering tokens, Juniper Mist uses the terms token and key interchangeably.

Attention: To enhance security and align with industry best practices, Mist has deprecated Basic Authentication for all use cases—including admin logins and scripts—effective September 2026. Before September 2026, all integrations should have transitioned to token-based authentication to ensure uninterrupted access and support. See Create API Tokens.
In Juniper Mist, there are two types of API tokens:
  • Organization Token

    Organization tokens are useful when you are building an application that automates work for your organization. Multiple users would need to access the application and thus would use the same organization token for authentication.

    • The token persists under the Mist organization.
    • The token is not bound to any specific user, meaning the access does not depend upon any user’s access to the organization.
    • Supports N org tokens, which can have different privileges.
    • The token can only be used for that specific organization.
    • Rate limiting is done by the individual token. For example, if OrgToken1 consumes 5000 API calls and reaches the rate limit, OrgToken2 is not impacted.
  • User Token

    User tokens are useful when you need to authenticate for yourself, like when running a script, for example.

    • The API token assumes the same privileges as the assigned user’s account privileges.

    • The token is bound to the specific user, meaning the access directly correlates to the user’s access to the organization.
    • The token can be used for any Managed Service Provider (MSP) or organization that the user has access to.
    • Supports N tokens, which all have the same privilege as the user account.
    • Rate limiting is done by the account that is tied to the user. For example, if UserToken1 consumes 5000 API calls and reaches the rate limit, UserToken2 AND account log in to the GUI are impacted.

You can create API tokens through the Mist Portal or REST API Explorer.

Create an Organization Token in the Mist Portal

  1. From the left menu of the Juniper Mist portal, select Organization > Admin > Settings.
  2. Scroll down to the API Token section and click Create Token.
  3. Select an Access Level to define the permissions for the token.
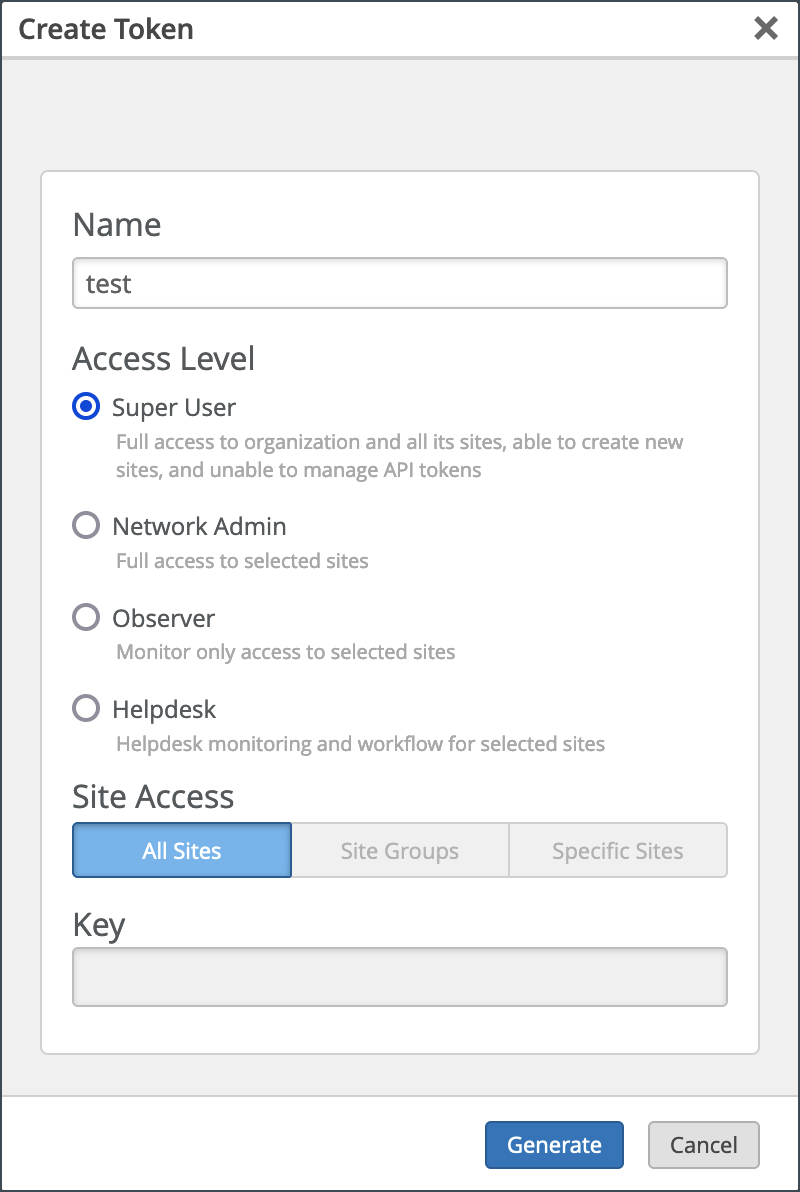
    Create Token interface with Name field containing 'test', Super User access selected, All Sites tab selected, empty Key field, and Generate and Cancel buttons.

  4. Click Generate.
  5. Click the copy button next to the Key field and store it somewhere for safekeeping.
    Note:

    The only time you will see the entire, untruncated key is upon creation. You will not be able to see the full key ever again. If you misplace the key, you will have to create a new key.
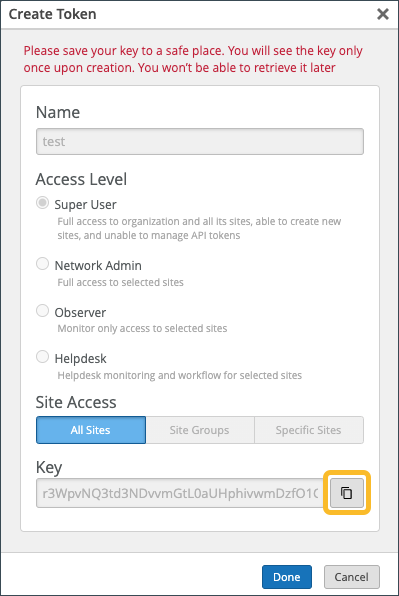
    Create Token interface with fields for token name, access level options, site access scope, generated token key with copy button, and Done and Cancel buttons. Warning to save key securely.

  6. Click Done at the bottom of the window.
  7. Click Save near the top-right corner of the page.

Create a User Token in the Mist Portal

You can generate an API user token from the My Account page in the Mist portal.

To generate an API user token:

  1. At the top-right corner of the Juniper Mist portal, click the Juniper Mist Account icon, and then click My Account.
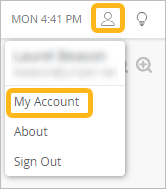
    User interface menu for account management with timestamp MON 4:41 PM, highlighted user profile icon, and dropdown options My Account highlighted in yellow, About, and Sign Out.
  2. In the API Token section, click Create Token. If you have enabled single sign-on for your organization, you will not be able to create API user tokens.
  3. Enter a name for the token and click Generate. The generated key is the user API token.
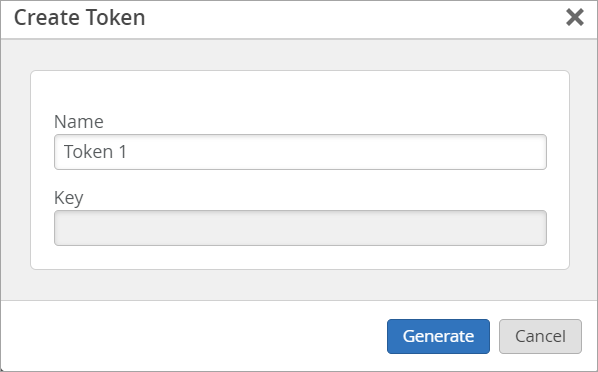
    Create Token dialog box with Name field pre-filled as Token 1, empty Key field, and buttons Generate and Cancel.
  4. Click the copy button next to the Key field.
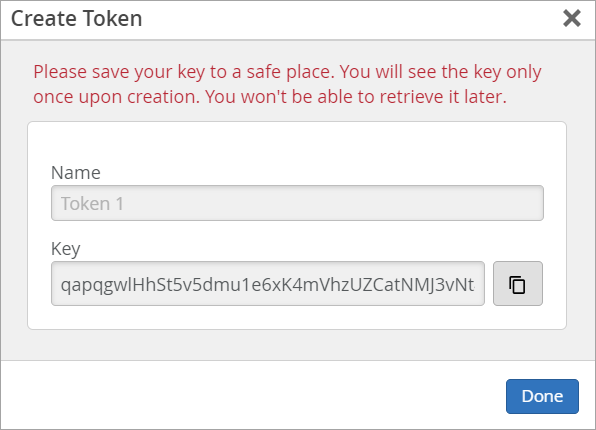
    Create Token dialog box with a warning to save the key securely. Name field with Token 1 entered, Key field showing a string of characters, copy button next to the key, and Done button at the bottom.

    Ensure to store the key somewhere for safekeeping as you will not be able to see the full key again. If you misplace the key, you’ll need to create a new key.

  5. Click Done.
    Note:

    If you need to delete a user token, click the token in the API Token section of the My Profile page, and then click Delete in the Edit Token page.
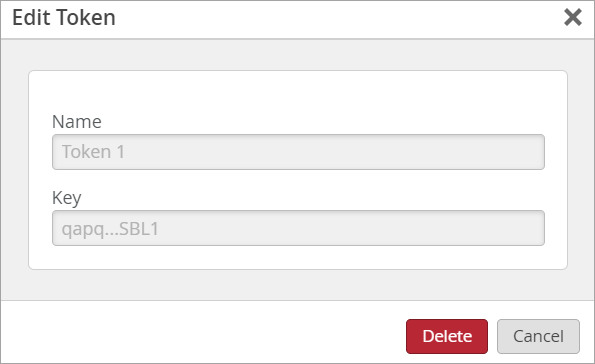
    Edit Token dialog with fields for Name and Key. Name field shows Token 1. Key field displays partially hidden value starting with qapq and ending with SBL1. Buttons: red Delete and gray Cancel.

Create a User or Organization Token Using the REST API Explorer

  1. Log in to the Juniper Mist portal.
    Note:

    You must be logged into the portal to use the REST API Explorer.

  2. Open a new browser window and paste your URL: {api-host}/api/v1/self/apitokens.
    Note:

    In place of {api-host}, you need to use the API endpoint for your global region. See API Endpoints and Global Regions.

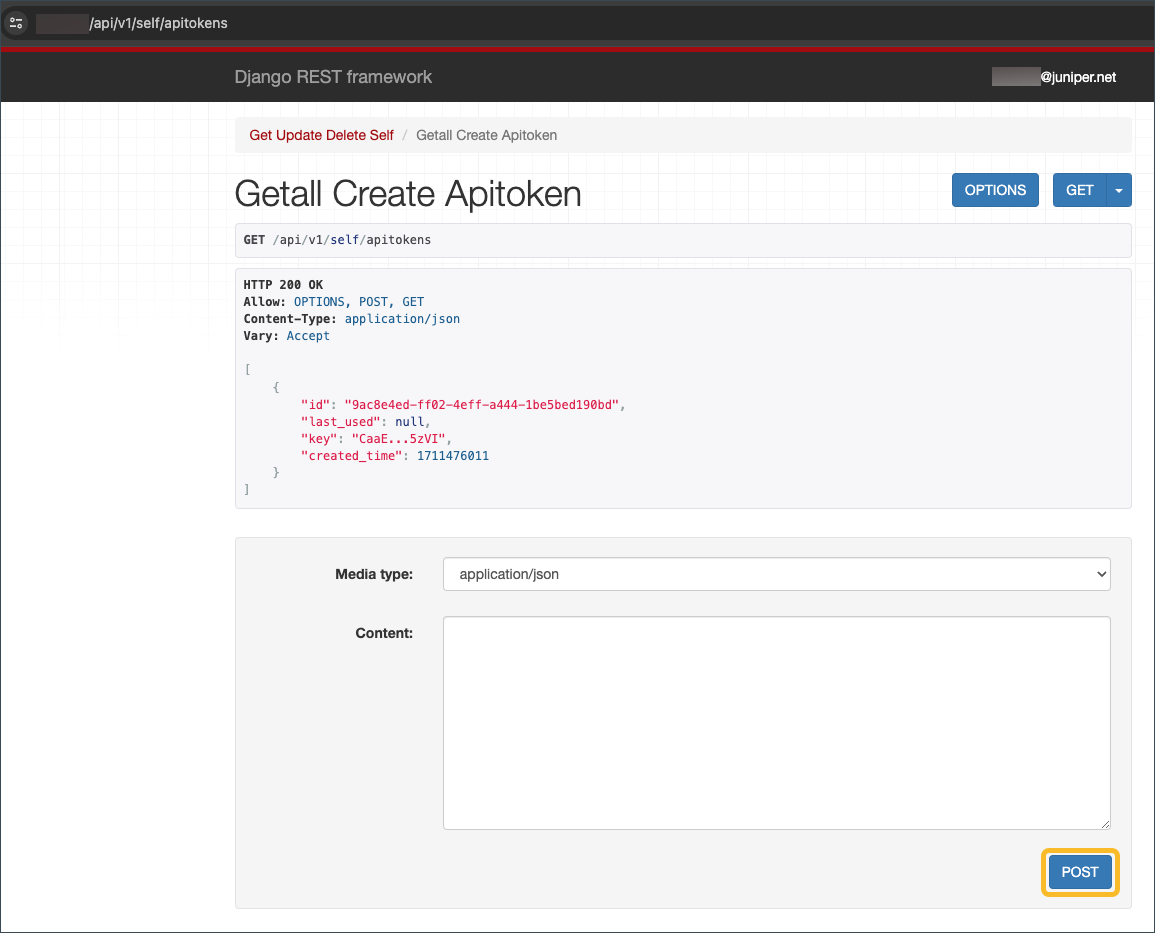
    The REST API Explorer is the API page for token control. Here you can create, read, update, and delete tokens and token information. This page initially displays the tokens that you have already created.

    This page also enables you and other users to make an API call directly from the browser. With Media type: applications/json already selected as the default, a GET request will be performed to show you a list of your tokens. A truncated key will display for any previously created tokens.

  3. Click POST.

    Django REST framework interface for managing API tokens, showing endpoint details, supported HTTP methods, and JSON response fields like id, last_used, key, and created_time.

    The response will be similar to this example:

  4. Copy the key (token) and store it for safekeeping.
    Note:

    The Juniper Mist API will never again display the actual token (key) in full, anywhere, after creating the key. After you navigate away from this page and come back, the key will appear but in a truncated version. You should treat this key as a password and store it in a safe place. If you lose this key, you will need to create a new one.

    Note:

    If you plan to share Python scripts with others, be sure not to store your API token in the script itself and use an environment file (.mist_env) in its place. Environment files store sensitive information in the script for you, so you don’t have to share your sensitive information directly in your script. For more information, see https://github.com/tmunzer/mist_library?tab=readme-ov-file#environment-file.