Help us improve your experience.

Let us know what you think.

Do you have time for a two-minute survey?


WindowsデバイスのEAP-TEAP認証を設定する

ネットワークを保護するために、次の手順に従って、EAP-TEAP(Tunneled Extensible Authentication Protocol)認証用にクライアントデバイスを構成します。

トンネル拡張認証プロトコル(TEAP)は、トランスポート層 セキュリティ(TLS)プロトコルを使用して相互に認証されたトンネルを確立することにより、ピアとサーバー間の安全な通信を可能にするトンネルベースのEAP方式です。トンネル内では、TLV オブジェクトを使用して、EAP ピアと EAP サーバーの間で認証関連データを伝達します。(RFC 7170 - トンネル拡張可能な認証プロトコル )

注:

ジュニパー Mist Access Assuranceは、マシンとユーザー両方の認証の認証方法としてEAP-TLSを使用したEAP-認証をサポートします。

既定では、Windows は起動時にコンピューターを認証し、ユーザーがサインインした後にユーザーの資格情報を使用して自動的に再認証することはありません。自動ユーザー認証を有効にするには、グループポリシー、MDM、またはXMLプロファイルを介して、Wi-Fiプロファイルで無線802.1Xシングルサインオン(SSO)をログオン前またはログオン後のいずれかに設定します。SSOが有効になっていない場合、ユーザー認証は通常、無線接続を手動で切断してから再接続した後にのみ行われます。シングル サインオンプロファイルのサンプルを参照してください。

現在、TEAP サポートは Windows 10 バージョン以降で利用できます。

TEAPで無線および有線プロファイルを手動またはスクリプトで設定でき、MDMまたはGPOを使用して配布できます。現在のMDMソリューションは、TEAP設定のすぐにのサポートを提供していません。

Windowsデバイスで無線EAP-TEAPを設定するには:

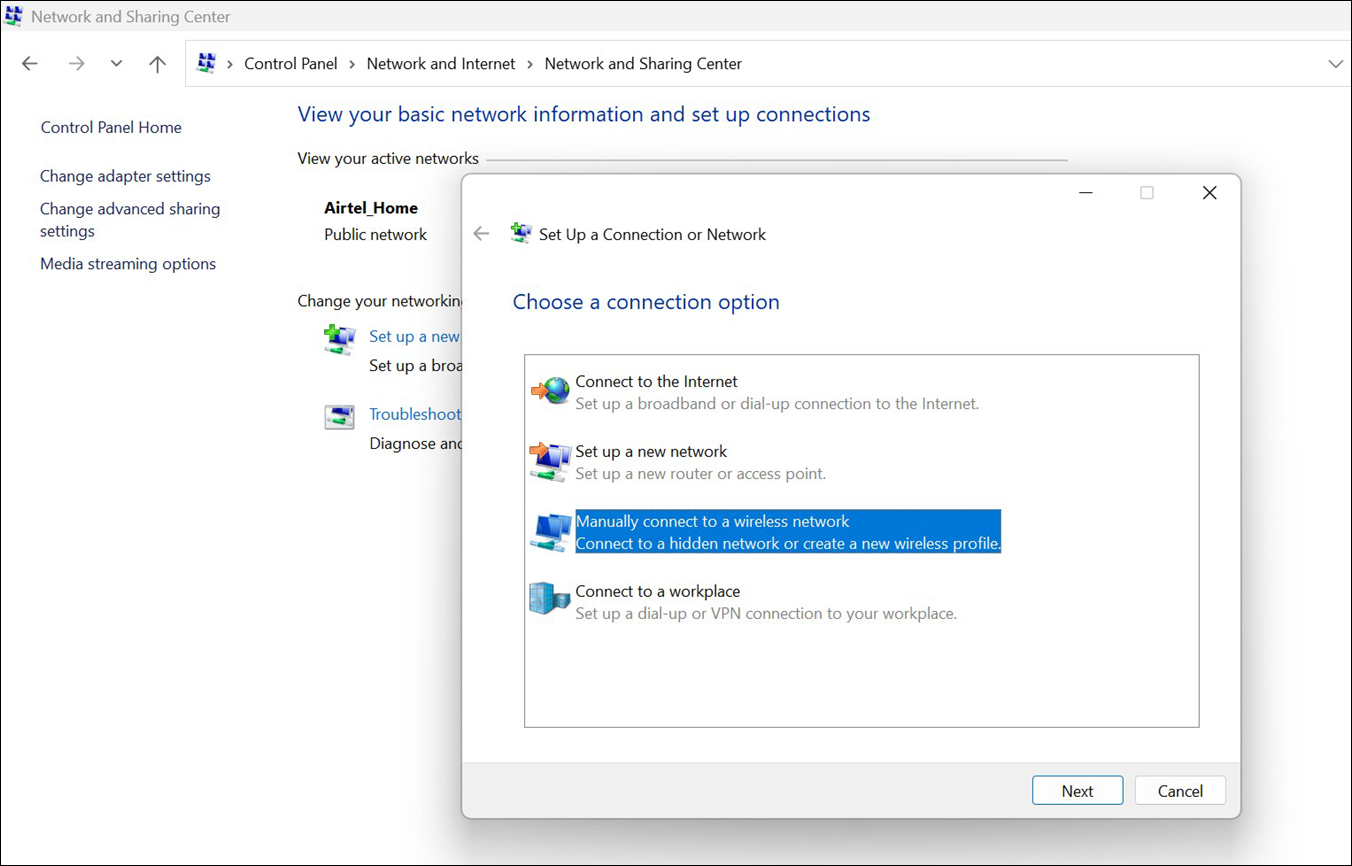
  1. Windows デバイスで、[ コントロール パネル ] > [ネットワークとインターネット >ネットワーク と共有センター] に移動します。次に、[ 新しい接続またはネットワークの設定] をクリックします。
  2. [無線ネットワークに手動で接続する]を選択し、[次へ]をクリックします。
    Network and Sharing Center displaying options for network setup. Highlighted option is Manually connect to a wireless network for connecting to hidden networks or creating new profiles.
  3. 無線ネットワークについて以下の詳細を入力し、 次へをクリックします。
    • ネットワーク名—SSID名を指定します。

    • セキュリティタイプ— WPA2-Enterprise または WPA3-Enterprise オプションを選択します。
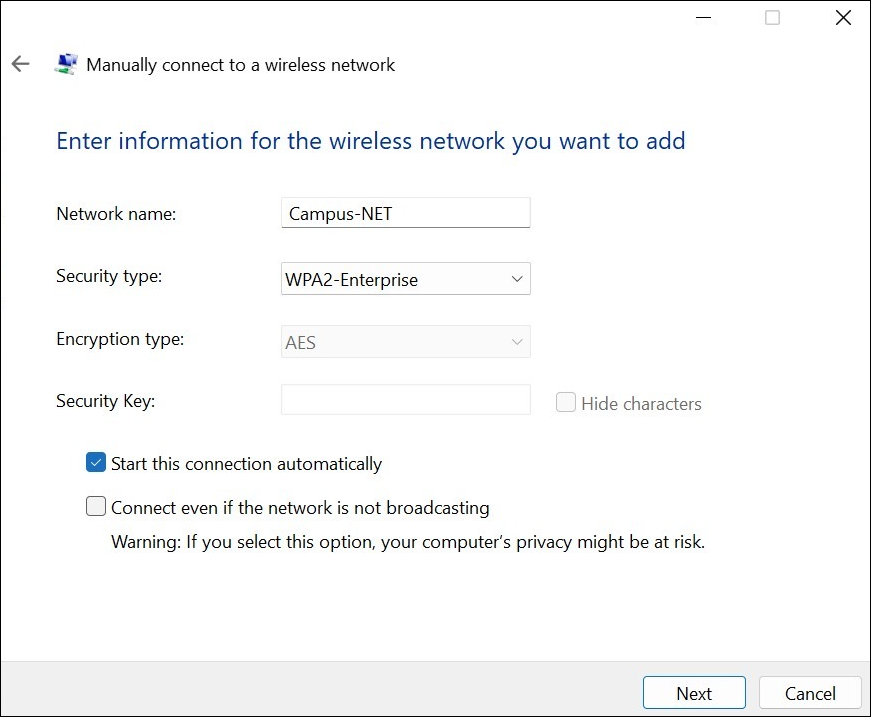
    Windows interface for manually connecting to a wireless network. Prompts for network name, security type, encryption type, and security key with options to hide characters. Includes checkboxes for automatic connection and connecting to hidden networks. Next and Cancel buttons at the bottom.

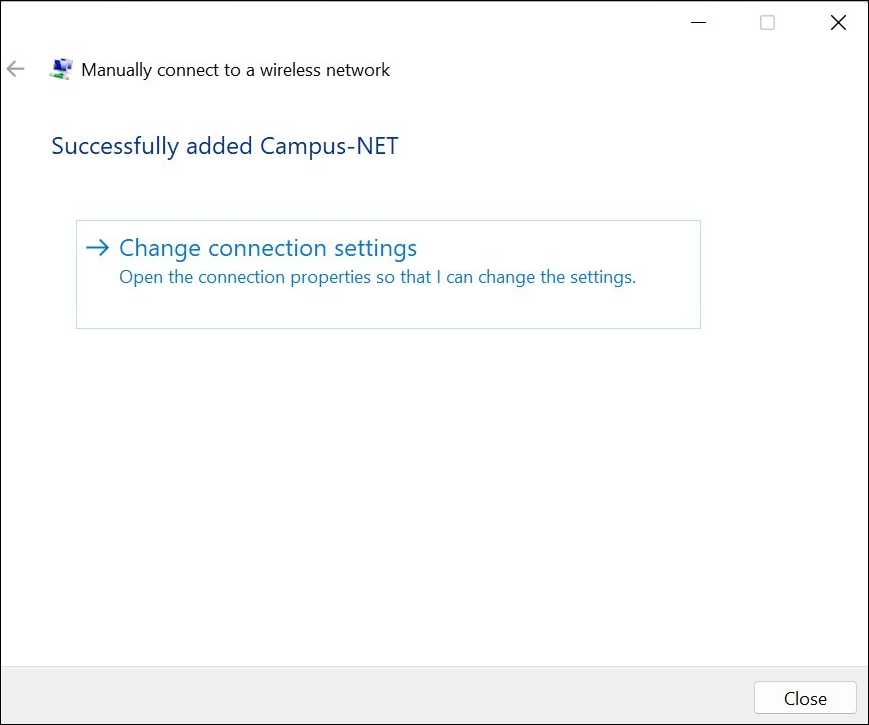
  4. 接続設定の変更をクリックします。
    Wireless network Campus-NET successfully added with options to change connection settings or close.

    [Wireless Network Properties]ダイアログボックスが表示されます。

  5. セキュリティタブを選択し、ネットワーク認証方法の選択でTEAPを選択します。次に、[設定]をクリックします。
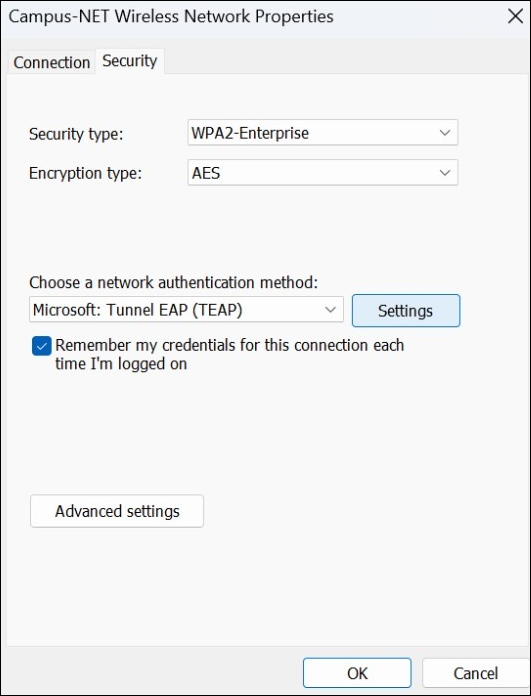
    Campus-NET Wireless Network Properties Security tab showing WPA2-Enterprise security type, AES encryption, Tunnel EAP authentication, and a checked Remember credentials option.

  6. [TEAP プロパティ] ダイアログ ボックスで次のオプションを選択します。
    • IDプライバシー—IDはデフォルトで匿名に設定されていますが、必要に応じて目的のIDに上書きできます。
    • これらのサーバーに接続—デフォルトのMist Access Assuranceサーバー証明書を使用している場合は auth.mist.com を入力します。カスタム RADIUS サーバー証明書を使用している場合は、証明書 SAN:DNS 名を指定します。
    • 信頼できるルート認証機関—Mist組織のCA証明書(またはカスタムRADIUSサーバー証明書)を選択します。
    • 認証方法—認証のプライマリおよびセカンダリEAP方法として、 Microsoft:スマートカードまたはその他の証明書(EAP-TLS) を選択します。
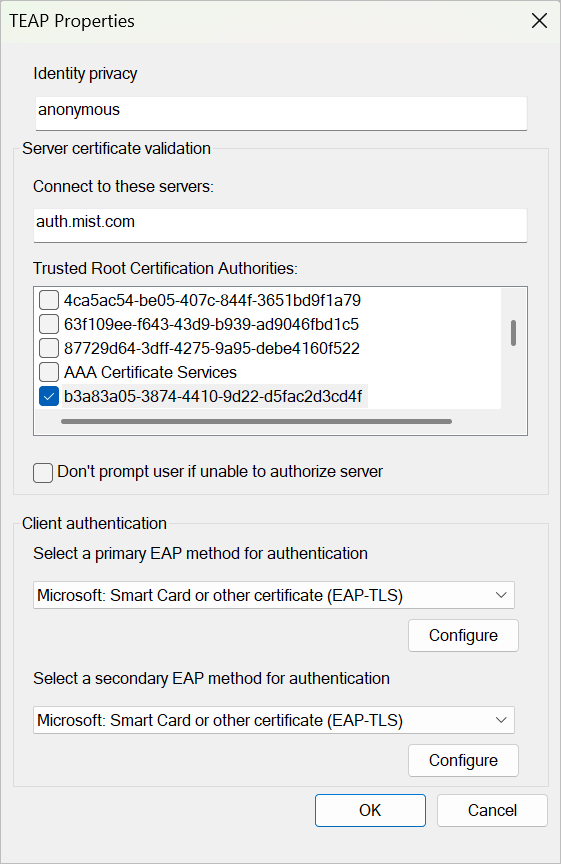
    TEAP Properties configuration window for authentication and certificate validation, including identity privacy, server certificate validation, EAP methods, and additional security options.

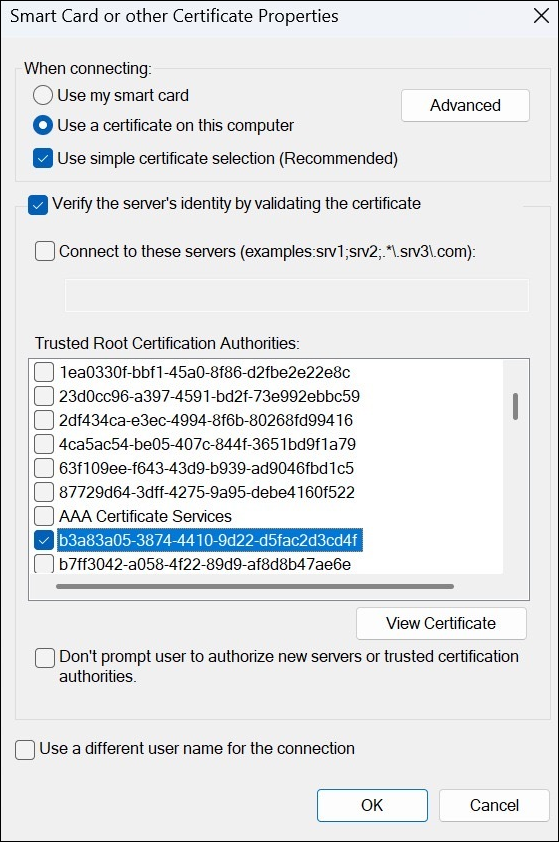
  7. プライマリとセカンダリの両方のEAP方式について 設定 をクリックします。それぞれに表示される [スマート カードまたはその他の証明書のプロパティ] ダイアログ ボックスで、次の操作を行います。
    • シンプルな 証明書選択を使用する(推奨) オプションが選択されていることを確認します。

    • クライアントがMist Access Assuranceサーバー証明書を信頼できるようにする、信頼できるルート認証機関(CA)を選択します。プライマリとセカンダリの両方のEAP方式に同じCAを選択していることを確認します

    • OKをクリックします。

    Smart Card or Certificate Properties dialog box for configuring certificate-based authentication, with options for certificate selection, server validation, and trusted authorities.

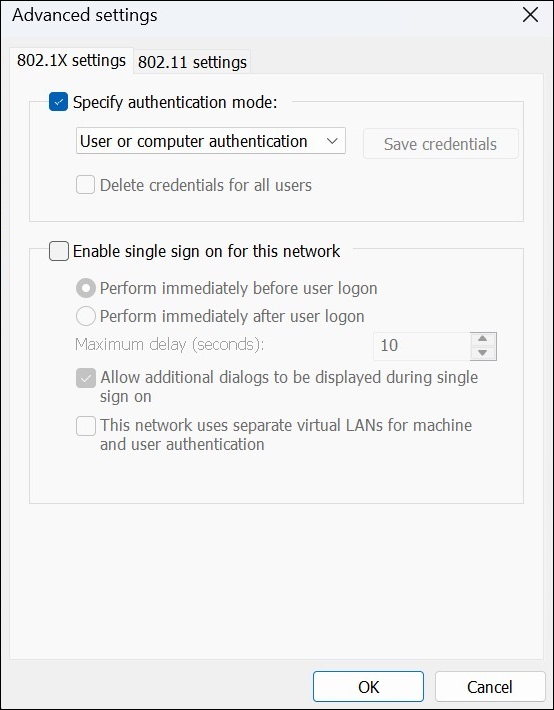
  8. [ワイヤレス ネットワークのプロパティ] ダイアログ ボックスの [セキュリティ] タブで、[ 詳細設定] をクリックします。
  9. 詳細設定ダイアログボックスで、次の操作を行います。
    1. [ 認証モードの指定 ] チェックボックスを選択し、[ユーザー] または [コンピューター認証] を選択します。
    2. OKをクリックし、閉じるをクリックします。
    Advanced settings window for configuring 802.1X and 802.11 network authentication, including authentication mode options, single sign-on settings, and OK and Cancel buttons.
  10. 設定を確認します。
    1. ジュニパー Mistポータルで、EAP-TEAPクライアント認証を許可する認証ポリシールールを設定します。
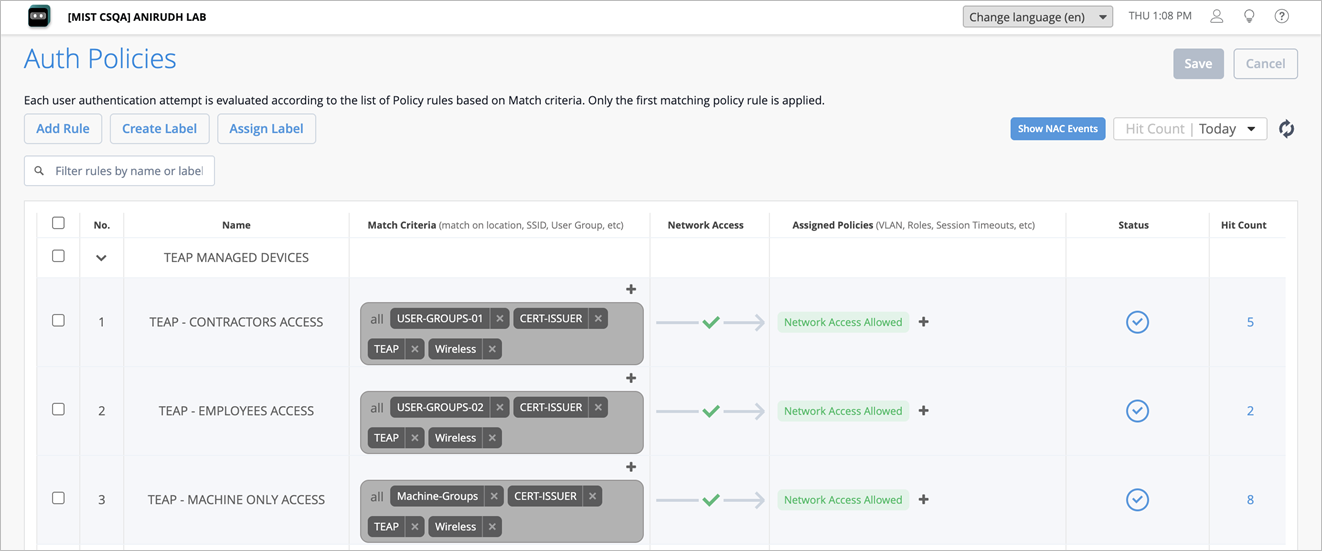
      User interface displaying authentication policies in a network system, titled Auth Policies. Includes policy names, match criteria, network access status, assigned policies, hit count, and active status indicators. Features options to add rules, create labels, assign labels, filter policies, save changes, and view NAC events.
    2. CA証明書を追加して、ジュニパー Mist Access Assuranceが、追加したCAによって発行されたクライアント証明書を信頼できるようにします。証明書を追加するには、組織>アクセス>証明書に移動します>認証局の追加ページ。CA証明書を追加する詳細な手順については、「認証機関(CA)証明書を使用する」を参照してください。
    3. クライアントデバイスをネットワークに接続します。
    4. 認証ポリシーページで NACイベントを表示 をクリックし、NACクライアント認証イベントを確認します。

      また、インサイトページ(監視>サービスレベル>インサイト)でNACクライアントを選択して、NACクライアント認証イベントを表示することもできます。

      次の例は、マシン証明書のみを使用してEAP-TEAPを介して認証したクライアントを示しています。
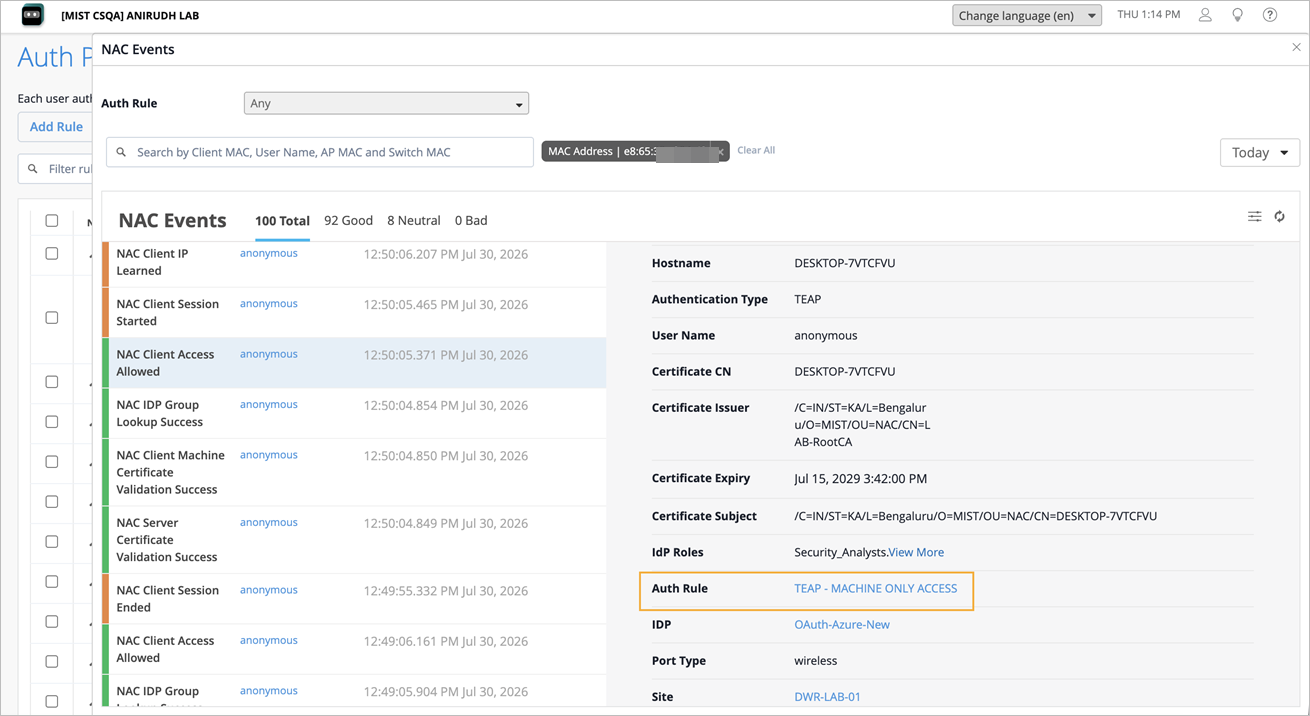
      Network access control events log showing authentication details, event categories Good, Neutral, Bad, filters, search options, and summary of 100 events.

      次の例は、ユーザーがログオンした後にEAP-TEAPを介して認証し、マシン証明書とユーザー証明書の両方の検証に成功したクライアントを示しています。
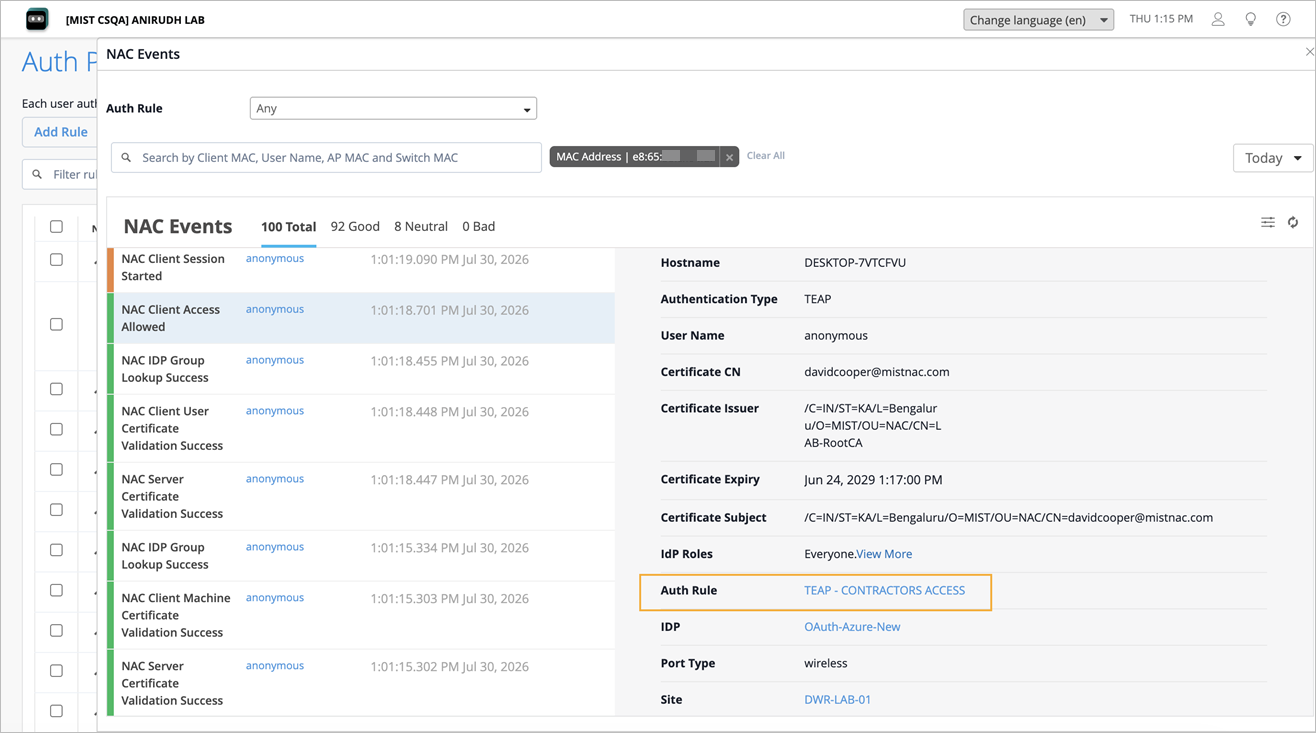
      NAC events log showing authentication details for a user or device, including timestamps, statuses, hostname, authentication type, certificate info, roles, and site.