Help us improve your experience.

Let us know what you think.

Do you have time for a two-minute survey?


Integrate Splunk with Mist Webhooks

Follow these instructions to configure Splunk and to set up webhooks from Juniper Mist™ to your Splunk instance.

Splunk uses HTTP Event Collection (HEC) to receive HTTP POST requests that include a payload of data. This enables cloud services like Mist to send data to Splunk using webhooks.

How you implement HEC depends on your Splunk service:

  • If you're running a managed Splunk Cloud, you'll need to raise a ticket with your Splunk support to have HEC configured.

  • If you have self-service Splunk or Splunk Enterprise (on-premise), you can use the following instructions to configure HEC to receive webhooks from Mist.

Configuring HEC in Splunk

Before you begin: Webhooks requires IP reachability from the Mist Cloud to your Splunk instance. In other words, you need a publicly accessible URL for your Splunk server with the HTTP port open.

  1. In your Splunk GUI, go to Settings > Data Inputs.
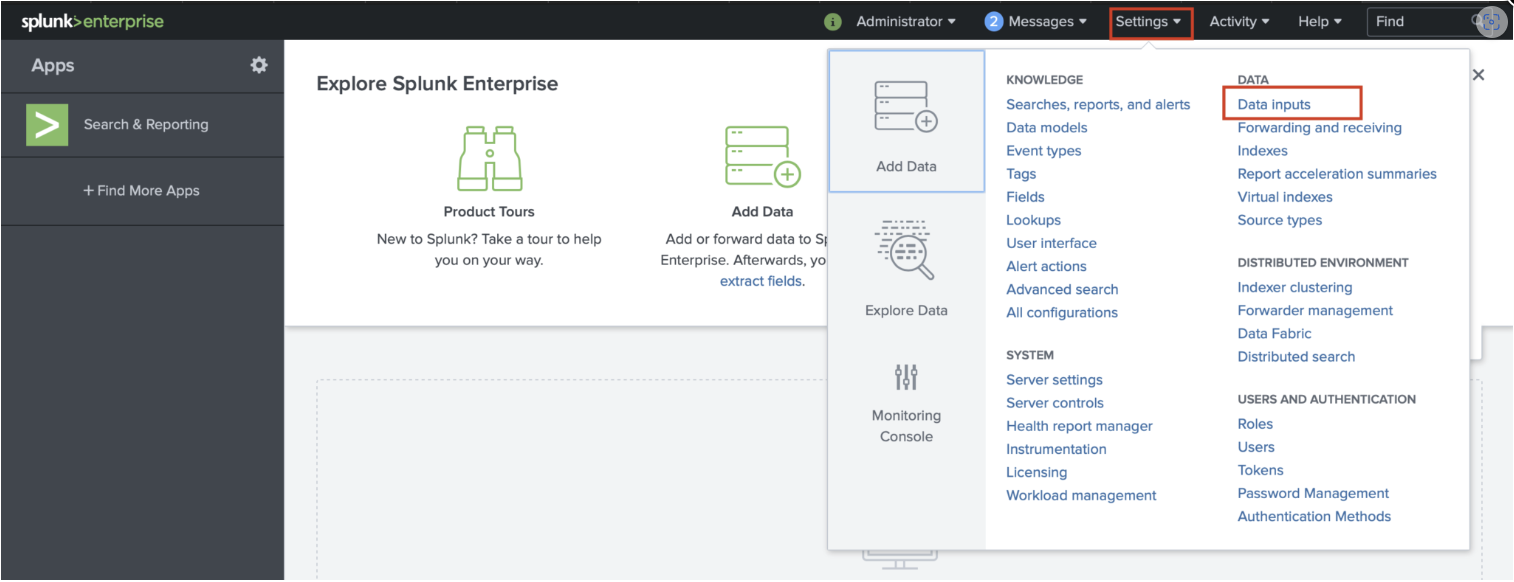
    Splunk Enterprise interface showing navigation options, a welcome screen with guides like Product Tours and Add Data, and a highlighted Data inputs option under Settings.
  2. Go to HTTP Event Collector > Add New.
  3. Provide a Name and Source Name Override.

    If your organization uses Splunk Output Groups, select the appropriate output group. Otherwise, ignore the Output Group selection.
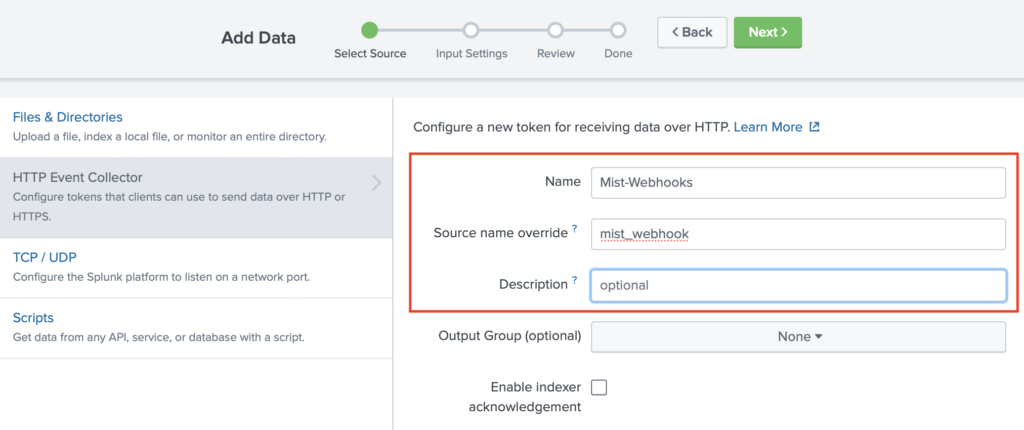
    Configuration screen for adding data in Splunk via HTTP Event Collector. Fields include name, source name override, description, output group, and indexer acknowledgment checkbox. Navigation includes steps: Select Source, Input Settings, Review, and Done, with Back and Next buttons.
  4. Click Next.
  5. Configure the following fields:
    1. For the Source type, click the Select button, hover over Structured, and select _json from the list.
    2. Create a new Index and name it network. For the Index Data Type, choose Metrics, and for the App, choose Search & Reporting.
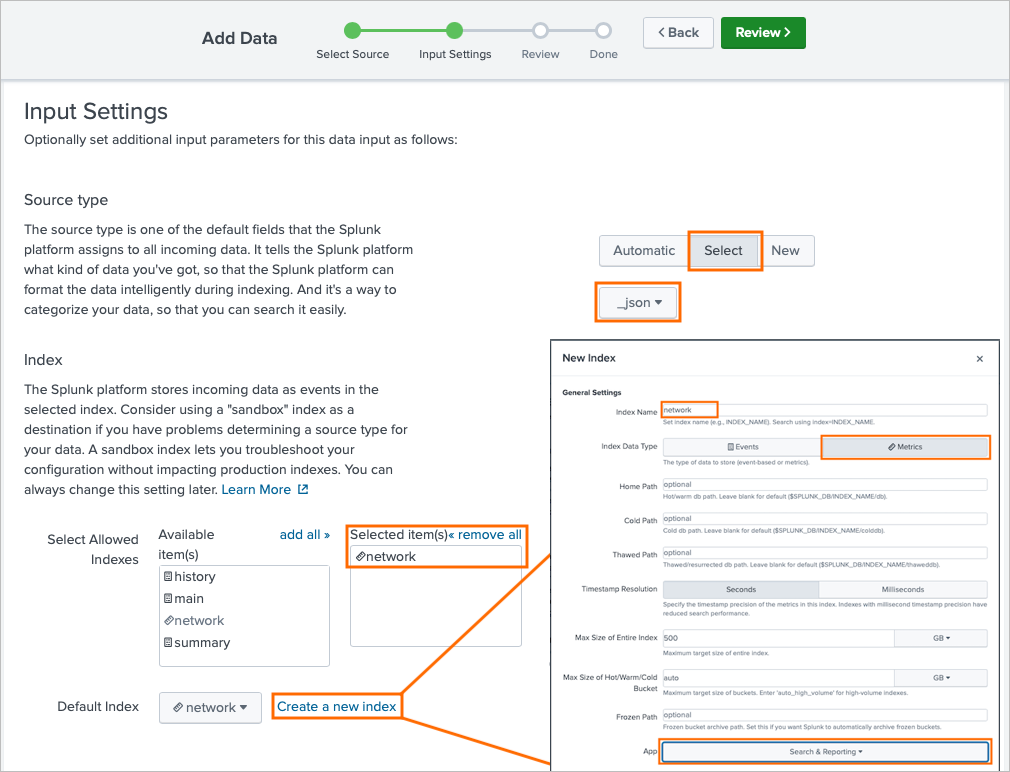
      Configure input settings in Splunk Add Data process, including source type, index creation, storage paths, timestamp resolution, and data size limits. Navigate steps at top.
    Once you Save the new index, click it from the Available item(s) list and it will appear in the Selected item(s) list.
  6. Click Review.
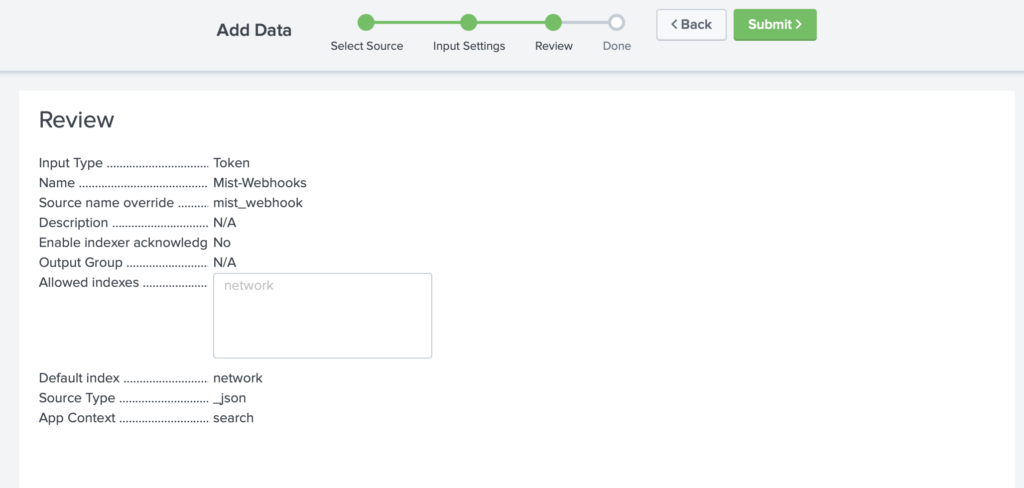
  7. Verify the settings and click Submit.
    User interface showing the Review step for adding data with fields for Input Type, Name, Source name override, Description, Enable indexer acknowledgment, Output Group, Allowed indexes, Default index, Source Type, and App Context. Progress bar indicates Review step with options to go Back or Submit.
  8. Record the Token Value. You will need this for the Mist Webhook configuration.
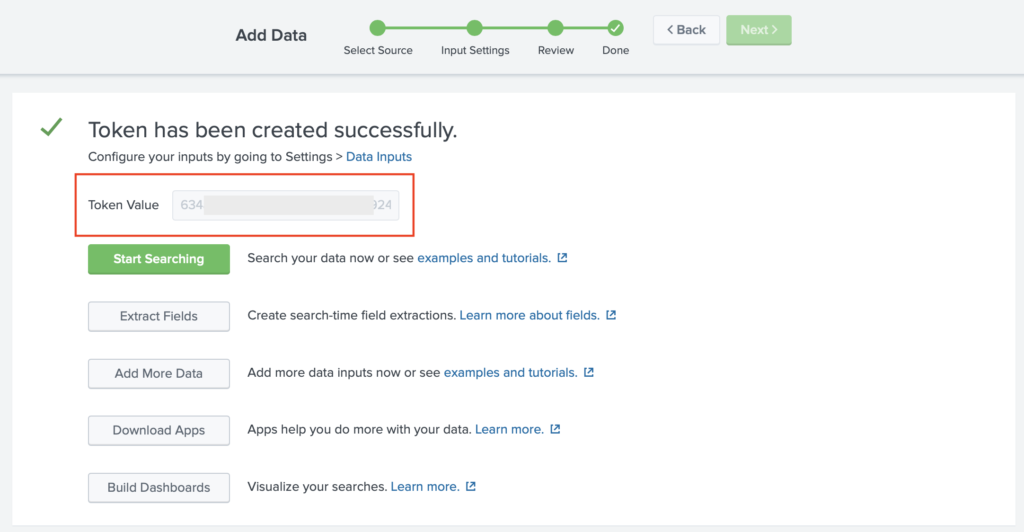
    User interface showing a completed token creation process with options to start searching, extract fields, add more data, download apps, and build dashboards. Progress bar indicates all steps are complete.
  9. Navigate back to Settings } Data Inputs } HTTP Event Collector.
  10. Click Global Settings in the upper right corner.
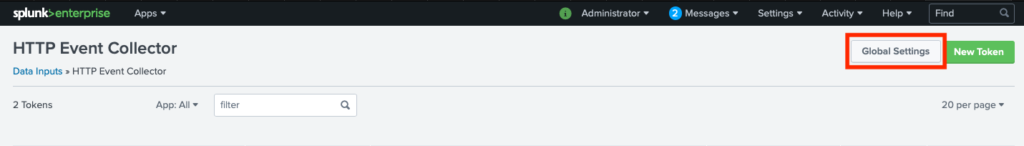
    HTTP Event Collector configuration page in Splunk Enterprise showing global settings, new token creation, token list with search and filter options, and pagination controls.
  11. Specify the default Source type as _json.

    Port 8088 is the default. You can specify a default index if needed.
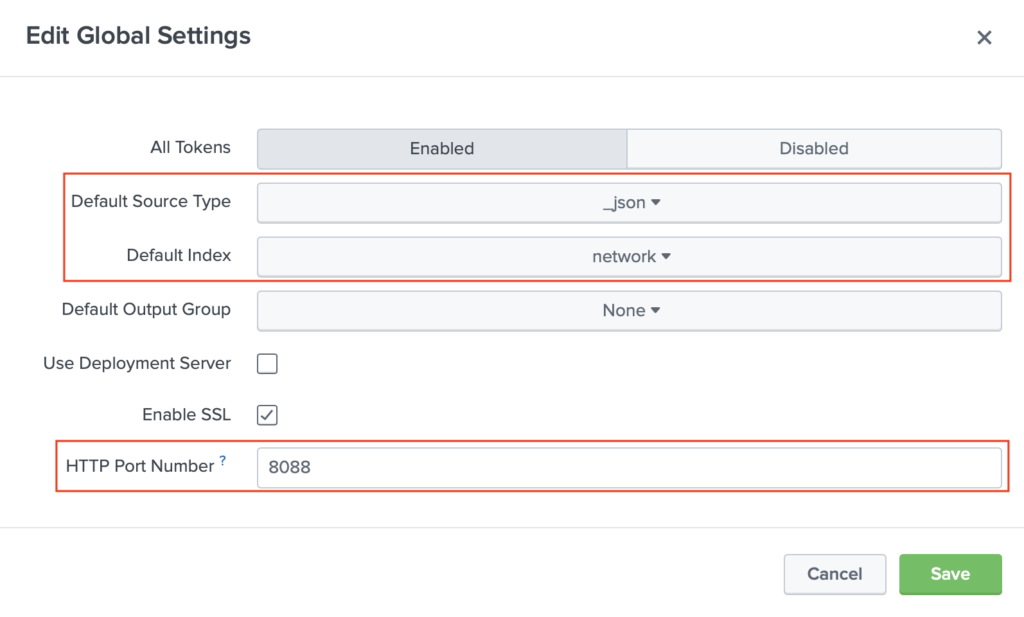
    Edit Global Settings interface with fields for configuring parameters: toggle for All Tokens, dropdowns for Default Source Type, Default Index, and Default Output Group, unchecked Use Deployment Server checkbox, checked Enable SSL checkbox, HTTP Port Number set to 8088, and Cancel and Save buttons.
    This completes the HEC setup in Splunk.
  12. Test the Splunk HEC configuration by executing the following command in a Linux CLI. The Linux machine must be able to reach the Splunk instance over the network.

The result of the previous step should look similar to: {“text”:”Success”,”code”:0}. If you do not see a success message, confirm that there are no firewalls blocking the HEC port on the Splunk instance.

Configuring Mist Webhooks to Point to Your Splunk Instance

Before you Begin

You must have the following information ready so that you can complete the Mist configuration:

  • The FQDN of your Splunk HEC instance
  • The port number HEC is listening on (Default is 8088)
  • Your Splunk HEC Token

You can configure webhooks in Mist at either the Org level, or the Site level. For this example, we configure an Org level webhook and the topics we will be subscribing to will be “audits”, “alarms”, and “device-events”.

  1. Log in to the Mist portal for your organization.
  2. Navigate to Organization } Settings and copy your Organization ID.
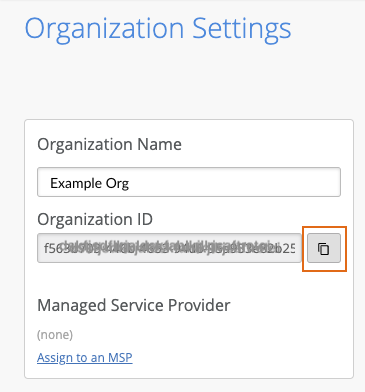
    Organization Settings page showing fields: Organization Name as Example Org, Organization ID partially blurred with copy icon, Managed Service Provider set to none with option to assign.
  3. Navigate to https://api.mist.com/api/v1/orgs/:org_id/webhooks.
    Note:

    You must substitute your real Organization ID for "org_id" in the URL above.

  4. In the following JSON code block, make the following substitutions:
    • Substitute the fully qualified domain name (FQDN) of your Splunk instance for {FQDN of SPLUNK}

    • Substitute the port on which your Splunk instance is listening for {PORT}

    • Substitute your actual Splunk token for {SPLUNK TOKEN}

    Note: Replace placeholder values with actual values, such as your FQDN, port, and token.
  5. After substitution, copy the entire block of JSON and paste it into the Content box at the bottom of the page.
  6. Click the POST button when you're ready.
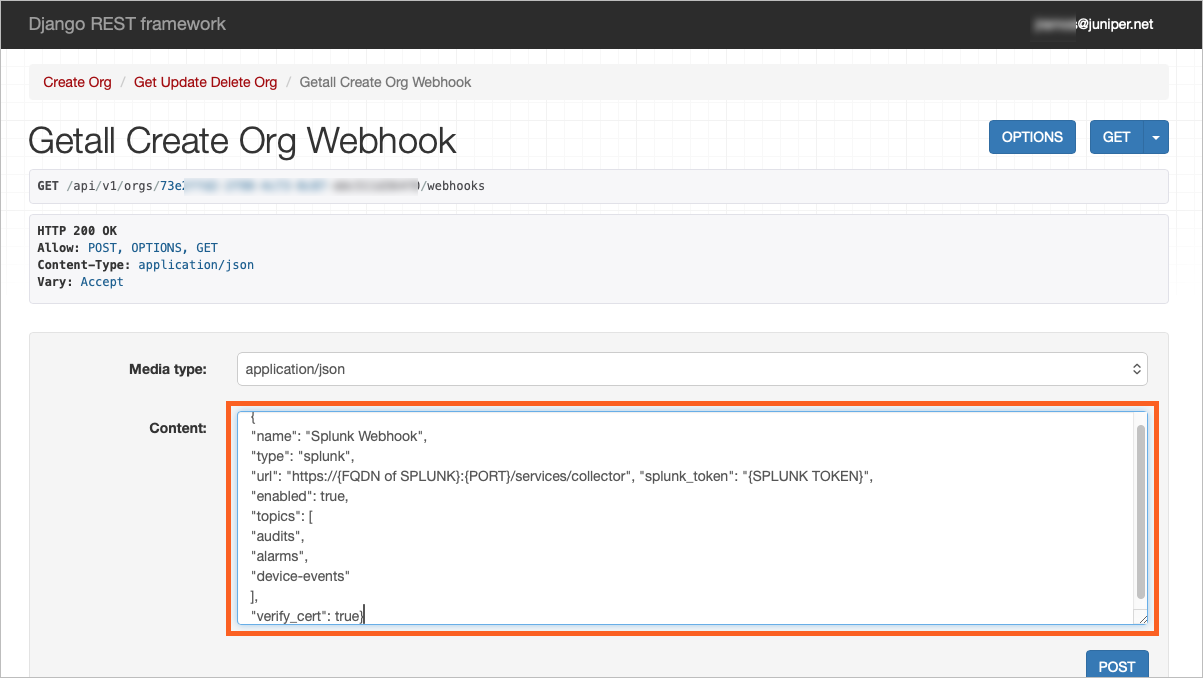
    Django REST framework interface showing a GET endpoint for managing organization webhooks at api/v1/orgs/{id}/webhooks with JSON response details and allowed methods including POST, OPTIONS, and GET.
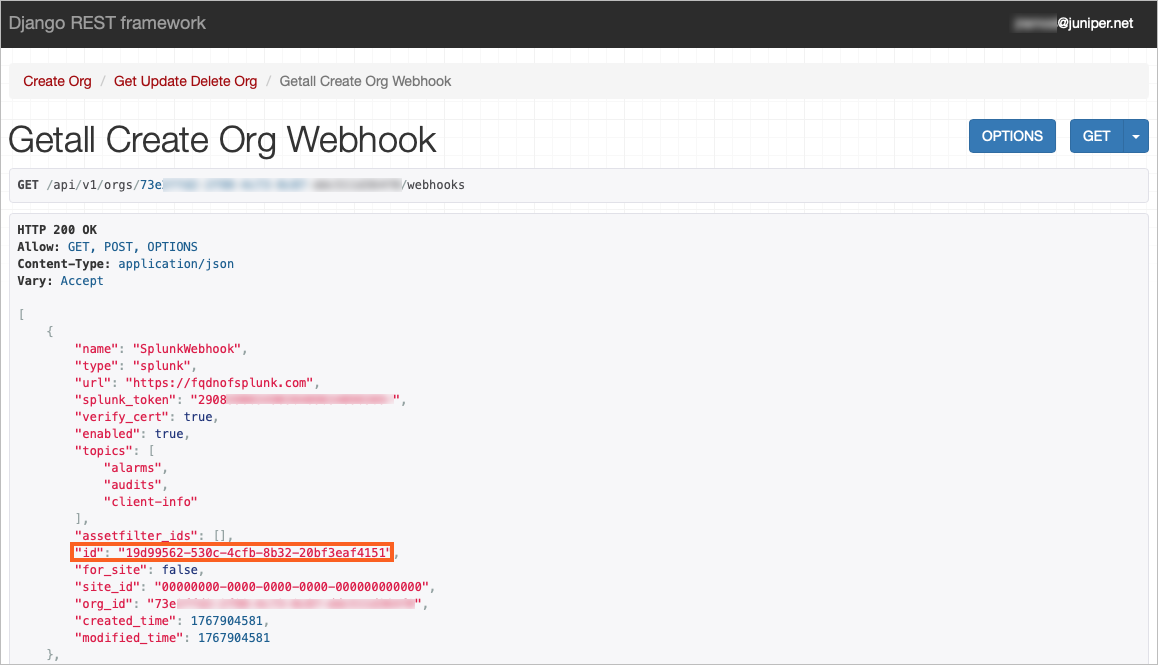
You can now verify the configuration is in the top field of the window and that the id field contains data.

Django REST framework API response displaying webhook details in JSON format, including name SplunkWebhook, type splunk, URL, topics alarms, audits, client-info, enabled status, and timestamps for creation and modification.

This confirms that Mist and Splunk can communicate.