Appendix: WAN Edge SSR or SRX Juniper Mist Cloud-managed eBGP Peering Via Active/Passive LAG
In this appendix, we describe the capability to manage and configure the WAN router through the Juniper Mist cloud. This feature is referred to as WAN Edge, and Juniper currently offers two device series for this purpose:
- The SRX Series Firewall product line.
- The Session Smart Router product line.
For integrating these device series into a campus fabric, two design options are practical:
- For small fabrics (or a proof of concept), you may choose the bridged overlay approach described in Appendix: IPv6 Overlay and Underlay eBGP Peering Towards Unmanaged SRX. This requires less configuration but comes with the known limitations in future scalability that were already highlighted in WAN Router Integration Using Service Block Function.
- The recommended approach is to use eBGP with the device to exchange routes, since the fabric already uses this method internally.
In this appendix, we present the approach that uses eBGP when SRX or SSR devices are managed by the Juniper Mist cloud. In the previous appendix, we used a design in which each of the four uplink interfaces between the fabric and the WAN router was configured independently, with all interfaces active at the same time. In this design, we changed that approach to a LAG configuration when the WAN router nodes operate in an active/passive mode for the following reasons:
- The SSR uses a stateful firewall design on the LAN interface connected to the EVPN fabric. When traffic flows asynchronously through the fabric and appears on a different LAN interface, the firewall state is not shared and the packets are dropped. When LAG is enabled using bonded interfaces, these stateful checks occur later and no longer on the individual LAN interfaces, which resolves the issue.
- The SRX places each interface for each VRF into a zone, and there are four uplinks. When hairpin traffic between VRFs is allowed, firewall policies must permit traffic between the zones. With a small number of VRFs, this is not an issue. However, as the number of VRFs grows, the number of firewall policies required for possible hairpin traffic between zones increases significantly. Using a LAG toward the fabric reduces the number of required policies by 75 percent, and internally a redundant interface (reth) can be used to map the interface into a zone.
- Some customers prefer a LAG with an active/passive WAN router design to avoid potential issues when asynchronous traffic is exchanged and both WAN router nodes operate as stateful devices.
Currently (July 2025) WAN Edge for SRX and SSR does not support IPv6. Customers with DualStack need to go with an unmanaged SRX design as described in Appendix: IPv6 Overlay and Underlay eBGP Peering Towards Unmanaged SRX. Also using an SSR managed by a conductor was not tested.
WAN Edge for SSR Specifics
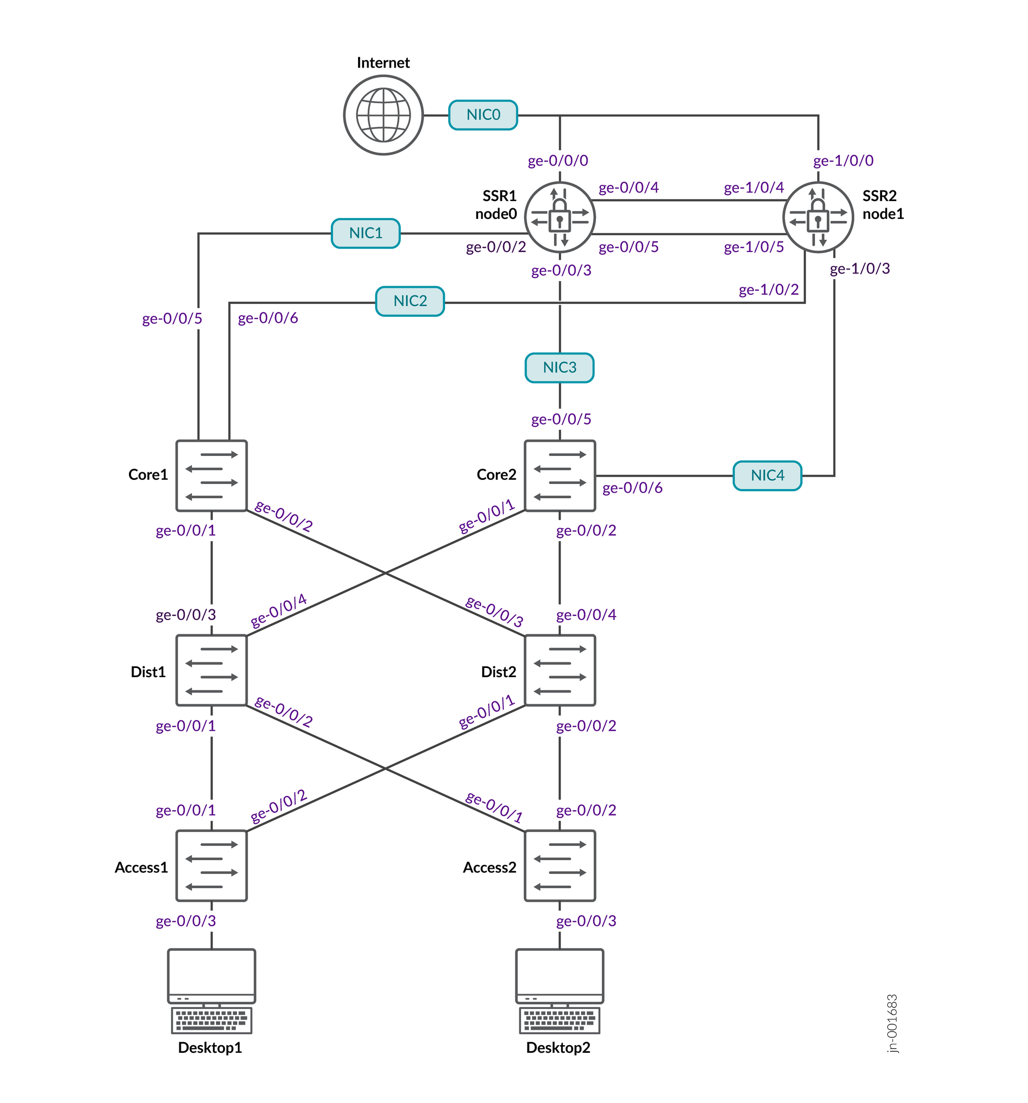
For this JVD, all testing was done using physical devices. If you want to build a virtual lab for feature evaluation then the SSR WAN router must also be physical devices (same SKU), and the remaining pieces of the lab infrastructure can be based on virtual machines. You can find instructions on how to use vJunos-switch VMs together with Juniper Mist cloud in the following NCE. To get the physical SSRs connected to the virtual lab infrastructure, we suggest using dedicated Ethernet NICs on the VM server since the SSR LACP messages and interface bonding require this. A suggested lab build-out is shown in the image below.
The LAG configuration and the BGP peering that must be established when using a pair of redundant SSR devices are illustrated in the topology example below for a single global VRF within the EVPN fabric.
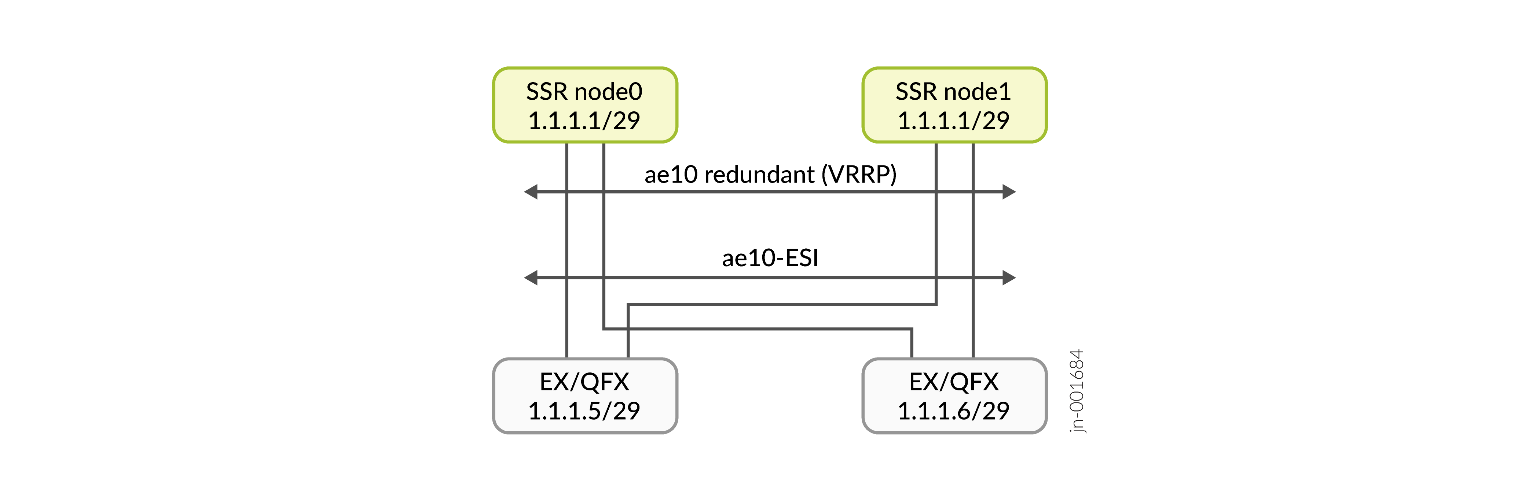
The design works in the following way:
- A single ae*-interface aggregates all four links on the SSR cluster.
- The ae*-interface must be configured for LAG with active LACP.
- The LAG must be configured for redundancy, which results in an active/standby VRRP operation.
- The SSR HA cluster determines which node is active.
- Only two cluster interfaces run active LACP at the same time.
- The standby node disables its interfaces until a failover occurs.
- One fabric ae* LAG is required.
- It must be configured as an ESI-LAG across the fabric nodes
- The same AE index key must be used on all fabric links.
- IP addressing and BGP peering:
- At least a /29 subnet is required because a minimum of three IP addresses are used in the peering subnet.
- The IP address on the SSR cluster moves between nodes.
- The IP addresses on the fabric must be unique for each node.
The picture below shows how the two service block functions of the fabric connect to the first WAN router.
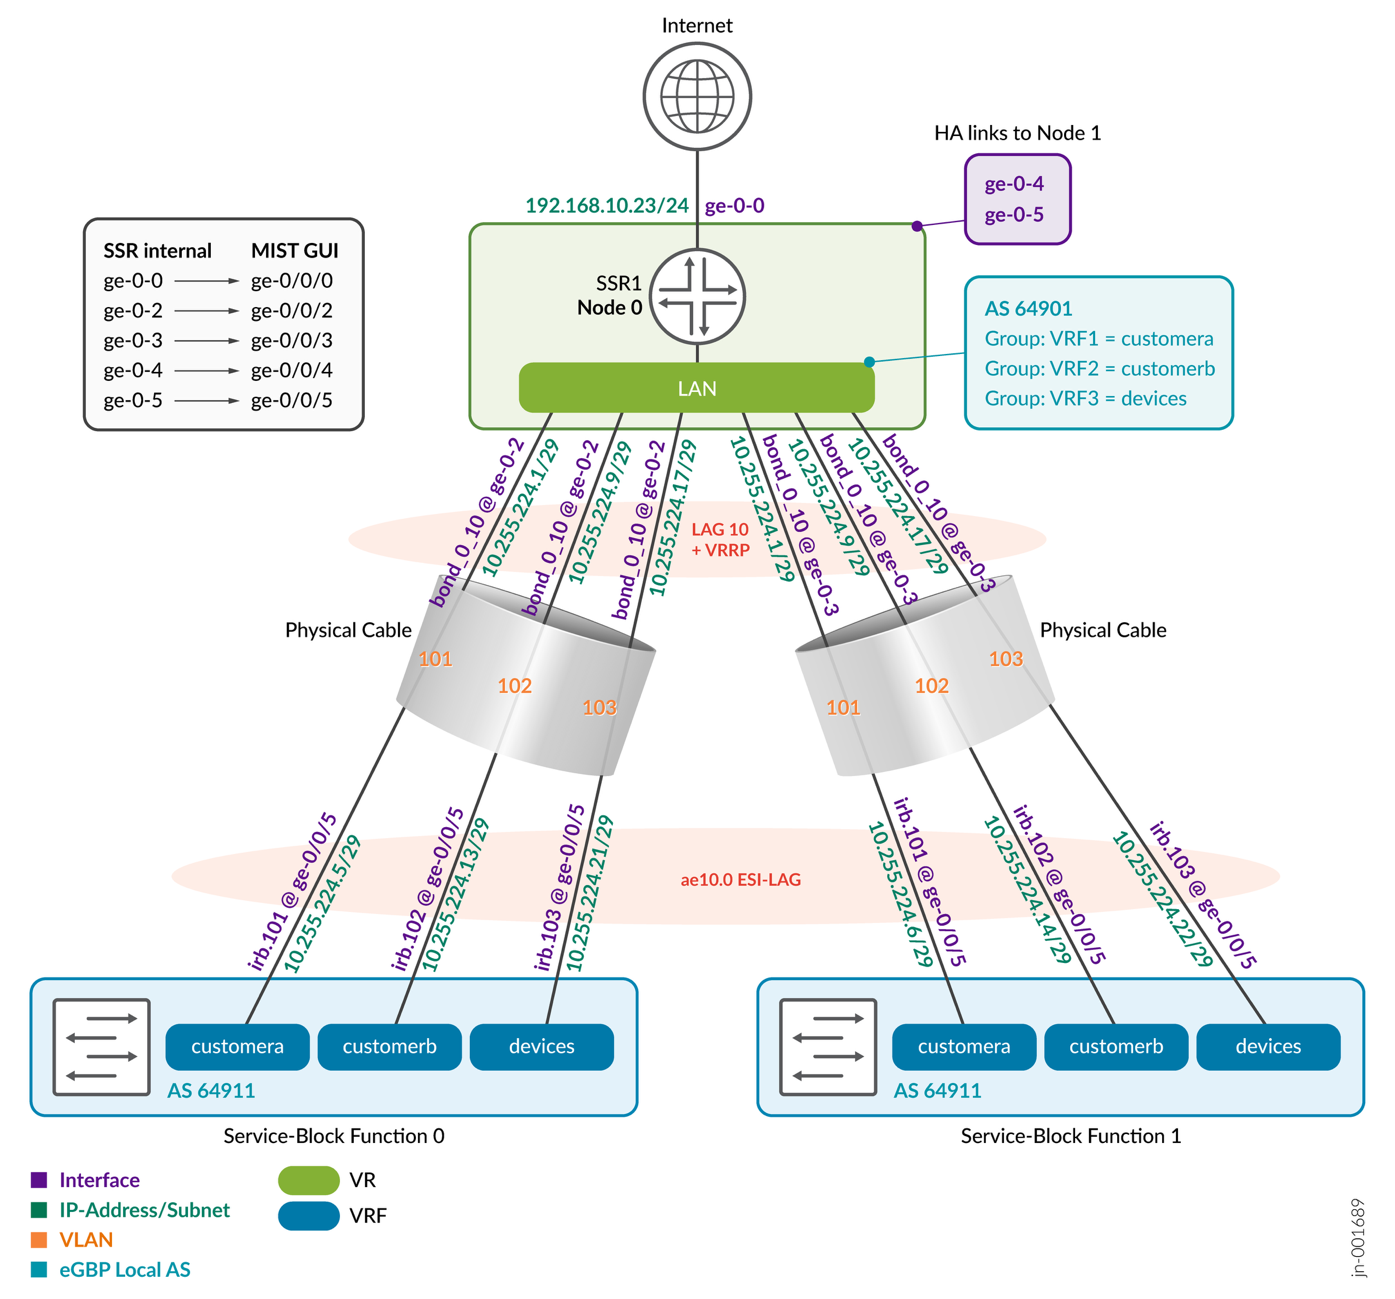
The picture below shows how the two service block functions of the fabric connect to the second WAN router.
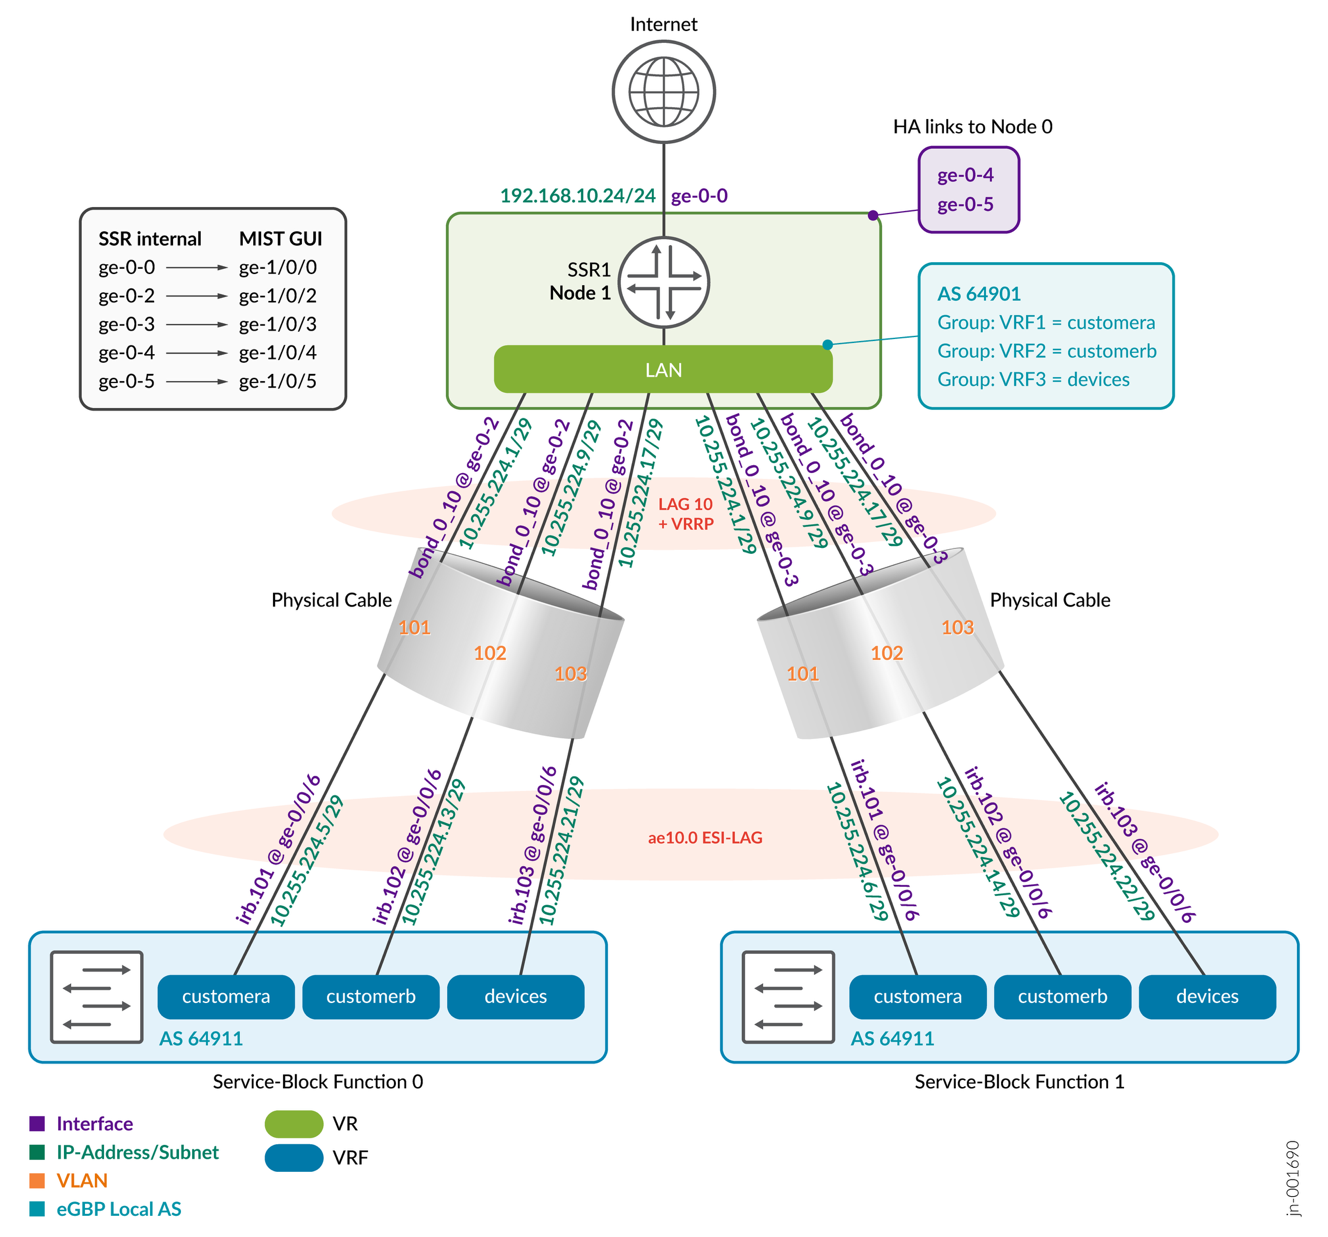
Below is the full configuration Table between core1 and core2 as service block function and the two WAN routers. You also see the ASN chosen for eBGP.
| Switch | Switch AS | VRF | Core P2P IP | Core IF | WAN Router | WAN Router P2P IP | WAN Router AS | WAN Router IF | VLAN ID |
|---|---|---|---|---|---|---|---|---|---|
| core1 | 64911 | customera | 10.255.224.5/29 |
irb.101 ge-0/0/5 ae10.0 |
ssr-node0 | 10.255.224.1/29 | 64901 |
bond_0_10 ge-0-2 ge-0/0/2 |
101 |
| core1 | 64911 | customerb | 10.255.224.13/29 |
irb.102 ge-0/0/5 ae10.0 |
ssr-node0 | 10.255.224.9/29 | 64901 |
bond_0_10 ge-0-2 ge-0/0/2 |
102 |
| core1 | 64911 | devices | 10.255.224.21/29 |
irb.103 ge-0/0/5 ae10.0 |
ssr-node0 | 10.255.224.17/29 | 64901 |
bond_0_10 ge-0-2 ge-0/0/2 |
103 |
| core1 | 64911 | customera | 10.255.224.5/29 |
irb.101 ge-0/0/6 ae10.0 |
ssr-node1 | 10.255.224.1/29 | 64901 |
bond_0_10 ge-0-2 ge-1/0/2 |
101 |
| core1 | 64911 | customerb | 10.255.224.13/29 |
irb.102 ge-0/0/6 ae10.0 |
ssr-node1 | 10.255.224.9/29 | 64901 |
bond_0_10 ge-0-2 ge-1/0/2 |
102 |
| core1 | 64911 | devices | 10.255.224.21/29 |
irb.103 ge-0/0/6 ae10.0 |
ssr-node1 | 10.255.224.17/29 | 64901 |
bond_0_10 ge-0-2 ge-1/0/2 |
103 |
| core2 | 64911 | customera | 10.255.224.6/29 |
irb.101 ge-0/0/5 ae10.0 |
ssr-node0 | 10.255.224.1/29 | 64901 |
bond_0_10 ge-0-3 ge-0/0/3 |
101 |
| core2 | 64911 | customerb | 10.255.224.14/29 |
irb.102 ge-0/0/5 ae10.0 |
ssr-node0 | 10.255.224.9/29 | 64901 |
bond_0_10 ge-0-3 ge-0/0/3 |
102 |
| core2 | 64911 | devices | 10.255.224.22/29 |
irb.103 ge-0/0/5 ae10.0 |
ssr-node0 | 10.255.224.17/29 | 64901 |
bond_0_10 ge-0-3 ge-0/0/3 |
103 |
| core2 | 64911 | customera | 10.255.224.6/29 |
irb.101 ge-0/0/6 ae10.0 |
ssr-node1 | 10.255.224.1/29 | 64901 |
bond_0_10 ge-0-3 ge-1/0/3 |
101 |
| core2 | 64911 | customerb | 10.255.224.14/29 |
irb.102 ge-0/0/6 ae10.0 |
ssr-node1 | 10.255.224.9/29 | 64901 |
bond_0_10 ge-0-2 ge-1/0/3 |
102 |
| core2 | 64911 | devices | 10.255.224.22/29 |
irb.103 ge-0/0/6 ae10.0 |
ssr-node1 | 10.255.224.17/29 | 64901 |
bond_0_10 ge-0-2 ge-1/0/3 |
103 |
The following are instructions describing what needs to be configured on the core1 switch as service block function.
#
# This is for Device: core1
#
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
#
# configure a Port-Profile:
# - Name=peering-uplinks
# - Mode=Trunk
# - Port Network=None
# - Trunk Networks:
# --- Trunk Network=trans101
# --- Trunk Network=trans102
# --- Trunk Network=trans103
# - Enable MTU=Checked  MTU=9018
#
# configure the Additional IP-Subnet 10.255.224.5/29 to Network=trans101
# configure the Additional IP-Subnet 10.255.224.13/29 to Network=trans102
# configure the Additional IP-Subnet 10.255.224.21/29 to Network=trans103
#
# Configure an Uplink Port to WAN-Router:
# - Port ID=ge-0/0/5-6
# - Configuration Profile=peering-uplinks
# - Port Aggregation:
# --- Enabled=Checked
# --- LACP=Enabled
# --- LACP Force-UP=Disabled
# --- LACP Periodic Slow=Disabled
# --- AE Index=10
# --- ESI-LAG=Checked/Enabled
#
# VRF Configuration
# - Override Site/Template Settings=Checked/Enabled
# - Enabled=Checked
# - Instance=customera
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans101
# - Instance=customerb
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans102
# - Instance=devices
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans103
#
# Enable BGP
# Create an Export policy called 'export-vrfs'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default  Prefix=0.0.0.0/0  Protocol=None  Then=Reject
# - Add Term w. Name=fabric-all-no-hosts  Prefix=0.0.0.0/0-30  Protocol=None  Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32  Protocol=None  Then=Accept
#
# Create an Export policy called 'import-default'
# - Name=default  Prefix=0.0.0.0/0  Protocol=BGP  Action=Accept
#
# Create a BGP Group with:
# - Name=customera
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.1
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.9
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.17
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Additional Junos CLI needed
#
# ERB+IP-Clos Fabric: on all non-EX92xx switches change to below
delete groups top protocols evpn default-gateway do-not-advertise
set groups top protocols evpn default-gateway no-gateway-community
The following are instructions describing what needs to be configured on core2 switch as service block function.
#
# This is for Device: core2
#
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
#
# configure a Port-Profile:
# - Name=peering-uplinks
# - Mode=Trunk
# - Port Network=None
# - Trunk Networks:
# --- Trunk Network=trans101
# --- Trunk Network=trans102
# --- Trunk Network=trans103
# - Enable MTU=Checked  MTU=9018
#
# configure the Additional IP-Subnet 10.255.224.6/29 to Network=trans101
# configure the Additional IP-Subnet 10.255.224.14/29 to Network=trans102
# configure the Additional IP-Subnet 10.255.224.22/29 to Network=trans103
#
# Configure an Uplink Port to WAN-Router:
# - Port ID=ge-0/0/5-6
# - Configuration Profile=peering-uplinks
# - Port Aggregation:
# --- Enabled=Checked
# --- LACP=Enabled
# --- LACP Force-UP=Disabled
# --- LACP Periodic Slow=Disabled
# --- AE Index=10
# --- ESI-LAG=Checked/Enabled
#
# VRF Configuration
# - Override Site/Template Settings=Checked/Enabled
# - Enabled=Checked
# - Instance=customera
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans101
# - Instance=customerb
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans102
# - Instance=devices
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans103
#
# Enable BGP
# Create an Export policy called 'export-vrfs'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default  Prefix=0.0.0.0/0  Protocol=None  Then=Reject
# - Add Term w. Name=fabric-all-no-hosts  Prefix=0.0.0.0/0-30  Protocol=None  Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32  Protocol=None  Then=Accept
#
# Create an Export policy called 'import-default'
# - Name=default  Prefix=0.0.0.0/0  Protocol=BGP  Action=Accept
#
# Create a BGP Group with:
# - Name=customera
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.1
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.9
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.17
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Additional Junos CLI needed
#
# ERB+IP-Clos Fabric: on all non-EX92xx switches change to below
delete groups top protocols evpn default-gateway do-not-advertise
set groups top protocols evpn default-gateway no-gateway-community
WAN Edge for SRX Specifics
For this JVD, all testing was performed using physical devices. If you want to build a virtual lab for feature evaluation, use vSRX version 3 and apply AppID demo licenses to those virtual machines. Instructions for using vJunos-switch VMs with the Juniper Mist cloud can be found in the following NCE. A suggested lab topology is shown in the diagram below.
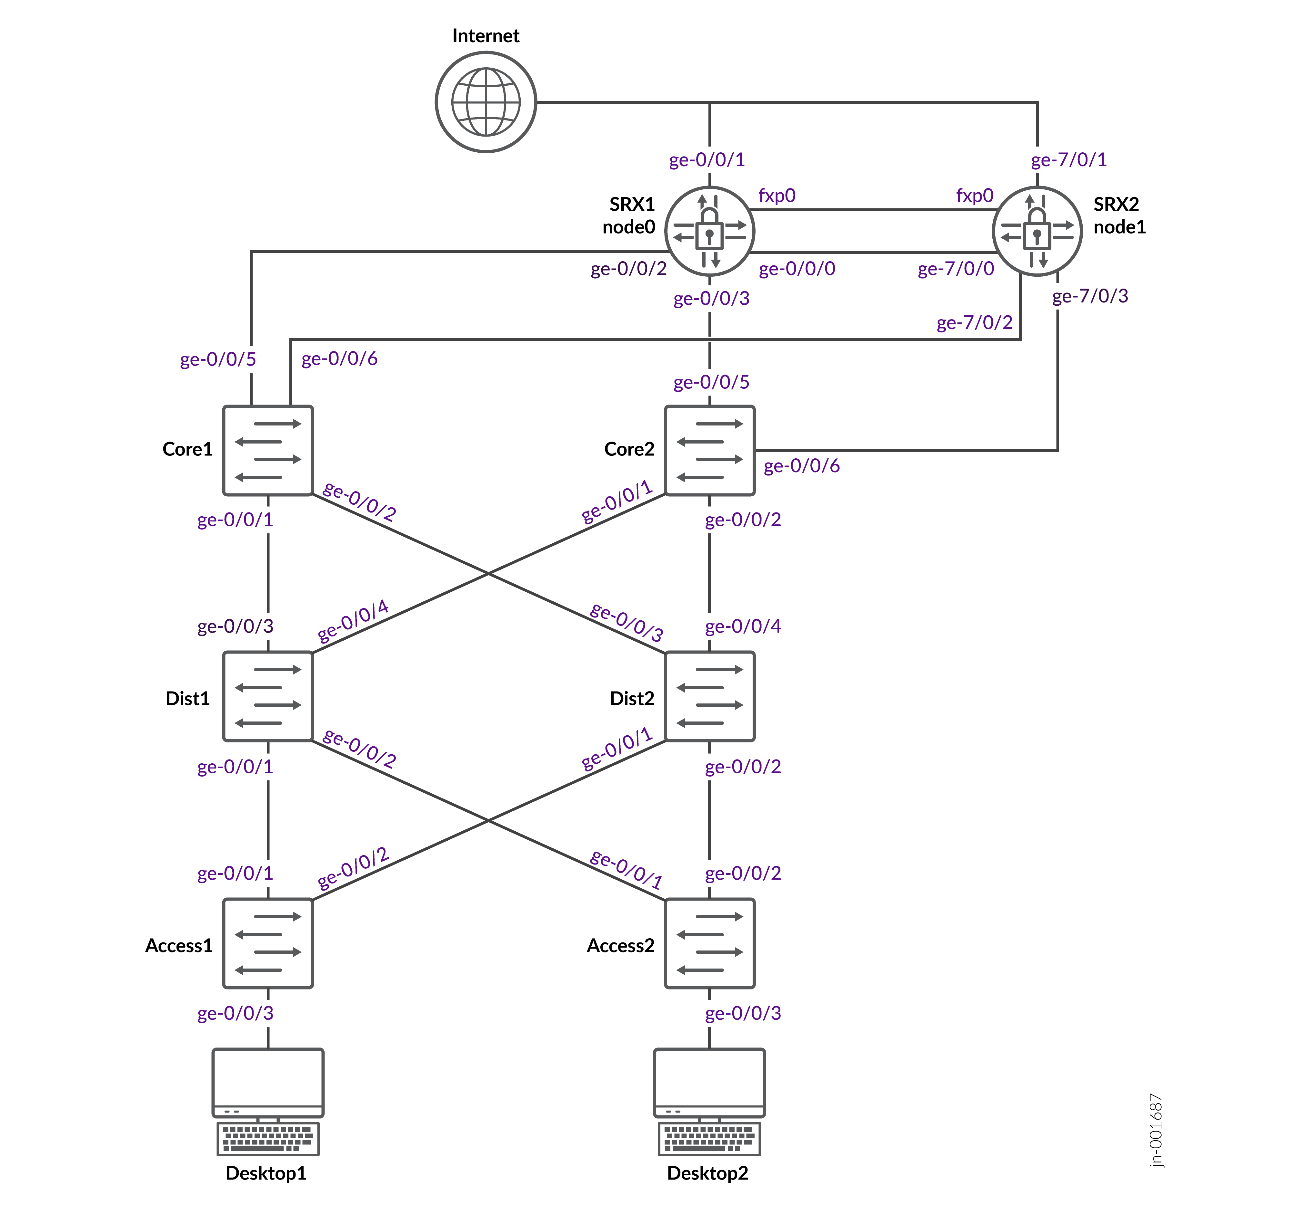
The LAG configuration and the BGP peering required for a pair of redundant SRXs are illustrated in the topology example below for a single global VRF within the EVPN fabric.
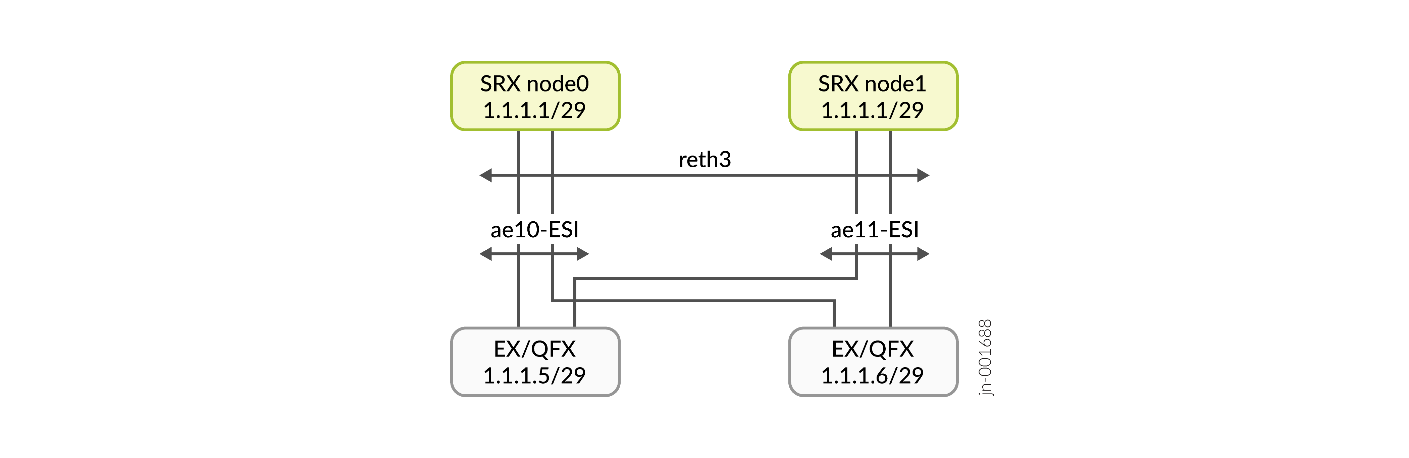
The design works in the following way:
- A single reth interface aggregates all four links on the SRX chassis cluster.
- The reth interface is configured for LAG with active LACP.
- All four SRX chassis cluster interfaces operate with active LACP at the same time.
- The SRX chassis cluster determines which node is active
- The standby node does not respond to ARP requests.
- Only the ae10 or ae11 interfaces on the fabric learn the active SRX remote MAC address.
- You need two fabric ae* LAGs:
- They are required to be ESI-LAGs from fabric nodes.
- They must use the same AE index key toward the corresponding SRX cluster node.
- IP addressing and BGP Peering:
- At least a /29 subnet is required because a minimum of three IP addresses are used in the peering subnet.
- The IP address on the SRX chassis cluster moves between nodes.
- The IP addresses on the fabric must be unique for each node.
The image below shows how the two service block functions of the fabric connect to the first WAN router.
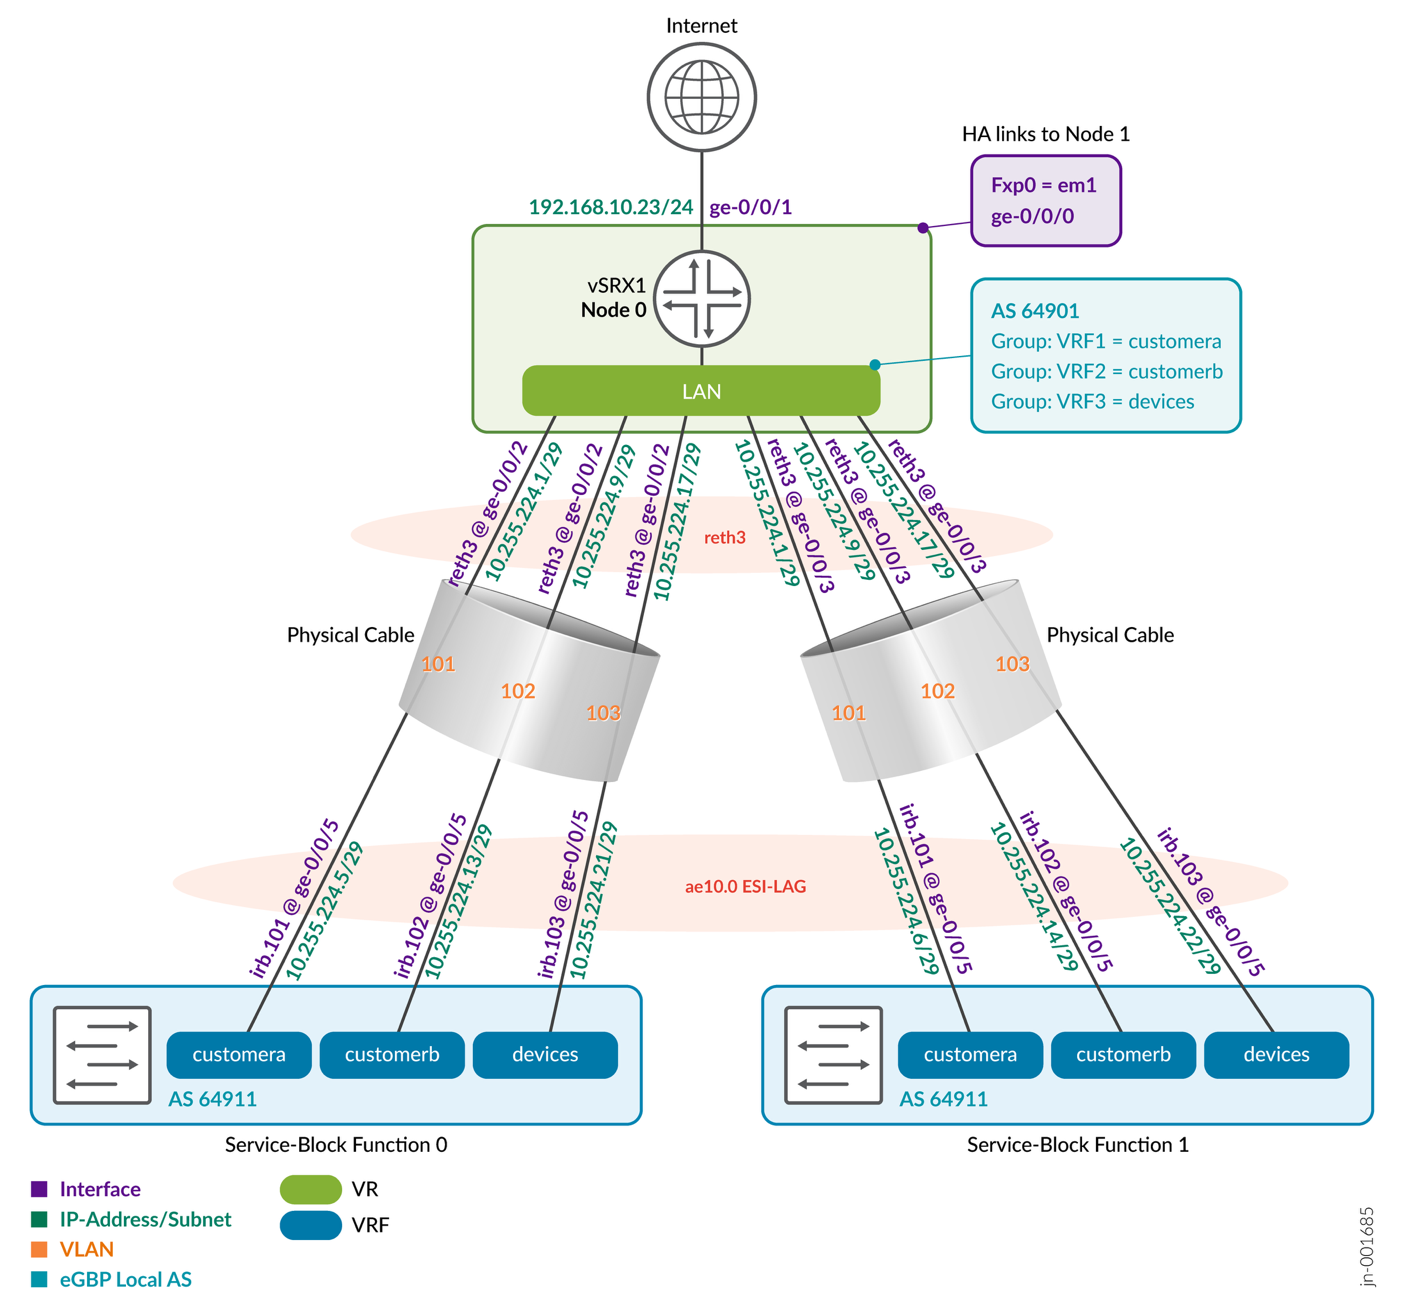
The image below shows how the two service block functions of the fabric connect to the second WAN router.
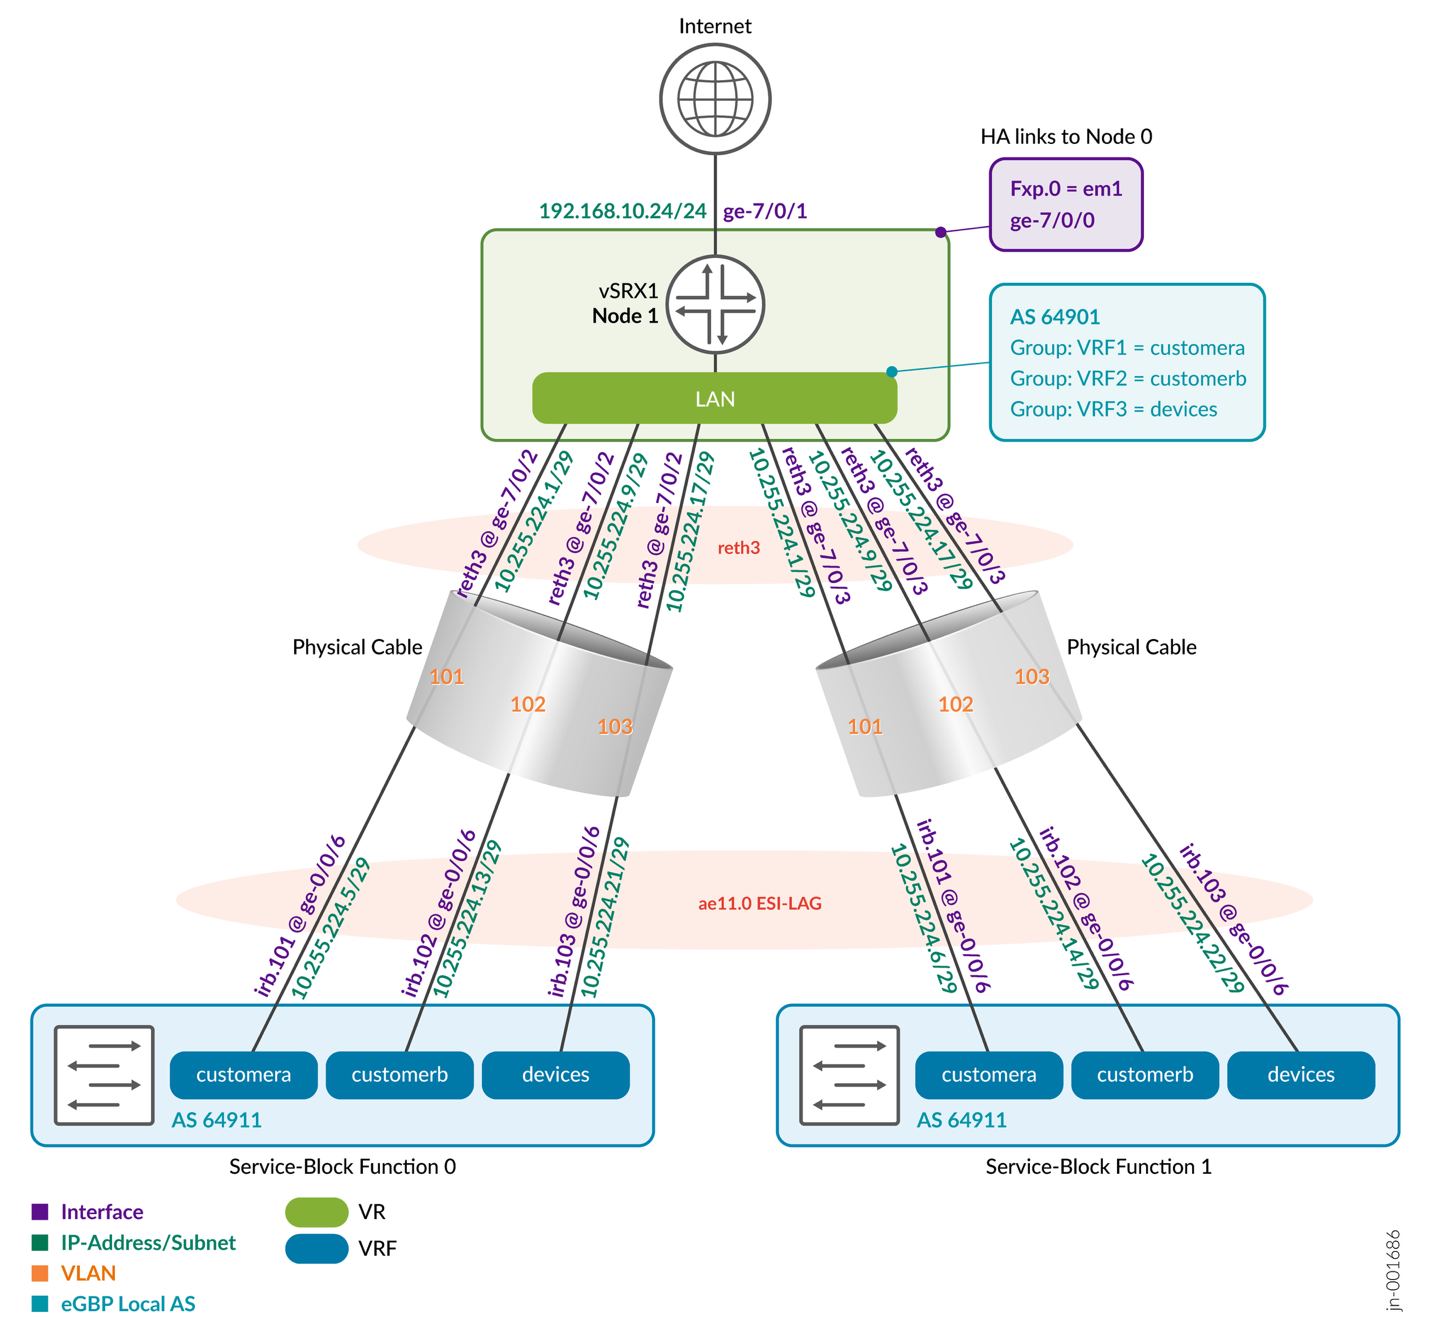
Below is the full configuration table between core1 and core2 as service block function and the two WAN routers. You also see the AS number chosen for eBGP.
| Switch | Switch AS | VRF | Core P2P IP | Core IF | WAN Router | WAN Router P2P IP | WAN Router AS | WAN Router IF | VLAN ID |
|---|---|---|---|---|---|---|---|---|---|
| core1 | 64911 | customera | 10.255.224.5/29 |
irb.101 ge-0/0/5 ae10.0 |
srx-node0 | 10.255.224.1/29 | 64901 |
reth3.101 ge-0/0/2 |
101 |
| core1 | 64911 | customerb | 10.255.224.13/29 |
irb.102 ge-0/0/5 ae10.0 |
srx-node0 | 10.255.224.9/29 | 64901 |
reth3.102 ge-0/0/2 |
102 |
| core1 | 64911 | devices | 10.255.224.21/29 |
irb.103 ge-0/0/5 ae10.0 |
srx-node0 | 10.255.224.17/29 | 64901 |
reth3.103 ge-0/0/2 |
103 |
| core1 | 64911 | customera | 10.255.224.5/29 |
irb.101 ge-0/0/6 ae11.0 |
srx-node1 | 10.255.224.1/29 | 64901 |
reth3.101 ge-7/0/2 |
101 |
| core1 | 64911 | customerb | 10.255.224.13/29 |
irb.102 ge-0/0/6 ae11.0 |
srx-node1 | 10.255.224.9/29 | 64901 |
reth3.102 ge-7/0/2 |
102 |
| core1 | 64911 | devices | 10.255.224.21/29 |
irb.103 ge-0/0/6 ae11.0 |
srx-node1 | 10.255.224.17/29 | 64901 |
reth3.103 ge-7/0/2 |
103 |
| core2 | 64911 | customera | 10.255.224.6/29 |
irb.101 ge-0/0/5 ae10.0 |
srx-node0 | 10.255.224.1/29 | 64901 |
reth3.101 ge-0/0/3 |
101 |
| core2 | 64911 | customerb | 10.255.224.14/29 |
irb.102 ge-0/0/5 ae10.0 |
srx-node0 | 10.255.224.9/29 | 64901 |
reth3.102 ge-0/0/3 |
102 |
| core2 | 64911 | devices | 10.255.224.22/29 |
irb.103 ge-0/0/5 ae10.0 |
srx-node0 | 10.255.224.17/29 | 64901 |
reth3.103 ge-0/0/3 |
103 |
| core2 | 64911 | customera | 10.255.224.6/29 |
irb.101 ge-0/0/6 ae11.0 |
srx-node1 | 10.255.224.1/29 | 64901 |
reth3.101 ge-7/0/3 |
101 |
| core2 | 64911 | customerb | 10.255.224.14/29 |
irb.102 ge-0/0/6 ae11.0 |
srx-node1 | 10.255.224.9/29 | 64901 |
reth3.102 ge-7/0/3 |
102 |
| core2 | 64911 | devices | 10.255.224.22/29 |
irb.103 ge-0/0/6 ae11.0 |
srx-node1 | 10.255.224.17/29 | 64901 |
reth3.103 ge-7/0/3 |
103 |
The following are instructions describing what needs to be configured on core1 switch as service block function.
#
# This is for Device: core1
#
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
#
# configure a Port-Profile:
# - Name=peering-uplinks
# - Mode=Trunk
# - Port Network=None
# - Trunk Networks:
# --- Trunk Network=trans101
# --- Trunk Network=trans102
# --- Trunk Network=trans103
# - Enable MTU=Checked  MTU=9018
#
# configure the Additional IP-Subnet 10.255.224.5/29 to Network=trans101
# configure the Additional IP-Subnet 10.255.224.13/29 to Network=trans102
# configure the Additional IP-Subnet 10.255.224.21/29 to Network=trans103
#
# Configure an Uplink Port to WAN-Router:
# - Port ID=ge-0/0/5
# - Configuration Profile=peering-uplinks
# - Port Aggregation:
# --- Enabled=Checked
# --- LACP=Enabled
# --- LACP Force-UP=Disabled
# --- LACP Periodic Slow=Disabled
# --- AE Index=10
# --- ESI-LAG=Checked/Enabled
#
# Configure an Uplink Port to WAN-Router:
# - Port ID=ge-0/0/6
# - Configuration Profile=peering-uplinks
# - Port Aggregation:
# --- Enabled=Checked
# --- LACP=Enabled
# --- LACP Force-UP=Disabled
# --- LACP Periodic Slow=Disabled
# --- AE Index=11
# --- ESI-LAG=Checked/Enabled
#
# VRF Configuration
# - Override Site/Template Settings=Checked/Enabled
# - Enabled=Checked
# - Instance=customera
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans101
# - Instance=customerb
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans102
# - Instance=devices
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans103
#
# Enable BGP
# Create an Export policy called 'export-vrfs'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default  Prefix=0.0.0.0/0  Protocol=None  Then=Reject
# - Add Term w. Name=fabric-all-no-hosts  Prefix=0.0.0.0/0-30  Protocol=None  Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32  Protocol=None  Then=Accept
#
# Create an Import policy called 'import-default'
# - Name=default  Prefix=0.0.0.0/0  Protocol=BGP  Action=Accept
#
# Create a BGP Group with:
# - Name=customera
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.1
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.9
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.17
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Additional Junos CLI needed
#
# ERB+IP-Clos Fabric: on all non-EX92xx switches change to below
delete groups top protocols evpn default-gateway do-not-advertise
set groups top protocols evpn default-gateway no-gateway-community
The following are the instructions what needs to be configured on core2 switch as service block function.
#
# This is for Device: core2
#
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
#
# configure a Port-Profile:
# - Name=peering-uplinks
# - Mode=Trunk
# - Port Network=None
# - Trunk Networks:
# --- Trunk Network=trans101
# --- Trunk Network=trans102
# --- Trunk Network=trans103
# - Enable MTU=Checked  MTU=9018
#
# configure the Additional IP-Subnet 10.255.224.6/29 to Network=trans101
# configure the Additional IP-Subnet 10.255.224.14/29 to Network=trans102
# configure the Additional IP-Subnet 10.255.224.22/29 to Network=trans103
#
# Configure an Uplink Port to WAN-Router:
# - Port ID=ge-0/0/5
# - Configuration Profile=peering-uplinks
# - Port Aggregation:
# --- Enabled=Checked
# --- LACP=Enabled
# --- LACP Force-UP=Disabled
# --- LACP Periodic Slow=Disabled
# --- AE Index=10
# --- ESI-LAG=Checked/Enabled
#
# Configure an Uplink Port to WAN-Router:
# - Port ID=ge-0/0/6
# - Configuration Profile=peering-uplinks
# - Port Aggregation:
# --- Enabled=Checked
# --- LACP=Enabled
# --- LACP Force-UP=Disabled
# --- LACP Periodic Slow=Disabled
# --- AE Index=11
# --- ESI-LAG=Checked/Enabled
#
#
# VRF Configuration
# - Override Site/Template Settings=Checked/Enabled
# - Enabled=Checked
# - Instance=customera
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans101
# - Instance=customerb
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans102
# - Instance=devices
# --- Override Template Defined VRF Instance=Checked/Enabled
# --- add to exiting Networks=trans103
#
# Enable BGP
# Create an Export policy called 'export-vrfs'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default  Prefix=0.0.0.0/0  Protocol=None  Then=Reject
# - Add Term w. Name=fabric-all-no-hosts  Prefix=0.0.0.0/0-30  Protocol=None  Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32  Protocol=None  Then=Accept
#
# Create an Export policy called 'import-default'
# - Name=default  Prefix=0.0.0.0/0  Protocol=BGP  Action=Accept
#
# Create a BGP Group with:
# - Name=customera
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.1
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.9
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs
# - Set Import=import-default
# Add also the following Neighbor
# --- IP_Address=10.255.224.17
# --- Neighbor_AS=64901
# --- Hold-Time=90
#
# Additional Junos CLI needed
#
# ERB+IP-Clos Fabric: on all non-EX92xx switches change to below
delete groups top protocols evpn default-gateway do-not-advertise
set groups top protocols evpn default-gateway no-gateway-community
EVPN Fabric Setup Side Configuration
Switch Template Configuration
Below is a switch template used for evaluation. You can reuse this switch template or create a new one.
{
  "additional_config_cmds": [],
  "networks": {
    "vlan1031": {
      "vlan_id": "1031",
      "subnet": "10.33.31.0/24"
    },
    "vlan1033": {
      "vlan_id": "1033",
      "subnet": "10.33.33.0/24"
    },
    "vlan1081": {
      "vlan_id": "1081",
      "subnet": "10.88.81.0/24"
    },
    "vlan1088": {
      "vlan_id": "1088",
      "subnet": "10.88.88.0/24"
    },
    "vlan1091": {
      "vlan_id": "1091",
      "subnet": "10.99.91.0/24"
    },
    "vlan1099": {
      "vlan_id": "1099",
      "subnet": "10.99.99.0/24"
    }
  },
  "port_usages": {
    "dynamic": {
      "mode": "dynamic",
      "rules": []
    },
    "vlan1088": {
      "mode": "access",
      "disabled": false,
      "port_network": "vlan1088",
      "voip_network": null,
      "stp_edge": false,
      "mac_auth_protocol": null,
      "all_networks": false,
      "networks": null,
      "port_auth": null,
      "enable_mac_auth": null,
      "mac_auth_only": null,
      "guest_network": null,
      "bypass_auth_when_server_down": null,
      "speed": "auto",
      "duplex": "auto",
      "mac_limit": 0,
      "persist_mac": false,
      "poe_disabled": false,
      "enable_qos": false,
      "storm_control": {},
      "mtu": null,
      "description": "",
      "disable_autoneg": false,
      "use_vstp": false,
      "allow_multiple_supplicants": null,
      "dynamic_vlan_networks": null,
      "stp_p2p": false,
      "stp_no_root_port": false,
      "reauth_interval": null
    },
    "vlan1099": {
      "mode": "access",
      "disabled": false,
      "port_network": "vlan1099",
      "voip_network": null,
      "stp_edge": false,
      "mac_auth_protocol": null,
      "all_networks": false,
      "networks": null,
      "port_auth": null,
      "enable_mac_auth": null,
      "mac_auth_only": null,
      "guest_network": null,
      "bypass_auth_when_server_down": null,
      "speed": "auto",
      "duplex": "auto",
      "mac_limit": 0,
      "persist_mac": false,
      "poe_disabled": false,
      "enable_qos": false,
      "storm_control": {},
      "mtu": null,
      "description": "",
      "disable_autoneg": false,
      "use_vstp": false,
      "allow_multiple_supplicants": null,
      "dynamic_vlan_networks": null,
      "stp_p2p": false,
      "stp_no_root_port": false,
      "reauth_interval": null
    }
  },
  "switch_matching": {
    "enable": true,
    "rules": []
  },
  "switch_mgmt": {
    "config_revert_timer": 10,
    "root_password": "juniper123",
    "local_accounts": {},
    "protect_re": {
      "enabled": false
    },
    "tacacs": {
      "enabled": false
    },
    "dhcp_option_fqdn": false
  },
  "mist_nac": {
    "enabled": true,
    "network": null
  },
  "radius_config": {
    "auth_servers": [],
    "acct_servers": [],
    "auth_servers_timeout": 5,
    "auth_servers_retries": 3,
    "fast_dot1x_timers": false,
    "acct_interim_interval": 0,
    "auth_server_selection": "ordered",
    "coa_enabled": false,
    "coa_port": ""
  },
  "vrf_config": {
    "enabled": false
  },
  "remote_syslog": {
    "enabled": false
  },
  "snmp_config": {
    "enabled": false
  },
  "dhcp_snooping": {
    "enabled": false
  },
  "dns_servers": [],
  "dns_suffix": [],
  "ntp_servers": [],
  "acl_policies": [],
  "port_mirroring": {},
  "disabled_system_defined_port_usages": [],
  "extra_routes": {},
  "extra_routes6": {},
  "bgp_config": null,
  "routing_policies": {},
  "name": "campus-fabric"
}
Apart from the overlay VLAN for the EVPN fabric, you need to do the following:
- Add a transport/peering VLAN for each VRF into the switch
template to make it available globally.
- Apart from the network name, just the VLAN ID needs to be configured.
- Make sure this is not used in the campus fabric VRF or on any access switches.
In our example, configure the following:
- For the first VRF we add the following network:
- Name=
trans101 - VLAN ID=
101 - IPv4 Subnet=
empty(we configure this on the service block using an additional IP address) - IPv6 Subnet=
empty(unused in this design)
- Name=
- For the second VRF we add the following network:
- Name=
trans102 - VLAN ID=
102 - IPv4 Subnet=
empty(we configure this on the service block using an additional IP address) - IPv6 Subnet=
empty(unused in this design)
- Name=
- For the third VRF we add the following network:
- Name=
trans103 - VLAN ID=
103 - IPv4 Subnet=
empty(we configure this on the service block using an additional IP address) - IPv6 Subnet=
empty(unused in this design)
- Name=
Core1 and Core2 = Service Block 0 and 1
Ensure your transport/peering VLANs are imported from the switch template (or else configured locally). For each transport VLAN and service block, configure an IP address as an additional IP with a /29 network.
The full configuration for the core1 switch is:
- Additional IP Configuration=
trans101- IP Address=
static - IPv4 Address=
10.255.224.5 - IPv4 Subnet Mask=
255.255.255.248 - IPv6 Address=
empty - IPv4 Subnet Mask=
empty - Network=
trans101
- IP Address=
- Additional IP Configuration=
trans102- IP Address=
static - IPv4 Address=
10.255.224.13 - IPv4 Subnet Mask=
255.255.255.248 - IPv6 Address=
empty - IPv4 Subnet Mask=
empty - Network=
trans102
- IP Address=
- Additional IP Configuration=
trans103- IP Address=
static - IPv4 Address=
10.255.224.21 - IPv4 Subnet Mask=
255.255.255.248 - IPv6 Address=
empty - IPv4 Subnet Mask=
empty - Network=
trans103
- IP Address=
The full configuration for the core2 switch is:
- Additional IP Configuration=
trans101- IP Address=
static - IPv4 Address=
10.255.224.6 - IPv4 Subnet Mask=
255.255.255.248 - IPv6 Address=
empty - IPv4 Subnet Mask=
empty - Network=
trans101
- IP Address=
- Additional IP Configuration=
trans102- IP Address=
static - IPv4 Address=
10.255.224.14 - IPv4 Subnet Mask=
255.255.255.248 - IPv6 Address=
empty - IPv4 Subnet Mask=
empty - Network=
trans102
- IP Address=
- Additional IP Configuration=
trans103- IP Address=
static - IPv4 Address=
10.255.224.22 - IPv4 Subnet Mask=
255.255.255.248 - IPv6 Address=
empty - IPv4 Subnet Mask=
empty - Network=
trans103
- IP Address=
Next, define a port profile either in the switch template or locally on each service block function switch. In our example we configure the following:
- Name=
peering-uplinks - Port Enabled=
Enabled - Mode=
Trunk - Port Network=
None - Trunk Network=
trans101andtrans102andtrans103 - Enable MTU=
Checked - MTU=
9018
For the SRX chassis cluster, the uplink port configuration on both service block functions requires a different ESI-LAG per uplink node. Hence, the following port configuration for the SRX chassis cluster uplinks are applied:
- Uplink to node0:
- Port IDs=
ge-0/0/5 - Interface=
L2 Interface - Configuration Profile=
peering-uplinks - Port Aggregation=
Enabled- AE Index=
10 - ESI-LAG=
Enabled
- AE Index=
- Port IDs=
- Uplink to node1:
- Port IDs=
ge-0/0/6 - Interface=
L2 Interface - Configuration Profile=
peering-uplinks - Port Aggregation=
Enabled- AE Index=
11 - ESI-LAG=
Enabled
- AE Index=
- Port IDs=
For the SSR HA cluster, the uplink port configuration on both service block functions can have a single LAG for all nodes. Hence, the following port configuration for the SSR cluster uplinks are applied:
- Port IDs=
ge-0/0/5-6 - Interface=
L2 Interface - Configuration Profile=
peering-uplinks - Port Aggregation=
Enabled- AE Index=
10 - ESI-LAG=
Enabled
- AE Index=
In the next step, customize each VRF on both service blocks by adding the transport VLAN to the overlay VLANs already imported from the EVPN fabric configuration.
When adding new VLANs to the campus fabric later, you must also add them to the customized VRFs on both service blocks.
This step is performed on both service blocks and works the same way on each; you must configure the following:
- VRF Configuration:
- Override Site/Template Settings=
Checked - Configuration=
Enabled - Instance=
customera- Override Site/Template Settings=
Checked - Add to existing Networks=
trans101
- Override Site/Template Settings=
- Instance=
customerb- Override Site/Template Settings=
Checked - Add to existing Networks=
trans102
- Override Site/Template Settings=
- Instance=
devices- Override Site/Template Settings=
Checked - Add to existing Networks=
trans103
- Override Site/Template Settings=
- Override Site/Template Settings=
You can now proceed with the BGP configuration, beginning with the creation of policies. Configure the following import routing policy to receive the default route from the WAN router:
- Name=
import-default - Term=
1- Name=
default - Prefix=
0.0.0.0/0 - Protocol=
BGP - Then=
Accept
- Name=
Configure the following export routing policy to announce the fabric overlay networks and the overlay loopback IP ranges used for DHCP relay:
- Name=
export-vrfs - Term=
1- Name=
exclude-default - Prefix=
0.0.0.0/0 - Protocol=
None - Then=
Reject
- Name=
- Term=
2- Name=
fabric-all-no-hosts - Prefix=
0.0.0.0/0-30 - Protocol=
None - Then=
Accept
- Name=
- Term=
3- Name=
overlaylo0 - Prefix=
172.16.192.0/23-32 - Protocol=
None - Then=
Accept
- Name=
Be sure to include the overlay loopback host routes as a second rule.
The overlay loopback configuration suggested earlier is not required for EVPN Multihoming or CRB campus fabrics. Refer to the JVD for more details.
Next, define the BGP peering groups and neighbors for each VRF. Configure the following BGP groups:
- Name=
customera- Type=
External - Network=
trans101 - BFD Interval=
1000 - Local AS=
64911 - Hold Time=
90 - Export=
export-vrfs - Import=
import-default - Neighbour=
1- IP Address=
10.255.224.1 - Neighbor AS=
64901 - Hold Time=
90
- IP Address=
- Type=
- Name=
customerb- Type=
External - Network=
trans102 - BFD Interval=
1000 - Local AS=
64911 - Hold Time=
90 - Export=
export-vrfs - Import=
import-default - Neighbour=
1- IP Address=
10.255.224.9 - Neighbor AS=
64901 - Hold Time=
90
- IP Address=
- Type=
- Name=
devices- Type=
External - Network=
trans103 - BFD Interval=
1000 - Local AS=
64911 - Hold Time=
90 - Export=
export-vrfs - Import=
import-default - Neighbour=
1- IP Address=
10.255.224.17 - Neighbor AS=
64901 - Hold Time=
90
- IP Address=
- Type=
Additional Junos CLI configuration on the service block switches is required. Without it, the fabric node responds only on the local IRB IP address when the WAN router sends ARP requests, while the WAN router may send those requests to a different interface due to LAG load balancing. Should you forget adding these changes it may happen that the BGP peering sessions cannot be established randomly, which is a symptom for the missing configuration.
Depending on the devices used as service block function, the fabric type and features like IPv4 or IPv6 underlay chosen you may require the following two additional Junos CLI line on each service block function.
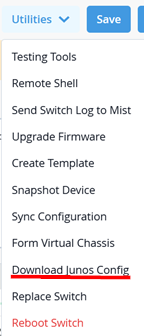
- On each service block function switch go to Utilities ->
Download Junos Config as shown below
Figure 9: Download Junos Config
- Open the downloaded file in an editor and search for the string
do-not-advertisesimilar to below example.Figure 10: Search for do-not-advertise string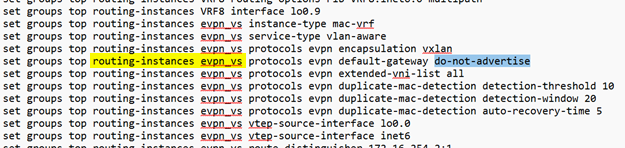
- If the string does not appear, then no change is needed to be made in your configuration. This is usually the case for EVPN Multihoming and CRB fabrics. You can then ignore the other instructions following now.
- If the string is found you require one out of two possible
configuration changes applied on each service block function.
- If the line where the string is found also contains the string
routing-instances evpn_vsas in above example then the configuration change below has to be applied as mandatory change. This is because the system uses theevpn_vsvirtual switch rather than the default switch and our configuration change must be valid for this.delete groups top routing-instances evpn_vs protocols evpn default-gateway do-not-advertise set groups top routing-instances evpn_vs protocols evpn default-gateway no-gateway-community
- In all other cases you should apply the following configuration as the system still uses the default virtual switch.
delete groups top protocols evpn default-gateway do-not-advertise
set groups top protocols evpn default-gateway no-gateway-community
- If the line where the string is found also contains the string
SSR HA Cluster Setup
Our lab had two SSR1500s in HA cluster mode.
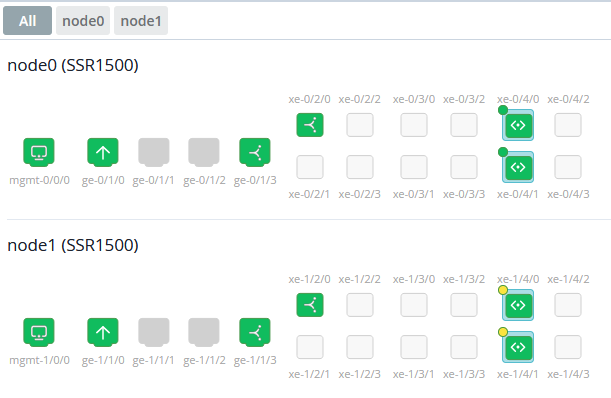
You need to ensure they are on the same firmware version:
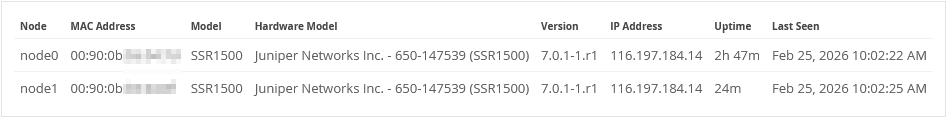
Below is the JSON file that was used for the hub profile:
{
  "ip_configs": {
    "VRF1": {
      "type": "static",
      "ip": "10.255.224.1"
    },
    "VRF2": {
      "type": "static",
      "ip": "10.255.224.9"
    },
    "VRF3": {
      "type": "static",
      "ip": "10.255.224.17"
    }
  },
  "dhcpd_config": {
    "enabled": true
  },
  "port_config": {
    "ge-0/0/0": {
      "name": "WAN-N0",
      "usage": "wan",
      "aggregated": false,
      "redundant": false,
      "critical": false,
      "disabled": false,
      "wan_type": "broadband",
      "ip_config": {
        "type": "static",
        "ip": "192.168.10.23",
        "netmask": "/24",
        "gateway": "192.168.10.1"
      },
      "disable_autoneg": false,
      "wan_source_nat": {
        "disabled": false
      },
      "vpn_paths": {
        "ssrcluster-WAN-N0.OrgOverlay": {
          "role": "hub"
        }
      }
    },
    "ge-1/0/0": {
      "name": "WAN-N1",
      "usage": "wan",
      "aggregated": false,
      "redundant": false,
      "critical": false,
      "disabled": false,
      "wan_type": "broadband",
      "ip_config": {
        "type": "static",
        "ip": "192.168.10.24",
        "netmask": "/24",
        "gateway": "192.168.10.1"
      },
      "disable_autoneg": false,
      "wan_source_nat": {
        "disabled": false
      },
      "vpn_paths": {
        "ssrcluster-WAN-N1.OrgOverlay": {
          "role": "hub"
        }
      }
    },
    "ge-0/0/2-3,ge-1/0/2-3": {
      "networks": [
        "VRF1",
        "VRF2",
        "VRF3"
      ],
      "usage": "lan",
      "mtu": 9000,
      "aggregated": true,
      "ae_disable_lacp": false,
      "ae_lacp_force_up": false,
      "ae_idx": 10,
      "redundant": true,
      "reth_idx": 3,
      "reth_node": "node0",
      "critical": false,
      "disabled": false
    }
  },
  "bgp_config": {
    "WAN": {
      "wan_name": "WAN-N0",
      "via": "wan",
      "type": "external",
      "no_readvertise_to_overlay": false,
      "local_as": 64001,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "neighbors": {
        "192.168.10.42": {
          "disabled": false,
          "neighbor_as": 64010
        }
      },
      "disable_bfd": false,
      "no_private_as": false
    },
    "VRF1": {
      "networks": [
        "VRF1"
      ],
      "via": "lan",
      "type": "external",
      "local_as": 64901,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "export_policy": "export-default",
      "import_policy": "import-fabric",
      "neighbors": {
        "10.255.224.5": {
          "disabled": false,
          "neighbor_as": 64911
        },
        "10.255.224.6": {
          "disabled": false,
          "neighbor_as": 64911
        }
      },
      "disable_bfd": false
    },
    "VRF2": {
      "networks": [
        "VRF2"
      ],
      "via": "lan",
      "type": "external",
      "local_as": 64901,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "export_policy": "export-default",
      "import_policy": "import-fabric",
      "neighbors": {
        "10.255.224.13": {
          "disabled": false,
          "neighbor_as": 64911
        },
        "10.255.224.14": {
          "disabled": false,
          "neighbor_as": 64911
        }
      },
      "disable_bfd": false
    },
    "VRF3": {
      "networks": [
        "VRF3"
      ],
      "via": "lan",
      "type": "external",
      "local_as": 64901,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "export_policy": "export-default",
      "import_policy": "import-fabric",
      "neighbors": {
        "10.255.224.21": {
          "disabled": false,
          "neighbor_as": 64911
        },
        "10.255.224.22": {
          "disabled": false,
          "neighbor_as": 64911
        }
      },
      "disable_bfd": false
    }
  },
  "routing_policies": {
    "export-default": {
      "terms": [
        {
          "matching": {
            "prefix": [
              "0.0.0.0/0"
            ],
            "protocol": [
              "bgp"
            ]
          },
          "actions": {
            "accept": true
          }
        },
        {
          "actions": {
            "accept": false
          }
        }
      ]
    },
    "import-fabric": {
      "terms": [
        {
          "matching": {
            "prefix": [
              "0.0.0.0/0"
            ],
            "protocol": [
              "bgp"
            ]
          },
          "actions": {
            "accept": false
          }
        },
        {
          "matching": {
            "prefix": [
              "0.0.0.0/0-32"
            ],
            "protocol": [
              "bgp"
            ]
          },
          "actions": {
            "accept": true
          }
        }
      ]
    }
  },
  "path_preferences": {
    "WAN": {
      "strategy": "ordered",
      "paths": [
        {
          "name": "WAN-N0",
          "type": "wan"
        },
        {
          "name": "WAN-N1",
          "type": "wan"
        }
      ]
    },
    "LAN": {
      "strategy": "ecmp",
      "paths": [
        {
          "type": "local",
          "networks": [
            "VRF1"
          ]
        },
        {
          "type": "local",
          "networks": [
            "VRF2"
          ]
        },
        {
          "type": "local",
          "networks": [
            "VRF3"
          ]
        }
      ]
    }
  },
  "service_policies": [
    {
      "name": "hairpin-traffic",
      "tenants": [
        "fabric1",
        "fabric2",
        "fabric3"
      ],
      "services": [
        "fabric"
      ],
      "action": "allow",
      "idp": {
        "enabled": false
      }
    },
    {
      "name": "internet",
      "tenants": [
        "fabric1",
        "fabric2",
        "fabric3"
      ],
      "services": [
        "any"
      ],
      "action": "allow",
      "path_preference": "WAN",
      "idp": {
        "enabled": false
      }
    },
    {
      "name": "default-route-inject",
      "tenants": [
        "default-helper"
      ],
      "services": [
        "default"
      ],
      "action": "allow",
      "path_preference": "LAN",
      "idp": {
        "enabled": false
      }
    }
  ],
  "name": "ssrcluster",
  "type": "gateway"
}
If you are not using the JSON file, follow the manual setup described below. Under Organization -> Applications, add a custom application for “fabric” that includes all RFC1918 networks, and another for default route injection, which is currently required to advertise a default route toward the EVPN fabric. Create the following applications:
- Name=
fabric- Type=
Custom Apps - IP Addresses=
10.0.0.0/8and172.16.0.0/12and192.168.0.0/16
- Type=
- Name=
default
- Type=
Custom Apps - IP Addresses=
0.0.0.0/0
Define the following networks:
- Each of the three RFC1918 networks that may be used as overlay
networks in the EVPN fabric must be defined. We use the naming
convention
fabricX. These networks must be advertised to the overlay, other spokes, and LAN-side BGP neighbors to support hairpin traffic between VRFs. - Define a network for each BGP peering per VRF, including the
VLAN ID and the correct
/29IP address information. Do not enable propagation to the overlay. In this example, three networks are defined using the naming conventionVRFX. - A default route must be injected toward the EVPN fabric. To
achieve this, create a
default-helpernetwork with a/32host address that falls outside thefabric?networks already in use. This network must be advertised to the overlay as shown below.
The intended configuration is illustrated below.
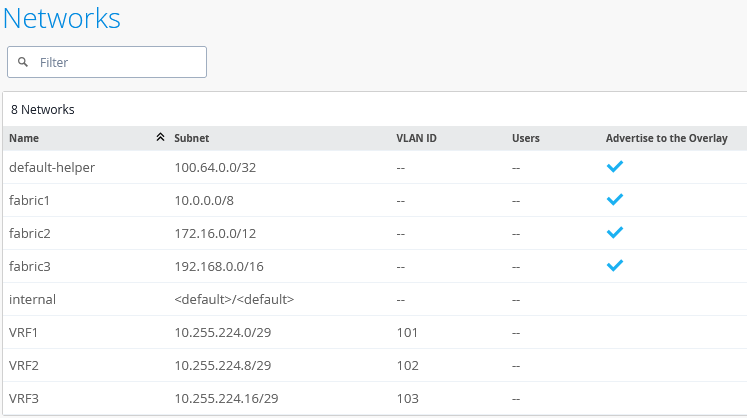
Create the first network:
- Name=
fabric1 - Subnet IPv4 Address=
10.0.0.0 - IPv4 Prefix Length=
8 - VLAN ID=
<empty> - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Checked/Enabled - Advertise to other Spokes=
Checked/Enabled - Advertise to Hub LAN BGP
Neighbor=
Checked/Enabled
Create the second network:
- Name=
fabric2 - Subnet IPv4 Address=
172.16.0.0 - IPv4 Prefix Length=
12 - VLAN ID=
<empty> - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Checked/Enabled - Advertise to other Spokes=
Checked/Enabled - Advertise to Hub LAN BGP
Neighbor=
Checked/Enabled
Create the third network:
- Name=
fabric3 - Subnet IPv4 Address=
192.168.0.0 - IPv4 Prefix Length=
16 - VLAN ID=
<empty> - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Checked/Enabled - Advertise to other Spokes=
Checked/Enabled - Advertise to Hub LAN BGP
Neighbor=
Checked/Enabled
Create the fourth network:
- Name=
VRF1 - Subnet IPv4 Address=
10.255.224.0 - IPv4 Prefix Length=
29 - VLAN ID=
101 - Access to MIST Cloud=
Unchecked/Disabled - Advertise to the Overlay=
Unchecked/Disabled - Networks Not Directly Attached=
fabric1andfabric2andfabric3
Create the fifth network:
- Name=
VRF2 - Subnet IP Address=
10.255.224.8 - Prefix Length=
29 - VLAN ID=
102 - Access to MIST Cloud=
Unchecked/Disabled - Advertise to the Overlay=
Unchecked/Disabled - Networks Not Directly Attached=
fabric1andfabric2andfabric3
Create the sixth network:
- Name=
VRF3 - Subnet IP Address=
10.255.224.16 - Prefix Length=
29 - VLAN ID=
103 - Access to MIST Cloud=
Unchecked/Disabled - Advertise to the Overlay=
Unchecked/Disabled - Networks Not Directly Attached=
fabric1andfabric2andfabric3
Create a seventh network, which is required to inject a default route. The interface IP address used must fall outside the range of the RFC1918 networks. However, the option to advertise to the Hub LAN BGP neighbor must be enabled for the injection to take effect:
- Name=
default-helper - Subnet IP Address=
100.64.0.0 - Prefix Length=
32 - VLAN ID=
none - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Checked/Enabled - Advertise to other Spokes=
Unchecked/Disabled - Advertise to Hub LAN BGP
Neighbor=
Checked/Enabled
In our design, static IP addresses were used on the WAN interfaces for the lab, and we recommend refining this approach for a production environment.
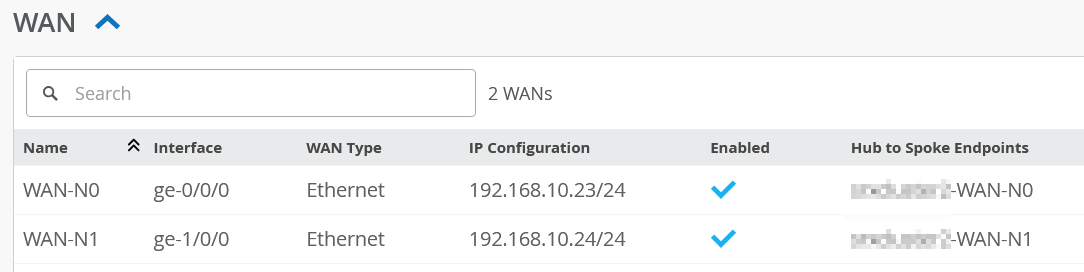
Next is the configuration of the LAN interfaces in the following design. Configure the following three LAN IP gateways:
- First GW
- Network=
VRF1 - IP Address=
10.255.224.1 - Prefix Length=
29
- Network=
- Second GW
- Network=
VRF2 - IP Address=
10.255.224.9 - Prefix Length=
29
- Network=
- Third GW
- Network=
VRF3 - IP Address=
10.255.224.17 - Prefix Length=
29
- Network=
Then, configure the LAG with the LAN interfaces towards the fabric like the following:
- Interface=
ge-0/0/2,ge-0/0/3,ge-1/0/2,ge-1/0/3 - Port Aggregation=
Checked/Enabled- Disable LACP=
Unchecked - Enable Force Up=
Unchecked - AE Index=
10
- Disable LACP=
- Redundant=
Checked/Enabled- Redundant Index=
1 - Redundant Group=
empty(default) - Primary Node=
node0
- Redundant Index=
- Networks=
VRF1andVRF2andVRF3
The result should look like the image shown below.
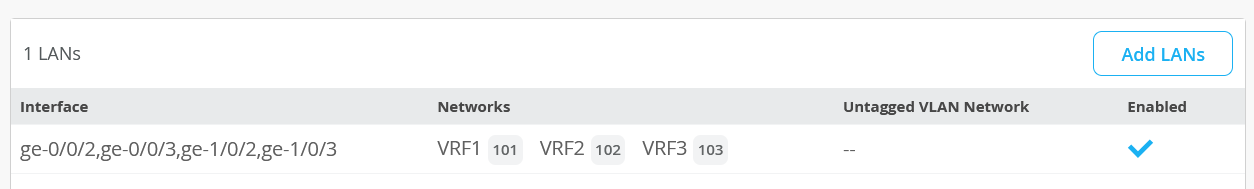
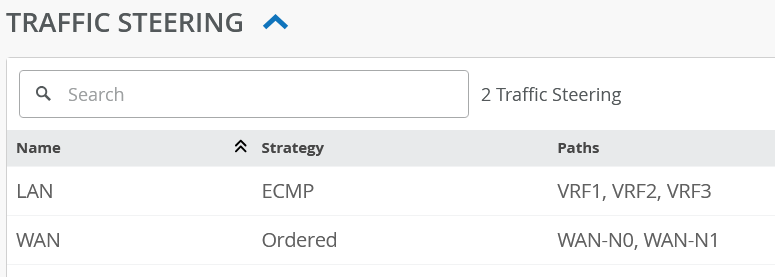
- The traffic steering rules are straightforward, as shown below: Create a LAN traffic steering rule using ECMP, including all VRF peering interfaces.
- Create a WAN traffic steering rule that includes both of your WAN interfaces.
For application policies, you need to configure the following:
- Rule=
1- Name=
hairpin-traffic - Network=
fabric1andfabric2andfabric3 - Application=fabric
- Traffic Steering=
N/A(do not configure any traffic steering on this rule for the SSR)
- Name=
- Rule=
2- Name=
internet - Network=
fabric1andfabric2andfabric3 - Application=
any - Traffic Steering=
WAN
- Name=
- Rule=
3- Name=
default-route-inject - Network=
default-helper - Application=
default - Traffic Steering=
LAN
- Name=
You can now begin the BGP configuration by creating the required routing policies.
Configure the following export routing policy:
- Name=
export-default - Term=
1- Prefix=
0.0.0.0/0 - Protocol=
BGP - Then=
Accept
- Prefix=
- Term=2
- Prefix=
N/A(do not set) - Protocol=
BGP - Then=
Reject
- Prefix=
Configure the following import routing policy:
- Name=
import-fabric - Term=
1- Prefix=
0.0.0.0/0 - Protocol=
BGP - Then=
Reject
- Prefix=
- Term=
2- Prefix=
0.0.0.0/0-32 - Protocol=
BGP - Then=
Accept
- Prefix=
Next, define the BGP peering groups and the two neighbors for each VRF, as part of the service block configuration.
- Configure the first BGP group:
- Name=
VRF1 - Peering Network=
LANandVRF1 - Advertise to the Overlay=
Checked/Enabled - Type=
External - Local AS=
64901 - Hold Time=
90 - Graceful Restart Time=
120 - Export=
export-default - Import=
import-fabric - Neighbour=
1- Neighbor=
Enabled - IP Address=
10.255.224.5 - Neighbor AS=
64911
- Neighbor=
- Neighbour=
2- Neighbor=
Enabled - IP Address=
10.255.224.6 - Neighbor AS=
64911
- Neighbor=
- Name=
- Configure the second BGP group:
- Name=
VRF2 - Peering Network=
LANandVRF2 - Advertise to the Overlay=
Checked/Enabled - Type=
External - Local AS=
64901 - Hold Time=
90 - Graceful Restart Time=
120 - Export=
export-default - Import=
import-fabric - Neighbour=
1- Neighbor=
Enabled - IP Address=
10.255.224.13 - Neighbor AS=
64911
- Neighbor=
- Neighbour=
2- Neighbor=
Enabled - IP Address=
10.255.224.14 - Neighbor AS=
64911
- Neighbor=
- Name=
- Configure the third BGP group:
- Name=
VRF3 - Peering Network=
LANandVRF3 - Advertise to the Overlay=
Checked/Enabled - Type=
External - Local AS=
64901 - Hold Time=
90 - Graceful Restart Time=
120 - Export=
export-default - Import=
import-fabric - Neighbour=
1- Neighbor=
Enabled - IP Address=
10.255.224.21 - Neighbor AS=
64911
- Neighbor=
- Neighbour=
2- Neighbor=
Enabled - IP Address=
10.255.224.22 - Neighbor AS=
64911
- Neighbor=
- Name=
SRX Chassis Cluster Setup
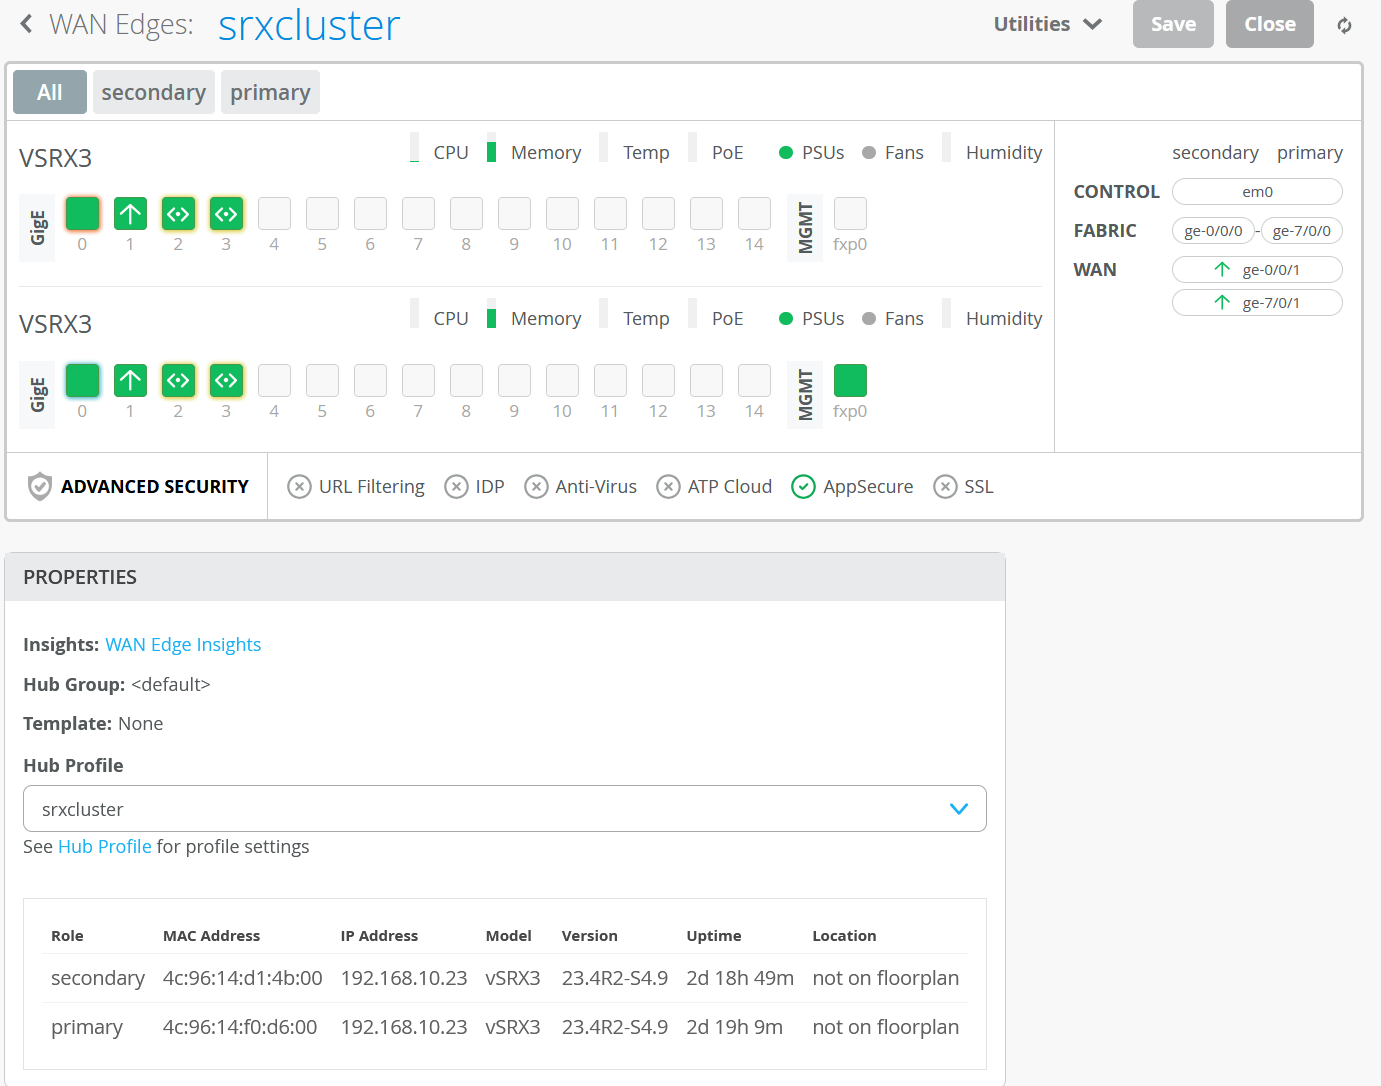
In our lab, we built the SRX chassis cluster based on vSRX3 VMs as seen below.
Below is the JSON file that was used for the hub profile.
{
  "ip_configs": {
    "VRF1": {
      "type": "static",
      "ip": "10.255.224.1"
    },
    "VRF2": {
      "type": "static",
      "ip": "10.255.224.9"
    },
    "VRF3": {
      "type": "static",
      "ip": "10.255.224.17"
    }
  },
  "dhcpd_config": {
    "enabled": true
  },
  "port_config": {
    "ge-0/0/1": {
      "name": "WAN-N0",
      "usage": "wan",
      "aggregated": false,
      "redundant": false,
      "critical": false,
      "disabled": false,
      "wan_type": "broadband",
      "ip_config": {
        "type": "static",
        "ip": "192.168.10.23",
        "netmask": "/24",
        "gateway": "192.168.10.1"
      },
      "disable_autoneg": false,
      "wan_source_nat": {
        "disabled": false
      },
      "vpn_paths": {
        "srxcluster-WAN-N0.OrgOverlay": {
          "role": "hub"
        }
      }
    },
    "ge-7/0/1": {
      "name": "WAN-N1",
      "usage": "wan",
      "aggregated": false,
      "redundant": false,
      "critical": false,
      "disabled": false,
      "wan_type": "broadband",
      "ip_config": {
        "type": "static",
        "ip": "192.168.10.24",
        "netmask": "/24",
        "gateway": "192.168.10.1"
      },
      "disable_autoneg": false,
      "wan_source_nat": {
        "disabled": false
      },
      "vpn_paths": {
        "srxcluster-WAN-N1.OrgOverlay": {
          "role": "hub"
        }
      }
    },
    "ge-0/0/2-3,ge-7/0/2-3": {
      "networks": [
        "VRF1",
        "VRF2",
        "VRF3"
      ],
      "usage": "lan",
      "mtu": 9018,
      "aggregated": true,
      "ae_disable_lacp": false,
      "ae_lacp_force_up": false,
      "redundant": true,
      "reth_idx": 3,
      "reth_node": "node0",
      "redundant_group": 3,
      "critical": false,
      "disabled": false
    }
  },
  "bgp_config": {
    "VRF1": {
      "networks": [
        "VRF1"
      ],
      "via": "lan",
      "type": "external",
      "local_as": 64901,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "export_policy": "export-default",
      "import_policy": "import-fabric",
      "neighbors": {
        "10.255.224.5": {
          "disabled": false,
          "neighbor_as": 64911
        },
        "10.255.224.6": {
          "disabled": false,
          "neighbor_as": 64911
        }
      },
      "disable_bfd": false
    },
    "VRF2": {
      "networks": [
        "VRF2"
      ],
      "via": "lan",
      "type": "external",
      "local_as": 64901,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "export_policy": "export-default",
      "import_policy": "import-fabric",
      "neighbors": {
        "10.255.224.13": {
          "disabled": false,
          "neighbor_as": 64911
        },
        "10.255.224.14": {
          "disabled": false,
          "neighbor_as": 64911
        }
      },
      "disable_bfd": false
    },
    "VRF3": {
      "networks": [
        "VRF3"
      ],
      "via": "lan",
      "type": "external",
      "local_as": 64901,
      "hold_time": 90,
      "graceful_restart_time": 120,
      "export_policy": "export-default",
      "import_policy": "import-fabric",
      "neighbors": {
        "10.255.224.21": {
          "disabled": false,
          "neighbor_as": 64911
        },
        "10.255.224.22": {
          "disabled": false,
          "neighbor_as": 64911
        }
      },
      "disable_bfd": false
    }
  },
  "routing_policies": {
    "export-default": {
      "terms": [
        {
          "matching": {
            "prefix": [
              "0.0.0.0/0"
            ],
            "protocol": [
              "static"
            ]
          },
          "actions": {
            "accept": true
          }
        }
      ]
    },
    "import-fabric": {
      "terms": [
        {
          "matching": {
            "prefix": [
              "0.0.0.0/0"
            ],
            "protocol": [
              "bgp"
            ]
          },
          "actions": {
            "accept": false
          }
        },
        {
          "matching": {
            "prefix": [
              "0.0.0.0/0-32"
            ],
            "protocol": [
              "bgp"
            ]
          },
          "actions": {
            "accept": true
          }
        }
      ]
    }
  },
  "path_preferences": {
    "WAN": {
      "strategy": "ordered",
      "paths": [
        {
          "name": "WAN-N0",
          "type": "wan"
        },
        {
          "name": "WAN-N1",
          "type": "wan"
        }
      ]
    },
    "LAN": {
      "strategy": "ecmp",
      "paths": [
        {
          "type": "local",
          "networks": [
            "VRF1"
          ]
        },
        {
          "type": "local",
          "networks": [
            "VRF2"
          ]
        },
        {
          "type": "local",
          "networks": [
            "VRF3"
          ]
        }
      ]
    }
  },
  "service_policies": [
    {
      "name": "hairpin-traffic",
      "tenants": [
        "fabric.VRF1",
        "fabric.VRF2",
        "fabric.VRF3"
      ],
      "services": [
        "fabric"
      ],
      "action": "allow",
      "path_preference": "LAN",
      "idp": {
        "enabled": false
      }
    },
    {
      "name": "internet",
      "tenants": [
        "fabric.VRF1",
        "fabric.VRF2",
        "fabric.VRF3"
      ],
      "services": [
        "any"
      ],
      "action": "allow",
      "path_preference": "WAN",
      "idp": {
        "enabled": false
      }
    }
  ],
  "additional_config_cmds": [
    "#",
    "set security zones security-zone VRF1 host-inbound-traffic system-services ping",
    "set security zones security-zone VRF2 host-inbound-traffic system-services ping",
    "set security zones security-zone VRF3 host-inbound-traffic system-services ping",
    "#",
    ""
  ],
  "ospf_areas": {},
  "extra_routes": {},
  "vrf_instances": {},
  "tunnel_configs": {},
  "tunnel_provider_options": {
    "jse": {},
    "zscaler": {}
  },
  "oob_ip_config": {
    "type": "dhcp",
    "node1": {
      "type": "dhcp"
    }
  },
  "ospf_config": {
    "enabled": false,
    "areas": {}
  },
  "remote_syslog": {
    "enabled": false,
    "files": [],
    "servers": [],
    "users": [],
    "time_format": "",
    "console": {
      "contents": []
    }
  },
  "name": "srxcluster",
  "type": "gateway"
}
If you are not using the JSON file, follow the manual setup described below.
Under Organization -> Applications, add a custom application for “fabric” with all RFC1918 networks. Create the application as follows:
- Name=
fabric - Type=
Custom Apps - IP Addresses=
10.0.0.0/8and172.16.0.0/12and192.168.0.0/16
Under Organization -> Networks, add the subnets for each VRF. It is mandatory to use the "Users" object with RFC1918 networks, as tested. Advertise to the Overlay is optional and is only required for the default-helper network to inject a default route toward the EVPN fabric.
- Create first Network:
- Name=
VRF1 - Subnet IP Address=
10.255.224.0 - Prefix Length=
29 - VLAN ID=
101 - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Unchecked/Disabled - Users
- Name=
fabric - IP Prefix1=
10.0.0.0/8 - IP Prefix2=
172.16.0.0/12 - IP Prefix3=
192.168.0.0/16
- Name=
- Name=
- Create second Network:
- Name=
VRF2 - Subnet IP Address=
10.255.224.8 - Prefix Length=
29 - VLAN ID=
102 - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Unchecked/Disabled - Users
- Name=
fabric - IP Prefix1=
10.0.0.0/8 - IP Prefix2=
172.16.0.0/12 - IP Prefix3=
192.168.0.0/16
- Name=
- Name=
- Create third Network:
- Name=
VRF3 - Subnet IP Address=
10.255.224.16 - Prefix Length=
29 - VLAN ID=
103 - Access to MIST Cloud=
Checked/Enabled - Advertise to the Overlay=
Unchecked/Disabled - Users
- Name=
fabric - IP Prefix1=
10.0.0.0/8 - IP Prefix2=
172.16.0.0/12 - IP Prefix3=
192.168.0.0/16
- Name=
- Name=
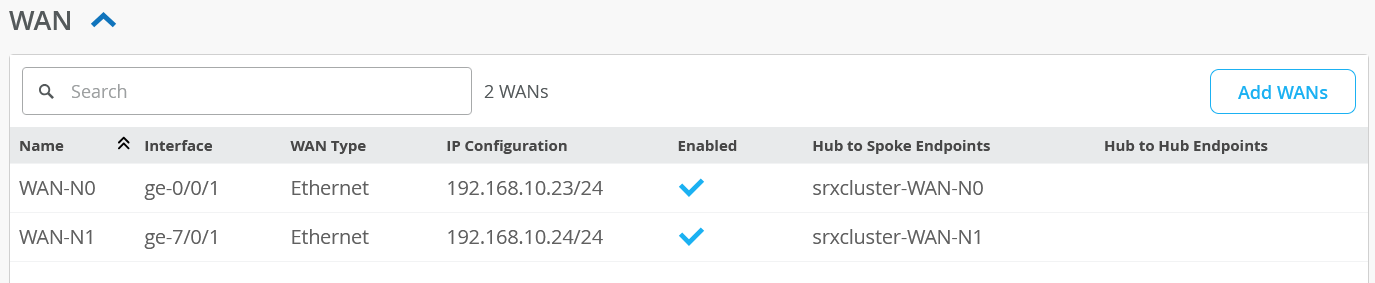
In our design, static IP addresses were used on the WAN interfaces for the lab, and we recommend refining this approach for a production environment.
Next is the configuration of the LAN interfaces. Configure the following three LAN IP gateways:
- First GW
- Network=
VRF1 - IP Address=
10.255.224.1 - Prefix Length=
29
- Network=
- Second GW
- Network=
VRF2 - IP Address=
10.255.224.9 - Prefix Length=
29
- Network=
- Third GW
- Network=
VRF3 - IP Address=
10.255.224.17 - Prefix Length=
29
- Network=
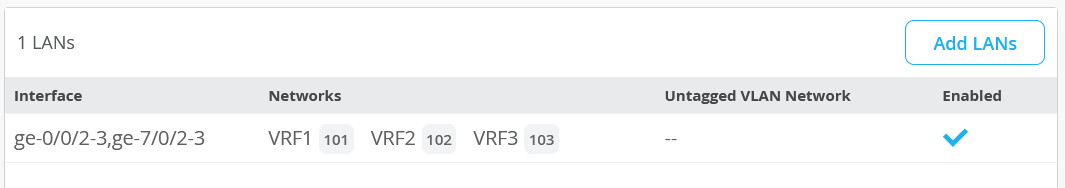
Then, configure the LAG with the LAN interfaces towards the fabric as follows:
- Interface=
ge-0/0/2-3,ge-7/0/2-3 - Port Aggregation=
Checked/Enabled- Disable LACP=
Unchecked - Enable Force Up=
Unchecked - AE Index=
10
- Disable LACP=
- Redundant=
Checked/Enabled- Redundant Index=
3 - Redundant Group=
3 - Primary Node=
node0
- Redundant Index=
- Networks=
VRF1andVRF2andVRF3
The result should look like the image shown below.
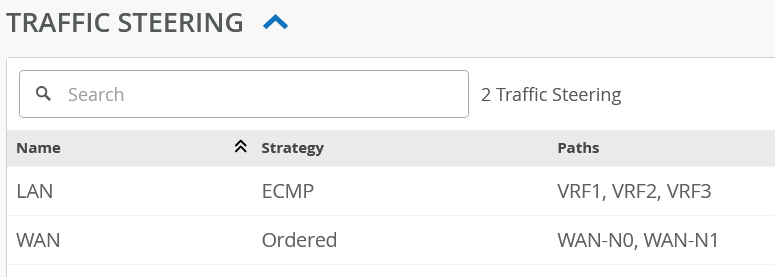
The traffic steering rules are straightforward, as shown below:
- Create a LAN traffic steering rule using ECMP, including all VRF peering interfaces.
- Create a WAN traffic steering rule that includes both of your WAN interfaces.
For application policies you need to configure the following:
- Rule=
1- Name=
hairpin-traffic - Network=
fabric.VRF1andfabric.VRF2andfabric.VRF3 - Application=
fabric - Traffic Steering=
LAN
- Name=
- Rule=
2- Name=
internet - Network=
fabric.VRF1andfabric.VRF2andfabric.VRF3 - Application=
any - Traffic Steering=
WAN
- Name=
You can now begin the BGP configuration by creating the required routing policies. Configure the following routing policy:
- Name=
export-default - Term=
1- Prefix=
0.0.0.0/0 - Protocol=
BGP - Then=
Accept
- Prefix=
- Term=
2- Prefix=
N/A(do not set) - Protocol=
BGP - Then=
Reject
- Prefix=
Configure the following routing policy:
- Name=
import-fabric - Term=
1- Prefix=
0.0.0.0/0 - Protocol=
BGP - Then=
Reject
- Prefix=
- Term=
2- Prefix=
0.0.0.0/0-32 - Protocol=
BGP - Then=
Accept
- Prefix=
Next, define the BGP peering groups and the two neighbors for each VRF, as part of the service block configuration.
- Configure the first BGP group:
- Name=
VRF1 - Peering Network=
LANandVRF1 - Advertise to the Overlay=
Checked/Enabled - Type=
External - Local AS=
64901 - Hold Time=
90 - Graceful Restart Time=
120 - Export=
export-default - Import=
import-fabric - Neighbour=
1- Neighbor=
Enabled - IP Address=
10.255.224.5 - Neighbor AS=
64911
- Neighbor=
- Neighbour=
2- Neighbor=
Enabled - IP Address=
10.255.224.6 - Neighbor AS=
64911
- Neighbor=
- Name=
- Configure the second BGP group:
- Name=
VRF2 - Peering Network=
LANandVRF2 - Advertise to the Overlay=
Checked/Enabled - Type=
External - Local AS=
64901 - Hold Time=
90 - Graceful Restart Time=
120 - Export=
export-default - Import=
import-fabric - Neighbour=
1- Neighbor=
Enabled - IP Address=
10.255.224.13 - Neighbor AS=
64911
- Neighbor=
- Neighbour=
2- Neighbor=
Enabled - IP Address=
10.255.224.14 - Neighbor AS=
64911
- Neighbor=
- Name=
- Configure the third BGP group:
- Name=
VRF3 - Peering Network=
LANandVRF3 - Advertise to the Overlay=
Checked/Enabled - Type=
External - Local AS=
64901 - Hold Time=
90 - Graceful Restart Time=
120 - Export=
export-default - Import=
import-fabric - Neighbour=
1- Neighbor=
Enabled - IP Address=
10.255.224.21 - Neighbor AS=
64911
- Neighbor=
- Neighbour=
2- Neighbor=
Enabled - IP Address=
10.255.224.22 - Neighbor AS=
64911
- Neighbor=
- Name=
OPTIONAL: On the SRX, we can add the below configuration to be able to ping the LAN interfaces on SRX chassis cluster for debugging.
set security zones security-zone VRF1 host-inbound-traffic system-services ping
set security zones security-zone VRF2 host-inbound-traffic system-services ping
set security zones security-zone VRF3 host-inbound-traffic system-services ping
Testing Your Applied Configuration
The output below was gathered from the first service block switch:
root@core1> show interfaces terse
Interface               Admin Link Proto    Local                 Remote
.
ge-0/0/5                up    up
ge-0/0/5.0              up    up   aenet    --> ae10.0
ge-0/0/6                up    up
ge-0/0/6.0              up    up   aenet    --> ae11.0
.
ae10                    up    up
ae10.0                  up    up   eth-switch
ae11                    up    up
ae11.0                  up    up   eth-switch
.
irb.0                   up    down inet
                                   multiservice
irb.101                 up    up   inet     10.255.224.5/29
                                   multiservice
irb.102                 up    up   inet     10.255.224.13/29
                                   multiservice
irb.103                 up    up   inet     10.255.224.21/29
                                   multiservice
.
lo0.0                   up    up   inet     172.16.254.2        --> 0/0
lo0.1                   up    up   inet     172.16.192.6        --> 0/0
lo0.2                   up    up   inet     172.16.192.7        --> 0/0
lo0.3                   up    up   inet     172.16.192.8        --> 0/0
.
root@core1> show lldp neighbors
Local Interface    Parent Interface    Chassis Id                               Port info          System Name
ge-0/0/1           -                   2c:6b:f5:01:eb:c0                        evpn_uplink-to-020004fd104e dist1
ge-0/0/2           -                   2c:6b:f5:79:0d:c0                        evpn_uplink-to-020004fd104e dist2
ge-0/0/5           ae10                00:10:db:ff:10:00                        ge-0/0/2            wanrouter_node0
ge-0/0/6           ae11                00:10:db:ff:10:00                        ge-7/0/2            wanrouter_node0
.
root@core1> show lacp interfaces
Aggregated interface: ae10
    LACP state:           Role   Exp   Def  Dist  Col  Syn  Aggr  Timeout  Activity
      ge-0/0/5           Actor    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-0/0/5         Partner    No    No   Yes  Yes  Yes   Yes     Fast    Active
    LACP protocol:        Receive State  Transmit State          Mux State
      ge-0/0/5                  Current   Fast periodic Collecting distributing
.
Aggregated interface: ae11
    LACP state:           Role   Exp   Def  Dist  Col  Syn  Aggr  Timeout  Activity
      ge-0/0/6           Actor    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-0/0/6         Partner    No    No   Yes  Yes  Yes   Yes     Fast    Active
    LACP protocol:        Receive State  Transmit State          Mux State
      ge-0/0/6                  Current   Fast periodic Collecting distributing
.
root@core1> show bgp summary
.
Threading mode: BGP I/O
Default eBGP mode: advertise - accept, receive - accept
Groups: 5 Peers: 7 Down peers: 0
Table          Tot Paths  Act Paths Suppressed    History Damp State    Pending
inet.0
                       8          8          0          0          0          0
bgp.evpn.0
                     208        104          0          0          0          0
Peer                     AS      InPkt     OutPkt    OutQ   Flaps Last Up/Dwn State|#Active/Received/Accepted/Damped...
10.255.224.1          64901      50894      50815       0       0 2w2d 3:42:31 Establ
  customera.inet.0: 1/1/1/0
10.255.224.9          64901      50893      50818       0       0 2w2d 3:42:30 Establ
  customerb.inet.0: 1/1/1/0
10.255.224.17         64901      50892      50818       0       0 2w2d 3:42:15 Establ
  devices.inet.0: 1/1/1/0
.
root@core1> show route table customera.inet.0
.
customera.inet.0: 11 destinations, 17 routes (11 active, 0 holddown, 0 hidden)
@ = Routing Use Only, # = Forwarding Use Only
+ = Active Route, - = Last Active, * = Both
0.0.0.0/0          *[BGP/170] 2w2d 03:44:01, localpref 100
                      AS path: 64901 I, validation-state: unverified
                    >  to 10.255.224.1 via irb.101
                    [EVPN/170] 2w2d 03:43:58
                    >  to 10.255.240.7 via ge-0/0/1.0
                       to 10.255.240.9 via ge-0/0/2.0
10.91.91.0/24      *[EVPN/170] 05:17:19
                       to 10.255.240.7 via ge-0/0/1.0
                    >  to 10.255.240.9 via ge-0/0/2.0
10.99.99.0/24      *[Direct/0] 2w2d 03:00:05
                    >  via irb.1099
                    [EVPN/170] 2w2d 02:59:49
                       to 10.255.240.7 via ge-0/0/1.0
                    >  to 10.255.240.9 via ge-0/0/2.0
                    [EVPN/170] 05:17:19
                       to 10.255.240.7 via ge-0/0/1.0
                    >  to 10.255.240.9 via ge-0/0/2.0
.
root@core1> show ethernet-switching table
.
MAC flags (S - static MAC, D - dynamic MAC, L - locally learned, P - Persistent static, C - Control MAC
           SE - statistics enabled, NM - non configured MAC, R - remote PE MAC, O - ovsdb MAC,
           B - Blocked MAC)
.
Ethernet switching table : 17 entries, 17 learned
Routing instance : evpn_vs
   Vlan                MAC                 MAC       GBP    Logical                SVLBNH/      Active
   name                address             flags     tag    interface              VENH Index   source
   trans1              00:10:db:ff:10:03   DLR              ae10.0
   trans1              2c:6b:f5:94:c3:f0   DRP              vtep.32771                          172.16.254.1
   trans2              00:10:db:ff:10:03   DLR              ae10.0
   trans2              2c:6b:f5:94:c3:f0   DRP              vtep.32771                          172.16.254.1
   trans3              00:10:db:ff:10:03   DLR              ae10.0
   trans3              2c:6b:f5:94:c3:f0   DRP              vtep.32771                          172.16.254.1
.
root@core1> show evpn database
Instance: evpn_vs
VLAN  DomainId  MAC address        Active source                  Timestamp        IP address
     10101      00:10:db:ff:10:03  00:11:00:00:00:01:00:01:02:0a  Jul 09 12:08:46  10.255.224.1
     10101      2c:6b:f5:94:c3:f0  172.16.254.1                   Jul 09 11:53:07  10.255.224.6
     10101      2c:6b:f5:d8:15:f0  irb.101                        Jul 09 11:53:07  10.255.224.5
     10102      00:10:db:ff:10:03  00:11:00:00:00:01:00:01:02:0a  Jul 09 12:08:46  10.255.224.9
     10102      2c:6b:f5:94:c3:f0  172.16.254.1                   Jul 09 11:53:07  10.255.224.14
     10102      2c:6b:f5:d8:15:f0  irb.102                        Jul 09 11:53:07  10.255.224.13
     10103      00:10:db:ff:10:03  00:11:00:00:00:01:00:01:02:0a  Jul 09 12:08:45  10.255.224.17
     10103      2c:6b:f5:94:c3:f0  172.16.254.1                   Jul 09 11:53:07  10.255.224.22
     10103      2c:6b:f5:d8:15:f0  irb.103                        Jul 09 11:53:07  10.255.224.21
.
The following output was gathered from the SRX chassis cluster:
root@wanrouter_node0> show interfaces terse
Interface               Admin Link Proto    Local                 Remote
.
ge-0/0/1.0              up    up   inet     192.168.10.23/24
ge-0/0/2                up    up
ge-0/0/2.101            up    up   aenet    --> reth3.101
ge-0/0/2.102            up    up   aenet    --> reth3.102
ge-0/0/2.103            up    up   aenet    --> reth3.103
ge-0/0/2.32767          up    up   aenet    --> reth3.32767
ge-0/0/3                up    up
ge-0/0/3.101            up    up   aenet    --> reth3.101
ge-0/0/3.102            up    up   aenet    --> reth3.102
ge-0/0/3.103            up    up   aenet    --> reth3.103
ge-0/0/3.32767          up    up   aenet    --> reth3.32767
.
ge-7/0/1                up    up
ge-7/0/1.0              up    up   inet     192.168.10.24/24
ge-7/0/2                up    up
ge-7/0/2.101            up    up   aenet    --> reth3.101
ge-7/0/2.102            up    up   aenet    --> reth3.102
ge-7/0/2.103            up    up   aenet    --> reth3.103
ge-7/0/2.32767          up    up   aenet    --> reth3.32767
ge-7/0/3                up    up
ge-7/0/3.101            up    up   aenet    --> reth3.101
ge-7/0/3.102            up    up   aenet    --> reth3.102
ge-7/0/3.103            up    up   aenet    --> reth3.103
ge-7/0/3.32767          up    up   aenet    --> reth3.32767
.
reth3                   up    up
reth3.101               up    up   inet     10.255.224.1/29
reth3.102               up    up   inet     10.255.224.9/29
reth3.103               up    up   inet     10.255.224.17/29
.
root@wanrouter_node0> show lldp neighbors
Local Interface    Parent Interface    Chassis Id                               Port info          System Name
.
ge-0/0/3           reth3               2c:6b:f5:94:c3:c0                        ge-0/0/5            core2
ge-7/0/3           reth3               2c:6b:f5:94:c3:c0                        ge-0/0/6            core2
ge-0/0/2           reth3               2c:6b:f5:d8:15:c0                        ge-0/0/5            core1
ge-7/0/2           reth3               2c:6b:f5:d8:15:c0                        ge-0/0/6            core1
.
.
root@wanrouter_node0> show lacp interfaces
Aggregated interface: reth3
    LACP state:           Role   Exp   Def  Dist  Col  Syn  Aggr  Timeout  Activity
      ge-0/0/2           Actor    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-0/0/2         Partner    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-0/0/3           Actor    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-0/0/3         Partner    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-7/0/2           Actor    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-7/0/2         Partner    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-7/0/3           Actor    No    No   Yes  Yes  Yes   Yes     Fast    Active
      ge-7/0/3         Partner    No    No   Yes  Yes  Yes   Yes     Fast    Active
    LACP protocol:        Receive State  Transmit State          Mux State
      ge-0/0/2                  Current   Fast periodic Collecting distributing
      ge-0/0/3                  Current   Fast periodic Collecting distributing
      ge-7/0/2                  Current   Fast periodic Collecting distributing
      ge-7/0/3                  Current   Fast periodic Collecting distributing
.
root@wanrouter_node0> show bgp summary
Threading mode: BGP I/O
Default eBGP mode: advertise - accept, receive - accept
Groups: 4 Peers: 6 Down peers: 0
Peer                     AS      InPkt     OutPkt    OutQ   Flaps Last Up/Dwn State|#Active/Received/Accepted/Damped...
10.255.224.5          64911      50855      50932       0       0 2w2d 4:00:34 Establ
  lan.inet.0: 4/6/6/0
10.255.224.6          64911      50853      50932       0       0 2w2d 4:00:32 Establ
  lan.inet.0: 4/6/6/0
10.255.224.13         64911      50860      50932       0       0 2w2d 4:00:33 Establ
  lan.inet.0: 4/6/6/0
10.255.224.14         64911      50854      50932       0       0 2w2d 4:00:34 Establ
  lan.inet.0: 4/6/6/0
10.255.224.21         64911      50859      50930       0       0 2w2d 4:00:18 Establ
  lan.inet.0: 4/6/6/0
10.255.224.22         64911      50855      50931       0       0 2w2d 4:00:32 Establ
  lan.inet.0: 4/6/6/0
.
root@wanrouter_node0> show route table lan.inet.0
.
lan.inet.0: 24 destinations, 46 routes (24 active, 0 holddown, 0 hidden)
+ = Active Route, - = Last Active, * = Both
.
0.0.0.0/0          *[Static/5] 2w2d 04:01:58
                    >  to 192.168.10.1 via ge-0/0/1.0
                    [Static/5] 2w2d 04:01:58
                    >  to 192.168.10.1 via ge-7/0/1.0
10.33.33.0/24      *[BGP/170] 1w0d 02:05:56, localpref 100, from 10.255.224.21
                      AS path: 64911 I, validation-state: unverified
                       to 10.255.224.21 via reth3.103
                    >  to 10.255.224.22 via reth3.103
                    [BGP/170] 2w2d 03:16:42, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.224.22 via reth3.103
10.88.88.0/24      *[BGP/170] 1w0d 02:05:56, localpref 100, from 10.255.224.13
                      AS path: 64911 I, validation-state: unverified
                       to 10.255.224.13 via reth3.102
                    >  to 10.255.224.14 via reth3.102
                    [BGP/170] 2w2d 03:16:42, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.224.14 via reth3.102
10.91.91.0/24      *[BGP/170] 05:34:12, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                       to 10.255.224.5 via reth3.101
                    >  to 10.255.224.6 via reth3.101
                    [BGP/170] 05:34:12, localpref 100
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                    >  to 10.255.224.5 via reth3.101
10.99.99.0/24      *[BGP/170] 1w0d 02:05:56, localpref 100, from 10.255.224.5
                      AS path: 64911 I, validation-state: unverified
                       to 10.255.224.5 via reth3.101
                    >  to 10.255.224.6 via reth3.101
                    [BGP/170] 2w2d 03:16:42, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.224.6 via reth3.101
.
root@wanrouter_node0> show security zones
node0:
--------------------------------------------------------------------------
.
Security zone: VRF1
  Zone ID: 11
  Send reset for non-SYN session TCP packets: On
  Policy configurable: Yes
  Interfaces bound: 1
  Interfaces:
    reth3.101
  Advanced-connection-tracking timeout: 1800
  Unidirectional-session-refreshing: No
.
Security zone: VRF2
  Zone ID: 12
  Send reset for non-SYN session TCP packets: On
  Policy configurable: Yes
  Interfaces bound: 1
  Interfaces:
    reth3.102
  Advanced-connection-tracking timeout: 1800
  Unidirectional-session-refreshing: No
.
Security zone: VRF3
  Zone ID: 13
  Send reset for non-SYN session TCP packets: On
  Policy configurable: Yes
  Interfaces bound: 1
  Interfaces:
    reth3.103
  Advanced-connection-tracking timeout: 1800
  Unidirectional-session-refreshing: No
.
root@wanrouter_node0> show chassis cluster statistics
Control link statistics:
    Control link 0:
        Heartbeat packets sent: 1395106
        Heartbeat packets received: 1395094
        Heartbeat packet errors: 0
Fabric link statistics:
    Child link 0
        Probes sent: 2794999
        Probes received: 2794999
    Child link 1
        Probes sent: 0
        Probes received: 0
Services Synchronized:
    Service name                              RTOs sent    RTOs received
    Translation context                       0            0
    Incoming NAT                              0            0
    Resource manager                          0            0
    DS-LITE create                            0            0
    Session create                            1723387      0
    IPv6 session create                       0            0
    IPv4/6 session RTO ACK                    0            0
    Session close                             596372       0
    IPv6 session close                        0            0
    Session change                            76606        0
    IPv6 session change                       0            0
    .
You can gather similar output from the WAN Edge Testing Tools.
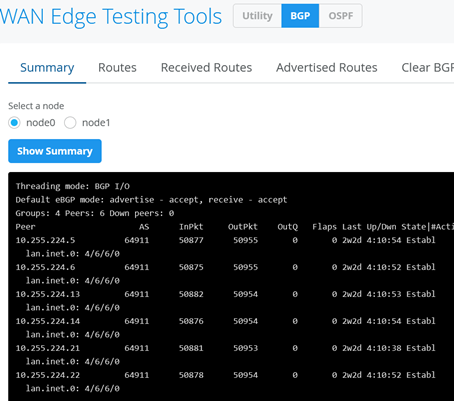
.
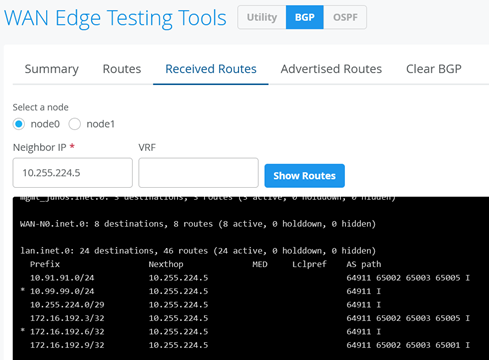
.