
Appendix: Layer 3 Exit With eBGP Routing Protocol (Full Active/Active Peering)
When you create any VLAN or VRF creation with campus fabric remember the following best practices:Create all VLANs in a switch template and then import them into the campus fabric configuration dialogue. Creating the VLANs anywhere else in the Juniper Mist portal ultimately leads to inconsistency which makes it hard to resolve issues.If needed, the fabric creates any required VRFs. Do not create VRFs manually elsewhere in the Juniper Mist portal. We recommend that you create port profiles within switch templates so that any changes are in sync on all switches in a fabric.
Before starting, a design must be created to determine how the routing protocol exchange will be implemented, how the point-to-point links will be configured, and how VLAN assignments will be distributed to indirectly identify the VRF. Even if a VRF is already created elsewhere in the fabric, such as on an access switch in an IP Clos design, the system will automatically recreate it on all service block functions when a Layer 3 exit is configured.
For each WAN router connection, an additional transport VLAN must be added to the VRF and then configured as a custom VRF on the service block function. Because this design uses two WAN routers, each VRF requires two additional transport VLANs on the service block function to establish BGP peering. When using transport VLANs, they must not be included in the overlay network definition of the EVPN fabric. These VLANs can be added to the switch template as long as they are not selected in the campus fabric configuration dialogue when defining networks. As an alternative, they can be created only on the service block function where they are locally required. All transport VLANs should be created with only a network name and a VLAN ID.
When defining point-to-point links, choose IP addresses from a range that does not overlap with the range used by the fabric, which by default is 10.255.240.0/20. A /31 subnet mask is commonly used, assigning the even IP address to the WAN router and the odd IP address to the fabric. The system requires a VLAN to be defined for each point-to-point link over a physical connection. This approach allows multiple VRFs to be multiplexed over a single uplink cable, with the VLAN internally referencing the associated VRF.For eBGP, private AS numbers must also be defined for the peering sessions. By default, the fabric internally uses AS 65000 for the EVPN control plane and then allocates AS numbers starting from 65001 from a configurable AS pool for each node. To avoid conflicts with these allocations, it is recommended to use private AS numbers below 65000.
Although it is technically possible to use a separate private AS per VRF for isolation, this is not considered a good practice because the QFX platform supports a maximum of 16 local VRFs. Using a shared AS across all VRFs on a service block function is the preferred approach. In this example, a different AS was chosen for each WAN router.
The image below shows how the two service block functions of the fabric connect to the first WAN router.
The image below shows how the two service block functions of the fabric connect to the second WAN router. Notice that we now use the second block of VLANs from each VRF.
Below is the full configuration table between core1 and core2 as service block function and the two WAN routers. You also see the AS number chosen for eBGP.
| Switch | Switch AS | VRF | Core P2P IP | Core IF | WAN Router | WAN Router P2P IP | WAN Router AS | WAN Router IF | VLAN ID |
|---|---|---|---|---|---|---|---|---|---|
| core1 | 64911 | customera | 10.255.224.1/31 | ge-0/0/3.101 | wanrouter1 | 10.255.224.0/31 | 64901 | ge-0/0/1.101 | 101 |
| core1 | 64911 | customerb | 10.255.224.3/31 | ge-0/0/3.102 | wanrouter1 | 10.255.224.2/31 | 64901 | ge-0/0/1.102 | 102 |
| core1 | 64911 | devices | 10.255.224.5/31 | ge-0/0/3.103 | wanrouter1 | 10.255.224.4/31 | 64901 | ge-0/0/1.103 | 103 |
| core1 | 64911 | customera | 10.255.225.1/31 | ge-0/0/4.101 | wanrouter2 | 10.255.225.0/31 | 64902 | ge-0/0/1.101 | 101 |
| core1 | 64911 | customerb | 10.255.225.3/31 | ge-0/0/4.102 | wanrouter2 | 10.255.225.2/31 | 64902 | ge-0/0/1.102 | 102 |
| core1 | 64911 | devices | 10.255.225.5/31 | ge-0/0/4.103 | wanrouter2 | 10.255.225.4/31 | 64902 | ge-0/0/1.103 | 103 |
| core2 | 64911 | customera | 10.255.226.1/31 | ge-0/0/3.201 | wanrouter1 | 10.255.226.0/31 | 64901 | ge-0/0/2.201 | 201 |
| core2 | 64911 | customerb | 10.255.226.3/31 | ge-0/0/3.202 | wanrouter1 | 10.255.226.2/31 | 64901 | ge-0/0/2.202 | 202 |
| core2 | 64911 | devices | 10.255.226.5/31 | ge-0/0/3.203 | wanrouter1 | 10.255.226.4/31 | 64901 | ge-0/0/2.203 | 203 |
| core2 | 64911 | customera | 10.255.227.1/31 | ge-0/0/4.201 | wanrouter2 | 10.255.227.0/31 | 64902 | ge-0/0/2.201 | 201 |
| core2 | 64911 | customerb | 10.255.227.3/31 | ge-0/0/4.202 | wanrouter2 | 10.255.227.2/31 | 64902 | ge-0/0/2.202 | 202 |
| core2 | 64911 | devices | 10.255.227.5/31 | ge-0/0/4.203 | wanrouter2 | 10.255.227.4/31 | 64902 | ge-0/0/2.203 | 203 |
Fabric Creation
The code block below shows the exported version of the switch template used in this fabric. This allows you to review our setup when importing. As you can see, we have a minimum of two VLANs per VRF. Remember that the L3 exit model requires one VLAN per WAN router and VRF).
{
  "additional_config_cmds": [],
  "networks": {
    "vlan1099": {
      "vlan_id": 1099,
      "subnet": "10.99.99.0/24"
    },
    "vlan1088": {
      "vlan_id": 1088,
      "subnet": "10.88.88.0/24"
    },
    "vlan1033": {
      "vlan_id": 1033,
      "subnet": "10.33.33.0/24"
    },
    "vlan1091": {
      "vlan_id": 1091,
      "subnet": "10.99.91.0/24"
    },
    "vlan1081": {
      "vlan_id": 1081,
      "subnet": "10.88.81.0/24"
    },
    "vlan1031": {
      "vlan_id": 1031,
      "subnet": "10.33.31.0/24"
    }
  },
  "port_usages": {
    "vlan1099": {
      "mode": "access",
      "disabled": false,
      "port_network": "vlan1099",
      "voip_network": null,
      "stp_edge": false,
      "mac_auth_protocol": null,
      "all_networks": false,
      "networks": null,
      "port_auth": null,
      "enable_mac_auth": null,
      "mac_auth_only": null,
      "guest_network": null,
      "bypass_auth_when_server_down": null,
      "speed": "auto",
      "duplex": "auto",
      "mac_limit": 0,
      "persist_mac": false,
      "poe_disabled": false,
      "enable_qos": false,
      "storm_control": {},
      "mtu": null,
      "description": "",
      "disable_autoneg": false
    },
    "vlan1088": {
      "mode": "access",
      "disabled": false,
      "port_network": "vlan1088",
      "voip_network": null,
      "stp_edge": false,
      "mac_auth_protocol": null,
      "all_networks": false,
      "networks": null,
      "port_auth": null,
      "enable_mac_auth": null,
      "mac_auth_only": null,
      "guest_network": null,
      "bypass_auth_when_server_down": null,
      "speed": "auto",
      "duplex": "auto",
      "mac_limit": 0,
      "persist_mac": false,
      "poe_disabled": false,
      "enable_qos": false,
      "storm_control": {},
      "mtu": null,
      "description": "",
      "disable_autoneg": false
    },
    "dynamic": {
      "mode": "dynamic",
      "reset_default_when": "link_down",
      "rules": []
    }
  },
  "switch_matching": {
    "enable": true,
    "rules": []
  },
  "switch_mgmt": {
    "config_revert_timer": 10,
    "root_password": "<password>",
    "protect_re": {
      "enabled": false
    },
    "tacacs": {
      "enabled": false
    }
  },
  "mist_nac": {
    "enabled": true,
    "network": null
  },
  "radius_config": {
    "auth_servers": [],
    "acct_servers": [],
    "auth_servers_timeout": 5,
    "auth_servers_retries": 3,
    "fast_dot1x_timers": false,
    "acct_interim_interval": 0,
    "auth_server_selection": "ordered",
    "coa_enabled": false,
    "coa_port": ""
  },
  "vrf_config": {
    "enabled": false
  },
  "remote_syslog": {
    "enabled": false
  },
  "snmp_config": {
    "enabled": false
  },
  "dhcp_snooping": {
    "enabled": false
  },
  "dns_servers": [],
  "dns_suffix": [],
  "ntp_servers": [],
  "acl_policies": [],
  "port_mirroring": {},
  "name": "campus-fabric"
}
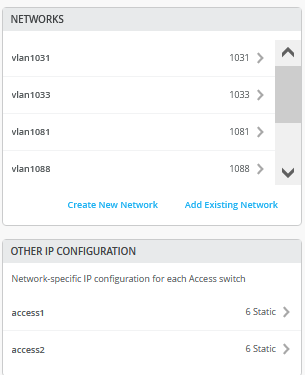
Inside the campus fabric configuration dialogue there is a page called “Configure Networks”. This is where you will import your 3*2=6 VLANs from the switch template and the result in our case will look like the image below.
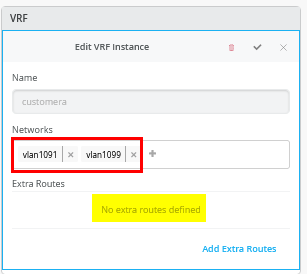
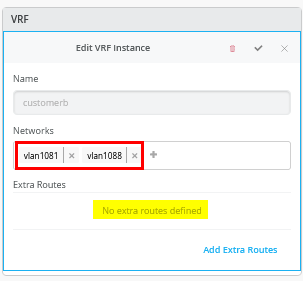
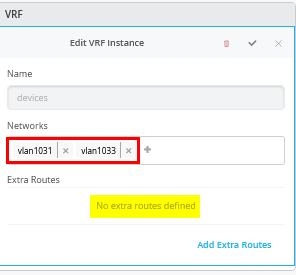
The next step is to create all three VRFs and attach two of the networks to each like that shown below.
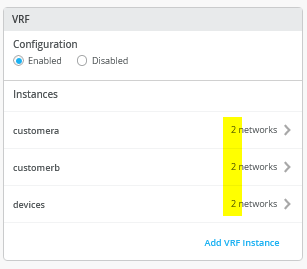
Then, go to each VRF and delete all manual routes you may have. Make sure each VRF has a minimum of two VLANs attached as those are used to identify the VRF later.
This is for the second VRF.
This is for the third VRF.
Core1 Switch Configuration
In this example, the service block function is virtual and co-located on the core switch. Therefore, you must configure the two core switches. The following block of pseudocode describes what you need to configure on the core1 switch:
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
# create network name:trans201 with VLAN-ID:201
# create network name:trans202 with VLAN-ID:202
# create network name:trans203 with VLAN-ID:203
#
# configure the Additional IP-Subnet 10.255.224.1 255.255.255.254 to Network/VLAN:trans101
# configure the Additional IP-Subnet 10.255.224.3 255.255.255.254 to Network/VLAN:trans102
# configure the Additional IP-Subnet 10.255.224.5 255.255.255.254 to Network/VLAN:trans103
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/3 as L3-Sub-Interfaces with MTU=9018
#
# configure the Additional IP-Subnet 10.255.225.1 255.255.255.254 to Network/VLAN:trans201
# configure the Additional IP-Subnet 10.255.225.3 255.255.255.254 to Network/VLAN:trans202
# configure the Additional IP-Subnet 10.255.225.5 255.255.255.254 to Network/VLAN:trans203
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/4 as L3-Sub-Interfaces with MTU=9018
#
# configure on VRF
# configure on instance customera
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans101
# add to existing overlay-vlans the vlan:trans201
#
# configure on instance customerb
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans102
# add to existing overlay-vlans the vlan:trans202
#
# configure on instance devices
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans103
# add to existing overlay-vlans the vlan:trans203
#
# Enable BGP
# Create an Export policy called 'export-vrfs'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default  Prefix=0.0.0.0/0  Protocol=None  Then=Reject
# - Add Term w. Name=fabric-all-no-hosts  Prefix=0.0.0.0/0-30  Protocol=None  Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32  Protocol=None  Then=Accept
#
# Create an Export policy called 'import-default'
# - Name=default  Prefix=0.0.0.0/0  Protocol=BGP  Action=Accept
#
# Create a BGP Group with:
# - Name=customera0
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.224.0  Neighbor_AS=64901  Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb0
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.224.2  Neighbor_AS=64901  Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices0
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.224.4  Neighbor_AS=64901  Hold-Time=90
#
# Create a BGP Group with:
# - Name=customera1
# - Type=External
# - Network (VLAN)=trans201
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.225.0  Neighbor_AS=64902  Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb1
# - Type=External
# - Network (VLAN)=trans202
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.225.2  Neighbor_AS=64902  Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices1
# - Type=External
# - Network (VLAN)=trans203
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.225.4  Neighbor_AS=64902  Hold-Time=90
We are sharing a couple of screenshots below that illustrate a major portion of the configuration described above. The first screenshot shows the additional transport VLANs that were defined locally. Only the first two of the six are displayed in the screenshot below. Please note that overlay VLANs, such as VLAN1099, are inherited through the switch template.
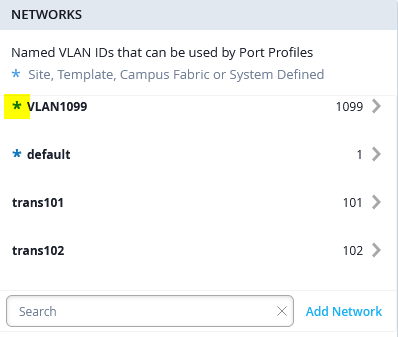
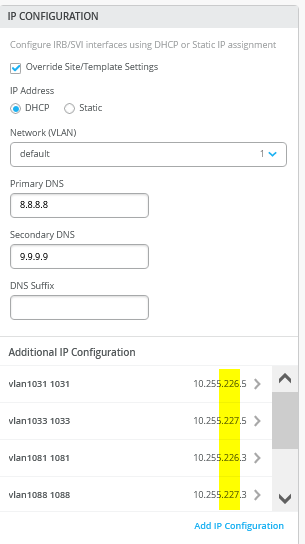
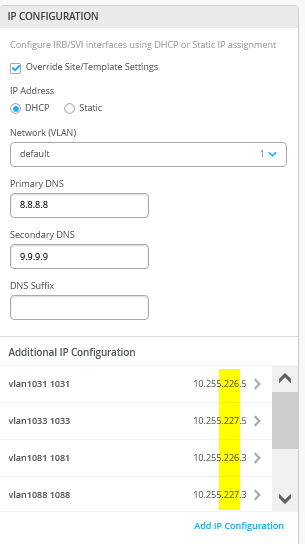
Begin with the additional IP configuration. Note that the same VLAN is used between the two service block functions, but each uses different point-to-point IP addresses. Also remember that the transport VLAN serves as a reference to the corresponding VRF when defining the BGP peering.
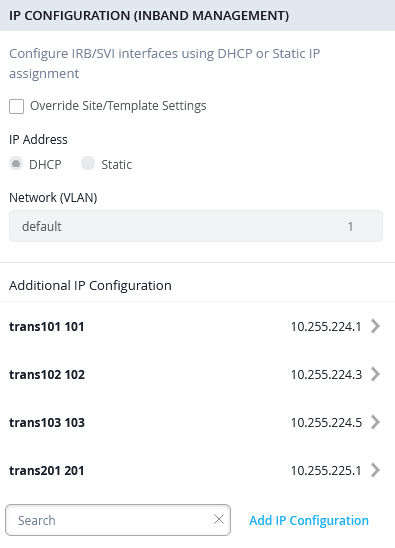
Here is an example of one of the six transport VLANs to be defined.
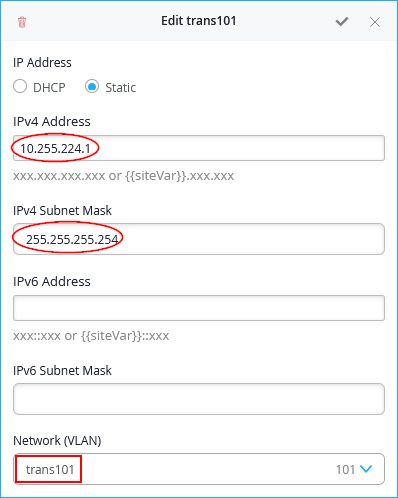
In the port configuration, it is essential to use Layer 3 subinterfaces and associate them with the first set of subinterfaces that were defined.
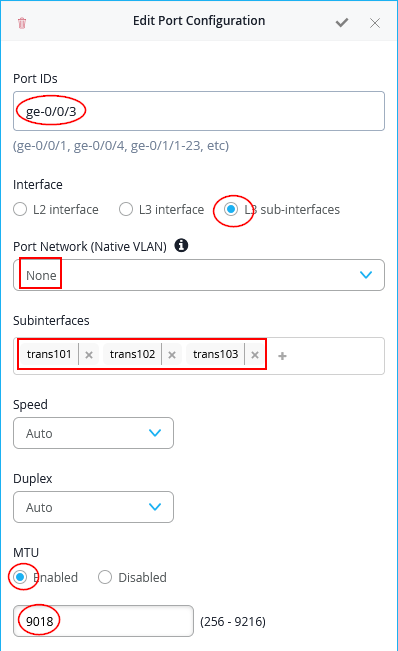
In the second port configuration toward the other WAN router, the remaining subinterfaces are associated accordingly.
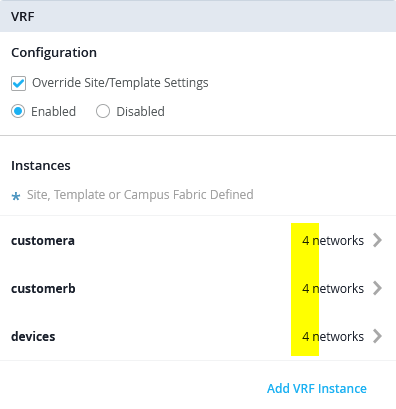
The next step is to add all transport VLANs to each VRF as custom networks, so they are recognized within the VRF. As shown, each VRF ultimately contains four networks: two used in the overlay and two additional transport VLANs added at the service block function.
An individual custom VRF would look like the example below.
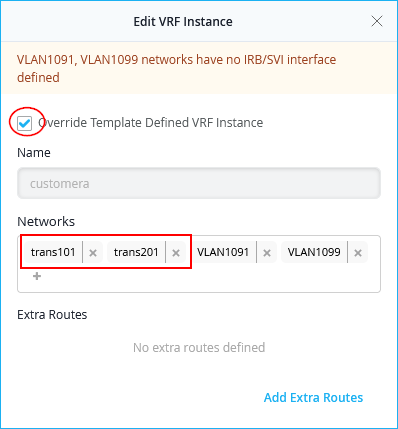
When overlay VLANs are added or removed later through a switch template and the campus fabric configuration interface, the same changes must also be made in the custom VRF on the service block function. These VLANs are not added automatically, so if this step is overlooked they will not be advertised to the WAN router.
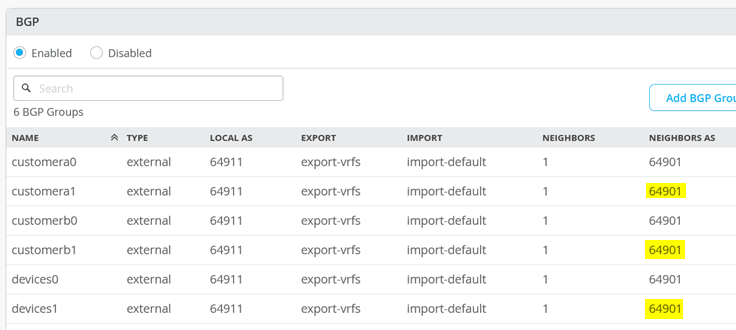
Now you need to enter the entire eBGP configuration with all six peers as you have three VRFs and two WAN routers. When finished, the overview page should look like the image below:
The next step is to define two routing policies.
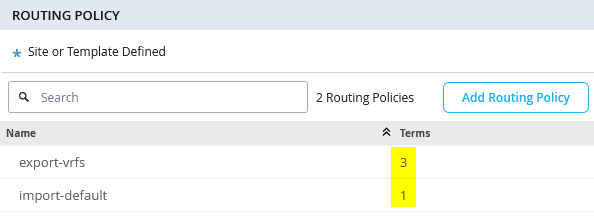
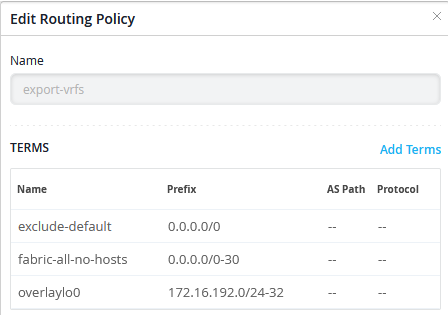
In this example, the export route policies include the following terms:
- Term=
exclude-defaultprevents the default route learned from the first WAN router from being exported to the second WAN router, and vice versa. - Term=
fabric-all-no-hostsautomatically exports all routes from the fabric across all configured VRFs and their associated VLANs. However, point-to-point links and single-host routes are excluded. This is achieved by using the prefix 0.0.0.0/0-30, where specifying 0-30 in Junos OS represents an “orlonger” prefix range up to /30. - Term=
overlaylo0exports the overlay loopback IP addresses used for DHCP relay down to the host prefix level, since they are typically assigned individually to lo0.x interfaces. To accomplish this, the prefix 172.16.192.0/24-32 is used, allowing the range to extend down to host-level prefixes, which is not done in the previous statement.
If desired, you can simplify the rule set by using a single term
such as 0.0.0.0/0-32 which exports all
routes—including those for individual clients in the fabric,
represented by their host IP addresses. This approach can also be
useful for debugging, as examining the AS path information on the
WAN router will reveal which EVPN fabric switch is announcing a
given host IP.
The downside, however, is that this approach may result in a large
number of routes being exchanged with the WAN router, whereas the
default setting of 0.0.0.0/0-30 limits route sharing
to prefixes associated only with the configured VLANs.
10.99.99.0/24      *[BGP/170] 01:00:32, localpref 100, from 10.255.224.1
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.224.1 via ge-0/0/1.101
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 01:00:32, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
10.99.99.99/32     *[BGP/170] 00:01:33, localpref 100, from 10.255.224.1
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.224.1 via ge-0/0/1.101
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 00:01:33, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
The import policy imports the default route from the WAN router.
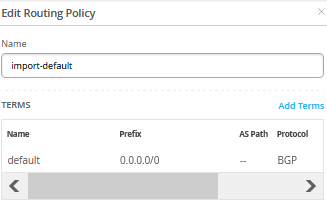
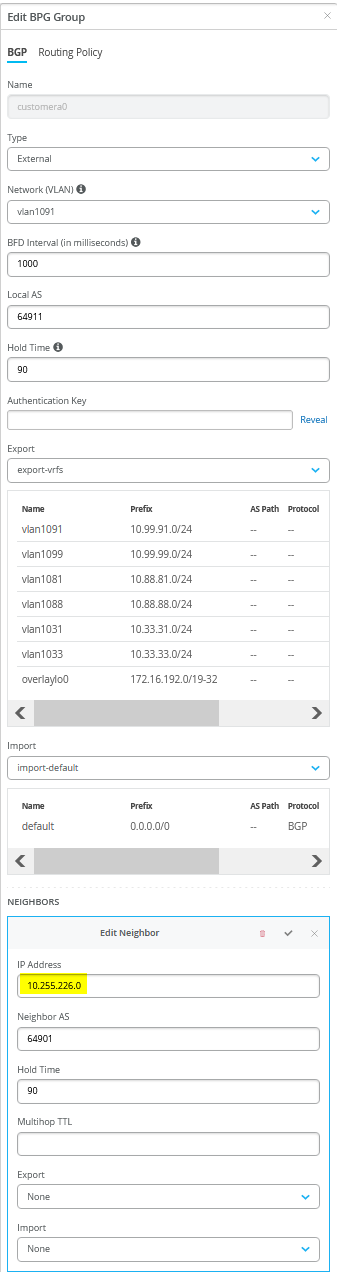
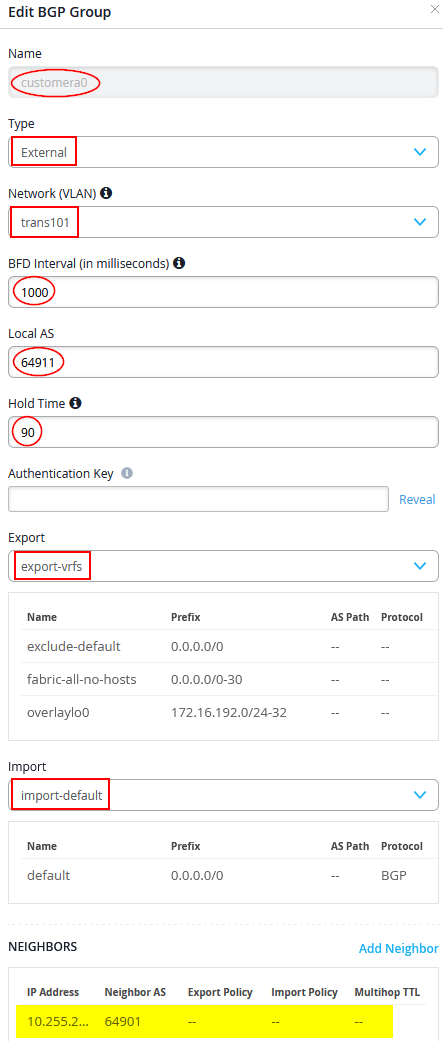
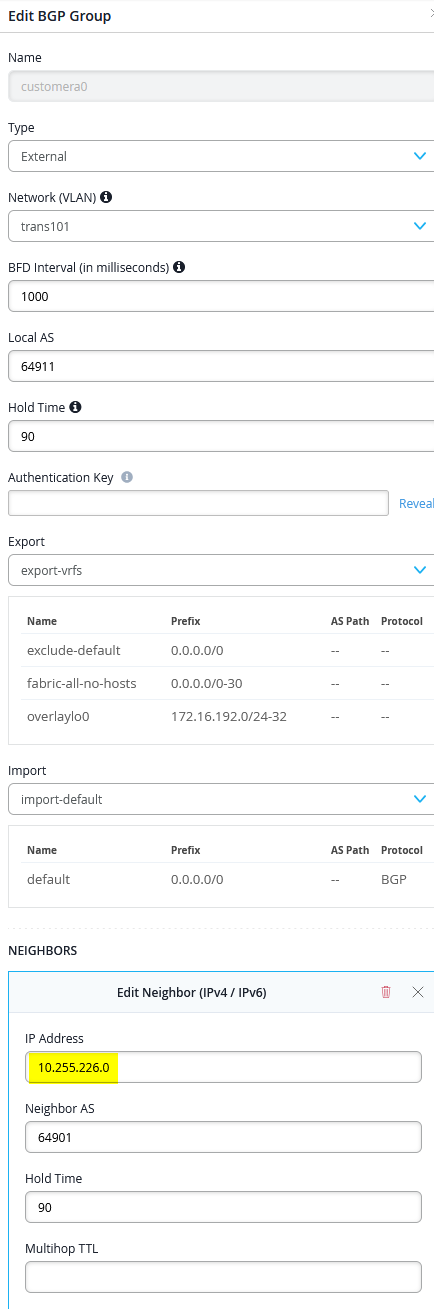
Figure 18 shows the configuration of a single BGP peering entry with the required entries called out.
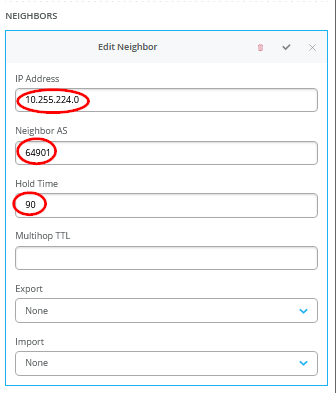
You must also define the WAN router as a BGP neighbor.
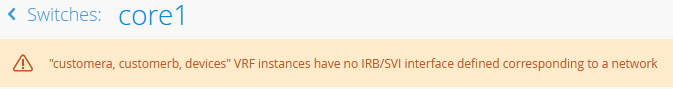
You may see a warning message as shown in Figure 19. It is safe to ignore those.
When overlay VLANs are added or removed later through a switch template and the campus fabric configuration interface, the same changes must also be made in the custom VRF on the service block function. These VLANs are not added automatically, so if this step is overlooked they will not be advertised to the WAN router.
Core2 Switch Configuration
The following pseudocode represents the configuration you must apply to the core2 switch. The changes from the first WAN router are highlighted.
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
# create network name:trans201 with VLAN-ID:201
# create network name:trans202 with VLAN-ID:202
# create network name:trans203 with VLAN-ID:203
#
# configure the Additional IP-Subnet 10.255.226.1 255.255.255.254 to Network/VLAN:trans101
# configure the Additional IP-Subnet 10.255.226.3 255.255.255.254 to Network/VLAN:trans102
# configure the Additional IP-Subnet 10.255.226.5 255.255.255.254 to Network/VLAN:trans103
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/3 as L3-Sub-Interfaces with MTU=9018
#
# configure the Additional IP-Subnet 10.255.227.1 255.255.255.254 to Network/VLAN:trans201
# configure the Additional IP-Subnet 10.255.227.3 255.255.255.254 to Network/VLAN:trans202
# configure the Additional IP-Subnet 10.255.227.5 255.255.255.254 to Network/VLAN:trans203
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/4 as L3-Sub-Interfaces with MTU=9018
#
# configure on VRF
# configure on instance customera
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans101
# add to existing overlay-vlans the vlan:trans201
#
# configure on instance customerb
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans102
# add to existing overlay-vlans the vlan:trans202
#
# configure on instance devices
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans103
# add to existing overlay-vlans the vlan:trans203
#
# Enable BGP
# Create an Export policy called 'export-vrfs'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default  Prefix=0.0.0.0/0  Protocol=None  Then=Reject
# - Add Term w. Name=fabric-all-no-hosts  Prefix=0.0.0.0/0-30  Protocol=None  Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32  Protocol=None  Then=Accept
#
# Create an Export policy called 'import-default'
# - Name=default  Prefix=0.0.0.0/0  Protocol=BGP  Action=Accept
#
# Create a BGP Group with:
# - Name=customera0
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.226.0  Neighbor_AS=64901  Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb0
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.226.2  Neighbor_AS=64901  Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices0
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.226.4  Neighbor_AS=64901  Hold-Time=90
#
# Create a BGP Group with:
# - Name=customera1
# - Type=External
# - Network (VLAN)=trans201
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.227.0  Neighbor_AS=64902  Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb1
# - Type=External
# - Network (VLAN)=trans202
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.227.2  Neighbor_AS=64902  Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices1
# - Type=External
# - Network (VLAN)=trans203
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.227.4  Neighbor_AS=64902  Hold-Time=90
Aside from the point-to-point subnets and the BGP neighbors, the configuration on the core2 switch is the same as the configuration on the core1 switch.
Juniper MX as a WAN Router
The following code blocks show the Junos OS CLI configuration for the point-to-point interfaces, the complete eBGP configuration with all BGP neighbors, and the import and export route policies for each WAN router. You may need to add default routes and interfaces to complete the configuration, as these must be advertised to the fabric, but we do not know how your device learns those routes.
The CLI configuration for the first WAN router is as follows:
set system host-name wanrouter1
#
delete interfaces ge-0/0/1
set interfaces ge-0/0/1 flexible-vlan-tagging
set interfaces ge-0/0/1 mtu 9014
set interfaces ge-0/0/1 unit 101 description trans101
set interfaces ge-0/0/1 unit 101 vlan-id 101
set interfaces ge-0/0/1 unit 101 family inet address 10.255.224.0/31
set interfaces ge-0/0/1 unit 102 description trans102
set interfaces ge-0/0/1 unit 102 vlan-id 102
set interfaces ge-0/0/1 unit 102 family inet address 10.255.224.2/31
set interfaces ge-0/0/1 unit 103 description trans103
set interfaces ge-0/0/1 unit 103 vlan-id 103
set interfaces ge-0/0/1 unit 103 family inet address 10.255.224.4/31
#
delete interfaces ge-0/0/2
set interfaces ge-0/0/2 flexible-vlan-tagging
set interfaces ge-0/0/2 mtu 9014
set interfaces ge-0/0/2 unit 101 description trans101
set interfaces ge-0/0/2 unit 101 vlan-id 101
set interfaces ge-0/0/2 unit 101 family inet address 10.255.226.0/31
set interfaces ge-0/0/2 unit 102 description trans102
set interfaces ge-0/0/2 unit 102 vlan-id 102
set interfaces ge-0/0/2 unit 102 family inet address 10.255.226.2/31
set interfaces ge-0/0/2 unit 103 description trans103
set interfaces ge-0/0/2 unit 103 vlan-id 103
set interfaces ge-0/0/2 unit 103 family inet address 10.255.226.4/31
# needed in and export policy
delete policy-options
set policy-options policy-statement fabric term 1 from protocol bgp
set policy-options policy-statement fabric term 1 from route-filter 0.0.0.0/0 orlonger
set policy-options policy-statement fabric term 1 then accept
set policy-options policy-statement fabric term 2 then reject
set policy-options policy-statement internet term 1 from protocol static
set policy-options policy-statement internet term 1 from route-filter 0.0.0.0/0 exact
set policy-options policy-statement internet term 1 then accept
set policy-options policy-statement internet term 2 then reject
#
delete routing-instances public-int
set routing-instances public-int instance-type virtual-router
set routing-instances public-int interface ge-0/0/1.101
set routing-instances public-int interface ge-0/0/1.102
set routing-instances public-int interface ge-0/0/1.103
set routing-instances public-int interface ge-0/0/2.101
set routing-instances public-int interface ge-0/0/2.102
set routing-instances public-int interface ge-0/0/2.103
#
delete routing-instances public-int protocols bgp group customera
set routing-instances public-int protocols bgp group customera type external
set routing-instances public-int protocols bgp group customera family inet unicast
set routing-instances public-int protocols bgp group customera multipath multiple-as
set routing-instances public-int protocols bgp group customera local-as 64901
set routing-instances public-int protocols bgp group customera hold-time 90
set routing-instances public-int protocols bgp group customera import fabric
set routing-instances public-int protocols bgp group customera export internet
set routing-instances public-int protocols bgp group customera bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customera bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customera bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customera neighbor 10.255.224.1 peer-as 64911
set routing-instances public-int protocols bgp group customera neighbor 10.255.226.1 peer-as 64911
#
delete routing-instances public-int protocols bgp group customerb
set routing-instances public-int protocols bgp group customerb type external
set routing-instances public-int protocols bgp group customerb family inet unicast
set routing-instances public-int protocols bgp group customerb multipath multiple-as
set routing-instances public-int protocols bgp group customerb local-as 64901
set routing-instances public-int protocols bgp group customerb hold-time 90
set routing-instances public-int protocols bgp group customerb import fabric
set routing-instances public-int protocols bgp group customerb export internet
set routing-instances public-int protocols bgp group customerb bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customerb bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customerb bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customerb neighbor 10.255.224.3 peer-as 64911
set routing-instances public-int protocols bgp group customerb neighbor 10.255.226.3 peer-as 64911
#
delete routing-instances public-int protocols bgp group devices
set routing-instances public-int protocols bgp group devices type external
set routing-instances public-int protocols bgp group devices family inet unicast
set routing-instances public-int protocols bgp group devices multipath multiple-as
set routing-instances public-int protocols bgp group devices local-as 64901
set routing-instances public-int protocols bgp group devices hold-time 90
set routing-instances public-int protocols bgp group devices import fabric
set routing-instances public-int protocols bgp group devices export internet
set routing-instances public-int protocols bgp group devices bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group devices bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group devices bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group devices neighbor 10.255.224.5 peer-as 64911
set routing-instances public-int protocols bgp group devices neighbor 10.255.226.5 peer-as 64911
The following is the configuration for the second WAN router:
set system host-name wanrouter2
#
delete interfaces ge-0/0/1
set interfaces ge-0/0/1 flexible-vlan-tagging
set interfaces ge-0/0/1 mtu 9014
set interfaces ge-0/0/1 unit 201 description trans201
set interfaces ge-0/0/1 unit 201 vlan-id 201
set interfaces ge-0/0/1 unit 201 family inet address 10.255.225.0/31
set interfaces ge-0/0/1 unit 202 description trans202
set interfaces ge-0/0/1 unit 202 vlan-id 202
set interfaces ge-0/0/1 unit 202 family inet address 10.255.225.2/31
set interfaces ge-0/0/1 unit 203 description trans203
set interfaces ge-0/0/1 unit 203 vlan-id 203
set interfaces ge-0/0/1 unit 203 family inet address 10.255.225.4/31
#
delete interfaces ge-0/0/2
set interfaces ge-0/0/2 flexible-vlan-tagging
set interfaces ge-0/0/2 mtu 9014
set interfaces ge-0/0/2 unit 201 description trans201
set interfaces ge-0/0/2 unit 201 vlan-id 201
set interfaces ge-0/0/2 unit 201 family inet address 10.255.227.0/31
set interfaces ge-0/0/2 unit 202 description trans202
set interfaces ge-0/0/2 unit 202 vlan-id 202
set interfaces ge-0/0/2 unit 202 family inet address 10.255.227.2/31
set interfaces ge-0/0/2 unit 203 description trans203
set interfaces ge-0/0/2 unit 203 vlan-id 203
set interfaces ge-0/0/2 unit 203 family inet address 10.255.227.4/31
# needed in and export policy
delete policy-options
set policy-options policy-statement fabric term 1 from protocol bgp
set policy-options policy-statement fabric term 1 from route-filter 0.0.0.0/0 orlonger
set policy-options policy-statement fabric term 1 then accept
set policy-options policy-statement fabric term 2 then reject
set policy-options policy-statement internet term 1 from protocol static
set policy-options policy-statement internet term 1 from route-filter 0.0.0.0/0 exact
set policy-options policy-statement internet term 1 then accept
set policy-options policy-statement internet term 2 then reject
#
delete routing-instances public-int
set routing-instances public-int instance-type virtual-router
set routing-instances public-int interface ge-0/0/1.201
set routing-instances public-int interface ge-0/0/1.202
set routing-instances public-int interface ge-0/0/1.203
set routing-instances public-int interface ge-0/0/2.201
set routing-instances public-int interface ge-0/0/2.202
set routing-instances public-int interface ge-0/0/2.203
#
delete routing-instances public-int protocols bgp group customera
set routing-instances public-int protocols bgp group customera type external
set routing-instances public-int protocols bgp group customera family inet unicast
set routing-instances public-int protocols bgp group customera multipath multiple-as
set routing-instances public-int protocols bgp group customera local-as 64902
set routing-instances public-int protocols bgp group customera hold-time 90
set routing-instances public-int protocols bgp group customera import fabric
set routing-instances public-int protocols bgp group customera export internet
set routing-instances public-int protocols bgp group customera bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customera bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customera bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customera neighbor 10.255.225.1 peer-as 64911
set routing-instances public-int protocols bgp group customera neighbor 10.255.227.1 peer-as 64911
#
delete routing-instances public-int protocols bgp group customerb
set routing-instances public-int protocols bgp group customerb type external
set routing-instances public-int protocols bgp group customerb family inet unicast
set routing-instances public-int protocols bgp group customerb multipath multiple-as
set routing-instances public-int protocols bgp group customerb local-as 64902
set routing-instances public-int protocols bgp group customerb hold-time 90
set routing-instances public-int protocols bgp group customerb import fabric
set routing-instances public-int protocols bgp group customerb export internet
set routing-instances public-int protocols bgp group customerb bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customerb bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customerb bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customerb neighbor 10.255.225.3 peer-as 64911
set routing-instances public-int protocols bgp group customerb neighbor 10.255.227.3 peer-as 64911
#
delete routing-instances public-int protocols bgp group devices
set routing-instances public-int protocols bgp group devices type external
set routing-instances public-int protocols bgp group devices family inet unicast
set routing-instances public-int protocols bgp group devices multipath multiple-as
set routing-instances public-int protocols bgp group devices local-as 64902
set routing-instances public-int protocols bgp group devices hold-time 90
set routing-instances public-int protocols bgp group devices import fabric
set routing-instances public-int protocols bgp group devices export internet
set routing-instances public-int protocols bgp group devices bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group devices bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group devices bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group devices neighbor 10.255.225.5 peer-as 64911
set routing-instances public-int protocols bgp group devices neighbor 10.255.227.5 peer-as 64911
You can use the following CLI commands to assist with debugging on WAN router1.
root@wanrouter1> show bgp summary
Threading mode: BGP I/O
Default eBGP mode: advertise - accept, receive - accept
Groups: 3 Peers: 6 Down peers: 0
Peer                     AS      InPkt     OutPkt    OutQ   Flaps Last Up/Dwn State|#Active/Received/Accepted/Damped...
10.255.224.1          64911        195        189       0       0     1:25:10 Establ
  public-int.inet.0: 5/6/6/0
10.255.224.3          64911        194        189       0       0     1:25:14 Establ
  public-int.inet.0: 5/6/6/0
10.255.224.5          64911        192        189       0       0     1:25:14 Establ
  public-int.inet.0: 5/6/6/0
10.255.226.1          64911        197        188       0       0     1:25:05 Establ
  public-int.inet.0: 5/6/6/0
10.255.226.3          64911        196        188       0       0     1:25:06 Establ
  public-int.inet.0: 5/6/6/0
10.255.226.5          64911        195        189       0       0     1:25:00 Establ
  public-int.inet.0: 5/6/6/0
#
root@wanrouter1> show route table public-int.inet.0
#
public-int.inet.0: 33 destinations, 51 routes (33 active, 0 holddown, 0 hidden)
+ = Active Route, - = Last Active, * = Both
#
0.0.0.0/0          *[Static/5] 01:25:28
                    >  to 192.168.230.1 via ge-0/0/0.0
10.31.31.0/24      *[BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.224.5 via ge-0/0/1.103
                    >  to 10.255.226.5 via ge-0/0/2.103
                    [BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.224.5 via ge-0/0/1.103
10.33.33.0/24      *[BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.224.5 via ge-0/0/1.103
                    >  to 10.255.226.5 via ge-0/0/2.103
                    [BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.224.5 via ge-0/0/1.103
10.81.81.0/24      *[BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.224.3 via ge-0/0/1.102
                    >  to 10.255.226.3 via ge-0/0/2.102
                    [BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.224.3 via ge-0/0/1.102
10.88.88.0/24      *[BGP/170] 01:24:06, localpref 100, from 10.255.224.3
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                       to 10.255.224.3 via ge-0/0/1.102
                    >  to 10.255.226.3 via ge-0/0/2.102
                    [BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                    >  to 10.255.226.3 via ge-0/0/2.102
10.91.91.0/24      *[BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.224.1 via ge-0/0/1.101
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 01:24:06, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.224.1 via ge-0/0/1.101
10.99.99.0/24      *[BGP/170] 01:24:41, localpref 100, from 10.255.224.1
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.224.1 via ge-0/0/1.101
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 01:24:41, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
10.255.224.0/31    *[Direct/0] 01:25:28
                    >  via ge-0/0/1.101
10.255.224.0/32    *[Local/0] 01:25:28
                       Local via ge-0/0/1.101
10.255.224.2/31    *[Direct/0] 01:25:28
                    >  via ge-0/0/1.102
10.255.224.2/32    *[Local/0] 01:25:28
                       Local via ge-0/0/1.102
10.255.224.4/31    *[Direct/0] 01:25:28
                    >  via ge-0/0/1.103
10.255.224.4/32    *[Local/0] 01:25:28
                       Local via ge-0/0/1.103
10.255.226.0/31    *[Direct/0] 01:25:27
                    >  via ge-0/0/2.101
10.255.226.0/32    *[Local/0] 01:25:27
                       Local via ge-0/0/2.101
10.255.226.2/31    *[Direct/0] 01:25:27
                    >  via ge-0/0/2.102
10.255.226.2/32    *[Local/0] 01:25:27
                       Local via ge-0/0/2.102
10.255.226.4/31    *[Direct/0] 01:25:27
                    >  via ge-0/0/2.103
10.255.226.4/32    *[Local/0] 01:25:27
                       Local via ge-0/0/2.103
172.16.192.1/32    *[BGP/170] 01:24:41, localpref 100, from 10.255.224.1
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.224.1 via ge-0/0/1.101
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 01:24:41, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
172.16.192.2/32    *[BGP/170] 01:24:07, localpref 100, from 10.255.224.1
                      AS path: 64911 65002 65004 65006 I, validation-state: unverified
                       to 10.255.224.1 via ge-0/0/1.101
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 01:24:07, localpref 100
                      AS path: 64911 65001 65004 65006 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
172.16.192.3/32    *[BGP/170] 01:24:07, localpref 100, from 10.255.224.3
                      AS path: 64911 65002 65004 65006 I, validation-state: unverified
                       to 10.255.224.3 via ge-0/0/1.102
                    >  to 10.255.226.3 via ge-0/0/2.102
                    [BGP/170] 01:24:07, localpref 100
                      AS path: 64911 65001 65004 65006 I, validation-state: unverified
                    >  to 10.255.226.3 via ge-0/0/2.102
172.16.192.4/32    *[BGP/170] 01:24:07, localpref 100, from 10.255.224.5
                      AS path: 64911 65002 65004 65006 I, validation-state: unverified
                       to 10.255.224.5 via ge-0/0/1.103
                    >  to 10.255.226.5 via ge-0/0/2.103
                    [BGP/170] 01:24:07, localpref 100
                      AS path: 64911 65001 65004 65006 I, validation-state: unverified
                    >  to 10.255.226.5 via ge-0/0/2.103
172.16.192.5/32    *[BGP/170] 01:24:41, localpref 100, from 10.255.224.3
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.224.3 via ge-0/0/1.102
                    >  to 10.255.226.3 via ge-0/0/2.102
                    [BGP/170] 01:24:41, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.226.3 via ge-0/0/2.102
172.16.192.6/32    *[BGP/170] 01:24:41, localpref 100, from 10.255.224.5
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.224.5 via ge-0/0/1.103
                    >  to 10.255.226.5 via ge-0/0/2.103
                    [BGP/170] 01:24:41, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.226.5 via ge-0/0/2.103
172.16.192.7/32    *[BGP/170] 01:25:23, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.224.1 via ge-0/0/1.101
                    [BGP/170] 01:25:17, localpref 100
                      AS path: 64911 65001 65003 65002 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
172.16.192.8/32    *[BGP/170] 01:25:27, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.224.3 via ge-0/0/1.102
                    [BGP/170] 01:25:18, localpref 100
                      AS path: 64911 65001 65003 65002 I, validation-state: unverified
                    >  to 10.255.226.3 via ge-0/0/2.102
172.16.192.9/32    *[BGP/170] 01:25:27, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.224.5 via ge-0/0/1.103
                    [BGP/170] 01:25:13, localpref 100
                      AS path: 64911 65001 65003 65002 I, validation-state: unverified
                    >  to 10.255.226.5 via ge-0/0/2.103
172.16.192.10/32   *[BGP/170] 01:25:17, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.226.1 via ge-0/0/2.101
                    [BGP/170] 01:25:23, localpref 100
                      AS path: 64911 65002 65003 65001 I, validation-state: unverified
                    >  to 10.255.224.1 via ge-0/0/1.101
172.16.192.11/32   *[BGP/170] 01:25:18, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.226.3 via ge-0/0/2.102
                    [BGP/170] 01:25:27, localpref 100
                      AS path: 64911 65002 65003 65001 I, validation-state: unverified
                    >  to 10.255.224.3 via ge-0/0/1.102
172.16.192.12/32   *[BGP/170] 01:25:13, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.226.5 via ge-0/0/2.103
                    [BGP/170] 01:25:27, localpref 100
                      AS path: 64911 65002 65003 65001 I, validation-state: unverified
                    >  to 10.255.224.5 via ge-0/0/1.103
192.168.230.0/24   *[Direct/0] 01:25:28
                    >  via ge-0/0/0.0
192.168.230.99/32  *[Local/0] 01:25:28
                       Local via ge-0/0/0.0
You can use the following CLI commands to assist with debugging on WAN router2.
root@wanrouter2> show bgp summary
Threading mode: BGP I/O
Default eBGP mode: advertise - accept, receive - accept
Groups: 3 Peers: 6 Down peers: 0
Peer                     AS      InPkt     OutPkt    OutQ   Flaps Last Up/Dwn State|#Active/Received/Accepted/Damped...
10.255.225.1          64911        201        193       0       0     1:27:07 Establ
  public-int.inet.0: 5/7/7/0
10.255.225.3          64911        200        193       0       0     1:27:04 Establ
  public-int.inet.0: 5/7/7/0
10.255.225.5          64911        197        192       0       0     1:27:00 Establ
  public-int.inet.0: 5/7/7/0
10.255.227.1          64911        200        192       0       0     1:27:02 Establ
  public-int.inet.0: 5/7/7/0
10.255.227.3          64911        200        192       0       0     1:26:58 Establ
  public-int.inet.0: 5/7/7/0
10.255.227.5          64911        198        193       0       0     1:27:08 Establ
  public-int.inet.0: 5/7/7/0
#
root@wanrouter2> show route table public-int.inet.0
#
public-int.inet.0: 33 destinations, 57 routes (33 active, 0 holddown, 0 hidden)
+ = Active Route, - = Last Active, * = Both
#
0.0.0.0/0          *[Static/5] 01:27:27
                    >  to 192.168.231.1 via ge-0/0/0.0
10.31.31.0/24      *[BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.225.5 via ge-0/0/1.203
                    >  to 10.255.227.5 via ge-0/0/2.203
                    [BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.225.5 via ge-0/0/1.203
10.33.33.0/24      *[BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.225.5 via ge-0/0/1.203
                    >  to 10.255.227.5 via ge-0/0/2.203
                    [BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.225.5 via ge-0/0/1.203
10.81.81.0/24      *[BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.225.3 via ge-0/0/1.202
                    >  to 10.255.227.3 via ge-0/0/2.202
                    [BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.225.3 via ge-0/0/1.202
10.88.88.0/24      *[BGP/170] 01:26:27, localpref 100, from 10.255.225.3
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                       to 10.255.225.3 via ge-0/0/1.202
                    >  to 10.255.227.3 via ge-0/0/2.202
                    [BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                    >  to 10.255.227.3 via ge-0/0/2.202
10.91.91.0/24      *[BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65001 65004 65005 I, validation-state: unverified
                       to 10.255.225.1 via ge-0/0/1.201
                    >  to 10.255.227.1 via ge-0/0/2.201
                    [BGP/170] 01:26:27, localpref 100
                      AS path: 64911 65002 65004 65005 I, validation-state: unverified
                    >  to 10.255.225.1 via ge-0/0/1.201
10.99.99.0/24      *[BGP/170] 01:27:03, localpref 100, from 10.255.225.1
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.225.1 via ge-0/0/1.201
                    >  to 10.255.227.1 via ge-0/0/2.201
                    [BGP/170] 01:27:03, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.227.1 via ge-0/0/2.201
10.255.225.0/31    *[Direct/0] 01:27:28
                    >  via ge-0/0/1.201
10.255.225.0/32    *[Local/0] 01:27:28
                       Local via ge-0/0/1.201
10.255.225.2/31    *[Direct/0] 01:27:28
                    >  via ge-0/0/1.202
10.255.225.2/32    *[Local/0] 01:27:28
                       Local via ge-0/0/1.202
10.255.225.4/31    *[Direct/0] 01:27:28
                    >  via ge-0/0/1.203
10.255.225.4/32    *[Local/0] 01:27:28
                       Local via ge-0/0/1.203
10.255.227.0/31    *[Direct/0] 01:27:27
                    >  via ge-0/0/2.201
10.255.227.0/32    *[Local/0] 01:27:27
                       Local via ge-0/0/2.201
10.255.227.2/31    *[Direct/0] 01:27:27
                    >  via ge-0/0/2.202
10.255.227.2/32    *[Local/0] 01:27:27
                       Local via ge-0/0/2.202
10.255.227.4/31    *[Direct/0] 01:27:27
                    >  via ge-0/0/2.203
10.255.227.4/32    *[Local/0] 01:27:27
                       Local via ge-0/0/2.203
172.16.192.1/32    *[BGP/170] 01:27:03, localpref 100, from 10.255.225.1
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.225.1 via ge-0/0/1.201
                    >  to 10.255.227.1 via ge-0/0/2.201
                    [BGP/170] 01:27:03, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.227.1 via ge-0/0/2.201
172.16.192.2/32    *[BGP/170] 01:26:28, localpref 100, from 10.255.225.1
                      AS path: 64911 65002 65004 65006 I, validation-state: unverified
                       to 10.255.225.1 via ge-0/0/1.201
                    >  to 10.255.227.1 via ge-0/0/2.201
                    [BGP/170] 01:26:28, localpref 100
                      AS path: 64911 65001 65004 65006 I, validation-state: unverified
                    >  to 10.255.227.1 via ge-0/0/2.201
172.16.192.3/32    *[BGP/170] 01:26:28, localpref 100, from 10.255.225.3
                      AS path: 64911 65002 65004 65006 I, validation-state: unverified
                       to 10.255.225.3 via ge-0/0/1.202
                    >  to 10.255.227.3 via ge-0/0/2.202
                    [BGP/170] 01:26:28, localpref 100
                      AS path: 64911 65001 65004 65006 I, validation-state: unverified
                    >  to 10.255.227.3 via ge-0/0/2.202
172.16.192.4/32    *[BGP/170] 01:26:28, localpref 100, from 10.255.225.5
                      AS path: 64911 65002 65004 65006 I, validation-state: unverified
                       to 10.255.225.5 via ge-0/0/1.203
                    >  to 10.255.227.5 via ge-0/0/2.203
                    [BGP/170] 01:26:28, localpref 100
                      AS path: 64911 65001 65004 65006 I, validation-state: unverified
                    >  to 10.255.227.5 via ge-0/0/2.203
172.16.192.5/32    *[BGP/170] 01:27:03, localpref 100, from 10.255.225.3
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.225.3 via ge-0/0/1.202
                    >  to 10.255.227.3 via ge-0/0/2.202
                    [BGP/170] 01:27:03, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.227.3 via ge-0/0/2.202
172.16.192.6/32    *[BGP/170] 01:27:03, localpref 100, from 10.255.225.5
                      AS path: 64911 65002 65003 65005 I, validation-state: unverified
                       to 10.255.225.5 via ge-0/0/1.203
                    >  to 10.255.227.5 via ge-0/0/2.203
                    [BGP/170] 01:27:03, localpref 100
                      AS path: 64911 65001 65003 65005 I, validation-state: unverified
                    >  to 10.255.227.5 via ge-0/0/2.203
172.16.192.7/32    *[BGP/170] 01:27:22, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.225.1 via ge-0/0/1.201
                    [BGP/170] 01:27:17, localpref 100
                      AS path: 64911 65001 65003 65002 I, validation-state: unverified
                    >  to 10.255.227.1 via ge-0/0/2.201
172.16.192.8/32    *[BGP/170] 01:27:19, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.225.3 via ge-0/0/1.202
                    [BGP/170] 01:27:12, localpref 100
                      AS path: 64911 65001 65003 65002 I, validation-state: unverified
                    >  to 10.255.227.3 via ge-0/0/2.202
172.16.192.9/32    *[BGP/170] 01:27:14, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.225.5 via ge-0/0/1.203
                    [BGP/170] 01:27:23, localpref 100
                      AS path: 64911 65001 65003 65002 I, validation-state: unverified
                    >  to 10.255.227.5 via ge-0/0/2.203
172.16.192.10/32   *[BGP/170] 01:27:17, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.227.1 via ge-0/0/2.201
                    [BGP/170] 01:27:22, localpref 100
                      AS path: 64911 65002 65003 65001 I, validation-state: unverified
                    >  to 10.255.225.1 via ge-0/0/1.201
172.16.192.11/32   *[BGP/170] 01:27:12, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.227.3 via ge-0/0/2.202
                    [BGP/170] 01:27:19, localpref 100
                      AS path: 64911 65002 65003 65001 I, validation-state: unverified
                    >  to 10.255.225.3 via ge-0/0/1.202
172.16.192.12/32   *[BGP/170] 01:27:23, localpref 100
                      AS path: 64911 I, validation-state: unverified
                    >  to 10.255.227.5 via ge-0/0/2.203
                    [BGP/170] 01:27:14, localpref 100
                      AS path: 64911 65002 65003 65001 I, validation-state: unverified
                    >  to 10.255.225.5 via ge-0/0/1.203
192.168.231.0/24   *[Direct/0] 01:27:28
                    >  via ge-0/0/0.0
192.168.231.98/32  *[Local/0] 01:27:28
                       Local via ge-0/0/0.0
Juniper SRX Series Firewall as WAN Router
The following example table and configurations show the differences between using an SRX Series Firewall in cluster mode and an MX router as the WAN router. On the fabric side, only the interface names of the SRX cluster change from the MX router configuration. Because the SRX Series Firewall runs in active/active cluster mode, there is only a single WAN router configuration and a single ASN to consider. That single configuration also includes cluster management and trust-zone management commands that are not present in a similar MX router-based configuration.
This SRX Series Firewall-based approach is less complicated than configuring redundant ethernet (reth) interfaces and link aggregation groups (LAG) on the MX router. In addition, there is need for additional CLI on the fabric side to insert virtual gateways, and so on.
Preventing Potential Asymmetric Route Issues Using As-Path Prepending
When stateful firewalls are connected to a fabric, there's a potential risk of asymmetric routing. Consider the following scenario: a client outside the fabric initiates a TCP connection to a client inside the fabric via the WAN router. During the initial TCP three-way handshake, the SYN packet is handled by the first WAN router. However, the SYN-ACK response from the fabric client may be processed by the second WAN router since both routers advertise the same default route into the fabric. The fabric, unaware of any preference, may choose the second WAN router due to ECMP load balancing or other internal mechanisms. If the stateful firewalls (acting as WAN routers) do not share session state, the second WAN router may drop the return packet, as it has no record of the session initiated through the first WAN router.
To prevent this issue, you can make the default route advertised by the second WAN router less preferred, ensuring that return traffic, under normal conditions, is directed to the first WAN router. In BGP, this is typically achieved through AS-Path prepending, which makes the route to the second WAN router less attractive. In the SRX cluster configuration shown below, we use two export filters toward the fabric—one of which includes AS-path prepending for the default route. These filters are then applied to the fabric neighbors based on which WAN router should be less preferred.
set policy-options policy-statement internet0 term 1 from protocol static
set policy-options policy-statement internet0 term 1 from route-filter 0.0.0.0/0 exact
set policy-options policy-statement internet0 term 1 then accept
set policy-options policy-statement internet0 term 2 then reject
set policy-options policy-statement internet1 term 1 from protocol static
set policy-options policy-statement internet1 term 1 from route-filter 0.0.0.0/0 exact
set policy-options policy-statement internet1 term 1 then as-path-prepend "64999 64999"
set policy-options policy-statement internet1 term 1 then accept
set policy-options policy-statement internet1 term 2 then reject
Once BGP peering with the fabric is established, you can verify the default routes received by the fabric. In the example below, the core1 switch serves as the service block function.
root@core1> show route aspath-regex ".* 64901 .*"
.
devices.inet.0: 13 destinations, 19 routes (13 active, 0 holddown, 0 hidden)
@ = Routing Use Only, # = Forwarding Use Only
+ = Active Route, - = Last Active, * = Both
.
0.0.0.0/0          *[BGP/170] 00:10:21, localpref 100
                      AS path: 64901 I, validation-state: unverified
                    >  to 10.255.224.4 via ge-0/0/5.103
                    [BGP/170] 00:10:21, localpref 100
                      AS path: 64999 64999 64901 I, validation-state: unverified
                    >  to 10.255.225.4 via ge-0/0/6.203
                    [EVPN/170] 00:10:21
                    >  to 10.255.240.7 via ge-0/0/1.0
                       to 10.255.240.9 via ge-0/0/2.0
.
customerb.inet.0: 14 destinations, 20 routes (14 active, 0 holddown, 0 hidden)
@ = Routing Use Only, # = Forwarding Use Only
+ = Active Route, - = Last Active, * = Both
.
0.0.0.0/0          *[BGP/170] 00:10:21, localpref 100
                      AS path: 64901 I, validation-state: unverified
                    >  to 10.255.224.2 via ge-0/0/5.102
                    [BGP/170] 00:10:21, localpref 100
                      AS path: 64999 64999 64901 I, validation-state: unverified
                    >  to 10.255.225.2 via ge-0/0/6.202
                    [EVPN/170] 00:10:21
                    >  to 10.255.240.7 via ge-0/0/1.0
                       to 10.255.240.9 via ge-0/0/2.0
.
customera.inet.0: 14 destinations, 20 routes (14 active, 0 holddown, 0 hidden)
@ = Routing Use Only, # = Forwarding Use Only
+ = Active Route, - = Last Active, * = Both
.
0.0.0.0/0          *[BGP/170] 00:08:53, localpref 100
                      AS path: 64901 I, validation-state: unverified
                    >  to 10.255.224.0 via ge-0/0/5.101
                    [BGP/170] 00:08:53, localpref 100
                      AS path: 64999 64999 64901 I, validation-state: unverified
                    >  to 10.255.225.0 via ge-0/0/6.201
                    [EVPN/170] 00:08:53
                    >  to 10.255.240.7 via ge-0/0/1.0
                       to 10.255.240.9 via ge-0/0/2.0
.
A similar approach is recommended for the fabric configuration
to ensure uplink traffic consistently prefers one WAN router. This
is achieved by making the routes advertised to the second WAN
router less attractive using AS-path prepending. Unlike the MX
router example above, which uses a shared
“export-vrfs” filter, we now use two
separate filters—“export-vrfs0” and
“export-vrfs1”—as shown in Figure 22.
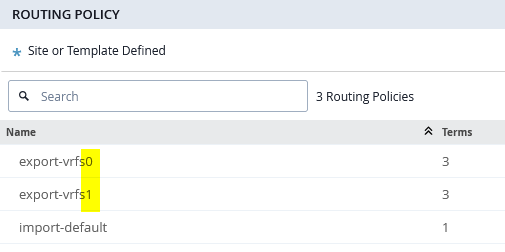
They may look the same but all statements in “export-vrfs1” have AP-path
prepending configured as in Figure 23.
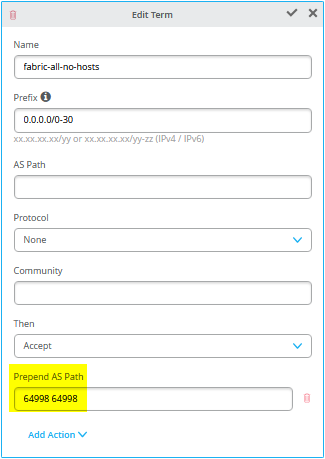
Once BGP peering with the SRX cluster is established, verify that the AS-path prepends in the fabric are visible, as shown in the example below from the SRX cluster. Start by checking the configuration on the fabric’s service block function—in this case, the core1 switch.
root@core1> show configuration | display set | match export-vrf
set groups top policy-options policy-statement export-vrfs0 term 01_exclude-default from route-filter-list 0-0-0-0_0
set groups top policy-options policy-statement export-vrfs0 term 01_exclude-default then reject
set groups top policy-options policy-statement export-vrfs0 term 02_fabric-all-no-hosts from route-filter-list 0-0-0-0_0-30
set groups top policy-options policy-statement export-vrfs0 term 02_fabric-all-no-hosts then accept
set groups top policy-options policy-statement export-vrfs0 term 03_overlaylo0 from route-filter-list 172-16-192-0_24-32
set groups top policy-options policy-statement export-vrfs0 term 03_overlaylo0 then accept
set groups top policy-options policy-statement export-vrfs1 term 01_exclude-default from route-filter-list 0-0-0-0_0
set groups top policy-options policy-statement export-vrfs1 term 01_exclude-default then reject
set groups top policy-options policy-statement export-vrfs1 term 02_fabric-all-no-hosts from route-filter-list 0-0-0-0_0-30
set groups top policy-options policy-statement export-vrfs1 term 02_fabric-all-no-hosts then as-path-prepend "64998 64998"
set groups top policy-options policy-statement export-vrfs1 term 02_fabric-all-no-hosts then accept
set groups top policy-options policy-statement export-vrfs1 term 03_overlaylo0 from route-filter-list 172-16-192-0_24-32
set groups top policy-options policy-statement export-vrfs1 term 03_overlaylo0 then as-path-prepend "64998 64998"
set groups top policy-options policy-statement export-vrfs1 term 03_overlaylo0 then accept
set groups top routing-instances customera protocols bgp group customera0 export export-vrfs0
set groups top routing-instances customera protocols bgp group customera1 export export-vrfs1
set groups top routing-instances customerb protocols bgp group customerb0 export export-vrfs0
set groups top routing-instances customerb protocols bgp group customerb1 export export-vrfs1
set groups top routing-instances devices protocols bgp group devices0 export export-vrfs0
set groups top routing-instances devices protocols bgp group devices1 export export-vrfs1
#
set groups top policy-options route-filter-list 0-0-0-0_0 0.0.0.0/0 exact
set groups top policy-options route-filter-list 0-0-0-0_0-30 0.0.0.0/0 upto /30
set groups top policy-options route-filter-list 172-16-192-0_24-32 172.16.192.0/24 upto /32
Then, we also ensure that we receive those routes according to our configuration on the SRX cluster as in the example below.
# neighbor-IP:10.255.224.1 which is assigned on srx-cluster to vrf:customera interface ge-0/0/2.1091
root@srx1> show route receive-protocol bgp 10.255.224.1
.
public-int.inet.0: 46 destinations, 101 routes (46 active, 0 holddown, 0 hidden)
  Prefix                  Nexthop              MED     Lclpref    AS path
* 10.99.91.0/24           10.255.224.1                            64911 65002 65004 65005 I
* 10.99.99.0/24           10.255.224.1                            64911 65002 65004 65005 I
* 172.16.192.1/32         10.255.224.1                            64911 65002 65004 65005 I
* 172.16.192.4/32         10.255.224.1                            64911 65002 65004 65006 I
* 172.16.192.7/32         10.255.224.1                            64911 I
  172.16.192.10/32        10.255.224.1                            64911 65002 65004 65001 I
.
# neighbor-IP:10.255.226.1 which is assigned on srx-cluster to vrf:customera interface ge-0/0/3.1091
root@srx1> show route receive-protocol bgp 10.255.226.1
.
public-int.inet.0: 46 destinations, 101 routes (46 active, 0 holddown, 0 hidden)
  Prefix                  Nexthop              MED     Lclpref    AS path
  10.99.91.0/24           10.255.226.1                            64911 65001 65004 65005 I
  10.99.99.0/24           10.255.226.1                            64911 65001 65004 65005 I
  172.16.192.1/32         10.255.226.1                            64911 65001 65004 65005 I
  172.16.192.4/32         10.255.226.1                            64911 65001 65004 65006 I
  172.16.192.7/32         10.255.226.1                            64911 65001 65004 65002 I
* 172.16.192.10/32        10.255.226.1                            64911 I
.
# neighbor-IP:10.255.225.1 which is assigned on srx-cluster to vrf:customera interface ge-7/0/2.1099
root@srx1> show route receive-protocol bgp 10.255.225.1
.
public-int.inet.0: 46 destinations, 101 routes (46 active, 0 holddown, 0 hidden)
  Prefix                  Nexthop              MED     Lclpref    AS path
  10.99.91.0/24           10.255.225.1                            64998 64998 64911 65002 65004 65005 I
  10.99.99.0/24           10.255.225.1                            64998 64998 64911 65002 65004 65005 I
  172.16.192.1/32         10.255.225.1                            64998 64998 64911 65002 65004 65005 I
  172.16.192.4/32         10.255.225.1                            64998 64998 64911 65002 65004 65006 I
  172.16.192.7/32         10.255.225.1                            64998 64998 64911 I
  172.16.192.10/32        10.255.225.1                            64998 64998 64911 65002 65004 65001 I
.
# neighbor-IP:10.255.227.1 which is assigned on srx-cluster to vrf:customera interface ge-7/0/3.1099
root@srx1> show route receive-protocol bgp 10.255.227.1
.
public-int.inet.0: 46 destinations, 101 routes (46 active, 0 holddown, 0 hidden)
  Prefix                  Nexthop              MED     Lclpref    AS path
  10.99.91.0/24           10.255.227.1                            64998 64998 64911 65001 65004 65005 I
  10.99.99.0/24           10.255.227.1                            64998 64998 64911 65001 65004 65005 I
  172.16.192.1/32         10.255.227.1                            64998 64998 64911 65001 65004 65005 I
  172.16.192.4/32         10.255.227.1                            64998 64998 64911 65001 65004 65006 I
  172.16.192.7/32         10.255.227.1                            64998 64998 64911 65001 65004 65002 I
  172.16.192.10/32        10.255.227.1                            64998 64998 64911 I
Table 2 shows the configuration information for the core1 and core2 switches as service block function along with the WAN router configuration for the SRX cluster. We’ve marked the changes with respect to Table 1 (for MX WAN routers in bold).
| Switch | Switch AS | VRF | Core P2P IP | Core IF | WAN Router | WAN Router P2P IP | WAN Router AS | WAN Router IF | VLAN ID |
|---|---|---|---|---|---|---|---|---|---|
| core1 | 64911 | customera | 10.255.224.1/31 | ge-0/0/5.101 | node0 | 10.255.224.0/31 | 64901 | ge-0/0/2.101 | 101 |
| core1 | 64911 | customerb | 10.255.224.3/31 | ge-0/0/5.102 | node0 | 10.255.224.2/31 | 64901 | ge-0/0/2.102 | 102 |
| core1 | 64911 | devices | 10.255.224.5/31 | ge-0/0/5.103 | node0 | 10.255.224.4/31 | 64901 | ge-0/0/2.103 | 103 |
| core1 | 64911 | customera | 10.255.225.1/31 | ge-0/0/6.101 | node1 | 10.255.225.0/31 | 64901 | ge-7/0/2.101 | 101 |
| core1 | 64911 | customerb | 10.255.225.3/31 | ge-0/0/6.102 | node1 | 10.255.225.2/31 | 64901 | ge-7/0/2.102 | 102 |
| core1 | 64911 | devices | 10.255.225.5/31 | ge-0/0/6.103 | node1 | 10.255.225.4/31 | 64901 | ge-7/0/2.103 | 103 |
| core2 | 64911 | customera | 10.255.226.1/31 | ge-0/0/5.201 | node0 | 10.255.226.0/31 | 64901 | ge-0/0/3.201 | 201 |
| core2 | 64911 | customerb | 10.255.226.3/31 | ge-0/0/5.202 | node0 | 10.255.226.2/31 | 64901 | ge-0/0/3.202 | 202 |
| core2 | 64911 | devices | 10.255.226.5/31 | ge-0/0/5.203 | node0 | 10.255.226.4/31 | 64901 | ge-0/0/3.203 | 203 |
| core2 | 64911 | customera | 10.255.227.1/31 | ge-0/0/6.201 | node1 | 10.255.227.0/31 | 64901 | ge-7/0/3.201 | 201 |
| core2 | 64911 | customerb | 10.255.227.3/31 | ge-0/0/6.202 | node1 | 10.255.227.2/31 | 64901 | ge-7/0/3.202 | 202 |
| core2 | 64911 | devices | 10.255.227.5/31 | ge-0/0/6.203 | node1 | 10.255.227.4/31 | 64901 | ge-7/0/3.203 | 203 |
The following pseudocode describes what you need to configure on the core1 switch for this example:
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
# create network name:trans201 with VLAN-ID:201
# create network name:trans202 with VLAN-ID:202
# create network name:trans203 with VLAN-ID:203
#
# configure the Additional IP-Subnet 10.255.224.1/31 to Network/VLAN:trans101
# configure the Additional IP-Subnet 10.255.224.3/31 to Network/VLAN:trans102
# configure the Additional IP-Subnet 10.255.224.5/31 to Network/VLAN:trans103
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/5 as L3-Sub-Interfaces with MTU=9018
#
# configure the Additional IP-Subnet 10.255.225.1/31 to Network/VLAN:trans201
# configure the Additional IP-Subnet 10.255.225.3/31 to Network/VLAN:trans202
# configure the Additional IP-Subnet 10.255.225.5/31 to Network/VLAN:trans203
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/6 as L3-Sub-Interfaces with MTU=9018
#
# configure on VRF
# configure on instance customera
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans101
# add to existing overlay-vlans the vlan:trans201
#
# configure on instance customerb
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans102
# add to existing overlay-vlans the vlan:trans202
#
# configure on instance devices
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans103
# add to existing overlay-vlans the vlan:trans203
#
# Enable BGP
# Create an Import policy called 'export-vrfs0'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default Prefix=0.0.0.0/0 Protocol=None Then=Reject
# - Add Term w. Name=fabric-all-no-hosts Prefix=0.0.0.0/0-30 Protocol=None Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32 Protocol=None Then=Accept
#
# Create an Export policy called 'export-vrfs1'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default Prefix=0.0.0.0/0 Protocol=None Then=Reject
# - Add Term w. Name=fabric-all-no-hosts Prefix=0.0.0.0/0-30 Protocol=None Then=Accept Add Action->Prepend AS Path='64998 64998'
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32 Protocol=None Then=Accept Add Action->Prepend AS Path='64998 64998'
#
# Create an Export policy called 'import-default'
# - Name=default Prefix=0.0.0.0/0 Protocol=BGP Action=Accept
#
# Create a BGP Group with:
# - Name=customera0
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs0 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.224.0 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb0
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs0 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.224.2 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices0
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs0 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.224.4 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=customera1
# - Type=External
# - Network (VLAN)=trans201
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs1 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.225.0 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb1
# - Type=External
# - Network (VLAN)=trans202
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs1 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.225.2 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices1
# - Type=External
# - Network (VLAN)=trans203
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs1 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.225.4 Neighbor_AS=64901 Hold-Time=90
The following pseudocode describes what you need to configure on the core2 switch for this example:
# create the following transport networks either in a switch-template or locally on each service switch
# create network name:trans101 with VLAN-ID:101
# create network name:trans102 with VLAN-ID:102
# create network name:trans103 with VLAN-ID:103
# create network name:trans201 with VLAN-ID:201
# create network name:trans202 with VLAN-ID:202
# create network name:trans203 with VLAN-ID:203
#
# configure the Additional IP-Subnet 10.255.226.1/31 to Network/VLAN:trans101
# configure the Additional IP-Subnet 10.255.226.3/31 to Network/VLAN:trans102
# configure the Additional IP-Subnet 10.255.226.5/31 to Network/VLAN:trans103
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/5 as L3-Sub-Interfaces with MTU=9018
#
# configure the Additional IP-Subnet 10.255.227.1/31 to Network/VLAN:trans201
# configure the Additional IP-Subnet 10.255.227.3/31 to Network/VLAN:trans202
# configure the Additional IP-Subnet 10.255.227.5/31 to Network/VLAN:trans203
# Then bind these 3 Network/VLANs to Port Interface ge-0/0/6 as L3-Sub-Interfaces with MTU=9018
#
# configure on VRF
# configure on instance customera
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans101
# add to existing overlay-vlans the vlan:trans201
#
# configure on instance customerb
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans102
# add to existing overlay-vlans the vlan:trans202
#
# configure on instance devices
# Override Template Defined VRF Instance=Checked/Enabled
# add to existing overlay-vlans the vlan:trans103
# add to existing overlay-vlans the vlan:trans203
#
# Enable BGP
# Create an Export policy called 'export-vrfs0'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default Prefix=0.0.0.0/0 Protocol=None Then=Reject
# - Add Term w. Name=fabric-all-no-hosts Prefix=0.0.0.0/0-30 Protocol=None Then=Accept
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32 Protocol=None Then=Accept
#
# Create an Export policy called 'export-vrfs1'
# Add to this export Policy the following Networks as:
# - Add Term w. Name=exclude-default Prefix=0.0.0.0/0 Protocol=None Then=Reject
# - Add Term w. Name=fabric-all-no-hosts Prefix=0.0.0.0/0-30 Protocol=None Then=Accept Add Action->Prepend AS Path='64998 64998'
# - Add Term w. Name=overlaylo0 Prefix=172.16.192.0/24-32 Protocol=None Then=Accept Add Action->Prepend AS Path='64998 64998'
#
# Create an Export policy called 'import-default'
# - Name=default Prefix=0.0.0.0/0 Protocol=BGP Action=Accept
#
# Create a BGP Group with:
# - Name=customera0
# - Type=External
# - Network (VLAN)=trans101
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs0 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.226.0 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb0
# - Type=External
# - Network (VLAN)=trans102
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs0 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.226.2 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices0
# - Type=External
# - Network (VLAN)=trans103
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs0 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.226.4 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=customera1
# - Type=External
# - Network (VLAN)=trans201
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs1 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.227.0 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=customerb1
# - Type=External
# - Network (VLAN)=trans202
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs1 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.227.2 Neighbor_AS=64901 Hold-Time=90
#
# Create a BGP Group with:
# - Name=devices1
# - Type=External
# - Network (VLAN)=trans203
# - BFD interval=1000
# - Local AS=64911
# - Hold Time=90
# - Set Export=export-vrfs1 and Import=import-default
# Add also the following Neighbor
# - IP_Address=10.255.227.4 Neighbor_AS=64901 Hold-Time=90
When finished configuring the individual service block functions (here, the core1 and core2 switches) your overview table should be as shown in Figure 24.
Figure 24 shows an overview of how the BGP looks after you have configured the individual service block functions for the core1 and core2 switches.
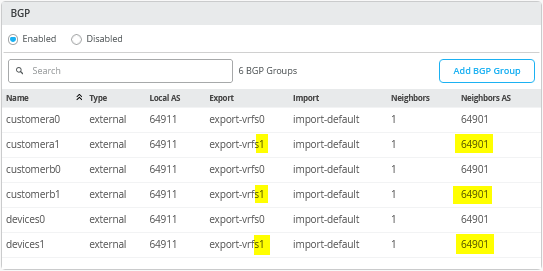
The following Junos OS CLI represents the entire configuration needed on the SRX Series Firewall cluster for this example.
set groups node0 system host-name srx1_node0
set groups node1 system host-name srx2_node1
set apply-groups "${node}"
set chassis aggregated-devices ethernet device-count 10
set chassis cluster control-link-recovery
set chassis cluster reth-count 5
set chassis cluster initial-hold 60
set chassis cluster redundancy-group 1 node 0 priority 200
set chassis cluster redundancy-group 1 node 1 priority 100
set chassis cluster redundancy-group 1 gratuitous-arp-count 4
# Interface monitoring turned OFF for vSRX
# set chassis cluster redundancy-group 1 interface-monitor ge-0/0/2 weight 255
# set chassis cluster redundancy-group 1 interface-monitor ge-0/0/3 weight 255
# set chassis cluster redundancy-group 1 interface-monitor ge-7/0/2 weight 255
# set chassis cluster redundancy-group 1 interface-monitor ge-7/0/3 weight 255
set interfaces fab0 fabric-options member-interfaces ge-0/0/0
set interfaces fab1 fabric-options member-interfaces ge-7/0/0
#
# rebuild trust zone to clear old interfaces bound
delete security zones security-zone trust
set security zones security-zone trust tcp-rst
set security zones security-zone trust host-inbound-traffic system-services all
set security zones security-zone trust host-inbound-traffic protocols all
#
delete interfaces ge-0/0/2
set interfaces ge-0/0/2 flexible-vlan-tagging
set interfaces ge-0/0/2 mtu 9018
set interfaces ge-0/0/2 unit 101 description trans101
set interfaces ge-0/0/2 unit 101 vlan-id 101
set interfaces ge-0/0/2 unit 101 family inet address 10.255.224.0/31
set security zones security-zone trust interfaces ge-0/0/2.101 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-0/0/2.101 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-0/0/2.101 host-inbound-traffic system-services ping
set interfaces ge-0/0/2 unit 102 description trans102
set interfaces ge-0/0/2 unit 102 vlan-id 102
set interfaces ge-0/0/2 unit 102 family inet address 10.255.224.2/31
set security zones security-zone trust interfaces ge-0/0/2.102 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-0/0/2.102 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-0/0/2.102 host-inbound-traffic system-services ping
set interfaces ge-0/0/2 unit 103 description trans103
set interfaces ge-0/0/2 unit 103 vlan-id 103
set interfaces ge-0/0/2 unit 103 family inet address 10.255.224.4/31
set security zones security-zone trust interfaces ge-0/0/2.103 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-0/0/2.103 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-0/0/2.103 host-inbound-traffic system-services ping
#
delete interfaces ge-0/0/3
set interfaces ge-0/0/3 flexible-vlan-tagging
set interfaces ge-0/0/3 mtu 9018
set interfaces ge-0/0/3 unit 101 description trans101
set interfaces ge-0/0/3 unit 101 vlan-id 101
set interfaces ge-0/0/3 unit 101 family inet address 10.255.226.0/31
set security zones security-zone trust interfaces ge-0/0/3.101 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-0/0/3.101 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-0/0/3.101 host-inbound-traffic system-services ping
set interfaces ge-0/0/3 unit 102 description trans102
set interfaces ge-0/0/3 unit 102 vlan-id 102
set interfaces ge-0/0/3 unit 102 family inet address 10.255.226.2/31
set security zones security-zone trust interfaces ge-0/0/3.102 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-0/0/3.102 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-0/0/3.102 host-inbound-traffic system-services ping
set interfaces ge-0/0/3 unit 103 description trans103
set interfaces ge-0/0/3 unit 103 vlan-id 103
set interfaces ge-0/0/3 unit 103 family inet address 10.255.226.4/31
set security zones security-zone trust interfaces ge-0/0/3.103 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-0/0/3.103 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-0/0/3.103 host-inbound-traffic system-services ping
delete interfaces ge-7/0/2
set interfaces ge-7/0/2 flexible-vlan-tagging
set interfaces ge-7/0/2 mtu 9018
set interfaces ge-7/0/2 unit 201 description trans201
set interfaces ge-7/0/2 unit 201 vlan-id 201
set interfaces ge-7/0/2 unit 201 family inet address 10.255.225.0/31
set security zones security-zone trust interfaces ge-7/0/2.201 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-7/0/2.201 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-7/0/2.201 host-inbound-traffic system-services ping
set interfaces ge-7/0/2 unit 202 description trans202
set interfaces ge-7/0/2 unit 202 vlan-id 202
set interfaces ge-7/0/2 unit 202 family inet address 10.255.225.2/31
set security zones security-zone trust interfaces ge-7/0/2.202 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-7/0/2.202 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-7/0/2.202 host-inbound-traffic system-services ping
set interfaces ge-7/0/2 unit 203 description trans203
set interfaces ge-7/0/2 unit 203 vlan-id 203
set interfaces ge-7/0/2 unit 203 family inet address 10.255.225.4/31
set security zones security-zone trust interfaces ge-7/0/2.203 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-7/0/2.203 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-7/0/2.203 host-inbound-traffic system-services ping
#
delete interfaces ge-7/0/3
set interfaces ge-7/0/3 flexible-vlan-tagging
set interfaces ge-7/0/3 mtu 9018
set interfaces ge-7/0/3 unit 201 description trans201
set interfaces ge-7/0/3 unit 201 vlan-id 201
set interfaces ge-7/0/3 unit 201 family inet address 10.255.227.0/31
set security zones security-zone trust interfaces ge-7/0/3.201 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-7/0/3.201 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-7/0/3.201 host-inbound-traffic system-services ping
set interfaces ge-7/0/3 unit 202 description trans202
set interfaces ge-7/0/3 unit 202 vlan-id 202
set interfaces ge-7/0/3 unit 202 family inet address 10.255.227.2/31
set security zones security-zone trust interfaces ge-7/0/3.202 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-7/0/3.202 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-7/0/3.202 host-inbound-traffic system-services ping
set interfaces ge-7/0/3 unit 203 description trans203
set interfaces ge-7/0/3 unit 203 vlan-id 203
set interfaces ge-7/0/3 unit 203 family inet address 10.255.227.4/31
set security zones security-zone trust interfaces ge-7/0/3.203 host-inbound-traffic protocols bgp
set security zones security-zone trust interfaces ge-7/0/3.203 host-inbound-traffic protocols bfd
set security zones security-zone trust interfaces ge-7/0/3.203 host-inbound-traffic system-services ping
#
# needed in and export policy
delete policy-options
set policy-options policy-statement fabric term 1 from protocol bgp
set policy-options policy-statement fabric term 1 from route-filter 0.0.0.0/0 orlonger
set policy-options policy-statement fabric term 1 then accept
set policy-options policy-statement fabric term 3 then reject
set policy-options policy-statement internet0 term 1 from protocol static
set policy-options policy-statement internet0 term 1 from route-filter 0.0.0.0/0 exact
set policy-options policy-statement internet0 term 1 then accept
set policy-options policy-statement internet0 term 3 then reject
set policy-options policy-statement internet1 term 1 from protocol static
set policy-options policy-statement internet1 term 1 from route-filter 0.0.0.0/0 exact
set policy-options policy-statement internet1 term 1 then as-path-prepend "64999 64999"
set policy-options policy-statement internet1 term 1 then accept
set policy-options policy-statement internet1 term 3 then reject
#
delete routing-instances public-int
set routing-instances public-int instance-type virtual-router
set routing-instances public-int interface ge-0/0/2.101
set routing-instances public-int interface ge-0/0/2.102
set routing-instances public-int interface ge-0/0/2.103
set routing-instances public-int interface ge-0/0/3.101
set routing-instances public-int interface ge-0/0/3.102
set routing-instances public-int interface ge-0/0/3.103
set routing-instances public-int interface ge-7/0/2.201
set routing-instances public-int interface ge-7/0/2.202
set routing-instances public-int interface ge-7/0/2.203
set routing-instances public-int interface ge-7/0/3.201
set routing-instances public-int interface ge-7/0/3.202
set routing-instances public-int interface ge-7/0/3.203
#
delete routing-instances public-int protocols bgp group customera
delete routing-instances public-int protocols bgp group customera0
set routing-instances public-int protocols bgp group customera0 type external
set routing-instances public-int protocols bgp group customera0 family inet unicast
set routing-instances public-int protocols bgp group customera0 multipath multiple-as
set routing-instances public-int protocols bgp group customera0 local-as 64901
set routing-instances public-int protocols bgp group customera0 hold-time 90
set routing-instances public-int protocols bgp group customera0 import fabric
set routing-instances public-int protocols bgp group customera0 export internet0
set routing-instances public-int protocols bgp group customera0 bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customera0 bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customera0 bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customera0 neighbor 10.255.224.1 peer-as 64911
set routing-instances public-int protocols bgp group customera0 neighbor 10.255.226.1 peer-as 64911
#
delete routing-instances public-int protocols bgp group customera1
set routing-instances public-int protocols bgp group customera1 type external
set routing-instances public-int protocols bgp group customera1 family inet unicast
set routing-instances public-int protocols bgp group customera1 multipath multiple-as
set routing-instances public-int protocols bgp group customera1 local-as 64901
set routing-instances public-int protocols bgp group customera1 hold-time 90
set routing-instances public-int protocols bgp group customera1 import fabric
set routing-instances public-int protocols bgp group customera1 export internet1
set routing-instances public-int protocols bgp group customera1 bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customera1 bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customera1 bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customera1 neighbor 10.255.225.1 peer-as 64911
set routing-instances public-int protocols bgp group customera1 neighbor 10.255.227.1 peer-as 64911
#
delete routing-instances public-int protocols bgp group customerb
delete routing-instances public-int protocols bgp group customerb0
set routing-instances public-int protocols bgp group customerb0 type external
set routing-instances public-int protocols bgp group customerb0 family inet unicast
set routing-instances public-int protocols bgp group customerb0 multipath multiple-as
set routing-instances public-int protocols bgp group customerb0 local-as 64901
set routing-instances public-int protocols bgp group customerb0 hold-time 90
set routing-instances public-int protocols bgp group customerb0 import fabric
set routing-instances public-int protocols bgp group customerb0 export internet0
set routing-instances public-int protocols bgp group customerb0 bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customerb0 bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customerb0 bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customerb0 neighbor 10.255.224.3 peer-as 64911
set routing-instances public-int protocols bgp group customerb0 neighbor 10.255.226.3 peer-as 64911
#
delete routing-instances public-int protocols bgp group customerb1
set routing-instances public-int protocols bgp group customerb1 type external
set routing-instances public-int protocols bgp group customerb1 family inet unicast
set routing-instances public-int protocols bgp group customerb1 multipath multiple-as
set routing-instances public-int protocols bgp group customerb1 local-as 64901
set routing-instances public-int protocols bgp group customerb1 hold-time 90
set routing-instances public-int protocols bgp group customerb1 import fabric
set routing-instances public-int protocols bgp group customerb1 export internet1
set routing-instances public-int protocols bgp group customerb1 bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group customerb1 bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group customerb1 bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group customerb1 neighbor 10.255.225.3 peer-as 64911
set routing-instances public-int protocols bgp group customerb1 neighbor 10.255.227.3 peer-as 64911
#
delete routing-instances public-int protocols bgp group devices
delete routing-instances public-int protocols bgp group devices0
set routing-instances public-int protocols bgp group devices0 type external
set routing-instances public-int protocols bgp group devices0 family inet unicast
set routing-instances public-int protocols bgp group devices0 multipath multiple-as
set routing-instances public-int protocols bgp group devices0 local-as 64901
set routing-instances public-int protocols bgp group devices0 hold-time 90
set routing-instances public-int protocols bgp group devices0 import fabric
set routing-instances public-int protocols bgp group devices0 export internet0
set routing-instances public-int protocols bgp group devices0 bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group devices0 bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group devices0 bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group devices0 neighbor 10.255.224.5 peer-as 64911
set routing-instances public-int protocols bgp group devices0 neighbor 10.255.226.5 peer-as 64911
#
delete routing-instances public-int protocols bgp group devices1
set routing-instances public-int protocols bgp group devices1 type external
set routing-instances public-int protocols bgp group devices1 family inet unicast
set routing-instances public-int protocols bgp group devices1 multipath multiple-as
set routing-instances public-int protocols bgp group devices1 local-as 64901
set routing-instances public-int protocols bgp group devices1 hold-time 90
set routing-instances public-int protocols bgp group devices1 import fabric
set routing-instances public-int protocols bgp group devices1 export internet1
set routing-instances public-int protocols bgp group devices1 bfd-liveness-detection minimum-interval 1000
set routing-instances public-int protocols bgp group devices1 bfd-liveness-detection multiplier 3
set routing-instances public-int protocols bgp group devices1 bfd-liveness-detection session-mode automatic
set routing-instances public-int protocols bgp group devices1 neighbor 10.255.225.5 peer-as 64911
set routing-instances public-int protocols bgp group devices1 neighbor 10.255.227.5 peer-as 64911
#
# Do not do SNAT on prefix for WAN-Interface (where the external DHCP-Server may be for Lab)
#
delete security nat source rule-set trust-to-untrust
set security nat source rule-set trust-to-untrust from zone trust
set security nat source rule-set trust-to-untrust to zone untrust
set security nat source rule-set trust-to-untrust rule source-nat-rule1 match destination-address 192.168.10.0/24
set security nat source rule-set trust-to-untrust rule source-nat-rule1 then source-nat off
set security nat source rule-set trust-to-untrust rule source-nat-rule2 match source-address 0.0.0.0/0
set security nat source rule-set trust-to-untrust rule source-nat-rule2 then source-nat interface
#
# WAN-Interfaces example
#
delete interfaces ge-0/0/1
delete interfaces ge-7/0/1
set interfaces ge-0/0/1 unit 0 family inet address 192.168.10.23/24
set interfaces ge-7/0/1 unit 0 family inet address 192.168.10.24/24
#
delete security zones security-zone untrust interfaces ge-0/0/1.0
set security zones security-zone untrust interfaces ge-0/0/1.0 host-inbound-traffic protocols all
set security zones security-zone untrust interfaces ge-0/0/1.0 host-inbound-traffic system-services all
#
delete security zones security-zone untrust interfaces ge-7/0/1.0
set security zones security-zone untrust interfaces ge-7/0/1.0 host-inbound-traffic protocols all
set security zones security-zone untrust interfaces ge-7/0/1.0 host-inbound-traffic system-services all
#
delete routing-instances public-int interface ge-0/0/1.0
delete routing-instances public-int interface ge-7/0/1.0
set routing-instances public-int interface ge-0/0/1.0
set routing-instances public-int interface ge-7/0/1.0
set routing-instances public-int routing-options static route 0.0.0.0/0 next-hop 192.168.10.1