
例:EXシリーズスイッチのポート、VLAN、およびルータートラフィック用のファイアウォールフィルターの設定
この例では、スイッチ上のポート、ネットワーク上のVLAN、スイッチ上のレイヤー3 インターフェイスに出入りするトラフィックを制御するために、ファイアウォールフィルターを構成して適用する方法を示します。ファイアウォールフィルターは、パケットフローの特定の処理ポイントでパケットを転送または拒否するかどうかを決定するパケットフローを定義します。
要件
この例では、以下のソフトウェアおよびハードウェアコンポーネントを使用しています。
-
EXシリーズスイッチ向けJunos OSリリース9.0以降。
-
ジュニパーネットワークス EX3200-48T スイッチ 2 台:1 つはアクセス スイッチとして使用し、もう 1 つは分散型スイッチとして使用
-
ジュニパーネットワークスEX-UM-4SFPアップリンクモジュール1台
-
ジュニパーネットワークスJシリーズルーター1台
この例でファイアウォールフィルターを設定して適用する前に、必ず以下を確認してください。
-
ファイアウォールフィルターの概念、ポリサー、CoSについて理解していること
-
分散型スイッチにアップリンクモジュールが取り付けられていること。 EX3200スイッチへのアップリンクモジュールの取り付けを参照してください。
概要
この構成例では、ファイアウォールフィルターを構成して適用し、パケットの内容を評価し、すべての voice-vlan、 employee-vlan、および guest-vlan トラフィックを処理するEXシリーズスイッチを送信元またはそこから発信するパケットをいつ破棄、転送、分類、カウント、および分析するかを決定するルールを提供する方法を示します。 表1 は、この例でEXシリーズスイッチ用に設定されたファイアウォールフィルターを示しています。
| コンポーネント | 目的/説明 |
|---|---|
|
ポートファイアウォールフィルター、 |
このファイアウォールフィルターは、2つの機能を実行します。
このファイアウォールフィルターは、アクセススイッチ上のポートインターフェイスに適用されます。 |
|
VLANファイアウォールフィルター、 |
不正なデバイスがHTTPセッションを使用して、VoIPコールのコール登録、アドミッション、およびコールステータスを管理するゲートキーバーデバイスを模倣することを防止します。TCPポートまたはUDPポートのみを使用する必要があります。ゲートキーパーのみがHTTPを使用します。つまり、TCPポート上のすべての このファイアウォールフィルターは、アクセススイッチ上のVLANインターフェイスに適用されます。 |
|
VLANファイアウォールフィルター、 |
企業サブネット宛ての このファイアウォールフィルターは、アクセススイッチ上のvlanインターフェイスに適用されます。 |
|
VLANファイアウォールフィルター、 |
ゲスト(非従業員)が このファイアウォールフィルターは、アクセススイッチ上のVLANインターフェイスに適用されます。 |
|
ルーターのファイアウォールフィルター、 |
このファイアウォールフィルターは、分散型スイッチ上のルーティングポート(レイヤー3アップリンクモジュール)に適用されます。 |
図1 は、スイッチ上のポート、VLAN、およびレイヤー3ルーティングファイアウォールフィルターのアプリケーションを示しています。
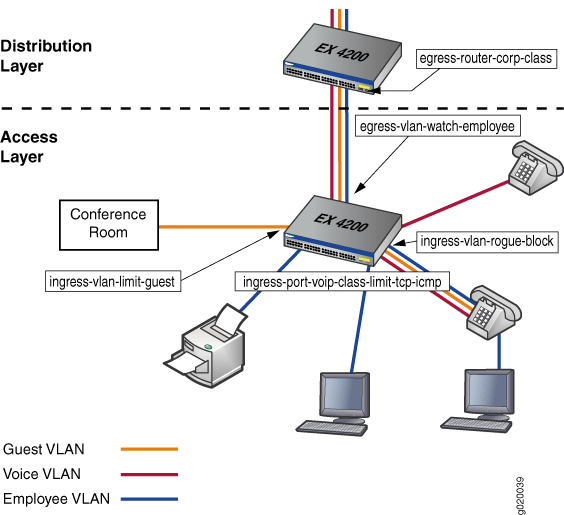
ネットワークトポロジー
この構成例のトポロジーは、アクセスレイヤーに1台のEX-3200-48Tスイッチ、分散型レイヤーに1台のEX-3200-48Tで構成されています。分散型スイッチのアップリンクモジュールは、Jシリーズルーターへのレイヤー3接続をサポートするように構成されています。
EXシリーズスイッチは、VLANメンバーシップをサポートするように構成されています。 表2は 、VLANのVLAN設定コンポーネントを示しています。
|
VLAN名 |
VLAN ID |
VLANサブネットと使用可能なIPアドレス |
VLANの説明 |
|---|---|---|---|
|
|
|
|
従業員VoIPトラフィックに使用する音声VLAN |
|
|
|
|
VLANスタンドアロンPC、VoIP電話のハブを介してネットワークに接続されたPC、無線アクセスポイント、およびプリンター。このVLANには、音声VLANが完全に含まれています。電話に接続するポートには、2つのVLAN |
|
|
|
|
ゲストのデータデバイス(PC)のVLAN。このシナリオは、ロビーや会議室などの訪問者に開放されているエリアを企業が設けており、訪問者は自分のPCをウェブや自社のVPNに接続するためにプラグインできるハブがあることを想定しています。 |
|
|
|
|
企業のセキュリティカメラ用のVLAN。 |
EXシリーズスイッチのポートはパワーオーバーイーサネット(PoE)をサポートしており、ポートに接続するVoIP電話にネットワーク接続と電力の両方を提供します。 表3は 、VLANに割り当てられているスイッチポートと、スイッチポートに接続されたデバイスのIPアドレスとMACアドレスを示しています。
|
スイッチとポート番号 |
VLANメンバーシップ |
IPアドレスとMACアドレス |
ポートデバイス |
|---|---|---|---|
|
ge-0/0/0、ge-0/0/1 |
|
IPアドレス: MACアドレス: |
それぞれが1台のPCに接続された2台のVoIP電話。 |
|
ge-0/0/2、ge-0/0/3 |
|
|
プリンター、無線アクセスポイント |
|
ge-0/0/4、ge-0/0/5 |
|
|
訪問者がPCを接続できる2つのハブ。ロビーや会議室など、訪問者に開放されている場所に設置されたハブ |
|
ge-0/0/6、ge-0/0/7 |
|
|
2台のセキュリティカメラ |
|
ge-0/0/9 |
|
IPアドレス: MACアドレス: |
ゲートキーパーデバイス。ゲートキーパーは、VoIP電話の通話登録、アドミッション、および通話ステータスを管理します。 |
|
ge-0/1/0 |
IPアドレス: |
ルーターへのレイヤー 3 接続。これはスイッチのアップリンクモジュール上のポートであることに注意してください |
音声トラフィックを優先し、TCPおよびICMPトラフィックのレートを制限するイングレスポートファイアウォールフィルターを構成する
ポート、VLAN、およびルーターインターフェイスにファイアウォールフィルターを設定して適用するには、以下のタスクを実行します。
手順
CLIクイックコンフィグレーション
音声トラフィックを優先し、 employee-vlan サブネット宛てのパケットのレートを制限するポートファイアウォールフィルターを素早く構成して適用するには、以下のコマンドをコピーしてスイッチ端末ウィンドウにペーストします。
[edit]
                         set firewall policer tcp-connection-policer if-exceeding burst-size-limit 30k bandwidth-limit 1m
                         set firewall policer tcp-connection-policer then discard
                         set firewall policer icmp-connection-policer if-exceeding burst-size-limit 30k bandwidth-limit 1m
                         set firewall policer icmp-connection-policer then discard
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term voip-high from source-mac-address 00.00.5E.00.53.01
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term voip-high from source-mac-address 00.00.5E.00.53.02
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term voip-high from protocol udp
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term voip-high then forwarding-class expedited-forwarding
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term voip-high then loss-priority low
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term network-control from precedence net-control
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term network-control then forwarding-class network-control
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term network-control then loss-priority low
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term tcp-connection from destination-address 192.0.2.16/28
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term tcp-connection from protocol tcp
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term tcp-connection then policer tcp-connection-policer
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term tcp-connection then count tcp-counter
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term tcp-connection then forwarding-class best-effort
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term tcp-connection then loss-priority high
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term icmp-connection from destination-address 192.0.2.16/28
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term icmp-connection from protocol icmp
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term icmp-connection then policer icmp-connection-policer
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term icmp-connection then count icmp-counter
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term icmp-connection then forwarding-class best-effort
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term icmp-connection then loss-priority high
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term best-effort then forwarding-class best-effort
                         set firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp term best-effort then loss-priority high
                         set interfaces ge-0/0/0 description "voice priority and tcp and icmp traffic rate-limiting filter at ingress port"
                         set interfaces ge-0/0/0 unit 0 family ethernet-switching filter input ingress-port-voip-class-limit-tcp-icmp
                         set interfaces ge-0/0/1 description "voice priority and tcp and icmp traffic rate-limiting filter at ingress port"
                         set interfaces ge-0/0/1 unit 0 family ethernet-switching filter input ingress-port-voip-class-limit-tcp-icmp
                         set class-of-service schedulers voice-high buffer-size percent 15
                         set class-of-service schedulers voice-high  priority high
                         set class-of-service schedulers net-control buffer-size percent 10
                         set class-of-service schedulers net-control priority high
                         set class-of-service schedulers best-effort buffer-size percent 75
                         set class-of-service schedulers best-effort priority low
                         set class-of-service scheduler-maps ethernet-diffsrv-cos-map forwarding-class expedited-forwarding scheduler voice-high
                         set class-of-service scheduler-maps ethernet-diffsrv-cos-map forwarding-class network-control scheduler net-control
                         set class-of-service scheduler-maps ethernet-diffsrv-cos-map forwarding-class best-effort scheduler best-effort
ステップバイステップの手順
音声トラフィックを優先し、 employee-vlan サブネット宛てのパケットのレートを制限するポートファイアウォールフィルターを構成して適用するには:
-
ポリサーの
tcp-connection-policerとicmp-connection-policerを定義します。[edit] user@switch# set firewall policer tcp-connection-policer if-exceeding burst-size-limit 30k bandwidth-limit 1m user@switch# set firewall policer tcp-connection-policer then discard user@switch# set firewall policer icmp-connection-policer if-exceeding burst-size-limit 30k bandwidth-limit 1m user@switch# set firewall policer icmp-connection-policer then discard
-
ファイアウォールフィルター
ingress-port-voip-class-limit-tcp-icmpを定義します。[edit firewall] user@switch# set family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp
-
用語
voip-highを定義します。[edit firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp ] user@switch# set term voip-high from source-mac-address 00.00.5E.00.53.01 user@switch# set term voip-high from source-mac-address 00.00.5E.00.53.02 user@switch# set term voip-high from protocol udp user@switch# set term voip-high then forwarding-class expedited-forwarding user@switch# set term voip-high then loss-priority low
-
用語
network-controlを定義します。[edit firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp ] user@switch# set term network-control from precedence net-control user@switch# set term network-control then forwarding-class network-control user@switch# set term network-control then loss-priority low
-
TCPトラフィックのレート制限を構成する用語
tcp-connectionを定義します。[edit firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp] user@switch# set term tcp-connection from destination-address 192.0.2.16/28 user@switch# set term tcp-connection from protocol tcp user@switch# set term tcp-connection then policer tcp-connection-policer user@switch# set term tcp-connection then count tcp-counter user@switch# set term tcp-connection then forwarding-class best-effort user@switch# set term tcp-connection then loss-priority high
-
ICMPトラフィックのレート制限を構成する条件
icmp-connectionを定義します。[edit firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp] user@switch# set term icmp-connection from destination-address 192.0.2.16/28 user@switch# set term icmp-connection from protocol icmp user@switch# set term icmp-connection then policer icmp-policer user@switch# set term icmp-connection then count icmp-counter user@switch# set term icmp-connection then forwarding-class best-effort user@switch# set term icmp-connection then loss-priority high
-
ファイアウォールフィルター内の他のどの条件にも一致しないすべてのパケットに暗黙的に一致させるため、一致条件なしの条件
best-effortを定義します。[edit firewall family ethernet-switching filter ingress-port-voip-class-limit-tcp-icmp] user@switch# set term best-effort then forwarding-class best-effort user@switch# set term best-effort then loss-priority high
-
ファイアウォールフィルター
ingress-port-voip-class-limit-tcp-icmpを、employee-vlan用のポートインターフェイスへの入力フィルターとして適用します。[edit interfaces] user@switch# set ge-0/0/0 description "voice priority and tcp and icmp traffic rate-limiting filter at ingress port" user@switch# set ge-0/0/0 unit 0 family ethernet-switching filter input ingress-port-voip-class-limit-tcp-icmp user@switch# set ge-0/0/1 description "voice priority and tcp and icmp traffic rate-limiting filter at ingress port" user@switch# set ge-0/0/1 unit 0 family ethernet-switching filter input ingress-port-voip-class-limit-tcp-icmp
-
異なるスケジューラに必要なパラメーターを設定します。
注:スケジューラのパラメーターを構成する場合、ネットワークトラフィックパターンと一致する数値を定義します。
[edit class-of-service]
user@switch# set schedulers voice-high buffer-size percent 15
user@switch# set schedulers voice-high priority  high
user@switch# set schedulers network—control buffer-size percent 10
user@switch# set schedulers network—control priority high
user@switch# set schedulers best-effort buffer-size percent 75
user@switch# set schedulers best-effort priority low
-
スケジューラマップを使用してスケジューラに転送クラスを割り当てます。
[edit class-of-service]
user@switch# set scheduler-maps ethernet-diffsrv-cos-map
user@switch# set scheduler-maps ethernet-diffsrv-cos-map forwarding-class expedited-forwarding scheduler voice-high
user@switch# set scheduler-maps ethernet-diffsrv-cos-map forwarding-class network-control scheduler net-control
user@switch# set scheduler-maps ethernet-diffsrv-cos-map forwarding-class best-effort scheduler best-effort
-
スケジューラマップを発信インターフェイスに関連付けます。
[edit class-of-service]
user@switch# set interfaces ge–0/1/0 scheduler-map ethernet-diffsrv-cos-map
結果
設定の結果の表示:
user@switch# show
    firewall {
        policer tcp-connection-policer {
            if-exceeding {
                bandwidth-limit 1m;
                burst-size-limit 30k;
            }
            then {
                discard;
            }
        }
        policer icmp-connection-policer {
            if-exceeding {
                bandwidth-limit 1m;
                burst-size-limit 30k;
            }
            then {
                discard;
            }
        }
        family ethernet-switching {
            filter ingress-port-voip-class-limit-tcp-icmp {
                 term voip-high {
                    from {
                        destination-mac-address 00.00.5E.00.53.01;
                            destination-mac-address 00.00.5E.00.53.02;
                        protocol udp;
                    }
                    then {
                        forwarding-class expedited-forwarding;
                        loss-priority low;
                    }
                }
                term network-control {
                    from {
                        precedence net-control ;
                    }
                    then {
                        forwarding-class network-control;
                        loss-priority low;
                    }
                }
                term tcp-connection {
                    from {
                        destination-address 192.0.2.16/28;
                        protocol tcp;
                    }
                    then {
                        policer tcp-connection-policer;
                            count tcp-counter;
                            forwarding-class best-effort;
                        loss-priority high;
                    }
                }
                term icmp-connection
                    from {
                        protocol icmp;
                    }
                    then {
                         policer icmp-connection-policer;
                            count icmp-counter;
                            forwarding-class best-effort;
                        loss-priority high;
                    }
                }
                term best-effort {
                    then {
                        forwarding-class best-effort;
                        loss-priority high;
                    }
                }
            }
        }
    }
    interfaces {
        ge-0/0/0 {
            description "voice priority and tcp and icmp traffic rate-limiting filter at ingress port";
            unit 0 {
                family ethernet-switching {
                    filter {
                        input ingress-port-voip-class-limit-tcp-icmp;
                    }
                }
            }
        }
        ge-0/0/1 {
            description "voice priority and tcp and icmp traffic rate-limiting filter at ingress port";
                unit 0 {
                family ethernet-switching {
                    filter {
                        input ingress-port-voip-class-limit-tcp-icmp;
                    }
                }
            }
        }
    }
    scheduler-maps {
        ethernet-diffsrv-cos-map {
            forwarding-class expedited-forwarding scheduler voice-high;
                forwarding-class network-control scheduler net-control;
            forwarding-class best-effort scheduler best-effort;
        }
    }
    interfaces {
        ge/0/1/0 {
            scheduler-map ethernet-diffsrv-cos-map;
        }
    }
VLANイングレスファイアウォールフィルターを設定して、不正デバイスによるVoIPトラフィックの妨害を防止する
ポート、VLAN、およびルーターインターフェイスにファイアウォールフィルターを設定して適用するには、以下のタスクを実行します。
手順
CLIクイックコンフィグレーション
voice-vlan上でVLANファイアウォールフィルターを素早く構成し、VoIPトラフィックを管理するゲートキーパーデバイスを模倣してHTTPセッションを使用する不正デバイスを阻止するには、以下のコマンドをコピーしてスイッチの端末ウィンドウに貼り付けます。
[edit]
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term to-gatekeeper from destination-address 192.0.2.14
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term to-gatekeeper from destination-port 80
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term to-gatekeeper then accept
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term from-gatekeeper from source-address 192.0.2.14
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term from-gatekeeper from source-port 80
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term from-gatekeeper then accept
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term not-gatekeeper from destination-port 80
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term not-gatekeeper then count rogue-counter
                         set firewall family ethernet-switching filter ingress-vlan-rogue-block term not-gatekeeper then discard
                         set vlans voice-vlan description "block rogue devices on voice-vlan"
                         set vlans voice-vlan filter input ingress-vlan-rogue-block
ステップバイステップの手順
voice-vlanでVLANファイアウォールフィルターを構成および適用して、VoIPトラフィックを管理するゲートキーパーデバイスを模倣してHTTPセッションを使用する不正デバイスを阻止するには:
-
ファイアウォールフィルター
ingress-vlan-rogue-blockを定義して、許可および制限するトラフィックのフィルター一致を指定します。[edit firewall] user@switch# set family ethernet-switching filter ingress-vlan-rogue-block
-
条件
to-gatekeeperを定義して、ゲートキーパーの宛先IPアドレスと一致するパケットを受け入れます。[edit firewall family ethernet-switching filter ingress-vlan-rogue-block] user@switch# set term to-gatekeeper from destination-address 192.0.2.14 user@switch# set term to-gatekeeper from destination-port 80 user@switch# set term to-gatekeeper then accept
-
条件
from-gatekeeperを定義して、ゲートキーパーの送信元IPアドレスと一致するパケットを受け入れます。[edit firewall family ethernet-switching filter ingress-vlan-rogue-block] user@switch# set term from-gatekeeper from source-address 192.0.2.14 user@switch# set term from-gatekeeper from source-port 80 user@switch# set term from-gatekeeper then accept
-
条件
not-gatekeeperを定義して、TCPポート上のすべてのvoice-vlanトラフィックがゲートキーパーデバイスに向けられるようにします。[edit firewall family ethernet-switching filter ingress-vlan-rogue-block] user@switch# set term not-gatekeeper from destination-port 80 user@switch# set term not-gatekeeper then count rogue-counter user@switch# set term not-gatekeeper then discard
-
VoIP電話のVLANインターフェイスに入力フィルターとしてファイアウォールフィルター
ingress-vlan-rogue-blockを適用します。[edit] user@switch# set vlans voice-vlan description "block rogue devices on voice-vlan" user@switch# set vlans voice-vlan filter input ingress-vlan-rogue-block
結果
設定の結果の表示:
user@switch# show
    firewall {
        family ethernet-switching {
            filter ingress-vlan-rogue-block {
                term to-gatekeeper {
                    from {
                        destination-address 192.0.2.14/32
                        destination-port 80;
                    }
                    then {
                        accept;
                    }
                }
                term from-gatekeeper {
                    from {
                        source-address 192.0.2.14/32
                        source-port 80;
                    }
                    then {
                        accept;
                    }
                }
                term not-gatekeeper {
                    from {
                        destination-port 80;
                    }
                    then {
                        count rogue-counter;
                        discard;
                    }
                }
        }
    vlans {
        voice-vlan {
            description "block rogue devices on voice-vlan";
            filter {
                 input ingress-vlan-rogue-block;
            }
        }
    }
従業員VLAN上のエグレストラフィックをカウント、監視、および分析するVLANファイアウォールフィルターを構成する
ポート、VLAN、およびルーターインターフェイスにファイアウォールフィルターを設定して適用するには、以下のタスクを実行します。
手順
CLIクイックコンフィグレーション
ファイアウォールフィルターは、 employee-vlan エグレストラフィックをフィルタリングするために、VLANインターフェイスに設定および適用されます。企業サブネット宛ての従業員トラフィックは許容されますが、監視はおこないません。ウェブを宛先とする従業員トラフィックは、カウントおよび分析されます。
VLANファイアウォールフィルターをすばやく設定して適用するには、以下のコマンドをコピーしてスイッチの端末ウィンドウに貼り付けます。
[edit]
                         set firewall family ethernet-switching filter egress-vlan-watch-employee term employee-to-corp from destination-address 192.0.2.16/28
                         set firewall family ethernet-switching filter egress-vlan-watch-employee term employee-to-corp then accept
                         set firewall family ethernet-switching filter egress-vlan-watch-employee term employee-to-web from destination-port 80
                         set firewall family ethernet-switching filter egress-vlan-watch-employee term employee-to-web then count employee-web-counter
                         set firewall family ethernet-switching filter egress-vlan-watch-employee term employee-to-web then analyzer employee-monitor
                         set vlans employee-vlan description "filter at egress VLAN to count and analyze employee to Web traffic"
                         set vlans employee-vlan filter output egress-vlan-watch-employee
ステップバイステップの手順
ウェブを宛先とする employee-vlan トラフィックをカウントして分析するには、エグレスポートファイアウォールフィルターを構成および適用します。
-
ファイアウォールフィルター
egress-vlan-watch-employeeを定義します。[edit firewall] user@switch# set family ethernet-switching filter egress-vlan-watch-employee
-
企業サブネットを宛先とするすべての
employee-vlanトラフィックを受け入れますが、監視はおこないemployee-to-corpという条件を定義します。[edit firewall family ethernet-switching filter egress-vlan-watch-employee] user@switch# set term employee-to-corp from destination-address 192.0.2.16/28 user@switch# set term employee-to-corp then accept
-
Webを宛先とするすべての
employee-vlanトラフィックをカウントおよび監視する条件employee-to-web定義します。[edit firewall family ethernet-switching filter egress-vlan-watch-employee] user@switch# set term employee-to-web from destination-port 80 user@switch# set term employee-to-web then count employee-web-counter user@switch# set term employee-to-web then analyzer employee-monitor
注:employee-monitorアナライザの設定については、例:EXシリーズ スイッチでの従業員リソース使用のローカル監視のためのポートミラーリングの設定を参照してください。 -
VoIP電話のポートインターフェイスへの出力フィルターとしてファイアウォールフィルター
egress-vlan-watch-employeeを適用します。[edit] user@switch# set vlans employee-vlan description "filter at egress VLAN to count and analyze employee to Web traffic" user@switch# set vlans employee-vlan filter output egress-vlan-watch-employee
結果
設定の結果の表示:
user@switch# show
    firewall {
        family ethernet-switching {
            filter egress-vlan-watch-employee {
                term employee-to-corp {
                    from {
                        destination-address 192.0.2.16/28
                    }
                    then {
                        accept;
                    }
                }
                term employee-to-web {
                    from {
                        destination-port 80;
                    }
                    then {
                        count employee-web-counter:
                        analyzer employee-monitor;
                    }
                }
            }
        }
    }
    vlans {
        employee-vlan {
            description "filter at egress VLAN to count and analyze employee to Web traffic";
            filter {
                 output egress-vlan-watch-employee;
            }
        }
    }
VLANファイアウォールフィルターを設定して、ゲストVLAN上でゲストから従業員へのトラフィックおよびピアツーピアアプリケーションを制限する
ポート、VLAN、およびルーターインターフェイスにファイアウォールフィルターを設定して適用するには、以下のタスクを実行します。
手順
CLIクイックコンフィグレーション
次の例では、最初のフィルター条件では、ゲストが他のゲストと話をすることは許可されますが、 employee-vlanの従業員と話をすることは許可されません。2つ目のフィルター条件では、ゲストがウェブにアクセスすることは許可しますが、 guest-vlan上のピアツーピアアプリケーションは使用できないようにします。
VLANファイアウォールフィルターを素早く構成して、ゲストから従業員へのトラフィックを制限し、ゲストが employee-vlan 上の従業員や従業員ホストと話したり、 guest-vlan上でピアツーピアアプリケーションの使用を試みたりすることをブロックするには、以下のコマンドをコピーして、スイッチの端末ウィンドウにペーストします:
[edit]
                         set firewall family ethernet-switching filter ingress-vlan-limit-guest term guest-to-guest from destination-address 192.0.2.33/28
                         set firewall family ethernet-switching filter ingress-vlan-limit-guest term guest-to-guest then accept
                         set firewall family ethernet-switching filter ingress-vlan-limit-guest term no-guest-employee-no-peer-to-peer from destination-mac-address 00.05.5E.00.00.DF
                         set firewall family ethernet-switching filter ingress-vlan-limit-guest term no-guest-employee-no-peer-to-peer then accept
                         set vlans guest-vlan description "restrict guest-to-employee traffic and peer-to-peer applications on guest VLAN"
                         set vlans guest-vlan forwarding-options filter input ingress-vlan-limit-guest
ステップバイステップの手順
VLANファイアウォールフィルターを構成および適用して、 guest-vlan上のゲストから従業員へのトラフィックおよびピアツーピアアプリケーションを制限するには:
-
ファイアウォールフィルター
ingress-vlan-limit-guestを定義します。[edit firewall] set firewall family ethernet-switching filter ingress-vlan-limit-guest -
guest-vlanのゲストが他のゲストと通信することは許可しますが、employee-vlanの従業員との通信は許可されないという条件guest-to-guest定義します。[edit firewall family ethernet-switching filter ingress-vlan-limit-guest] user@switch# set term guest-to-guest from destination-address 192.0.2.33/28 user@switch# set term guest-to-guest then accept
-
no-guest-employee-no-peer-to-peerという用語を定義することで、guest-vlanWeb 上のゲストはアクセスできますが、guest-vlan上のピアツーピアアプリケーションは使用できないようにします。注:destination-mac-addressはデフォルトのゲートウェイであり、VLAN内のあらゆるホストに対してネクストホップルーターとなります。[edit firewall family ethernet-switching filter ingress-vlan-limit-guest] user@switch# set term no-guest-employee-no-peer-to-peer from destination-mac-address 00.05.5E.00.00.DF user@switch# set term no-guest-employee-no-peer-to-peer then accept
-
ファイアウォールフィルター
ingress-vlan-limit-guestを、guest-vlanのインターフェイスへの入力フィルターとして適用します。[edit] user@switch# set vlans guest-vlan description "restrict guest-to-employee traffic and peer-to-peer applications on guest VLAN" user@switch# set vlans guest-vlan forwarding-options filter input ingress-vlan-limit-guest
結果
設定の結果の表示:
user@switch# show
    firewall {
        family ethernet-switching {
            filter ingress-vlan-limit-guest {
                term guest-to-guest {
                    from {
                        destination-address 192.0.2.33/28;
                    }
                    then {
                        accept;
                    }
                }
                term no-guest-employee-no-peer-to-peer {
                    from {
                        destination-mac-address 00.05.5E.00.00.DF;
                    }
                    then {
                        accept;
                    }
                }
            }
        }
    }
    vlans {
        guest-vlan {
            description "restrict guest-to-employee traffic and peer-to-peer applications on guest VLAN";
            filter {
                input ingress-vlan-limit-guest;
            }
        }
    }
企業サブネットを宛先とするエグレストラフィックに優先度を付与するルーターファイアウォールフィルターの設定
ポート、VLAN、およびルーターインターフェイスにファイアウォールフィルターを設定して適用するには、以下のタスクを実行します。
手順
CLIクイックコンフィグレーション
ルーティングポート(レイヤー3アップリンクモジュール)にファイアウォールフィルターを素早く構成して、 employee-vlan トラフィックをフィルタリングし、企業サブネット宛てのトラフィックに最高の転送クラス優先度を与えるには、以下のコマンドをコピーしてスイッチ端末ウィンドウにペーストします:
[edit]
                         set firewall family inet filter egress-router-corp-class term corp-expedite from destination-address 192.0.2.16/28
                         set firewall family inet filter egress-router-corp-class term corp-expedite then forwarding-class expedited-forwarding
                         set firewall family inet filter egress-router-corp-class term corp-expedite then loss-priority low
                         set firewall family inet filter egress-router-corp-class term not-to-corp then accept
                         set interfaces ge-0/1/0 description "filter at egress router to expedite destined for corporate network"
                         set ge-0/1/0 unit 0 family inet address 203.0.113.0
                         set interfaces ge-0/1/0 unit 0 family inet filter output egress-router-corp-class
ステップバイステップの手順
ルーティングポート(レイヤー3アップリンクモジュール)にファイアウォールフィルターを設定して適用し、企業サブネットを宛先とする employee-vlan トラフィックに最高の優先度を付与するには、次の手順に従います。
-
ファイアウォールフィルター
egress-router-corp-classを定義します。[edit] user@switch# set firewall family inet filter egress-router-corp-class
-
用語
corp-expediteを定義します。[edit firewall] user@switch# set family inet filter egress-router-corp-class term corp-expedite from destination-address 192.0.2.16/28 user@switch# set family inet filter egress-router-corp-class term corp-expedite then forwarding-class expedited-forwarding user@switch# set family inet filter egress-router-corp-class term corp-expedite then loss-priority low
-
用語
not-to-corpを定義します。[edit firewall] user@switch# set family inet filter egress-router-corp-class term not-to-corp then accept
-
ファイアウォールフィルター
egress-router-corp-classを、ルーターへのレイヤー3接続を提供するスイッチのアップリンクモジュール上のポートの出力フィルターとして適用します。[edit interfaces] user@switch# set ge-0/1/0 description "filter at egress router to expedite employee traffic destined for corporate network" user@switch# set ge-0/1/0 unit 0 family inet address 203.0.113.0 user@switch# set ge-0/1/0 unit 0 family inet filter output egress-router-corp-class
結果
設定の結果の表示:
user@switch# show
    firewall {
        family inet {
            filter egress-router-corp-class {
                term corp-expedite {
                    from {
                        destination-address 192.0.2.16/28;
                    }
                    then {
                        forwarding-class expedited-forwarding;
                        loss-priority low;
                    }
                }
                term not-to-corp {
                    then {
                        accept;
                    }
                }
            }
        }
    }
    interfaces {
        ge-0/1/0 {
            unit 0 {
                description "filter at egress router interface to expedite employee traffic destined for corporate network";
                family inet {
                    source-address 203.0.113.0
                    filter {
                        output egress-router-corp-class;
                    }
                }
            }
        }
    }
検証
ファイアウォールフィルターが正常に動作していることを確認するには、以下のタスクを実行します。
ファイアウォールフィルターとポリサーの動作を検証する
目的
スイッチに設定されたファイアウォールフィルターとポリサーの動作状態を確認します。
アクション
以下の動作モードコマンドを使用します。
user@switch>                              show firewall
Filter: ingress-port-voip-class-limit-tcp-icmp
Counters:
Name                                              Packets
icmp-counter                                            0
tcp-counter                                             0
Policers:
Name                                              Packets
icmp-connection-policer                                 0
tcp-connection-policer                                  0

Filter: ingress-vlan-rogue-block

Filter: egress-vlan-watch-employee
Counters:
Name                                              Packets
employee-web—counter                                    0
意味
show firewallコマンドは、スイッチ上で構成されたファイアウォールフィルター、ポリサー、およびカウンターの名前を表示します。出力フィールドには、設定されたすべてのカウンターのバイト数とパケット数、およびすべてのポリサーのパケット数が表示されます。
スケジューラーとスケジューラーマップの動作確認
目的
スイッチ上でスケジューラとスケジューラマップが動作していることを確認します。
アクション
以下の動作モードコマンドを使用します。
user@switch>                              show class-of-service scheduler-map

Scheduler map: default, Index: 2

  Scheduler: default-be, Forwarding class: best-effort, Index: 20
    Transmit rate: 95 percent, Rate Limit: none, Buffer size: 95 percent,
    Priority: low
    Drop profiles:
      Loss priority   Protocol    Index    Name
      Low             non-TCP         1    default-drop-profile
      Low             TCP             1    default-drop-profile
      High            non-TCP         1    default-drop-profile
      High            TCP             1    default-drop-profile

  Scheduler: default-nc, Forwarding class: network-control, Index: 22
    Transmit rate: 5 percent, Rate Limit: none, Buffer size: 5 percent,
    Priority: low
    Drop profiles:
      Loss priority   Protocol    Index    Name
      Low             non-TCP         1    default-drop-profile
      Low             TCP             1    default-drop-profile
      High            non-TCP         1    default-drop-profile
      High            TCP             1    default-drop-profileScheduler map: ethernet-diffsrv-cos-map, Index: 21657

  Scheduler: best-effort, Forwarding class: best-effort, Index: 61257
    Transmit rate: remainder, Rate Limit: none, Buffer size: 75 percent,
    Priority: low
    Drop profiles:
      Loss priority   Protocol    Index    Name
      Low             non-TCP         1    <default-drop-profile>
      Low             TCP             1    <default-drop-profile>
      High            non-TCP         1    <default-drop-profile>
      High            TCP             1    <default-drop-profile>

  Scheduler: voice-high, Forwarding class: expedited-forwarding, Index: 3123
    Transmit rate: remainder, Rate Limit: none, Buffer size: 15 percent,
    Priority: high
    Drop profiles:
      Loss priority   Protocol    Index    Name
      Low             non-TCP         1    <default-drop-profile>
      Low             TCP             1    <default-drop-profile>
      High            non-TCP         1    <default-drop-profile>
      High            TCP             1    <default-drop-profile>

  Scheduler: net-control, Forwarding class: network-control, Index: 2451
    Transmit rate: remainder, Rate Limit: none, Buffer size: 10 percent,
    Priority: high
    Drop profiles:
      Loss priority   Protocol    Index    Name
      Low             non-TCP         1    <default-drop-profile>
      Low             TCP             1    <default-drop-profile>
      High            non-TCP         1    <default-drop-profile>
      High            TCP             1    <default-drop-profile>
意味
設定されたスケジューラーとスケジューラーマップに関する統計を表示します。