
PTXルーターの選択的クラスベースフィルタリング
PTXルーターの選択的クラスベースフィルタリング
サポートされているPTXシリーズルーターとラインカードでは、送信元または宛先の分類(ソースクラス使用率、SCU)および(宛先クラス使用率、DCU)に基づいてIPv4およびIPv6トラフィックをフィルタリングできます。これは、クラス内のすべてのパケットではなく、クラス内のパケットのサブセットにフィルターを選択的に適用できることを意味するため便利です。さらに、パケット転送エンジン(PFE)を介するパケットフローが最適化され、フィルタリングがより効率的になります。
サービスプロバイダは、クラスベースのフィルタリングにより、次のような高度なサービスを提供できます。
-
送信元または宛先パケットクラスおよびその他のフィルター基準に基づいてパケットの転送クラスを調整することによる、ホップごとの動作操作。
-
特定の顧客インターフェイスへのトラフィックレート制限があり、大量のトラフィックをドロップする(DDoS攻撃を受けるなど)。通常、発信インターフェイスフィルターを導入してトラフィックのレートを制限します。しかし、分散システムではトラフィックがファブリックを通過し、限られたファブリック帯域幅を消費するため、これは非効率的である可能性があります。PTXのような仮想出力キューイングシステムでは、出力フィルターが実行される前にegressキューへの入場が行われ、出力フィルターへの後続のドロップアクションには補正が必要です。より多くのトラフィックをキューに受け入れる必要があり、より多くのファブリック帯域幅とより多くのegressオンチップバッファスペースが必要になります(これは限られたリソースです)。クラスベースのフィルターは、パケットがエグレスキューに受け入れられる前にイングレスパイプラインで実行されます。このメカニズムは、特定の宛先に向けて大量のトラフィックをドロップすることが予想される場合、通常の出力インターフェイスフィルターよりも推奨されます。
クラスベースのフィルタリングは、通常のトラフィックパターンを模倣してアプリケーションやサーバーのリソースをターゲットとする「低速」のDoS攻撃にも有効です。
クラスベースのフィルタリングをサポートするために、PTXルーターの転送テーブルに2つの新しいバインドポイント、 source-class と destination-classが導入されます。
CLI階層をここに示します。 src-class-name または dest-class-name は、対応するポリシーで定義したフィルターの名前です。
routing-options forwarding-table source-class src-class-name family [inet | inet6] filter <filter-name>
routing-options forwarding-table destination-class dest-class-name family [inet | inet6] filter
<filter-name>
また、複数のSCUおよびDCUクラスにまたがってインスタンス固有のフィルターを設定することもできます。デフォルトでは、フィルターに対してインスタンス化されるカウンターとポリサーのセットは 1 つだけです。インスタンス固有フィルターでは、フィルター接続ポイントごとに個別のカウンターとポリサーのセットが作成されます。
firewall family [inet | inet6] filter <filter name> instance-specific
PTXルーターのクラスベースフィルタリングについて
当初は、送信元クラス使用率(SCU)機能が導入され、送信元プレフィックスごとに特定のインターフェイスに送信されたトラフィックの統計内訳(送信元クラスによって識別されます)を提供しました。宛先クラス使用率(DCU)はもともと、宛先プレフィックスごとのインターフェイスで受信したトラフィックの統計的な内訳を提供するために導入されました(宛先クラスによって識別されます)。
送信元クラスまたは宛先クラスの両方が、送信元または宛先の検索プロセスでパケットに割り当てられます。そのため、ソースと宛先のフィルター一致条件は、ルックアップ後にフィルターが実行された場合にのみ評価できます。
ジュニパールーターは複数のフィルターバインドポイントをサポートしています。送信元と宛先の分類の結果を活用する可能性のあるものを以下に、使用ガイドラインとともに示します。
-
出力インターフェイスフィルター(set interfaces<インターフェイス名>ファミリーinetフィルター<出力>。すべてのPTXプラットフォームでサポートされますが、定常状態で大量のトラフィックを廃棄することが予想される場合(たとえば、DDoS攻撃緩和フィルターを実装する場合)は推奨されません。破棄されたDDoS攻撃トラフィックは、ファブリック帯域幅とエグレスオンチップバッファスペースが限られているため、DDoS攻撃基準に一致しない他のトラフィックによって補償されない場合があります。
-
転送テーブルフィルター検索後にフィルターします(set forwarding-options family inet filter <filter-name>出力)。Express 2(PE)およびExpress 3(ZX)プラットフォームでサポートされます。ただし、フィルターはegressパイプラインでインスタンス化されるため、破棄動作は通常の出力インターフェイスフィルターと似ています。
-
送信元または宛先クラス固有のバインドポイント(set routing-options forwarding-table source-class src-class-name family [inet | inet6] filter <filter- name>)。Express 2(PE)、Express 3(ZX)、Express 4(BT)プラットフォームでサポートされています。このフィルターは、ingressパイプラインでインスタンス化されます。これは、大量のトラフィックを破棄する場合に推奨されるオプションです。このオプションは、転送クラスをオーバーライドし、その後キュー割り当てを出力する必要がある場合にも推奨されます。仮想出力キューイング システムでは、キューはイングレス パイプラインで選択され、オーバーライドはイングレス パイプラインでも実行する必要があります。
-
これらのフィルターアクションは、ソースまたは宛先クラス固有のバインドポイントにバインドされたフィルターではサポートされていないことに注意してください。
-
ルーティングインスタンス
-
ネクストIP
-
ネクストインターフェイス
-
カプセル化解除
-
カプセル化する
-
-
ホストバウンドパケットには、選択クラスベースフィルターは適用できません。
-
uRPFルックアップに失敗したが、uRPFフェイルフィルターによって復元されたパケットは、SCU/DCUルックアップの対象になりません。したがって、そのようなパケットには選択クラスベースフィルターを適用できません。
-
フィルターは、SCU/DCU機能が有効になっているインターフェイスで受信するパケットにのみ適用されます。つまり、SCUが出力インターフェイスに設定されているかどうかに関係なく、フィルターが適用されます。
-
選択クラスベースのフィルターを適用する必要があるパケットは、パフォーマンスを低下させる可能性があります。パフォーマンスの低下は、受信トラフィックのレート、平均パケットサイズ、およびフィルターの対象となるトラフィックの量によって決まります。ただし、選択クラスベースフィルターが適用されていないパケットは、パフォーマンスに影響を与えません。
-
DCUアカウンティングは、フィルターによってドロップされたパケットに適用されます。
-
SCU出力アカウンティングは、フィルターによってドロップされたパケットには適用されません。
-
選択クラスベースのフィルターは、インターフェイス固有のノブはインターフェイス接続されたフィルターにのみ適用できるため、このノブと一緒に使用することはできません。
-
選択クラスベースのフィルターのリスト(入出力リスト)はサポートされていません。
-
論理システムはサポートされていません。
-
サポートされているペイロードプロトコルは、IPv4とIPv6のみです。MPLSはサポートされていません。
-
パケットがSCUとDCU選択クラスベースフィルターの両方に一致する場合、最後のフィルター(つまりDCUフィルター)のみがパケットに適用され、両方のフィルターは適用されません。
例:選択的クラスベースのフィルタリング(PTXルーター)
この例では、送信元または宛先の分類に基づいて、IPv4およびIPv6トラフィックフローにファイアウォールアクション(破棄、拒否、またはポリシング)を適用する方法を示します。これは、Junos Evolved OSリリース21を実行しているPTX10001-36MR、PTX10003-160C、PTX10003-80C、PTX10004、およびPTX10008ルーターに適用されます。 2、JUNOS Evolved OSリリース21.4を実行しているPTX10016ルーター、またはPTX3000、PTX-5000、PTX1000、PTX10002、PTX10008、PTX10016ルーター(Junos OSリリース21.2以降のソフトウェアを実行している)ルーター。
要件
この例では、カスタマーエッジ、プロバイダエッジ、プロバイダルーターで構成されるネットワークトポロジーにおいて、BGPを使用してデバイス間でルートを交換できるため、BGPを使用しています。詳細については、 BGP設定の概要 を参照してください。
概要
この例では、カスタマー エッジ(CE)デバイス、プロバイダ エッジ(PE)デバイス、プロバイダ コア(P)デバイスの 3 つのルーティング デバイスを使用します。IPv4トラフィックの設定は、SCUクラスとDCUクラスの2セットに加えて、ファイアウォールフィルターで構成されています。次の図では、/32 IPプレフィックスは、それぞれカスタマーエッジ(CE)ルーターとプロバイダ(P)ルーターに接続されたホストを表しています。
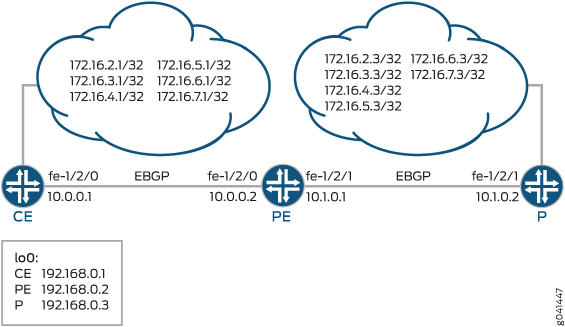
この例では、 scu-1 と scu-2 の 2 つのトラフィック クラスを定義します。最初のクラスはサブネット 172.16.2.0/24 内のプレフィックスに割り当てられ、2 つ目のクラスはサブネット 172.16.3.0/24 内のプレフィックスに割り当てられます。その他のプレフィックスにはクラス割り当てがありません。以下のCLIスニペットに示すように、ソースクラスscu-1およびソースクラスscu-2にプレフィックスを割り当てるルーティングポリシーがPEルーターで定義されています。
show policy-options
policy-statement scu-class {
    term gold {
        from {
            route-filter 172.16.2.0/24 orlonger;
              }
        then source-class scu-1;
        accept;
    term silver {
        from {
            route-filter 172.16.3.0/24 orlonger;
              }
        then source-class scu-2;
        accept;
        }
CEからPEのインターフェイスに入るトラフィックを考慮するために、PEルーターで定義された dcu-class と呼ばれるポリシーは、ルートフィルターを使用して トラフィックをdcu-1に配置し、他のプレフィックスにはクラス割り当てがありません。
show policy-options
policy-statement dcu-class {
    term gold {
        from {
            route-filter 172.16.5.0/24 orlonger;
            }
        then destination-class dcu-1;
        accept;
        }
次に、ポリシーが転送テーブルに適用されます。
forwarding-table {
    export [ dcu_class scu_class ];
}
次のステップでは、PE ルーターにフィルターを設定します。
show firewall {
    family inet {
        filter f1 {
            term t1 {
                from {
                    protocol icmp;
                    }
                then {
                    count c1;
                    }
                }
            }
        }
    }
そして、そのフィルターをPEルーター上の特定のソースクラスと宛先クラスのバインドポイントにアタッチします。
show routing-options forwarding-table
source-class scu-1 {
    family inet {
        filter {
            f1;
        }
    }
}
destination-class dcu-1 {
    family inet {
        filter {
            f1;
        }
    }
}
設定
手順
CLIクイックコンフィグレーション
この例をすばやく設定するには、以下のコマンドをコピーしてテキストファイルに貼り付け、改行を削除して、ネットワーク構成に合わせて必要な詳細を変更してから、コマンドをコピー&ペーストしてCLIに貼り付けます。
この例では、静的ルートを使用して、動作をテストするための接続とループバックインターフェイスアドレスを提供しています。
デバイスCE
set interfaces et-1/2/0 unit 0 family inet address 10.0.0.1/30
set interfaces lo0 unit 0 family inet address 192.168.0.1/32
set interfaces lo0 unit 0 family inet address 172.16.0.1/32
set protocols bgp group ext type external
set protocols bgp group ext export send-direct
set protocols bgp group ext export send-static
set protocols bgp group ext peer-as 200
set protocols bgp group ext neighbor 10.0.0.2
set policy-options policy-statement send-direct term 1 from protocol direct set policy-options policy-statement send-direct term 1 then accept
set policy-options policy-statement send-static term 1 from protocol static set policy-options policy-statement send-static term 1 then accept
set routing-options static route 10.1.0.0/30 next-hop 10.0.0.2 set routing-options autonomous-system 100
デバイスPE
set interfaces et-1/2/0 unit 0 family inet address 10.0.0.2/30
set interfaces et-1/2/1 unit 0 family inet accounting source-class-usage input
set interfaces et-1/2/1 unit 0 family inet accounting destination-class-usage
set interfaces et-1/2/1 unit 0 family inet address 10.1.0.1/30
set interfaces lo0 unit 0 family inet address 192.168.0.2/32
set protocols bgp group ext type external
set protocols bgp group ext export send-direct
set protocols bgp group ext neighbor 10.0.0.1 peer-as 100
set protocols bgp group ext neighbor 10.1.0.2 peer-as 300
set policy-options policy-statement dcu_class term gold from route-filter 172.16.5.0/24 orlonger
set policy-options policy-statement dcu_class term gold then destination-class dcu-1
set policy-options policy-statement scu_class term gold from route-filter 172.16.2.0/24 orlonger
set policy-options policy-statement scu_class term gold then source-class scu-1
set policy-options policy-statement scu_class term silver from route-filter 172.16.3.0/24 orlonger
set policy-options policy-statement scu_class term silver then source-class scu-1
set policy-options policy-statement send-direct term 1 from protocol direct
set policy-options policy-statement send-direct term 1 then accept
set firewall family inet filter f1 term 0 from protocol icmp
set firewall family inet filter f1 term 0 then count c1
set firewall family inet filter f1 term 0 then accept
set routing-options autonomous-system 200
set routing-options forwarding-table export dcu_class
set routing-options forwarding-table export scu_class
デバイスP
set interfaces et-1/2/1 unit 0 family inet address 10.1.0.2/30
set interfaces lo0 unit 0 family inet address 192.168.0.3/32
set interfaces lo0 unit 0 family inet address 172.16.0.3/32
set interfaces lo0 unit 0 family inet address 172.16.0.3/32
set interfaces lo0 unit 0 family inet address 172.16.0.3/32
set interfaces lo0 unit 0 family inet address 172.16.0.3/32
set interfaces lo0 unit 0 family inet address 172.16.0.3/32
set interfaces lo0 unit 0 family inet address 172.16.0.3/32
set protocols bgp group ext type external
set protocols bgp group ext export send-direct
set protocols bgp group ext export send-static
set protocols bgp group ext peer-as 200
set protocols bgp group ext neighbor 10.1.0.1
set policy-options policy-statement send-direct term 1 from protocol direct
set policy-options policy-statement send-direct term 1 then accept
set policy-options policy-statement send-static term 1 from protocol static
set policy-options policy-statement send-static term 1 then accept
set routing-options static route 10.0.0.0/30 next-hop 10.1.0.1
set routing-options static route 172.16.2.0/24 discard
set routing-options static route 172.16.3.0/24 discard
set routing-options static route 172.16.4.0/24 discard set routing-options static route 172.16.5.0/24 discard set routing-options static route 172.16.6.0/24 discard set routing-options static route 172.16.7.0/24 discard set routing-options autonomous-system 300
ステップバイステップの手順
送信元プレフィックスと宛先プレフィックスを転送クラスでグループ化するには:
-
PEルーター上にルーターインターフェイスを作成します。
[edit interfaces]
set et-1/2/0 unit 0 family inet accounting source-class-usage output
set et-1/2/0 unit 0 family inet address 10.0.0.2/30
set et-1/2/1 unit 0 family inet accounting source-class-usage input
set et-1/2/1 unit 0 family inet accounting destination-class-usage
set et-1/2/1 unit 0 family inet address 10.1.0.1/30
set lo0 unit 0 family inet address 192.168.0.2/32
-
PE ルーターに BGP を設定します。
[edit]
set protocols bgp group ext type external
set protocols bgp group ext export send-direct
set protocols bgp group ext neighbor 10.0.0.1 peer-as 100
set protocols bgp group ext neighbor 10.1.0.2 peer-as 300
-
PEルーターの自律システム(AS)番号を設定します。
[edit]
set routing-options autonomous-system 200
-
PE ルーターで DCU ポリシーを設定します。
[edit]
set policy-options policy-statement dcu_class term class-1 from route-filter 172.16.5.0/24 orlonger
set policy-options policy-statement dcu_class term class-1 then destination-class dcu-1
-
PE ルーターで SCU ポリシーを設定します。
[edit]
set policy-options policy-statement scu_class term class-1 from route-filter 172.16.2.0/24 orlonger
set policy-options policy-statement scu_class term class-1 then source-class scu-1
-
ポリシーをPEルーターの転送テーブルに適用します。
[edit]
set routing-options forwarding-table export dcu_class
set routing-options forwarding-table export scu_class
-
PE ルーターにフィルターを作成します。
[edit]
set firewall family inet filter f1 from protocol icmp then count c1
-
フィルターをPEルーター上のソースクラスと宛先クラスのバインドポイントにバインドします。
フィルターを宛先クラスの使用状況にバインドします。
[edit]
set routing-options forwarding-table destination-class dcu-1 family inet filter f1
ソースクラスの使用状況にフィルターをバインドします。
[edit]
set routing-options forwarding-table source-class scu-1 family inet filter f1
-
(オプション)PE ルーターで直接ルートをアドバタイズするルーティングポリシーを設定します。
[edit]
set policy-options policy-statement send-direct term 1 from protocol direct
set policy-options policy-statement send-direct term 1 then accept
結果
設定モードから、PE ルーターで show interfaces、 show protocols、 show policy-options、 show routing-options コマンドを発行して、設定を確認します。出力に意図した設定が表示されない場合は、この例の手順を繰り返して設定を修正します。
show interfaces
et-1/2/0 {
    unit 0 {
        family inet {
            address 10.0.0.2/30;
            }
        }
     }
et-1/2/1 {
    unit 0 {
        family inet {
            accounting {
                source-class-usage { input;
                    }
            }
            address 10.1.0.1/30;
            }
        }
     }
lo0 {
    unit 0 {
        family inet {
            address 192.168.0.2/32;
                }
            }
        }
show interface statistics et-1/2/0
Physical interface: et-1/2/0:0, Enabled, Physical link is Up
    Interface index: 1087, SNMP ifIndex: 622
    Link-level type: Ethernet, MTU: 1514, LAN-PHY mode, Speed: 10Gbps, BPDU Error: None, Loop Detect PDU Error: None, MAC-REWRITE Error: None, Loopback: Disabled,
    Source filtering: Disabled, Flow control: Enabled, Media type: Fiber Device flags	: Present Running
    Interface flags: SNMP-Traps
    CoS queues	: 8 supported, 8 maximum usable queues
    Current address: e4:5d:37:4e:e8:40, Hardware address: e4:5d:37:4e:e8:40 Last flapped	: 2021-03-16 09:33:43 PDT (03:39:51 ago)
    Statistics last cleared: 2021-03-16 13:13:01 PDT (00:00:33 ago) Input rate	: 0 bps (0 pps)
    Output rate	: 0 bps (0 pps) Input errors: 0, Output errors: 0 Active alarms : None
    Active defects : None
    PCS statistics	Seconds
        Bit errors	0
        Errored blocks	0
    PRBS Mode : Disabled
    Interface transmit statistics: Disabled Link Degrade :
        Link Monitoring	:  Disable

    Logical interface et-1/2/0:0.0 (Index 1047) (SNMP ifIndex 673)
        Flags: Up SNMP-Traps
        Encapsulation: ENET2
        Input packets : 14
        Output packets: 6
        Protocol inet, MTU: 1500
        Flags: Sendbcast-pkt-to-re, SCU-out
                            Packets     Bytes
       Source class (packet-per-second) (bits-per-second)
                scu-1  6   504
                   (   0)(    0)
    Addresses, Flags: Is-Preferred Is-Primary
        Destination: 44.4.4/24, Local: 44.4.4.4, Broadcast: 44.4.4.255
    Protocol inet6, MTU: 1500
        Flags: None, SCU-out
                    Packets  Bytes
        Source class (packet-per-second) (bits-per-second)
            scu-1    0    0
            (        0) ( 0)
        Addresses, Flags: Is-Preferred Is-Primary
            Destination: 4001::/64, Local: 4001::4001
        Addresses, Flags: Is-Preferred
            Destination: fe80::/64, Local: fe80::e65d:37ff:fe4e:e840
        Protocol multiservice, MTU: Unlimited
            Flags: None
show firewall
Filter: f1
Counters:
Name        Bytes        Packets
c1            0            0
Filter: v4_instance_new-scu-scu-1
Counters:
Name                            Bytes        Packets
c_v4_instance_new-scu-scu-1       504            6
Filter: v6_instance_new-scu-scu-1
Counters:
Name                            Bytes        Packets
c_v6_instance_new-scu-scu-1        0            0
show policy-options
policy-statement dcu_class {
    term class-1 {
        from {
            route-filter 172.16.5.0/24 orlonger;
            }
        then destination-class dcu-1;
            }
        }
policy-statement scu_class {
    term class-1 {
        from {
            route-filter 172.16.2.0/24 orlonger;
            }
        then source-class scu-1;
        }
       }
policy-statement send-direct {
    term 1 {
        from protocol direct;
        then accept;
    }
}
show routing-options
autonomous-system 200;
forwarding-table {
    export [ dcu_class scu_class ];
}
デバイスの設定が完了したら、設定モードからコミットを入力します。