
BNG-Redundanz für DHCP-Anwender mit paketgestützter Wiederherstellung
Erfahren Sie mehr über Breitband-Netzwerk-Gateway (BNG)-Redundanz mit paketgesteuerter basierter Wiederherstellung, die einfache, benutzerfreundliche und leichtgewichtige zustandslose Anwender Redundanz bietet.
BNG-Redundanz für DHCP-Abonnenten mit paketgestützter Wiederherstellung Übersicht
Die BNG-Redundanz für DHCP-Anwender mit paketgetriggerter Wiederherstellung bietet eine einfache, benutzerfreundliche und leichtgewichtige zustandslose Redundanz mit minimalem Datenverkehrsverlust. Die zustandslose BNG-Redundanz für DHCP-Anwender unterstützt dynamisches C-VLAN und statisches VLAN-Modell sowohl für Relay als auch für Server. Die paketgesteuerte Wiederherstellung nutzt die vorhandenen Funktionen wie die automatische Konfiguration von VLAN- und paketgesteuerten Abonnenten.
- Automatische Konfiguration des VLAN
- Paketgesteuerte Abonnenten
- Vorteile der BNG-Redundanz für DHCP-Anwender mit paketgestützter Wiederherstellung
Automatische Konfiguration des VLAN
Die automatische Konfigurationsfunktion erstellt beim Empfang des ersten VLAN-Pakets vom Client eine dynamische logische VLAN (DVLAN)-Schnittstelle. Beim Empfang des ersten Pakets authentifiziert die Routing-Engine den Anwender beim Authentifizierungsserver. Der Authentifizierungsserver benötigt möglicherweise die Details zur Buchhaltung und zu erweiterten Diensten für die Authentifizierung des Anwenders. Die Routing-Engine erstellt die logische DVLAN-Schnittstelle basierend auf der Anforderung des Authentifizierungsservers. Nach dem Erstellen der logischen DVLAN-Schnittstelle leitet das System das Paket zur weiteren Verarbeitung an den Protokollstapel weiter.
Paketgesteuerte Abonnenten
Die paketgesteuerte Funktion für Anwender erstellt beim Empfang eines Pakets von Clients mit der vorab zugewiesenen IPv4- oder IPv6-Adresse eine logische IP-Demux-Schnittstelle. Die Weiterleitungsebene validiert die Quell-IP-Adresse und stimmt mit der konfigurierten IP-Adresse oder den Präfixbereichen überein. Nach der Validierung der Quell-IP-Adresse leitet die Weiterleitungsebene das Paket an die Routing-Engine weiter. Die Routing-Engine authentifiziert den Anwender beim Authentifizierungsserver gemäß dem Volumen der Buchhaltung und erweiterten Services wie Firewall-Filter und CoS. Die Routing-Engine erstellt eine logische IP-Demux-Schnittstelle gemäß den vom Authentifizierungsserver angeforderten Diensten.
Vorteile der BNG-Redundanz für DHCP-Anwender mit paketgestützter Wiederherstellung
- Bietet eine einfache BNG-Bereitstellung für Backups.
Funktionsweise der BNG-Redundanz für DHCP-Abonnenten mit paketgestützter Wiederherstellung
Das primäre BNG hostet die Abonnenten während des normalen Datenverkehrsflusses. Wenn der Datenverkehrsfluss in der primären BNG ausfällt, leiten die Zugriffsknoten den Datenverkehr an die Backup-BNG um. Das primäre BNG kann aus folgenden Gründen ausfallen:
- Ausfall eines Zwischenknotens oder Verbindungsausfalls, der den MPLS-Pfad zwischen Zugriffsknoten und primärem BNG unterbricht.
- Primärer BNG-Verbindungs- oder Portausfall.
- Primärer BNG-Linecard-Fehler.
- Fehler der primären BNG-Routing-Engine.
- Primärer BNG-Chassis-Fehler.
- Ausfall der primären BNG-zu-Core-Netzwerkverbindung.
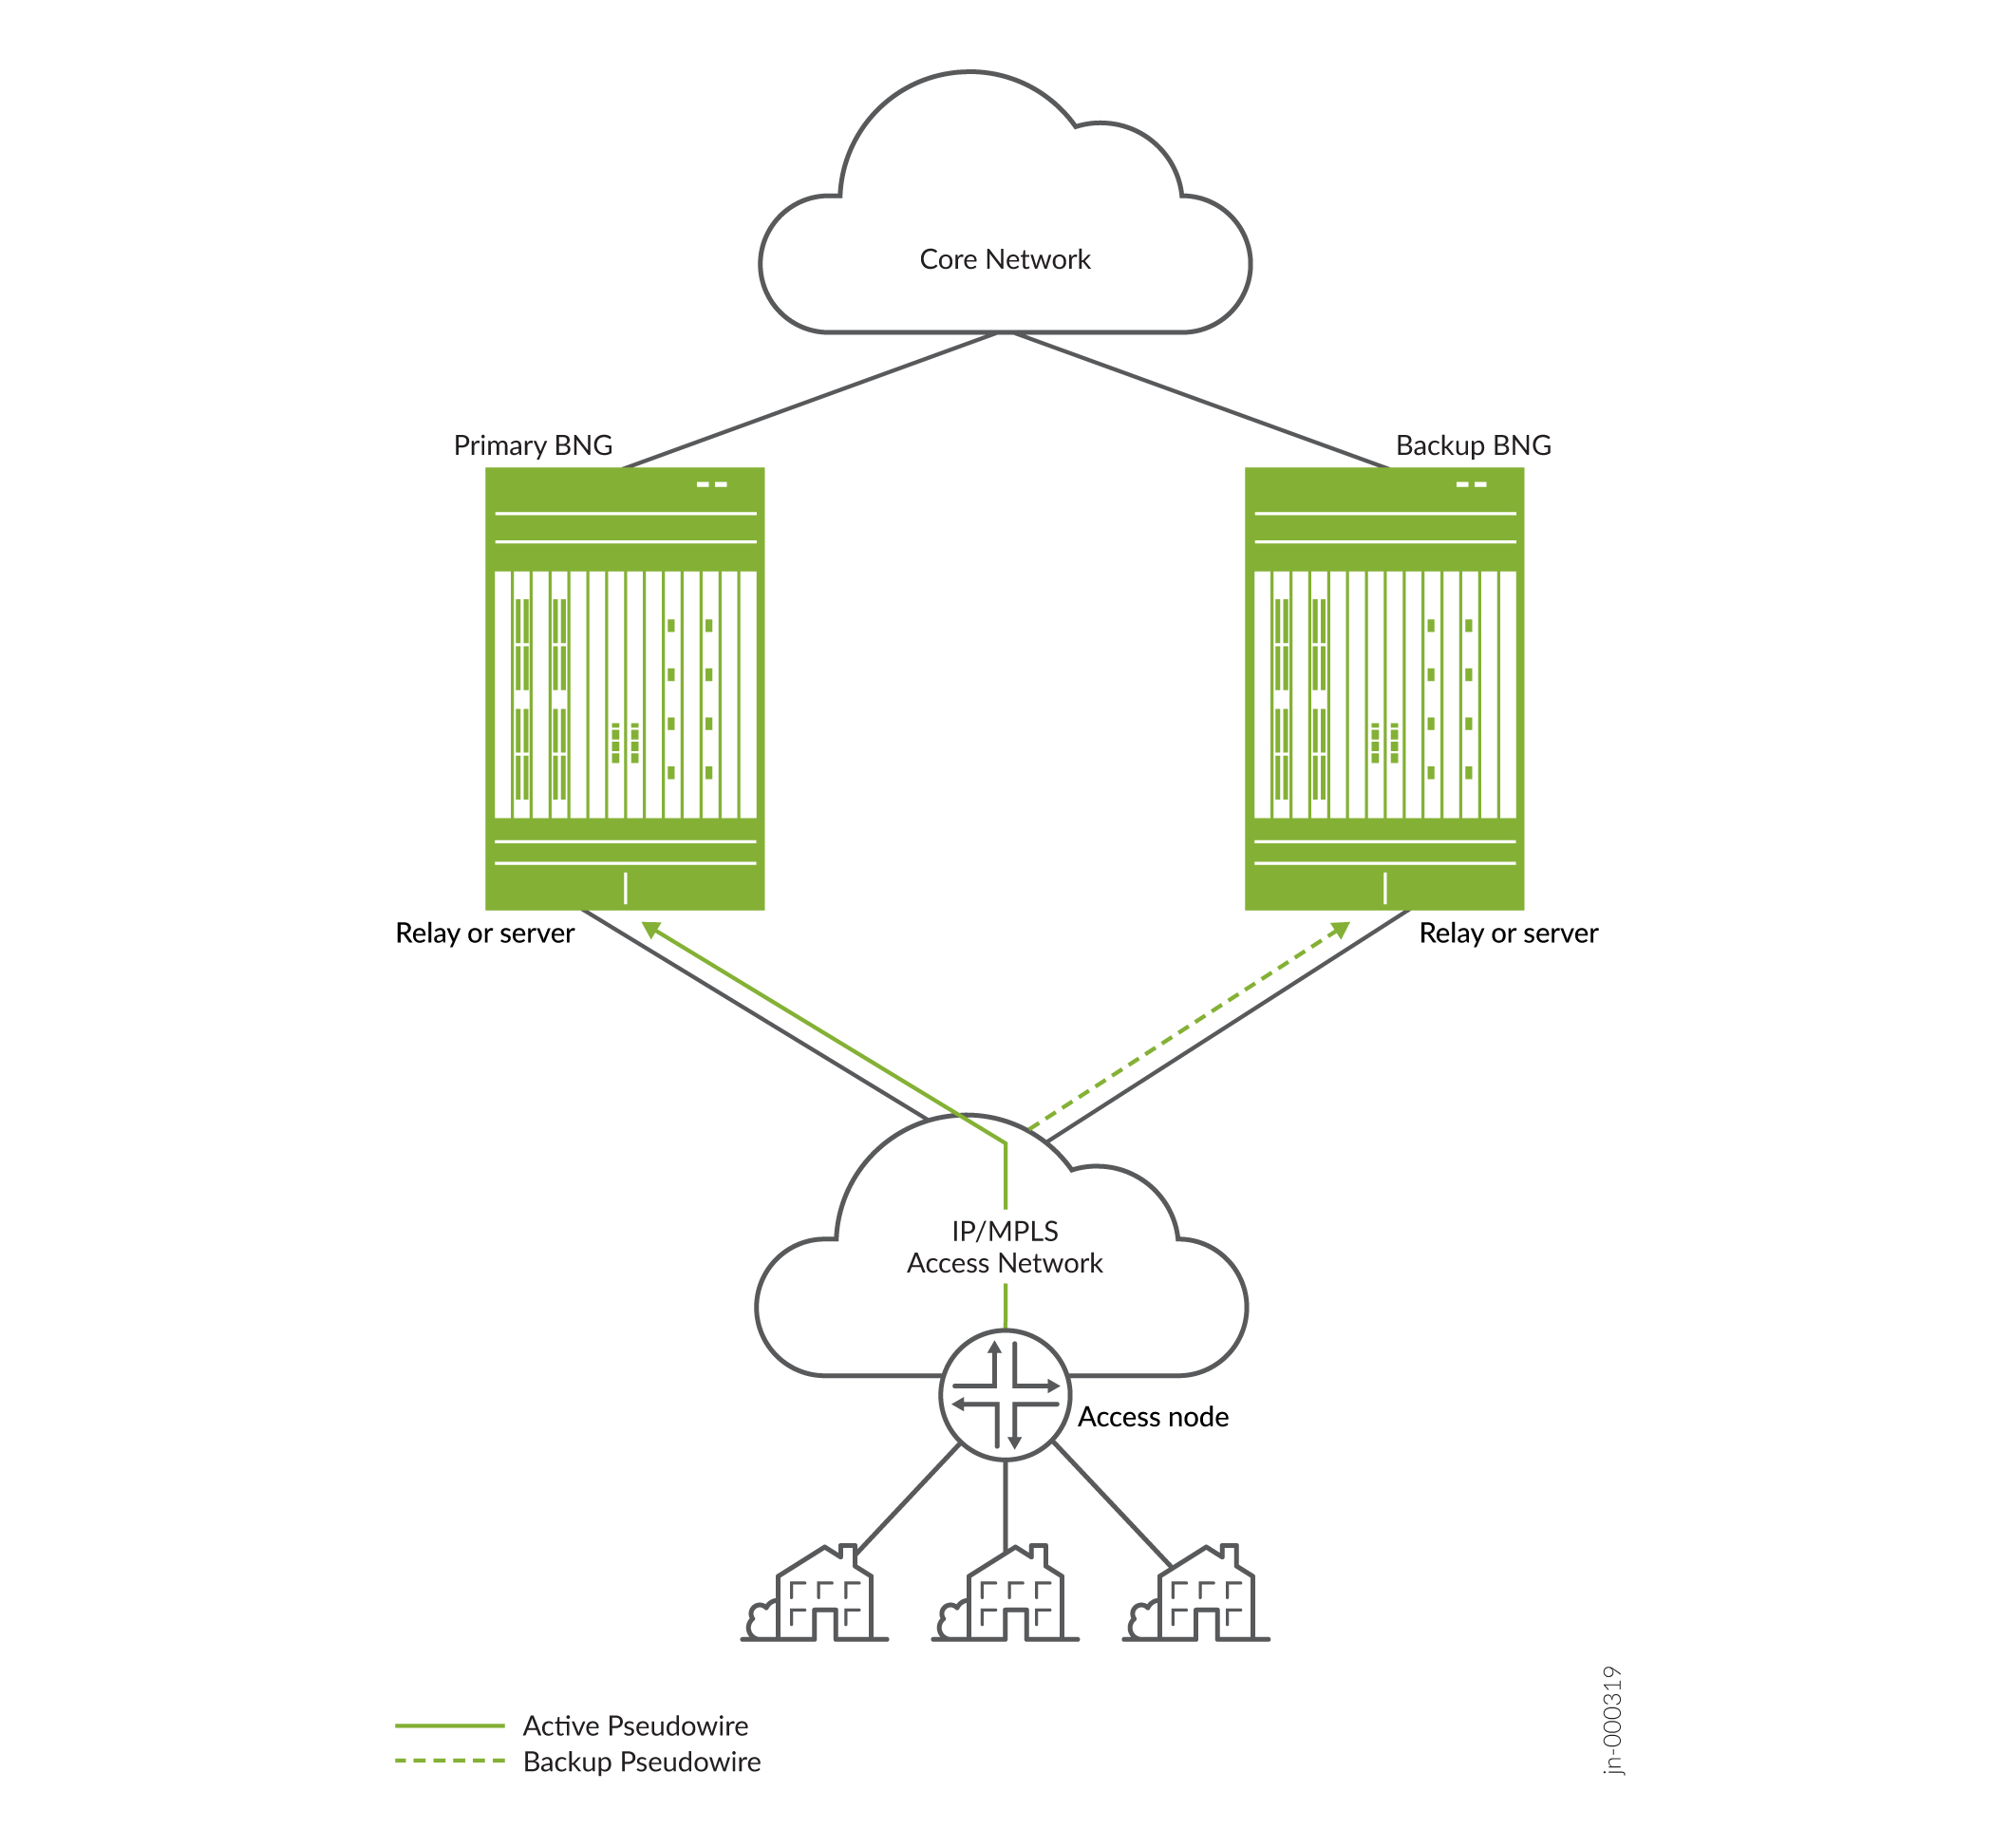
Abbildung 1 zeigt das Topologiediagramm für eine Layer 2-Verbindung basierend auf einem IP/MPLS-Pseudowire Headend Termination (PWHT)-Szenario.
Basierend auf dem ersten Datenverkehr nach dem Failover erstellt die Routing-Engine DVLAN und dynamischen IP-Anwender. Die Packet Forwarding Engine leitet den nachfolgenden Datenverkehr in der Weiterleitungsebene gemäß der QoS und den an den IP-Anwender angeschlossenen Services an den Core-Router weiter. Diese QoS und die Services sind nicht die gleichen QoS und Services des Anwenders, die in der primären BNG erstellt wurden. Dies sind die üblichen standardmäßigen dynamischen IP-Anwenderprofilfunktionen, die vom RADIUS-Server oder der lokalen Konfiguration zugewiesen werden, bis die Sitzungslease-Erneuerung und -Authentifizierung erfolgt.
Sobald das System den DHCP-Anwender in der sekundären BNG erstellt hat, stellt es begrenzte QoS und andere Services bei bestmöglichem Datenverkehr mit minimaler Unterbrechung bereit. Wenn der DHCP-Client-Lease-Timer abläuft, wird versucht, die Lease-Zeit neu auszuhandeln, und es findet ein neuer DHCP-Protokollaustausch statt. Diesmal erstellt das System den voll funktionsfähigen DHCP-Anwender zusammen mit QoS und erweiterten Services wie die des primären BNG. Die Packet Forwarding Engine leitet den Datenverkehr entsprechend auch an den Core-Router weiter. Das System löscht den dynamischen IP-Anwender, wenn der voll funktionsfähige DHCP-Anwender aktiv ist.
Die Umschaltung des Datenverkehrs auf das Backup-BNG und das Zurücksetzen auf den primären BNG-Prozess ist ähnlich. Wenn die Wiederherstellung nach dem ersten Lease-Timeout erfolgt, fährt das System mit dem Switchover-Prozess fort. Wenn die Wiederherstellung vor dem ersten Lease-Timeout erfolgt, fährt das System mit der Wiederherstellung fort, da es noch über die zuvor zugewiesene IP-Adresse und DHCP-Bindungen verfügt.
Die BNG-Redundanz mit paketgetriggerter Wiederherstellungsfunktion unterstützt die folgende Zugriffsnetzwerktopologie für BNG-Redundanz:
- Layer 2 VPN-Szenario
- Layer 2-Schaltung basierend auf IP/MPLS PWHT-Szenario
- Ethernet-VPN – virtueller privater drahtloser Service (EVPN-VPWS)
Konfigurieren der BNG-Redundanz mithilfe der paketgesteuerten Wiederherstellung für DHCP-Anwender
Überblick
Ab Version 22.4R1 unterstützt Junos die Konfiguration der BNG-Redundanz (Broadband Network Gateway) mit paketauslöserbasierter Wiederherstellung, die eine benutzerfreundliche und leichtgewichtige zustandslose Redundanz für Anwender ermöglicht.
Dieser Abschnitt enthält ein Konfigurationsbeispiel für paketgetriggerte BNG-Redundanz für DHCP-Abonnenten unter Verwendung eines lokalen DHCP-Servers.
Anforderungen
Im Konfigurationsbeispiel werden die folgenden Geräte verwendet:
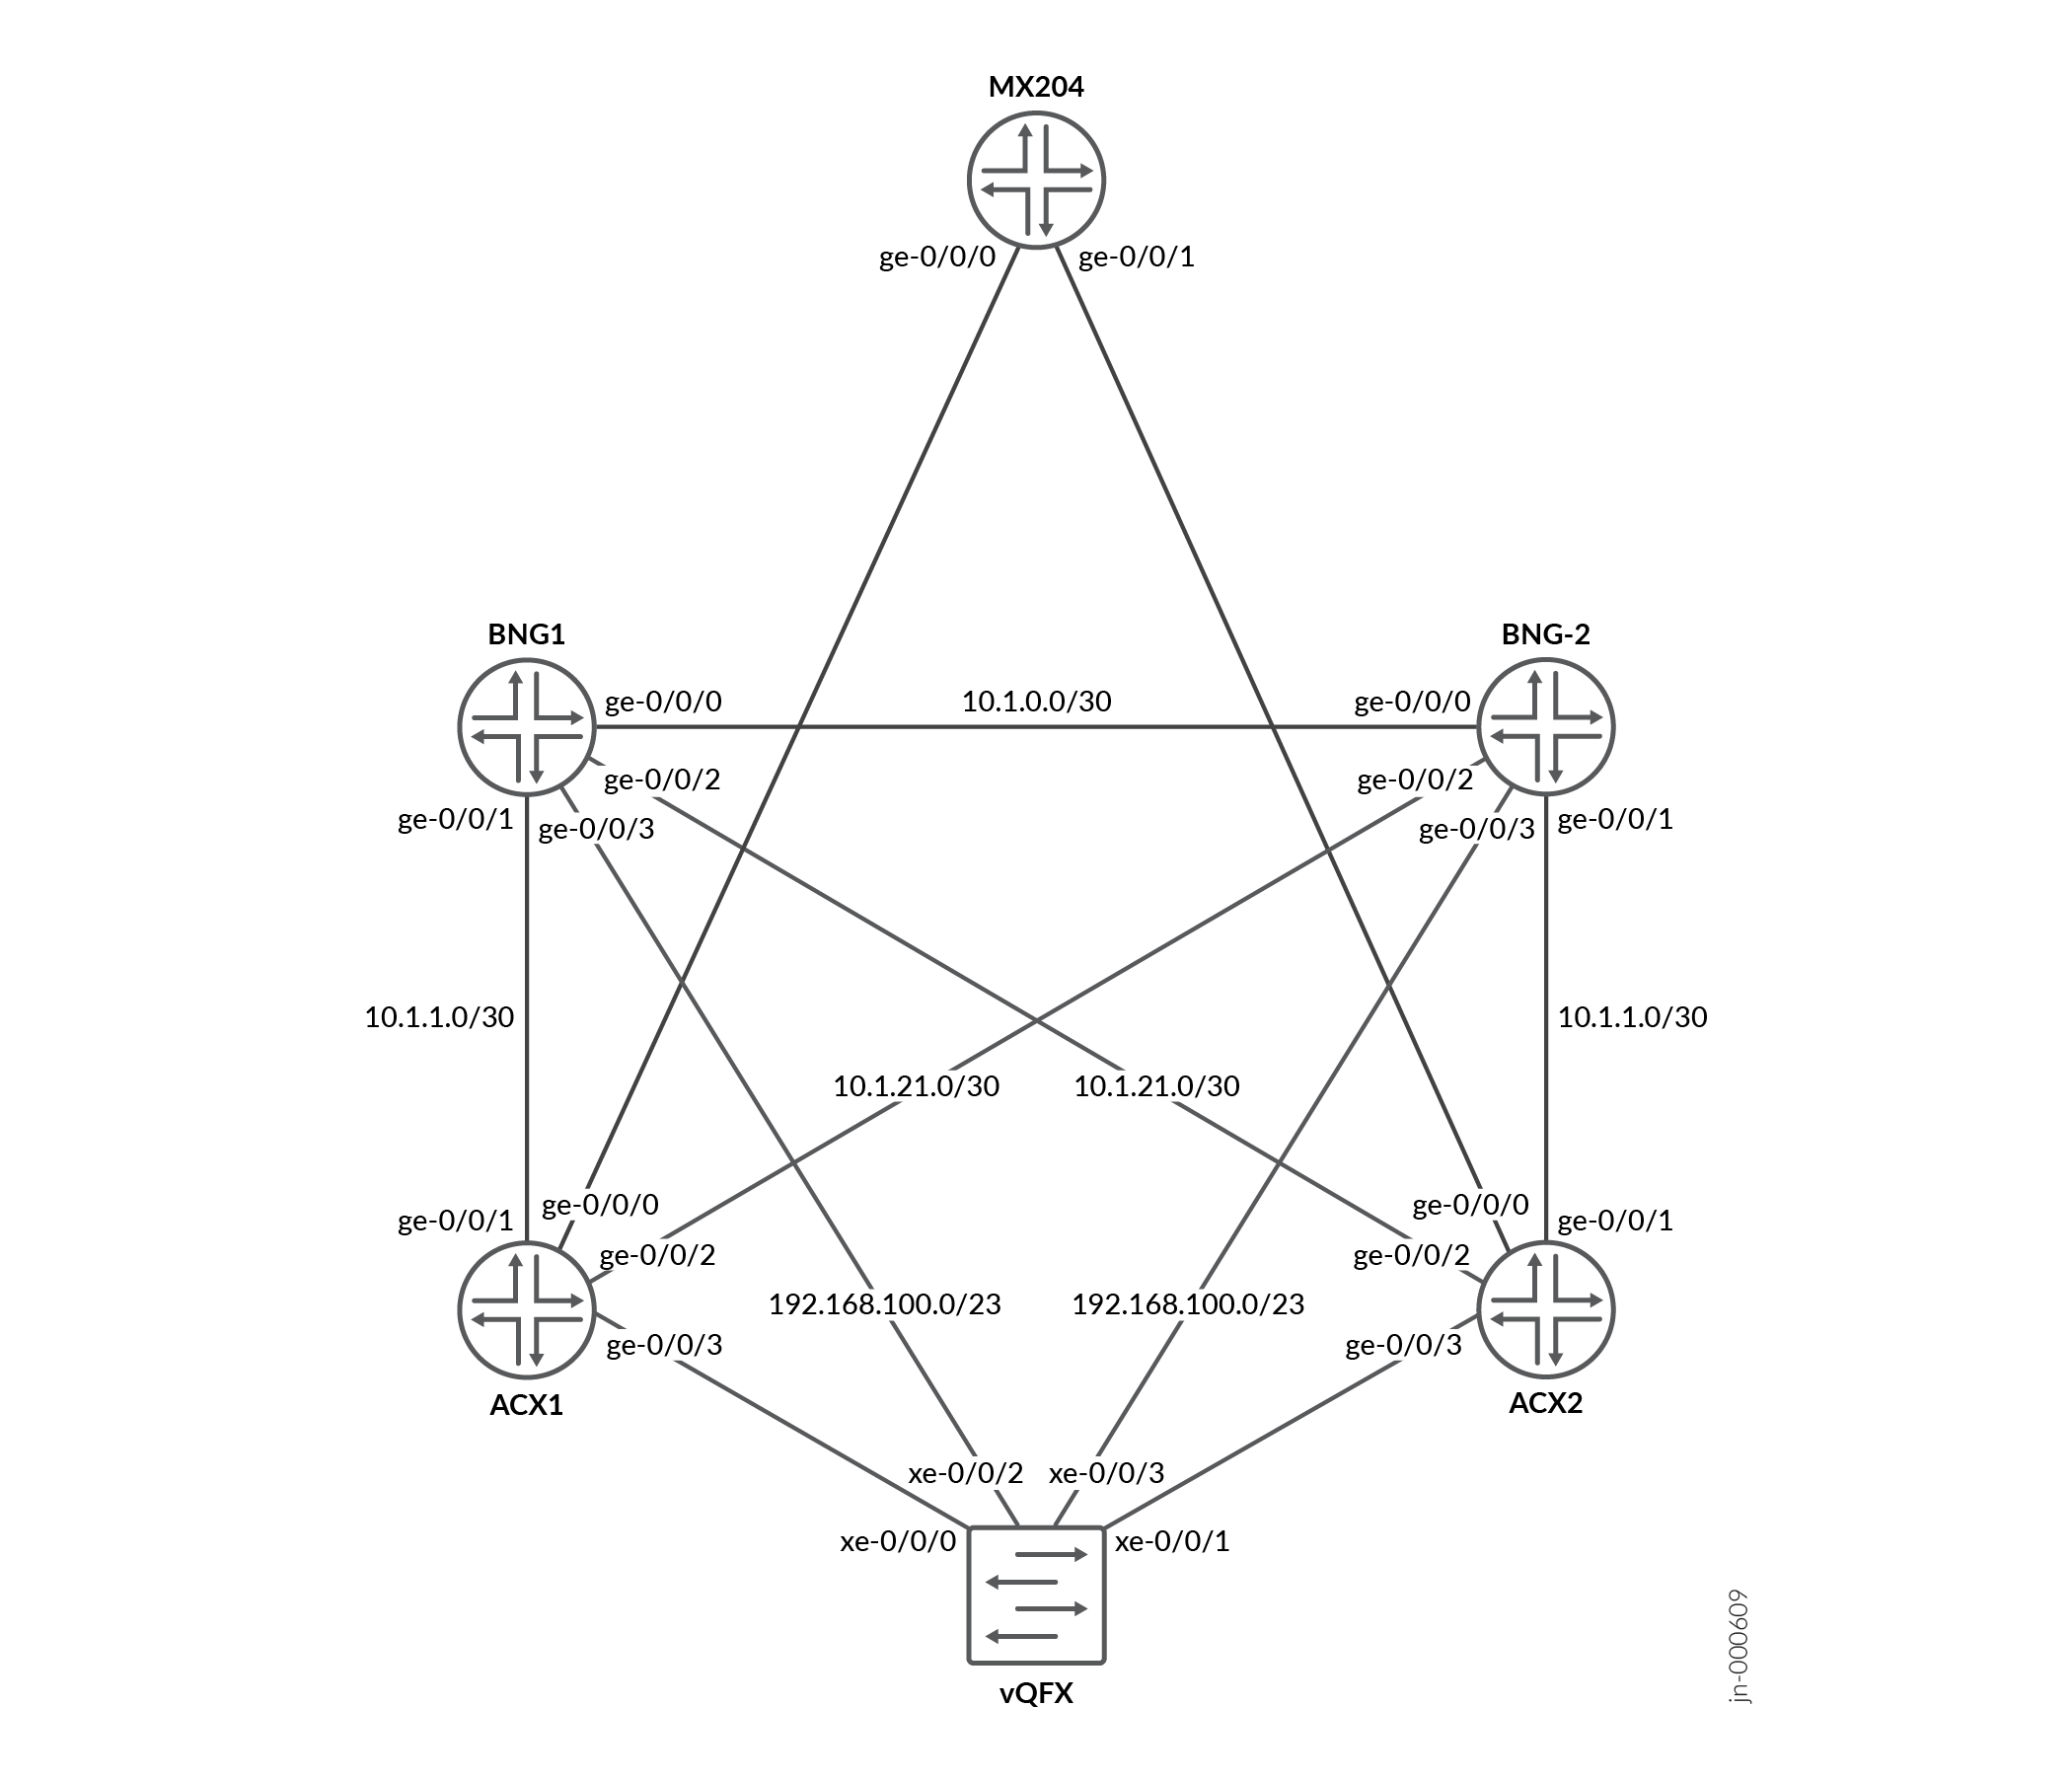
- BNG1- und BNG2-Breitbandnetzwerk-Gateways führen EVPN-VPWS-Pseudowire Headend Termination (PWHT) mit den ACX-Aggregationsknoten aus und beenden die IPoE-Sitzungen. Die BNG implementiert die paketgesteuerte Redundanz für die IPoE-Sitzungen.
- ACX1- und ACX2-Geräte aggregieren den Datenverkehr der Access Nodes über die Cloud Metro Fabric zu den BNGs.
- Das MX204-Gerät wird für simulierte Peripheriekonnektivität verwendet.
- vQFX-Instanz für Q-in-Q-Tunneling und VLAN-Übersetzung.
Topologie
Abbildung 2 zeigt die physische Topologie mit zwei vMX-Geräten, die als BNG1- und BNG2-Server konfiguriert sind, zwei Zugriffsgeräten ACX1 und ACX2, einem vQFX- und einem MX204-Gerät.
Konfiguration
- CLI-Schnellkonfiguration
- Gerät BNG1
- Gerät BNG2
- Gerät ACX1
- Gerät ACX2
- Schritt-für-Schritt-Anleitung
- BNG1 konfigurieren
- BNG2 konfigurieren
- Konfiguration von ACX1
- Konfiguration von ACX2
CLI-Schnellkonfiguration
Gerät BNG1
Um dieses Beispiel schnell zu konfigurieren, kopieren Sie die folgenden Befehle, fügen Sie sie in eine Textdatei ein, entfernen Sie alle Zeilenumbrüche, ändern Sie alle erforderlichen Details, um sie an Ihre Netzwerkkonfiguration anzupassen, und kopieren Sie dann die Befehle und fügen Sie sie dann in die CLI auf der Hierarchieebene [edit] ein.
set system host-name BNG1
set system configuration-database max-db-size 698343424
set system services ssh root-login allow
set chassis network-services enhanced-ip
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED ********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
set interfaces ge-0/0/0 apply-groups GR-CORE-INTF
set interfaces ge-0/0/0 unit 0 family inet address 10.1.0.1/30
set interfaces ge-0/0/0 unit 0 family iso
set interfaces ge-0/0/0 unit 0 family mpls
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.1.1/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.21.2/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
set interfaces ge-0/0/3 mtu 9192
set interfaces ge-0/0/3 unit 0 family inet address 192.168.100.171/23
set interfaces lo0 unit 0 family inet address 172.31.100.3/32
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 primary
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 preferred
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0003.00
set interfaces lo0 unit 0 family mpls
set protocols isis interface ge-0/0/0.0
set protocols isis interface ge-0/0/1.0
set protocols isis interface ge-0/0/2.0
set protocols isis interface lo0.0 passive
set protocols isis level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
set routing-options router-id 172.31.100.3
set routing-options autonomous-system 65000
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.3
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP cluster 1.1.1.1
set protocols bgp group IBGP neighbor 172.31.100.4
set protocols bgp group IBGP neighbor 172.31.100.11
set protocols bgp group IBGP neighbor 172.31.100.12
set protocols ldp deaggregate
set protocols ldp transport-address 172.31.100.3
set protocols ldp interface all
set protocols mpls interface all
set system services subscriber-management traceoptions file submgmt.log
set system services subscriber-management traceoptions file size 30m
set system services subscriber-management traceoptions file files 10
set system services subscriber-management traceoptions flag all
set system services subscriber-management gres-route-flush-delay
set system services subscriber-management enable
set system processes general-authentication-service traceoptions file authd
set system processes general-authentication-service traceoptions file size 10m
set system processes general-authentication-service traceoptions file files 10
set system processes general-authentication-service traceoptions flag all
set system processes smg-service traceoptions file smgd
set system processes smg-service traceoptions file size 10m
set system processes smg-service traceoptions file files 10
set system processes smg-service traceoptions level all
set system processes smg-service traceoptions flag all
set system processes dhcp-service traceoptions file jdhcpd
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions file files 10
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
set system processes dhcp-service traceoptions flag all
set chassis fpc 0 pic 0 tunnel-services bandwidth 1g
set chassis fpc 0 performance-mode
set access-profile no-auth
set access profile no-auth authentication-order none
set access address-protection
set chassis pseudowire-service device-count 10
set interfaces ps0 anchor-point lt-0/0/10
set interfaces ps0 flexible-vlan-tagging
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include delimiter "@"
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include user-prefix vlan
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include interface-name
set interfaces ps0 auto-configure stacked-vlan-ranges access-profile no-auth
set interfaces ps0 auto-configure remove-when-no-subscribers
set interfaces ps0 mtu 2022
set interfaces ps0 esi 00:10:00:00:01:00:00:00:10:00
set interfaces ps0 esi single-active
set interfaces ps0 esi df-election-type preference value 1000
set interfaces ps0 unit 0 encapsulation ethernet-ccc
set interfaces lo0 unit 20 description "VRF:internet Loopback"
set interfaces lo0 unit 20 family inet address 172.16.100.3/32 primary
set routing-instances internet instance-type vrf
set routing-instances internet routing-options auto-export
set routing-instances internet interface lo0.20
set routing-instances internet route-distinguisher 172.31.100.3:12
set routing-instances internet vrf-import internet-vrf-import-pol
set routing-instances internet vrf-export internet-vrf-export-pol
set routing-instances internet vrf-table-label
set policy-options policy-statement internet-vrf-export-pol term all then community add 65000:999
set policy-options policy-statement internet-vrf-export-pol term all then accept
set policy-options policy-statement internet-vrf-import-pol term default from community 65000:999
set policy-options policy-statement internet-vrf-import-pol term default then accept
set policy-options policy-statement internet-vrf-import-pol term subs from community 65000:1131
set policy-options policy-statement internet-vrf-import-pol term subs then accept
set policy-options policy-statement internet-vrf-import-pol term other from community 65000:113
set policy-options policy-statement internet-vrf-import-pol term other then accept
set policy-options community 65000:113 members target:65000:113
set policy-options community 65000:1131 members target:65000:1131
set policy-options community 65000:999 members target:65000:999
set interfaces lo0 unit 313 description "VRF:dhcp-subs Loopback"
set interfaces lo0 unit 313 family inet address 172.16.16.3/32
set interfaces lo0 unit 313 family inet address 10.42.0.1/32 primary
set interfaces lo0 unit 313 family inet6 address 2015:cafe:2000::1/128
set routing-instances dhcp-subs instance-type vrf
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 next-table internet.inet6.0
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 no-readvertise
set routing-instances dhcp-subs routing-options router-id 172.16.16.3
set routing-instances dhcp-subs routing-options flow term-order standard
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 next-table internet.inet.0
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 no-readvertise
set routing-instances dhcp-subs routing-options static route 10.42.0.0/16 discard
set routing-instances dhcp-subs routing-options static route 10.42.0.0/16 tag 200
set routing-instances dhcp-subs routing-options auto-export
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection failure-action clear-binding-if-interface-up
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd version automatic
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd minimum-interval 30000
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd multiplier 3
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides client-discover-match incoming-interface
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides dual-stack dhcp-ds
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface demux0.0
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface ps0.0
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds authentication username-include mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds on-demand-address-allocation
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds classification-key mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds protocol-master inet
set routing-instances dhcp-subs system services dhcp-local-server no-stale-timer-refresh
set routing-instances dhcp-subs system services dhcp-local-server stale-timer 60
set routing-instances dhcp-subs access address-assignment high-utilization 80
set routing-instances dhcp-subs access address-assignment abated-utilization 70
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet network 10.42.0.0/16
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 low 10.42.0.2
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 high 10.42.255.254
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes maximum-lease-time 600
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes server-identifier 10.42.0.1
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes router 10.42.0.1
set routing-instances dhcp-subs access-profile no-auth
set routing-instances dhcp-subs interface lo0.313
set routing-instances dhcp-subs route-distinguisher 172.31.100.3:13
set routing-instances dhcp-subs vrf-import dhcp-subs-vrf-import-pol
set routing-instances dhcp-subs vrf-export dhcp-subs-vrf-export-pol
set routing-instances dhcp-subs vrf-table-label
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from protocol direct
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from route-filter 172.16.16.3/32 exact
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from protocol static
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from tag 200
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then community add 65000:1131
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then accept
set policy-options policy-statement dhcp-subs-vrf-import-pol term all from community 65000:111
set policy-options policy-statement dhcp-subs-vrf-import-pol term all then accept
set policy-options community 65000:111 members target:65000:111
set policy-options community 65000:111 members target:65000:11
set access domain map none access-profile no-auth
set access domain map none target-routing-instance dhcp-subs
set access domain map ps0.* access-profile no-auth
set access domain map ps0.* target-routing-instance dhcp-subs
set access domain map ps0:* access-profile no-auth
set access domain map ps0:* target-routing-instance dhcp-subs
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-address 255.255.255.255/32
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-port dhcp
set firewall family inet filter rpf-pass-dhcp term allow-dhcp then accept
set firewall family inet filter rpf-pass-dhcp term default then discard
set system dynamic-profile-options versioning
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" actual-transit-statistics
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" demux-options underlying-interface "$junos-underlying-interface"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet rpf-check fail-filter rpf-pass-dhcp
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet demux-source $junos-subscriber-ip-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 demux-source $junos-subscriber-ipv6-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 unnumbered-address lo0.313
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds dynamic-profile prod-dhcp-base
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix next-hop "$junos-framed-route-nexthop"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles auto-pwht interfaces interface-set "$junos-phy-ifd-interface-set-name" interface "$junos-interface-ifd-name" unit "$junos-interface-unit"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp restricted
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-id "$junos-vlan-id"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate loose
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags outer "$junos-stacked-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags inner "$junos-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" demux-options underlying-interface "$junos-interface-ifd-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate strict
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.42.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.43.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include delimiter "@"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include user-prefix vlan
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include interface-name
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges session-timeout 600
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet mac-validate strict
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet6 unnumbered-address lo0.313
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht accept any
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht ranges any,any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht accept any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht ranges any
set routing-instances EVPN-VPWS-BNG-1 instance-type evpn-vpws
set routing-instances EVPN-VPWS-BNG-1 protocols evpn interface ps0.0 vpws-service-id local 9999
set routing-instances EVPN-VPWS-BNG-1 protocols evpn interface ps0.0 vpws-service-id remote 1111
set routing-instances EVPN-VPWS-BNG-1 interface ps0.0
set routing-instances EVPN-VPWS-BNG-1 route-distinguisher 172.31.100.3:11
set routing-instances EVPN-VPWS-BNG-1 vrf-target target:65000:11
Gerät BNG2
set system host-name BNG2
set system configuration-database max-db-size 698343424
set system services ssh root-login allow
set chassis network-services enhanced-ip
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED-ADD-DESCRIPTION********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
set interfaces ge-0/0/0 apply-groups GR-CORE-INTF
set interfaces ge-0/0/0 unit 0 family inet address 10.1.0.2/30
set interfaces ge-0/0/0 unit 0 family iso
set interfaces ge-0/0/0 unit 0 family mpls
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.2.2/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.12.2/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
set interfaces ge-0/0/3 mtu 9192
set interfaces ge-0/0/3 unit 0 family inet address 192.168.100.171/23
set interfaces lo0 unit 0 family inet address 172.31.100.4/32
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 primary
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 preferred
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0004.00
set interfaces lo0 unit 0 family mpls
set protocols isis interface ge-0/0/0.0
set protocols isis interface ge-0/0/1.0
set protocols isis interface ge-0/0/2.0
set protocols isis interface lo0.0 passive
set protocols isis level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
set routing-options router-id 172.31.100.4
set routing-options autonomous-system 65000
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.4
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP cluster 2.2.2.2
set protocols bgp group IBGP neighbor 172.31.100.3
set protocols bgp group IBGP neighbor 172.31.100.11
set protocols bgp group IBGP neighbor 172.31.100.12
set protocols ldp deaggregate
set protocols ldp transport-address 172.31.100.4
set protocols ldp interface all
set protocols mpls interface all
set system services subscriber-management traceoptions file submgmt.log
set system services subscriber-management traceoptions file size 30m
set system services subscriber-management traceoptions file files 10
set system services subscriber-management traceoptions flag all
set system services subscriber-management gres-route-flush-delay
set system services subscriber-management enable
set system processes general-authentication-service traceoptions file authd
set system processes general-authentication-service traceoptions file size 10m
set system processes general-authentication-service traceoptions file files 10
set system processes general-authentication-service traceoptions flag all
set system processes smg-service traceoptions file smgd
set system processes smg-service traceoptions file size 10m
set system processes smg-service traceoptions file files 10
set system processes smg-service traceoptions level all
set system processes smg-service traceoptions flag all
set system processes dhcp-service traceoptions file jdhcpd
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions file files 10
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
set system processes dhcp-service traceoptions flag all
set chassis fpc 0 pic 0 tunnel-services bandwidth 1g
set chassis fpc 0 performance-mode
set access-profile no-auth
set access profile no-auth authentication-order none
set access address-protection
set chassis pseudowire-service device-count 10
set interfaces ps0 anchor-point lt-0/0/10
set interfaces ps0 flexible-vlan-tagging
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include delimiter "@"
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include user-prefix vlan
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include interface-name
set interfaces ps0 auto-configure stacked-vlan-ranges access-profile no-auth
set interfaces ps0 auto-configure remove-when-no-subscribers
set interfaces ps0 mtu 2022
set interfaces ps0 esi 00:10:00:00:01:00:00:00:10:00
set interfaces ps0 esi single-active
set interfaces ps0 esi df-election-type preference value 999
set interfaces ps0 unit 0 encapsulation ethernet-ccc
set interfaces lo0 unit 20 description "VRF:internet Loopback"
set interfaces lo0 unit 20 family inet address 172.16.100.4/32 primary
set routing-instances internet instance-type vrf
set routing-instances internet routing-options auto-export
set routing-instances internet interface lo0.20
set routing-instances internet route-distinguisher 172.31.100.4:12
set routing-instances internet vrf-import internet-vrf-import-pol
set routing-instances internet vrf-export internet-vrf-export-pol
set routing-instances internet vrf-table-label
set policy-options policy-statement internet-vrf-export-pol term all then community add 65000:999
set policy-options policy-statement internet-vrf-export-pol term all then accept
set policy-options policy-statement internet-vrf-import-pol term default from community 65000:999
set policy-options policy-statement internet-vrf-import-pol term default then accept
set policy-options policy-statement internet-vrf-import-pol term subs from community 65000:1131
set policy-options policy-statement internet-vrf-import-pol term subs then accept
set policy-options policy-statement internet-vrf-import-pol term other from community 65000:113
set policy-options policy-statement internet-vrf-import-pol term other then accept
set policy-options community 65000:113 members target:65000:113
set policy-options community 65000:1131 members target:65000:1131
set policy-options community 65000:999 members target:65000:999
set interfaces lo0 unit 313 description "VRF:dhcp-subs Loopback"
set interfaces lo0 unit 313 family inet address 172.16.16.4/32
set interfaces lo0 unit 313 family inet address 10.43.0.1/32 primary
set interfaces lo0 unit 313 family inet6 address   2016:cafe:2000::1/128
set routing-instances dhcp-subs instance-type vrf
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 next-table internet.inet6.0
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 no-readvertise
set routing-instances dhcp-subs routing-options router-id 172.16.16.4
set routing-instances dhcp-subs routing-options flow term-order standard
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 next-table internet.inet.0
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 no-readvertise
set routing-instances dhcp-subs routing-options static route 10.43.0.0/16 discard
set routing-instances dhcp-subs routing-options static route 10.43.0.0/16 tag 200
set routing-instances dhcp-subs routing-options auto-export
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection failure-action clear-binding-if-interface-up
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd version automatic
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd minimum-interval 30000
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd multiplier 3
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides client-discover-match incoming-interface
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides dual-stack dhcp-ds
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface demux0.0
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface ps0.0
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds authentication username-include mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds on-demand-address-allocation
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds classification-key mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds protocol-master inet
set routing-instances dhcp-subs system services dhcp-local-server no-stale-timer-refresh
set routing-instances dhcp-subs system services dhcp-local-server stale-timer 60
set routing-instances dhcp-subs access address-assignment high-utilization 80
set routing-instances dhcp-subs access address-assignment abated-utilization 70
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet network 10.43.0.0/16
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 low 10.43.0.2
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 high 10.43.254.254
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes maximum-lease-time 600
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes server-identifier 10.43.0.1
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes router 10.43.0.1
set routing-instances dhcp-subs access-profile no-auth
set routing-instances dhcp-subs interface lo0.313
set routing-instances dhcp-subs route-distinguisher 172.31.100.4:13
set routing-instances dhcp-subs vrf-import dhcp-subs-vrf-import-pol
set routing-instances dhcp-subs vrf-export dhcp-subs-vrf-export-pol
set routing-instances dhcp-subs vrf-table-label
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from protocol direct
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from route-filter 172.16.16.4/32 exact
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from protocol static
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from tag 200
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then community add 65000:1131
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then accept
set policy-options policy-statement dhcp-subs-vrf-import-pol term all from community 65000:111
set policy-options policy-statement dhcp-subs-vrf-import-pol term all then accept
set policy-options community 65000:111 members target:65000:111
set policy-options community 65000:111 members target:65000:11
set policy-options community 65000:113 members target:65000:113
set policy-options community 65000:1131 members target:65000:1131
set access-profile no-auth
set access profile no-auth authentication-order none
set access address-protection
set access domain map none access-profile no-auth
set access domain map none target-routing-instance dhcp-subs
set access domain map ps0.* access-profile no-auth
set access domain map ps0.* target-routing-instance dhcp-subs
set access domain map ps0:* access-profile no-auth
set access domain map ps0:* target-routing-instance dhcp-subs
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-address 255.255.255.255/32
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-port dhcp
set firewall family inet filter rpf-pass-dhcp term allow-dhcp then accept
set firewall family inet filter rpf-pass-dhcp term default then discard
set system dynamic-profile-options versioning
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" actual-transit-statistics
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" demux-options underlying-interface "$junos-underlying-interface"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet rpf-check fail-filter rpf-pass-dhcp
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet demux-source $junos-subscriber-ip-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 demux-source $junos-subscriber-ipv6-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 unnumbered-address lo0.313
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds dynamic-profile prod-dhcp-base
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix next-hop "$junos-framed-route-nexthop"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles auto-pwht interfaces interface-set "$junos-phy-ifd-interface-set-name" interface "$junos-interface-ifd-name" unit "$junos-interface-unit"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp restricted
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-id "$junos-vlan-id"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate loose
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags outer "$junos-stacked-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags inner "$junos-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" demux-options underlying-interface "$junos-interface-ifd-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate strict
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.42.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.43.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include delimiter "@"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include user-prefix vlan
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include interface-name
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges session-timeout 600
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet mac-validate strict
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet6 unnumbered-address lo0.313
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht accept any
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht ranges any,any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht accept any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht ranges any
set routing-instances EVPN-VPWS-BNG-2 instance-type evpn-vpws
set routing-instances EVPN-VPWS-BNG-2 protocols evpn interface ps0.0 vpws-service-id local 9999
set routing-instances EVPN-VPWS-BNG-2 protocols evpn interface ps0.0 vpws-service-id remote 1111
set routing-instances EVPN-VPWS-BNG-2 interface ps0.0
set routing-instances EVPN-VPWS-BNG-2 route-distinguisher 172.31.100.4:11
set routing-instances EVPN-VPWS-BNG-2 vrf-target target:65000:11
Gerät ACX1
set system host-name ACX1
set system services ssh root-login allow
set chassis network-services enhanced-ip
set system processes dhcp-service traceoptions file dhcp_logfile
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED-ADD-DESCRIPTION********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.1.2/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.12.1/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
set chassis aggregated-devices ethernet device-count 10
set interfaces ge-0/0/3 gigether-options 802.3ad ae10
set interfaces ae10 flexible-vlan-tagging
set interfaces ae10 encapsulation flexible-ethernet-services
set interfaces ae10 esi 00:11:11:11:11:11:11:11:11:11
set interfaces ae10 esi all-active
set interfaces ae10 aggregated-ether-options lacp active
set interfaces ae10 aggregated-ether-options lacp system-id 00:00:00:00:00:10
set interfaces ae10 unit 0 encapsulation vlan-ccc
set interfaces ae10 unit 0 vlan-id-list 301-500
set interfaces ae10 unit 0 input-vlan-map push
set interfaces ae10 unit 0 input-vlan-map vlan-id 100
set interfaces ae10 unit 0 output-vlan-map pop
set interfaces lo0 unit 0 family inet address 172.31.100.11/32
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0011.00
set interfaces lo0 unit 0 family mpls
set protocols isis interface all level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
set routing-options router-id 172.31.100.11
set routing-options autonomous-system 65000
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.11
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP neighbor 172.31.100.3
set protocols bgp group IBGP neighbor 172.31.100.4
set protocols ldp interface all
set protocols mpls interface all
set routing-instances EVPN-VPWS instance-type evpn-vpws
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id local 1111
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id remote 9999
set routing-instances EVPN-VPWS interface ae10.0
set routing-instances EVPN-VPWS route-distinguisher 172.31.100.11:11
set routing-instances EVPN-VPWS vrf-target target:65000:11
Gerät ACX2
set system host-name ACX2
set system services ssh root-login allow
set chassis network-services enhanced-ip
set system processes dhcp-service traceoptions file dhcp_logfile
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED-ADD-DESCRIPTION********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.2.1/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.21.1/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
set interfaces ge-0/0/3 gigether-options 802.3ad ae10
set interfaces ae10 flexible-vlan-tagging
set interfaces ae10 encapsulation flexible-ethernet-services
set interfaces ae10 esi 00:11:11:11:11:11:11:11:11:11
set interfaces ae10 esi all-active
set interfaces ae10 aggregated-ether-options lacp active
set interfaces ae10 aggregated-ether-options lacp system-id 00:00:00:00:00:10
set interfaces ae10 unit 0 encapsulation vlan-ccc
set interfaces ae10 unit 0 vlan-id-list 301-500
set interfaces ae10 unit 0 input-vlan-map push
set interfaces ae10 unit 0 input-vlan-map vlan-id 100
set interfaces ae10 unit 0 output-vlan-map pop
set interfaces lo0 unit 0 family inet address 172.31.100.12/32
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0012.00
set interfaces lo0 unit 0 family mpls
set protocols isis interface all level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
set routing-options router-id 172.31.100.12
set routing-options autonomous-system 65000
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.12
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP neighbor 172.31.100.3
set protocols bgp group IBGP neighbor 172.31.100.4
set protocols ldp interface all
set protocols mpls interface all
set routing-instances EVPN-VPWS instance-type evpn-vpws
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id local 1111
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id remote 9999
set routing-instances EVPN-VPWS interface ae10.0
set routing-instances EVPN-VPWS route-distinguisher 172.31.100.12:11
set routing-instances EVPN-VPWS vrf-target target:65000:11
Schritt-für-Schritt-Anleitung
BNG1 konfigurieren
-
Melden Sie sich beim BNG1-Gerät an. Stellen Sie sicher, dass auf dem Gerät Junos Version 22.4R1 oder höher ausgeführt wird.
-
Konfigurieren Sie die Systemeinstellungen.
set system host-name BNG1
set system configuration-database max-db-size 698343424
set system services ssh root-login allow
set chassis network-services enhanced-ip
-
Erstellen Sie eine Gruppe, um die Konfiguration allgemeiner Kernschnittstellen wie MTU, Haltezeit und Dämpfungsparameter zu definieren.
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED ********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
-
Konfigurieren Sie die Schnittstellen zu Core-Geräten.
set interfaces ge-0/0/0 apply-groups GR-CORE-INTF
set interfaces ge-0/0/0 unit 0 family inet address 10.1.0.1/30
set interfaces ge-0/0/0 unit 0 family iso
set interfaces ge-0/0/0 unit 0 family mpls
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.1.1/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.21.2/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
-
Konfigurieren Sie die Schnittstelle zur vQFX.
set interfaces ge-0/0/3 mtu 9192
set interfaces ge-0/0/3 unit 0 family inet address 192.168.100.171/23
-
Konfigurieren Sie die Loopback-Schnittstelle.
set interfaces lo0 unit 0 family inet address 172.31.100.3/32
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 primary
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 preferred
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0003.00
set interfaces lo0 unit 0 family mpls
-
Konfigurieren Sie das IS-IS-Protokoll im Core-Netzwerk.
set protocols isis interface ge-0/0/0.0
set protocols isis interface ge-0/0/1.0
set protocols isis interface ge-0/0/2.0
set protocols isis interface lo0.0 passive
set protocols isis level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
-
Konfigurieren Sie Routing-Optionen.
set routing-options router-id 172.31.100.3
set routing-options autonomous-system 65000
-
Konfigurieren des BGP-Protokolls zwischen dem BNG und den Zugriffsgeräten
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.3
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP cluster 1.1.1.1
set protocols bgp group IBGP neighbor 172.31.100.4
set protocols bgp group IBGP neighbor 172.31.100.11
set protocols bgp group IBGP neighbor 172.31.100.12
-
Konfigurieren Sie LDP und MPLS für alle Core-Schnittstellen.
set protocols ldp deaggregate
set protocols ldp transport-address 172.31.100.3
set protocols ldp interface all
set protocols mpls interface all
-
Konfigurieren Sie globale Services für die Anwenderverwaltung, wie z. B. die Verwaltung von Abonnenten, die Ablaufverfolgung und die Aktivierung einer erweiterten Anwenderverwaltung.
set system services subscriber-management traceoptions file submgmt.log
set system services subscriber-management traceoptions file size 30m
set system services subscriber-management traceoptions file files 10
set system services subscriber-management traceoptions flag all
set system services subscriber-management gres-route-flush-delay
set system services subscriber-management enable
-
Konfigurieren Sie Ablaufverfolgungsoptionen für den allgemeinen Authentifizierungsdienst.
set system processes general-authentication-service traceoptions file authd
set system processes general-authentication-service traceoptions file size 10m
set system processes general-authentication-service traceoptions file files 10
set system processes general-authentication-service traceoptions flag all
-
Konfigurieren Sie Systemdienste, einschließlich Ablaufverfolgungsvorgänge und Routing-Engine-Failover, für den wichtigsten Sitzungsverwaltungsprozess für die erweiterte Anwenderverwaltung, smg-service.
set system processes smg-service traceoptions file smgd
set system processes smg-service traceoptions file size 10m
set system processes smg-service traceoptions file files 10
set system processes smg-service traceoptions level all
set system processes smg-service traceoptions flag all
-
Definieren Sie globale Ablaufverfolgungsvorgänge für erweiterte DHCP-Prozesse auf lokalen DHCP-Servern und erweiterten DHCP-Relay-Agents.
set system processes dhcp-service traceoptions file jdhcpd
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions file files 10
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
set system processes dhcp-service traceoptions flag all
-
Konfigurieren Sie die Tunnel-Services und alle zusätzlichen Chassis-Konfigurationen.
set chassis fpc 0 pic 0 tunnel-services bandwidth 1g
set chassis fpc 0 performance-mode
-
Konfigurieren Sie Zugriffsprofile für DHCP-Abonnenten.
set access-profile no-auth
set access profile no-auth authentication-order none
set access address-protection
-
Konfigurieren Sie die Pseudowire-Schnittstelle für die Verwendung dynamischer gestapelter VLANs. Konfigurieren Sie außerdem zusätzliche Einstellungen für die Benutzeroberfläche und das VLAN-Abonnement. Konfigurieren Sie Ethernet Segment Identifier (ESI) für EVPN-Active-Standby-Multihoming.
set chassis pseudowire-service device-count 10
set interfaces ps0 anchor-point lt-0/0/10
set interfaces ps0 flexible-vlan-tagging
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include delimiter "@"
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include user-prefix vlan
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include interface-name
set interfaces ps0 auto-configure stacked-vlan-ranges access-profile no-auth
set interfaces ps0 auto-configure remove-when-no-subscribers
set interfaces ps0 mtu 2022
set interfaces ps0 esi 00:10:00:00:01:00:00:00:10:00
set interfaces ps0 esi single-active
set interfaces ps0 esi df-election-type preference value 1000
set interfaces ps0 unit 0 encapsulation ethernet-ccc
-
Konfigurieren Sie Internet-VRF für Internetrouten.
set interfaces lo0 unit 20 description "VRF:internet Loopback"
set interfaces lo0 unit 20 family inet address 172.16.100.3/32 primary
set routing-instances internet instance-type vrf
set routing-instances internet routing-options auto-export
set routing-instances internet interface lo0.20
set routing-instances internet route-distinguisher 172.31.100.3:12
set routing-instances internet vrf-import internet-vrf-import-pol
set routing-instances internet vrf-export internet-vrf-export-pol
set routing-instances internet vrf-table-label
set policy-options policy-statement internet-vrf-export-pol term all then community add 65000:999
set policy-options policy-statement internet-vrf-export-pol term all then accept
set policy-options policy-statement internet-vrf-import-pol term default from community 65000:999
set policy-options policy-statement internet-vrf-import-pol term default then accept
set policy-options policy-statement internet-vrf-import-pol term subs from community 65000:1131
set policy-options policy-statement internet-vrf-import-pol term subs then accept
set policy-options policy-statement internet-vrf-import-pol term other from community 65000:113
set policy-options policy-statement internet-vrf-import-pol term other then accept
set policy-options community 65000:113 members target:65000:113
set policy-options community 65000:1131 members target:65000:1131
set policy-options community 65000:999 members target:65000:999
-
Konfigurieren Sie die Optionen für den lokalen DHCP-Server auf einer Routing-Instanz. Sie konfigurieren und wenden Routing-Richtlinien für die DHCP-Anwender-Routing-Instanz an und wenden diese an, erstellen Domänenzuordnungen, Firewall-Filter und dynamische Profile für DHCP-Anwender.
set interfaces lo0 unit 313 description "VRF:dhcp-subs Loopback"
set interfaces lo0 unit 313 family inet address 172.16.16.3/32
set interfaces lo0 unit 313 family inet address 10.42.0.1/32 primary
set interfaces lo0 unit 313 family inet6 address 2015:cafe:2000::1/128
set routing-instances dhcp-subs instance-type vrf
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 next-table internet.inet6.0
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 no-readvertise
set routing-instances dhcp-subs routing-options router-id 172.16.16.3
set routing-instances dhcp-subs routing-options flow term-order standard
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 next-table internet.inet.0
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 no-readvertise
set routing-instances dhcp-subs routing-options static route 10.42.0.0/16 discard
set routing-instances dhcp-subs routing-options static route 10.42.0.0/16 tag 200
set routing-instances dhcp-subs routing-options auto-export
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection failure-action clear-binding-if-interface-up
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd version automatic
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd minimum-interval 30000
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd multiplier 3
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides client-discover-match incoming-interface
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides dual-stack dhcp-ds
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface demux0.0
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface ps0.0
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds authentication username-include mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds on-demand-address-allocation
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds classification-key mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds protocol-master inet
set routing-instances dhcp-subs system services dhcp-local-server no-stale-timer-refresh
set routing-instances dhcp-subs system services dhcp-local-server stale-timer 60
set routing-instances dhcp-subs access address-assignment high-utilization 80
set routing-instances dhcp-subs access address-assignment abated-utilization 70
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet network 10.42.0.0/16
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 low 10.42.0.2
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 high 10.42.255.254
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes maximum-lease-time 600
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes server-identifier 10.42.0.1
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes router 10.42.0.1
set routing-instances dhcp-subs access-profile no-auth
set routing-instances dhcp-subs interface lo0.313
set routing-instances dhcp-subs route-distinguisher 172.31.100.3:13
set routing-instances dhcp-subs vrf-import dhcp-subs-vrf-import-pol
set routing-instances dhcp-subs vrf-export dhcp-subs-vrf-export-pol
set routing-instances dhcp-subs vrf-table-label
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from protocol direct
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from route-filter 172.16.16.3/32 exact
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from protocol static
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from tag 200
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then community add 65000:1131
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then accept
set policy-options policy-statement dhcp-subs-vrf-import-pol term all from community 65000:111
set policy-options policy-statement dhcp-subs-vrf-import-pol term all then accept
set policy-options community 65000:111 members target:65000:111
set policy-options community 65000:111 members target:65000:11
set access domain map none access-profile no-auth
set access domain map none target-routing-instance dhcp-subs
set access domain map ps0.* access-profile no-auth
set access domain map ps0.* target-routing-instance dhcp-subs
set access domain map ps0:* access-profile no-auth
set access domain map ps0:* target-routing-instance dhcp-subs
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-address 255.255.255.255/32
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-port dhcp
set firewall family inet filter rpf-pass-dhcp term allow-dhcp then accept
set firewall family inet filter rpf-pass-dhcp term default then discard
set system dynamic-profile-options versioning
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" actual-transit-statistics
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" demux-options underlying-interface "$junos-underlying-interface"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet rpf-check fail-filter rpf-pass-dhcp
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet demux-source $junos-subscriber-ip-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 demux-source $junos-subscriber-ipv6-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 unnumbered-address lo0.313
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds dynamic-profile prod-dhcp-base
-
Konfigurieren und Anwenden dynamischer Profile für die Pseudowire-Schnittstelle.
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix next-hop "$junos-framed-route-nexthop"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles auto-pwht interfaces interface-set "$junos-phy-ifd-interface-set-name" interface "$junos-interface-ifd-name" unit "$junos-interface-unit"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp restricted
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-id "$junos-vlan-id"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate loose
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags outer "$junos-stacked-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags inner "$junos-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" demux-options underlying-interface "$junos-interface-ifd-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate strict
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.42.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.43.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include delimiter "@"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include user-prefix vlan
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include interface-name
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges session-timeout 600
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet mac-validate strict
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet6 unnumbered-address lo0.313
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht accept any
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht ranges any,any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht accept any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht ranges any
-
Konfigurieren Sie eine Routing-Instanz vom Typ evpn-vpws, indem Sie die Routenunterscheidung und das VRF-Ziel definieren.
set routing-instances EVPN-VPWS-BNG-1 instance-type evpn-vpws
set routing-instances EVPN-VPWS-BNG-1 protocols evpn interface ps0.0 vpws-service-id local 9999
set routing-instances EVPN-VPWS-BNG-1 protocols evpn interface ps0.0 vpws-service-id remote 1111
set routing-instances EVPN-VPWS-BNG-1 interface ps0.0
set routing-instances EVPN-VPWS-BNG-1 route-distinguisher 172.31.100.3:11
set routing-instances EVPN-VPWS-BNG-1 vrf-target target:65000:11
BNG2 konfigurieren
-
Melden Sie sich beim BNG2-Gerät an. Stellen Sie sicher, dass auf dem Gerät Junos Version 22.4R1 oder höher ausgeführt wird.
-
Konfigurieren Sie Systemdienste.
set system host-name BNG2
set system configuration-database max-db-size 698343424
set system services ssh root-login allow
set chassis network-services enhanced-ip
-
Erstellen Sie eine Gruppe, um die Konfiguration gemeinsamer Kernschnittstellen wie MTU, Haltezeit und Dämpfungsparameter zu definieren.
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED-ADD-DESCRIPTION********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
-
Konfigurieren Sie die Schnittstellen zu Core-Geräten.
set interfaces ge-0/0/0 apply-groups GR-CORE-INTF
set interfaces ge-0/0/0 unit 0 family inet address 10.1.0.2/30
set interfaces ge-0/0/0 unit 0 family iso
set interfaces ge-0/0/0 unit 0 family mpls
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.2.2/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.12.2/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
-
Konfigurieren Sie die Schnittstelle zur vQFX.
set interfaces ge-0/0/3 mtu 9192
set interfaces ge-0/0/3 unit 0 family inet address 192.168.100.171/23
-
Konfigurieren Sie die Loopback-Schnittstelle für die Verwendung im Zugriffsnetzwerk der Anwender-Verwaltung.
set interfaces lo0 unit 0 family inet address 172.31.100.4/32
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 primary
set interfaces lo0 unit 0 family inet address 192.168.0.1/32 preferred
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0004.00
set interfaces lo0 unit 0 family mpls
-
Konfigurieren Sie das IS-IS-Protokoll im Core-Netzwerk.
set protocols isis interface ge-0/0/0.0
set protocols isis interface ge-0/0/1.0
set protocols isis interface ge-0/0/2.0
set protocols isis interface lo0.0 passive
set protocols isis level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
-
Konfigurieren Sie Routing-Optionen.
set routing-options router-id 172.31.100.4
set routing-options autonomous-system 65000
-
Konfigurieren Sie das BGP-Protokoll zwischen der BNG und den Zugriffsgeräten.
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.4
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP cluster 2.2.2.2
set protocols bgp group IBGP neighbor 172.31.100.3
set protocols bgp group IBGP neighbor 172.31.100.11
set protocols bgp group IBGP neighbor 172.31.100.12
-
Konfigurieren Sie LDP und MPLS für alle Core-Schnittstellen.
set protocols ldp deaggregate
set protocols ldp transport-address 172.31.100.4
set protocols ldp interface all
set protocols mpls interface all
-
Konfigurieren Sie globale Services für die Anwenderverwaltung, wie z. B. die Verwaltung von Abonnenten, die Ablaufverfolgung und die Aktivierung einer erweiterten Anwenderverwaltung.
set system services subscriber-management traceoptions file submgmt.log
set system services subscriber-management traceoptions file size 30m
set system services subscriber-management traceoptions file files 10
set system services subscriber-management traceoptions flag all
set system services subscriber-management gres-route-flush-delay
set system services subscriber-management enable
-
Konfigurieren Sie Ablaufverfolgungsoptionen für den allgemeinen Authentifizierungsdienst.
set system processes general-authentication-service traceoptions file authd
set system processes general-authentication-service traceoptions file size 10m
set system processes general-authentication-service traceoptions file files 10
set system processes general-authentication-service traceoptions flag all
-
Konfigurieren Sie Systemdienste, einschließlich Ablaufverfolgungsvorgänge und Routing-Engine-Failover, für den wichtigsten Sitzungsverwaltungsprozess für die erweiterte Anwenderverwaltung, smg-service.
set system processes smg-service traceoptions file smgd
set system processes smg-service traceoptions file size 10m
set system processes smg-service traceoptions file files 10
set system processes smg-service traceoptions level all
set system processes smg-service traceoptions flag all
-
Definieren Sie globale Ablaufverfolgungsvorgänge für erweiterte DHCP-Prozesse auf lokalen DHCP-Servern und erweiterten DHCP-Relay-Agents.
set system processes dhcp-service traceoptions file jdhcpd
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions file files 10
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
set system processes dhcp-service traceoptions flag all
-
Konfigurieren Sie die Tunnel-Services und alle zusätzlichen Chassis-Konfigurationen.
set chassis fpc 0 pic 0 tunnel-services bandwidth 1g
set chassis fpc 0 performance-mode
-
Konfigurieren Sie Zugriffsprofile für DHCP-Abonnenten.
set access-profile no-auth
set access profile no-auth authentication-order none
set access address-protection
-
Konfigurieren Sie die Pseudowire-Schnittstelle für die Verwendung dynamischer gestapelter VLANs. Konfigurieren Sie außerdem zusätzliche Einstellungen für die Benutzeroberfläche und das VLAN-Abonnement. Konfigurieren Sie Ethernet Segment Identifier (ESI) für EVPN-Active-Standby-Multihoming.
set chassis pseudowire-service device-count 10
set interfaces ps0 anchor-point lt-0/0/10
set interfaces ps0 flexible-vlan-tagging
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include delimiter "@"
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include user-prefix vlan
set interfaces ps0 auto-configure stacked-vlan-ranges authentication username-include interface-name
set interfaces ps0 auto-configure stacked-vlan-ranges access-profile no-auth
set interfaces ps0 auto-configure remove-when-no-subscribers
set interfaces ps0 mtu 2022
set interfaces ps0 esi 00:10:00:00:01:00:00:00:10:00
set interfaces ps0 esi single-active
set interfaces ps0 esi df-election-type preference value 999
set interfaces ps0 unit 0 encapsulation ethernet-ccc
-
Konfigurieren Sie Internet-VRF für Internetrouten.
set interfaces lo0 unit 20 description "VRF:internet Loopback"
set interfaces lo0 unit 20 family inet address 172.16.100.4/32 primary
set routing-instances internet instance-type vrf
set routing-instances internet routing-options auto-export
set routing-instances internet interface lo0.20
set routing-instances internet route-distinguisher 172.31.100.4:12
set routing-instances internet vrf-import internet-vrf-import-pol
set routing-instances internet vrf-export internet-vrf-export-pol
set routing-instances internet vrf-table-label
set policy-options policy-statement internet-vrf-export-pol term all then community add 65000:999
set policy-options policy-statement internet-vrf-export-pol term all then accept
set policy-options policy-statement internet-vrf-import-pol term default from community 65000:999
set policy-options policy-statement internet-vrf-import-pol term default then accept
set policy-options policy-statement internet-vrf-import-pol term subs from community 65000:1131
set policy-options policy-statement internet-vrf-import-pol term subs then accept
set policy-options policy-statement internet-vrf-import-pol term other from community 65000:113
set policy-options policy-statement internet-vrf-import-pol term other then accept
set policy-options community 65000:113 members target:65000:113
set policy-options community 65000:1131 members target:65000:1131
set policy-options community 65000:999 members target:65000:999
-
Konfigurieren Sie die Optionen für den lokalen DHCP-Server auf einer Routing-Instanz. Sie konfigurieren und wenden Routing-Richtlinien für die DHCP-Anwender-Routing-Instanz an und wenden diese an, erstellen Domänenzuordnungen, Firewall-Filter und dynamische Profile für DHCP-Anwender.
set interfaces lo0 unit 313 description "VRF:dhcp-subs Loopback"
set interfaces lo0 unit 313 family inet address 172.16.16.4/32
set interfaces lo0 unit 313 family inet address 10.43.0.1/32 primary
set interfaces lo0 unit 313 family inet6 address   2016:cafe:2000::1/128
set routing-instances dhcp-subs instance-type vrf
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 next-table internet.inet6.0
set routing-instances dhcp-subs routing-options rib dhcp-subs.inet6.0 static route ::/0 no-readvertise
set routing-instances dhcp-subs routing-options router-id 172.16.16.4
set routing-instances dhcp-subs routing-options flow term-order standard
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 next-table internet.inet.0
set routing-instances dhcp-subs routing-options static route 0.0.0.0/0 no-readvertise
set routing-instances dhcp-subs routing-options static route 10.43.0.0/16 discard
set routing-instances dhcp-subs routing-options static route 10.43.0.0/16 tag 200
set routing-instances dhcp-subs routing-options auto-export
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection failure-action clear-binding-if-interface-up
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd version automatic
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd minimum-interval 30000
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls liveness-detection method bfd multiplier 3
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides client-discover-match incoming-interface
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls overrides dual-stack dhcp-ds
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface demux0.0
set routing-instances dhcp-subs system services dhcp-local-server group dhcp-ls interface ps0.0
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds authentication username-include mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds on-demand-address-allocation
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds classification-key mac-address
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds protocol-master inet
set routing-instances dhcp-subs system services dhcp-local-server no-stale-timer-refresh
set routing-instances dhcp-subs system services dhcp-local-server stale-timer 60
set routing-instances dhcp-subs access address-assignment high-utilization 80
set routing-instances dhcp-subs access address-assignment abated-utilization 70
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet network 10.43.0.0/16
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 low 10.43.0.2
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet range range1 high 10.43.254.254
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes maximum-lease-time 600
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes server-identifier 10.43.0.1
set routing-instances dhcp-subs access address-assignment pool ipv4-pool-0 family inet dhcp-attributes router 10.43.0.1
set routing-instances dhcp-subs access-profile no-auth
set routing-instances dhcp-subs interface lo0.313
set routing-instances dhcp-subs route-distinguisher 172.31.100.4:13
set routing-instances dhcp-subs vrf-import dhcp-subs-vrf-import-pol
set routing-instances dhcp-subs vrf-export dhcp-subs-vrf-export-pol
set routing-instances dhcp-subs vrf-table-label
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from protocol direct
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop from route-filter 172.16.16.4/32 exact
set policy-options policy-statement dhcp-subs-vrf-export-pol term loop then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from protocol static
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools from tag 200
set policy-options policy-statement dhcp-subs-vrf-export-pol term pools then community add 65000:113
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then community add 65000:1131
set policy-options policy-statement dhcp-subs-vrf-export-pol term subs then accept
set policy-options policy-statement dhcp-subs-vrf-import-pol term all from community 65000:111
set policy-options policy-statement dhcp-subs-vrf-import-pol term all then accept
set policy-options community 65000:111 members target:65000:111
set policy-options community 65000:111 members target:65000:11
set policy-options community 65000:113 members target:65000:113
set policy-options community 65000:1131 members target:65000:1131
set access-profile no-auth
set access profile no-auth authentication-order none
set access address-protection
set access domain map none access-profile no-auth
set access domain map none target-routing-instance dhcp-subs
set access domain map ps0.* access-profile no-auth
set access domain map ps0.* target-routing-instance dhcp-subs
set access domain map ps0:* access-profile no-auth
set access domain map ps0:* target-routing-instance dhcp-subs
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-address 255.255.255.255/32
set firewall family inet filter rpf-pass-dhcp term allow-dhcp from destination-port dhcp
set firewall family inet filter rpf-pass-dhcp term allow-dhcp then accept
set firewall family inet filter rpf-pass-dhcp term default then discard
set system dynamic-profile-options versioning
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles prod-dhcp-base routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" actual-transit-statistics
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" demux-options underlying-interface "$junos-underlying-interface"
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet rpf-check fail-filter rpf-pass-dhcp
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet demux-source $junos-subscriber-ip-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 demux-source $junos-subscriber-ipv6-address
set dynamic-profiles prod-dhcp-base interfaces demux0 unit "$junos-interface-unit" family inet6 unnumbered-address lo0.313
set routing-instances dhcp-subs system services dhcp-local-server dual-stack-group dhcp-ds dynamic-profile prod-dhcp-base
-
Konfigurieren und Anwenden dynamischer Profile für die Pseudowire-Schnittstelle.
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix next-hop "$junos-framed-route-nexthop"
set dynamic-profiles auto-pwht routing-instances "$junos-routing-instance" routing-options access route $junos-framed-route-ip-address-prefix metric "$junos-framed-route-cost"
set dynamic-profiles auto-pwht interfaces interface-set "$junos-phy-ifd-interface-set-name" interface "$junos-interface-ifd-name" unit "$junos-interface-unit"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp restricted
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-id "$junos-vlan-id"
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate loose
set dynamic-profiles auto-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" no-traps
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" proxy-arp
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags outer "$junos-stacked-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" vlan-tags inner "$junos-vlan-id"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" demux-options underlying-interface "$junos-interface-ifd-name"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet mac-validate strict
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet unnumbered-address "$junos-loopback-interface"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.42.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges dynamic-profile PROF_AUTOSENSE_IPDEMUX network 10.43.0.0/16
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include delimiter "@"
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include user-prefix vlan
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges authentication username-include interface-name
set dynamic-profiles auto-stacked-pwht interfaces "$junos-interface-ifd-name" unit "$junos-interface-unit" family inet auto-configure address-ranges session-timeout 600
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX routing-instances "$junos-routing-instance" interface "$junos-interface-name"
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet mac-validate strict
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet unnumbered-address lo0.313
set dynamic-profiles PROF_AUTOSENSE_IPDEMUX interfaces demux0 unit "$junos-underlying-interface-unit" family inet6 unnumbered-address lo0.313
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht accept any
set interfaces ps0 auto-configure stacked-vlan-ranges dynamic-profile auto-stacked-pwht ranges any,any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht accept any
set interfaces ps0 auto-configure vlan-ranges dynamic-profile auto-pwht ranges any
-
Konfigurieren Sie eine Routing-Instanz vom Typ evpn-vpws, indem Sie die Routenunterscheidung und das VRF-Ziel definieren.
set routing-instances EVPN-VPWS-BNG-2 instance-type evpn-vpws
set routing-instances EVPN-VPWS-BNG-2 protocols evpn interface ps0.0 vpws-service-id local 9999
set routing-instances EVPN-VPWS-BNG-2 protocols evpn interface ps0.0 vpws-service-id remote 1111
set routing-instances EVPN-VPWS-BNG-2 interface ps0.0
set routing-instances EVPN-VPWS-BNG-2 route-distinguisher 172.31.100.4:11
set routing-instances EVPN-VPWS-BNG-2 vrf-target target:65000:11
Konfiguration von ACX1
-
Melden Sie sich beim ACX1-Gerät an.
-
Konfigurieren Sie Systemeinstellungen und DHCP-Diensteinstellungen.
set system host-name ACX1
set system services ssh root-login allow
set chassis network-services enhanced-ip
set system processes dhcp-service traceoptions file dhcp_logfile
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
-
Erstellen Sie eine Gruppe, um die Konfiguration gemeinsamer Kernschnittstellen wie MTU, Haltezeit und Dämpfungsparameter zu definieren.
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED-ADD-DESCRIPTION********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
-
Konfigurieren Sie die Schnittstellen zu den Core-Geräten
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.1.2/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.12.1/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
-
Konfigurieren Sie die aggregierte Schnittstelle mit entsprechender VLAN- und Ethernet Segment Identifier (ESI)-Konfiguration.
set chassis aggregated-devices ethernet device-count 10
set interfaces ge-0/0/3 gigether-options 802.3ad ae10
set interfaces ae10 flexible-vlan-tagging
set interfaces ae10 encapsulation flexible-ethernet-services
set interfaces ae10 esi 00:11:11:11:11:11:11:11:11:11
set interfaces ae10 esi all-active
set interfaces ae10 aggregated-ether-options lacp active
set interfaces ae10 aggregated-ether-options lacp system-id 00:00:00:00:00:10
set interfaces ae10 unit 0 encapsulation vlan-ccc
set interfaces ae10 unit 0 vlan-id-list 301-500
set interfaces ae10 unit 0 input-vlan-map push
set interfaces ae10 unit 0 input-vlan-map vlan-id 100
set interfaces ae10 unit 0 output-vlan-map pop
-
Konfigurieren Sie die Loopback-Schnittstellen.
set interfaces lo0 unit 0 family inet address 172.31.100.11/32
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0011.00
set interfaces lo0 unit 0 family mpls
-
Konfigurieren Sie das IS-IS-Protokoll für das Kernnetzwerk.
set protocols isis interface all level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
-
Konfigurieren Sie Routing-Optionen.
set routing-options router-id 172.31.100.11
set routing-options autonomous-system 65000
-
Konfigurieren Sie das BGP-Protokoll zwischen den Zugriffsgeräten und BNG.
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.11
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP neighbor 172.31.100.3
set protocols bgp group IBGP neighbor 172.31.100.4
-
Konfigurieren Sie die LDP- und MPLS-Protokolle auf den Core-Schnittstellen.
set protocols ldp interface all
set protocols mpls interface all
-
Konfigurieren Sie eine Routing-Instanz vom Typ evpn-vpws, indem Sie die Routenunterscheidung und das VRF-Ziel definieren.
set routing-instances EVPN-VPWS instance-type evpn-vpws
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id local 1111
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id remote 9999
set routing-instances EVPN-VPWS interface ae10.0
set routing-instances EVPN-VPWS route-distinguisher 172.31.100.11:11
set routing-instances EVPN-VPWS vrf-target target:65000:11
Konfiguration von ACX2
-
Melden Sie sich beim ACX2-Gerät an.
-
Konfigurieren Sie Systemeinstellungen und DHCP-Diensteinstellungen.
set system host-name ACX2
set system services ssh root-login allow
set chassis network-services enhanced-ip
set system processes dhcp-service traceoptions file dhcp_logfile
set system processes dhcp-service traceoptions file size 10m
set system processes dhcp-service traceoptions level all
set system processes dhcp-service traceoptions flag packet
-
Erstellen Sie eine Gruppe, um die Konfiguration gemeinsamer Kernschnittstellen wie MTU, Haltezeit und Dämpfungsparameter zu definieren.
set groups GR-CORE-INTF interfaces <*> description ********GR-CORE-INTF-SETTINGS-APPLIED-ADD-DESCRIPTION********
set groups GR-CORE-INTF interfaces <*> traps
set groups GR-CORE-INTF interfaces <*> mtu 9192
set groups GR-CORE-INTF interfaces <*> hold-time up 2000
set groups GR-CORE-INTF interfaces <*> hold-time down 0
set groups GR-CORE-INTF interfaces <*> damping half-life 30
set groups GR-CORE-INTF interfaces <*> damping max-suppress 600
set groups GR-CORE-INTF interfaces <*> damping reuse 250
set groups GR-CORE-INTF interfaces <*> damping suppress 2000
set groups GR-CORE-INTF interfaces <*> damping enable
set groups GR-CORE-INTF interfaces <*> unit 0 traps
set groups GR-CORE-INTF interfaces <*> unit 0 family inet mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family iso mtu 9106
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls mtu 9170
set groups GR-CORE-INTF interfaces <*> unit 0 family mpls maximum-labels 5
-
Konfigurieren Sie die Schnittstellen zu den Core-Geräten.
set interfaces ge-0/0/1 apply-groups GR-CORE-INTF
set interfaces ge-0/0/1 unit 0 family inet address 10.1.2.1/30
set interfaces ge-0/0/1 unit 0 family iso
set interfaces ge-0/0/1 unit 0 family mpls
set interfaces ge-0/0/2 apply-groups GR-CORE-INTF
set interfaces ge-0/0/2 unit 0 family inet address 10.1.21.1/30
set interfaces ge-0/0/2 unit 0 family iso
set interfaces ge-0/0/2 unit 0 family mpls
-
Konfigurieren Sie die aggregierte Schnittstelle mit entsprechender VLAN- und Ethernet Segment Identifier (ESI)-Konfiguration.
set interfaces ge-0/0/3 gigether-options 802.3ad ae10
set interfaces ae10 flexible-vlan-tagging
set interfaces ae10 encapsulation flexible-ethernet-services
set interfaces ae10 esi 00:11:11:11:11:11:11:11:11:11
set interfaces ae10 esi all-active
set interfaces ae10 aggregated-ether-options lacp active
set interfaces ae10 aggregated-ether-options lacp system-id 00:00:00:00:00:10
set interfaces ae10 unit 0 encapsulation vlan-ccc
set interfaces ae10 unit 0 vlan-id-list 301-500
set interfaces ae10 unit 0 input-vlan-map push
set interfaces ae10 unit 0 input-vlan-map vlan-id 100
set interfaces ae10 unit 0 output-vlan-map pop
-
Konfigurieren Sie die Loopback-Schnittstellen.
set interfaces lo0 unit 0 family inet address 172.31.100.12/32
set interfaces lo0 unit 0 family iso address 49.0001.1000.0000.0012.00
set interfaces lo0 unit 0 family mpls
-
Konfigurieren Sie das IS-IS-Protokoll für das Kernnetzwerk.
set protocols isis interface all level 1 disable
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from interface lo0.0
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK from route-filter 172.31.0.0/16 prefix-length-range /32-/32
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then tag 101
set policy-options policy-statement PL-ISIS-EXPORT term LOCAL-LOOPBACK then accept
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES from protocol direct
set policy-options policy-statement PL-ISIS-EXPORT term DIRECT-ROUTES then accept
set policy-options policy-statement PL-ISIS-EXPORT then reject
set protocols isis export PL-ISIS-EXPORT
-
Konfigurieren Sie Routing-Optionen.
set routing-options router-id 172.31.100.12
set routing-options autonomous-system 65000
-
Konfigurieren Sie das BGP-Protokoll zwischen den Zugriffsgeräten und BNG.
set protocols bgp group IBGP type internal
set protocols bgp group IBGP local-address 172.31.100.12
set protocols bgp group IBGP family evpn signaling
set protocols bgp group IBGP neighbor 172.31.100.3
set protocols bgp group IBGP neighbor 172.31.100.4
-
Konfigurieren Sie die LDP- und MPLS-Protokolle auf den Core-Schnittstellen.
set protocols ldp interface all
set protocols mpls interface all
-
Konfigurieren Sie eine Routing-Instanz vom Typ evpn-vpws, indem Sie die Routenunterscheidung und das VRF-Ziel definieren.
set routing-instances EVPN-VPWS instance-type evpn-vpws
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id local 1111
set routing-instances EVPN-VPWS protocols evpn interface ae10.0 vpws-service-id remote 9999
set routing-instances EVPN-VPWS interface ae10.0
set routing-instances EVPN-VPWS route-distinguisher 172.31.100.12:11
set routing-instances EVPN-VPWS vrf-target target:65000:11
Verifizierung
Zweck
Sie können die Konfiguration überprüfen, indem Sie den show evpn vpws-instance Befehl auf dem BNG und den Geräten eingeben, um die Details der VPWS-Instanz des EVPN anzuzeigen.
Aktion
-
Überprüfung auf dem BNG1-Gerät.
show evpn vpws-instance Instance: EVPN-VPWS-BNG-1, Instance type: EVPN VPWS, Encapsulation type: MPLS Route Distinguisher: 172.31.100.3:11 Number of local interfaces: 1 (1 up) Interface name ESI Mode Role Status Control-Word Flow-Label-Tx Flow-Label-Rx ps0.0 00:10:00:00:01:00:00:00:10:00 single-active Primary Up No No No Local SID: 9999 Advertised Label: 46 PE addr ESI Label End.Dx2 SID Mode Role TS Status 172.31.100.4 00:10:00:00:01:00:00:00:10:00 64 single-active Backup 2023-07-24 11:08:27.958 Resolved Remote SID: 1111 PE addr ESI Label End.Dx2 SID Mode Role TS Status 172.31.100.11 00:11:11:11:11:11:11:11:11:11 300112 all-active Primary 2023-07-24 11:08:17.689 Resolved 172.31.100.12 00:11:11:11:11:11:11:11:11:11 300096 all-active Primary 2023-07-24 11:08:17.689 Resolved Number of protect interfaces: 0 Fast Convergence Information ESI: 00:10:00:00:01:00:00:00:10:00 Number of PE nodes: 1 PE: 172.31.100.4 Advertised SID: 9999 Fast Convergence Information ESI: 00:11:11:11:11:11:11:11:11:11 Number of PE nodes: 2 PE: 172.31.100.11 Advertised SID: 1111 PE: 172.31.100.12 Advertised SID: 1111 DF Election Information for Single-Active ESI ESI: 00:10:00:00:01:00:00:00:10:00 DF Election Algorithm: Preference based Primary PE: 172.31.100.3, Preference: 1000 Backup PE: 172.31.100.4, Preference: 999 Last DF Election: 2023-07-24 11:08:27 -
Überprüfung auf dem BNG2-Gerät.
show evpn vpws-instance Instance: EVPN-VPWS-BNG-2, Instance type: EVPN VPWS, Encapsulation type: MPLS Route Distinguisher: 172.31.100.4:11 Number of local interfaces: 1 (1 up) Interface name ESI Mode Role Status Control-Word Flow-Label-Tx Flow-Label-Rx ps0.0 00:10:00:00:01:00:00:00:10:00 single-active Backup Up No No No Local SID: 9999 Advertised Label: 64 PE addr ESI Label End.Dx2 SID Mode Role TS Status 172.31.100.3 00:10:00:00:01:00:00:00:10:00 46 single-active Primary 2023-07-24 11:08:27.750 Resolved Remote SID: 1111 PE addr ESI Label End.Dx2 SID Mode Role TS Status 172.31.100.11 00:11:11:11:11:11:11:11:11:11 300112 all-active Primary 2023-07-24 10:59:26.019 Resolved 172.31.100.12 00:11:11:11:11:11:11:11:11:11 300096 all-active Primary 2023-07-24 10:59:26.317 Resolved Number of protect interfaces: 0 Fast Convergence Information ESI: 00:10:00:00:01:00:00:00:10:00 Number of PE nodes: 1 PE: 172.31.100.3 Advertised SID: 9999 Fast Convergence Information ESI: 00:11:11:11:11:11:11:11:11:11 Number of PE nodes: 2 PE: 172.31.100.11 Advertised SID: 1111 PE: 172.31.100.12 Advertised SID: 1111 DF Election Information for Single-Active ESI ESI: 00:10:00:00:01:00:00:00:10:00 DF Election Algorithm: Preference based Primary PE: 172.31.100.3, Preference: 1000 Backup PE: 172.31.100.4, Preference: 999 Last DF Election: 2023-07-24 11:08:27 -
Überprüfung auf ACX1-Gerät.
show evpn vpws-instance Instance: EVPN-VPWS, Instance type: EVPN VPWS, Encapsulation type: MPLS Route Distinguisher: 172.31.100.11:11 Number of local interfaces: 1 (1 up) Interface name ESI Mode Role Status Control-Word Flow-Label-Tx Flow-Label-Rx ae10.0 00:11:11:11:11:11:11:11:11:11 all-active Primary Up No No No Local SID: 1111 Advertised Label: 300112 PE addr ESI Label End.Dx2 SID Mode Role TS Status 172.31.100.12 00:11:11:11:11:11:11:11:11:11 300096 all-active Primary 2023-07-24 10:59:26.522 Resolved Remote SID: 9999 PE addr ESI Label End.Dx2 SID Mode Role TS Status 172.31.100.4 00:10:00:00:01:00:00:00:10:00 64 single-active Backup 2023-07-24 11:08:27.963 Resolved 172.31.100.3 00:10:00:00:01:00:00:00:10:00 46 single-active Primary 2023-07-24 11:08:27.749 Resolved Number of protect interfaces: 0 Fast Convergence Information ESI: 00:10:00:00:01:00:00:00:10:00 Number of PE nodes: 2 PE: 172.31.100.4 Advertised SID: 9999 PE: 172.31.100.3 Advertised SID: 9999 Fast Convergence Information ESI: 00:11:11:11:11:11:11:11:11:11 Number of PE nodes: 1 PE: 172.31.100.12 Advertised SID: 1111 -
Überprüfung auf dem ACX2-Gerät.
show evpn vpws-instance
Instance: EVPN-VPWS, Instance type: EVPN VPWS, Encapsulation type: MPLS
  Route Distinguisher: 172.31.100.12:11
  Number of local interfaces: 1 (1 up)

    Interface name  ESI                            Mode          Role       Status     Control-Word    Flow-Label-Tx    Flow-Label-Rx
    ae10.0          00:11:11:11:11:11:11:11:11:11 all-active      Primary    Up         No              No               No
        Local SID: 1111 Advertised Label: 300096
            PE addr         ESI                           Label  End.Dx2 SID     Mode           Role     TS                      Status
            172.31.100.11   00:11:11:11:11:11:11:11:11:11 300112                 all-active     Primary  2023-07-24 10:59:26.224 Resolved
        Remote SID: 9999
            PE addr         ESI                           Label  End.Dx2 SID     Mode           Role     TS                      Status
            172.31.100.4    00:10:00:00:01:00:00:00:10:00 64                     single-active  Backup   2023-07-24 11:08:27.960 Resolved
            172.31.100.3    00:10:00:00:01:00:00:00:10:00 46                     single-active  Primary  2023-07-24 11:08:27.750 Resolved
  Number of protect interfaces: 0

    Fast Convergence Information
    ESI: 00:10:00:00:01:00:00:00:10:00 Number of PE nodes: 2
        PE: 172.31.100.4
            Advertised SID: 9999
        PE: 172.31.100.3
            Advertised SID: 9999

    Fast Convergence Information
    ESI: 00:11:11:11:11:11:11:11:11:11 Number of PE nodes: 1
        PE: 172.31.100.11
            Advertised SID: 1111
Bedeutung
Die BNG-Geräte sind in einem Aktiv-Standby-Multihoming-Modus konfiguriert. Im stationären Zustand werden alle Datenströme auf BNG1 gerichtet, das das primäre Gerät zwischen BNG1 und BNG2 ist. Falls BNG1 einen Fehler erfährt, wird BNG2 zum primären designierten Spediteur. Die Zugriffsgeräte werden im Aktiv-Aktiv-Multihoming konfiguriert, wobei der gesamte Datenverkehr von den CE-Geräten durch Load Balancing übertragen wird.